
 synacktiv/octoscan
Octoscan은 GitHub Actions 워크플로우를 위한 정적 취약점 스캐너입니다.

Octoscan은 GitHub 액션 워크플로를 위한 정적 취약점 스캐너입니다.

각 규칙에 대한 취약한 워크플로는 testdata에 있으며, 규칙을 시험하려면 ./octoscan scan testdata를 실행하세요.
$ go mod tidy
$ go build
또는 docker 사용:
$ docker pull ghcr.io/synacktiv/octoscan:latest
Octoscan은 로컬 git 저장소에 대해 실행하거나 dl 액션을 사용하여 모든 워크플로를 다운로드할 수 있습니다:
$ octoscan dl -h
Octoscan.

Usage:
	octoscan dl [options] --org <org> [--repo <repo> --token <pat> --default-branch --max-branches <num> --path <path> --output-dir <dir> --include-archives]

Options:
	-h, --help  						Show help
	-d, --debug  						Debug output
	--verbose  						Verbose output
	--org <org>  						Organizations to target
	--repo <repo>  						Repository to target
	--token <pat>  						GHP to authenticate to GitHub
	--default-branch  					Only download workflows from the default branch
	--max-branches <num>  					Limit the number of branches to download
	--path <path>  						GitHub file path to download [default: .github/workflows]
	--output-dir <dir>  					Output dir where to download files [default: octoscan-output]
	--include-archives  					Also download archived repositories
./octoscan dl --token ghp_<token> --org apache --repo incubator-answer
무엇을 실행해야 할지 모르겠다면 그냥 이것을 실행하세요:
./octoscan scan path/to/repos/ --disable-rules shellcheck,local-action --filter-triggers external
오탐을 줄이고 가장 흥미로운 결과를 제공합니다.
dl 명령으로 워크플로를 다운로드한 경우, 기본적으로 octoscan이 모든 브랜치의 모든 워크플로를 다운로드하기 때문에 중복된 워크플로가 있을 수 있습니다. 중복된 워크플로를 삭제하고 분석 속도를 높이려면 분석을 실행하기 전에 fdupes 명령을 사용할 수 있습니다:
fdupes -n -r -N -d path/to/repo
$ octoscan scan -h
octoscan

Usage:
	octoscan scan [options] --list-rules
	octoscan scan [options] <target>
	octoscan scan [options] <target> [--debug-rules --filter-triggers=<triggers> --filter-run --ignore=<pattern> ((--disable-rules | --enable-rules ) <rules>) --config-file <config>]

Options:
	-h, --help
	-v, --version
	-d, --debug
	--verbose
	--format <format>  				Output format, json, sarif or custom template to format error messages in Go template syntax. See https://github.com/rhysd/actionlint/tree/main/docs/usage.md#format
	--oneline 					Use one line per one error. Useful for reading error messages from programs

Args:
	<target>					Target File or directory to scan
	--filter-triggers <triggers>			Scan workflows with specific triggers (comma separated list: "push,pull_request_target" or pre-configured: external/allnopr)
	--filter-run					Search for expression injection only in run shell scripts.
	--ignore <pattern>				Regular expression matching to error messages you want to ignore.
	--disable-rules <rules>				Disable specific rules. Split on ","
	--enable-rules <rules>				Enable specific rules, this will disable all other rules. Split on ","
	--debug-rules					Enable debug rules.
	--config-file <config>				Config file.

Examples:
	$ octoscan scan ci.yml --disable-rules shellcheck,local-action --filter-triggers external
이 도구는 push/pull_request 이벤트에서 저장소를 스캔하는 GitHub action으로 직접 사용할 수도 있습니다. 자세한 내용은 이 저장소를 확인하세요.
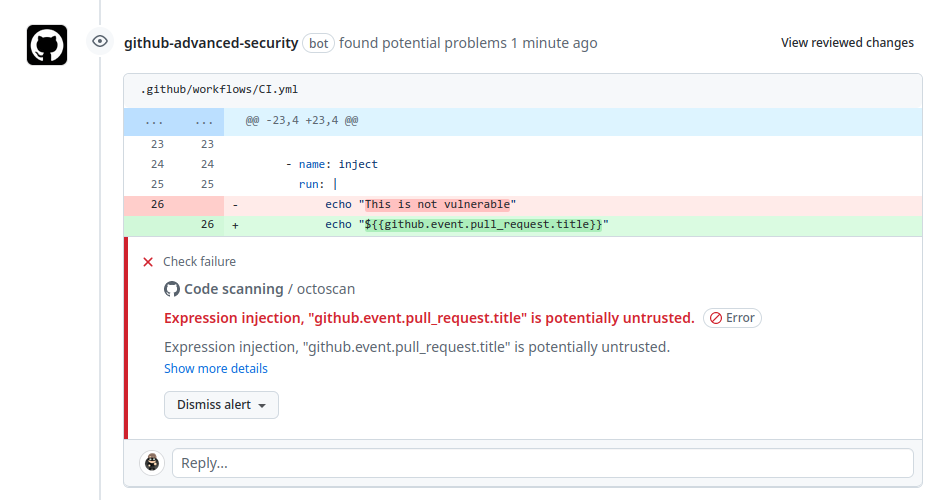
전체 규칙 목록은 다음 명령으로 확인할 수 있습니다:
$ octoscan scan --list-rules
2024/08/07 16:50:48 [INFO] Available rules
- shellcheck
	Checks for shell script sources in "run:" using shellcheck
- credentials
	Checks for credentials in "services:" configuration
- dangerous-action
	Check for dangerous actions.
- dangerous-checkout
	Check for dangerous checkout.
- expression-injection
	Check for expression injection.
- dangerous-write
	Check for dangerous write operation on $GITHUB_OUTPUT or $GITHUB_ENV.
- local-action
	Check for local actions.
- runner-label
	Checks for GitHub-hosted and preset self-hosted runner labels in "runs-on:"
- unsecure-commands
	Check 'ACTIONS_ALLOW_UNSECURE_COMMANDS' env variable.
- known-vulnerability
	Check for known vulnerabilities.
- bot-check
	Check for if statements that are based on a bot identity.
- dangerous-artefact
	Check for workflow that upload artefacts containing sensitive files.
- overprovisioned-secrets
	Check for dumps (toJSON(secrets)) and dynamic accesses (secrets[...]) of the secrets context.
- toctou
	Check for checkouts of a mutable PR reference in workflows triggered after an approval (comment, dispatch, label).
- prompt-injection
	Check for AI agents that process untrusted input, that anyone can trigger or that have dangerous tools.
- unsound-condition
	Check for "if:" conditions that can be bypassed or that are always true.
- debug-external-trigger
	Check for workflow that can be externally triggered.
- debug-artefacts
	Check for workflow that upload artefacts.
- debug-js-exec
	Check for workflow that execute system commands in JS scripts.
- debug-oidc-action
	Check for OIDC actions.
- repo-jacking
	Verify that external actions are pointing to a valid GitHub user or organization.
workflow_run 또는 pull_request_target과 같은 트리거는 시크릿에 대한 읽기 권한이 있고 대상 저장소에 대한 쓰기 권한을 가질 수 있으므로 권한이 있는 컨텍스트에서 실행됩니다. 신뢰할 수 없는 코드에 대해 명시적 체크아웃을 수행하면 해당 컨텍스트에서 공격자 코드가 다운로드됩니다.

actions/checkout v7부터 이 액션은 pull_request_target 및 workflow_run 워크플로에서 포크 PR 코드를 가져오는 것을 거부합니다(이 보호 기능은 SHA, 마이너 또는 패치 핀에는 적용되지 않고, 플로팅 메이저 태그 v2 이상에 백포트되었습니다). 이 규칙은 다음을 보고합니다:
ref 또는 PR의 헤드 저장소인 repository를 사용한 체크아웃을 보고하며, 권한이 있는 이벤트의 경우 고정된 버전에 이 보호 기능이 있는지 알려줍니다;allow-unsafe-pr-checkout을 보고합니다: 이는 의도적인 옵트아웃이므로 주의 깊게 살펴보세요.스크립트(git, gh pr checkout) 및 기타 이벤트(issue_comment...)에 의해 수행되는 체크는 이 보호 기능의 적용을 받지 않습니다.
이 규칙은 위험한 액션이 사용될 경우 사용자에게 경고합니다. 주로 신뢰할 수 없는 아티팩트에 초점을 맞춥니다.






