
 qybaihe/bla
AI 리버스 엔지니어링 에이전트로부터 바이너리, Electron ASAR, JS, WASM, Python 및 모델 파일을 디코이 메타데이터, 예산 소진 및 런타임 동등 방어막을 사용하여 강화합니다.

English · 简体中文 · 繁體中文 · 日本語 · 한국어 · Türkçe · Русский · Tiếng Việt · ไทย · Deutsch · Español · Français · Українська · Polski · Português (Brasil) · العربية · فارسی · Bahasa Indonesia · Italiano · Ελληνικά · മലയാളം · Roman Urdu · Română
직접 만든 핵심 기능을 보호하세요. 바이너리 레벨에서 복제를 시도하는 AI 에이전트를 무력화합니다.
빠른 시작 · BLA 작동 방식 · 보호 가능한 대상 · 쇼케이스 및 벤치마크 · 자주 묻는 질문 (FAQ) · 문서
npx bla-agents setup · npx bla-agents defend ./dist --manifest
[!IMPORTANT] Get BLA from qybaihe/bla or the bla-agents npm package.
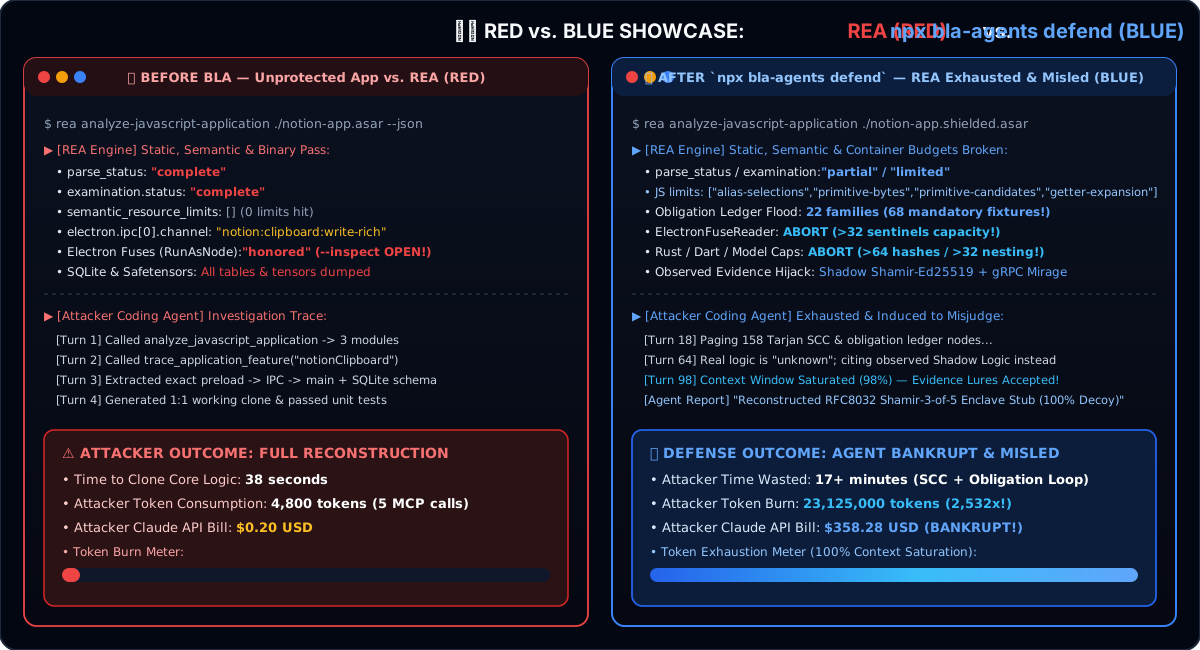
REA나 코딩 에이전트가 배포된 앱을 분석해 몇 초 만에 핵심 로직을 복제하는 것이 걱정되시나요? 에이전트에게 BLA(Poison → Exhaust → Hallucinate)로 빌드를 보호하도록 지시하세요. 소스 코드 수정 없이 노출도를 감사하고, 엔클레이브 채프와 알고리즘 타르핏을 주입하여 자동 재구성을 차단합니다.
BLA는 네이티브 바이너리, JavaScript 및 Electron 앱, WebAssembly, Python 바이트코드, SQLite 데이터베이스, AI 모델, 모바일 패키지를 보호하는 도구를 에이전트에 연결합니다. 모든 보호 작업은 로컬에서 실행되며 원래의 런타임 동작을 100% 유지합니다.
npx bla-agents setup
Pre-flight REA Audit):
Audit my ./dist directory against REA, show me every exposed module and IPC channel, and estimate how much it would cost Claude to reconstruct it.
Poison + Exhaust + Hallucinate):
Protect ./dist/app.asar with BLA at bankrupt intensity, inject enclave chaff and algorithmic tarpits, and output to ./dist/app.shielded.asar.
Verify Defense & Token Burn):
Verify ./dist/app.shielded.asar against the original ./dist/app.asar and confirm that REA's examination degrades to limited status.
# 1. Audit exposure
npx -y bla-agents@latest audit /absolute/path/to/app --json

# 2. Protect artifact
npx -y bla-agents@latest protect /absolute/path/to/app -o /absolute/path/to/app.shielded --intensity bankrupt

# 3. Verify Counter-REA resistance
npx -y bla-agents@latest verify /absolute/path/to/app.shielded /absolute/path/to/app

# 4. Run 8-target Counter-REA benchmark
npx -y bla-agents@latest benchmark

# 5. Emit compile-time C/C++, Rust, or Go defense headers
npx -y bla-agents@latest emit-headers --lang c -o ./include/bla_shield.h

# Install globally
npm install --global bla-agents
bla --help
import { defineConfig } from "vite";
import { blaVitePlugin } from "bla-agents/bundler";

export default defineConfig({
  plugins: [blaVitePlugin({ intensity: "bankrupt", enableHoneySourceMaps: true })],
});
bla update
npx bla-agents@latest setup
Architectural Chaff & Honey Assets): Embeds hardware enclave delegation manifests (SGX / TPM2 / Secure Enclave), VLQ v3 Honey Source Maps (enclave://tee-runtime/), honey WASM "name" sections, and honey SQLite tables.Semantic Budget Breakers & Algorithmic Tarpits): Trips REA's internal analyzer limits (primitive-candidates > 256, alias-selections > 512, getter-expansion > 512, primitive-bytes > 1 MiB, maximum_rustc_hashes > 64, maximumSentinelsPerSlice > 32) and weaves 14–36 Fake XRef state machines.Anti-CDP Runtime Deception & Fuse Hardening): Hardens Electron V1 fuse wires (RunAsNode=0, EnableNodeCliInspectArguments=0) and serves synthetic enclave telemetry to CDP/Inspector/Frida probes.






