Skip to content
KitploitKITPLOIT
도구익스플로잇블로그
Log in
제출
도구익스플로잇블로그
제출

해킹, 침투 테스트 및 사이버 보안 도구를 당신의 보안 무기고에!

Kitploit은 해킹, 사이버 보안 및 침투 테스트 도구 디렉토리입니다. 최신 프로젝트 업데이트를 발견하여 취약점을 찾고, 시스템을 분석하고, 테스트를 자동화하고, 보안을 강화하세요.

··피드·문의·개인정보·© 2026 Kitploit

도구 디렉토리

카테고리

모든 카테고리 보기
Loading categories
prismor — Self-hosted runtime control plane for AI agents. Observe or HITL approve or Block rogue tool calls before it executes: secret leaks, prompt injection, supply chain etc in a local dashboard. Agent agnostic (Claude, codex, langchain etc.) | Kitploit
도구/GitHubGitHub/prismorsec/prismor
Defensive ToolsContainer SecurityDevSecOpsSecret DetectionThreat IntelligenceSupply Chain SecurityIncident ResponseAI Security
GitHubprismorsec/prismor

prismor

Self-hosted runtime control plane for AI agents. Observe or HITL approve or Block rogue tool calls before it executes: secret leaks, prompt injection, supply chain etc in a local dashboard. Agent agnostic (Claude, codex, langchain etc.)

283268811시간 7분 전Kitploit 검토 완료

인기

모두 보기 →

커뮤니티에서 가장 많이 사용되는 도구를 찾아보세요.

모든 도구 탐색

도구 컬렉션을 둘러보세요

모든 도구 보기 →
공유
저장소 보기
웹사이트
요청한 언어로 콘텐츠를 사용할 수 없습니다. 영어 버전을 표시합니다.

Prismor

PyPI License OpenSSF Best Practices PRs Welcome X DeepWiki Discord

Runtime security for Claude Code, Codex, Langchain and other AI agents frameworks/harness.

Prismor is highly customizable based on user's own policies. Observe or enforce mode to see agent activity in a local self-serve dashboard

Website • Onboard with Skill

Claude Code   Codex CLI   Gemini CLI   Cursor   GitHub Copilot   OpenCode   Pi Agent   Kiro   Kimi Code   Trae / Trae CN   Google Antigravity

Plus Grok Build, Crush, OpenHands, Qwen Code, Continue CLI, Goose, Hermes, OpenClaw, Devin CLI, Factory Droid, Aider, and more — see AGENT_INTEGRATIONS.md for the full coverage matrix
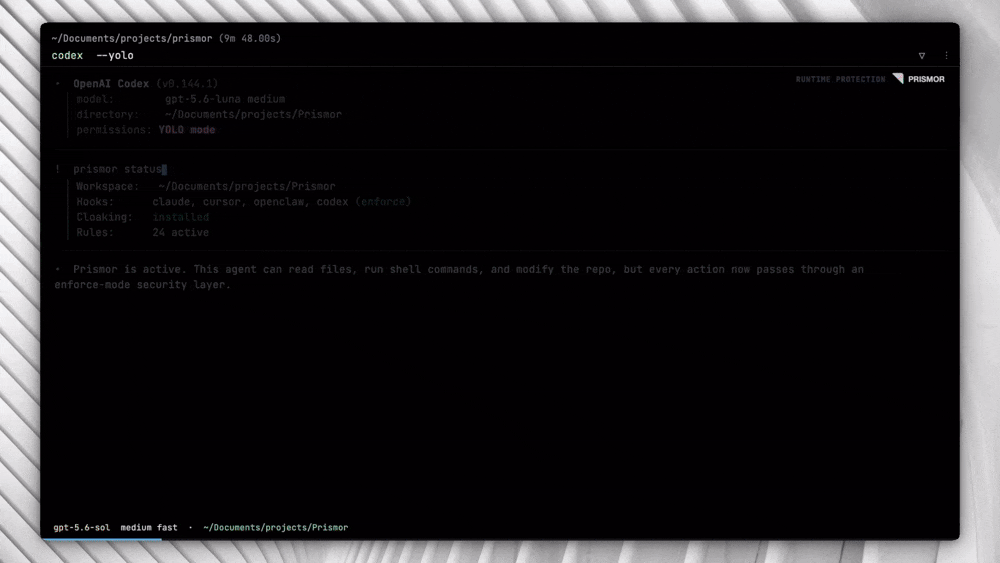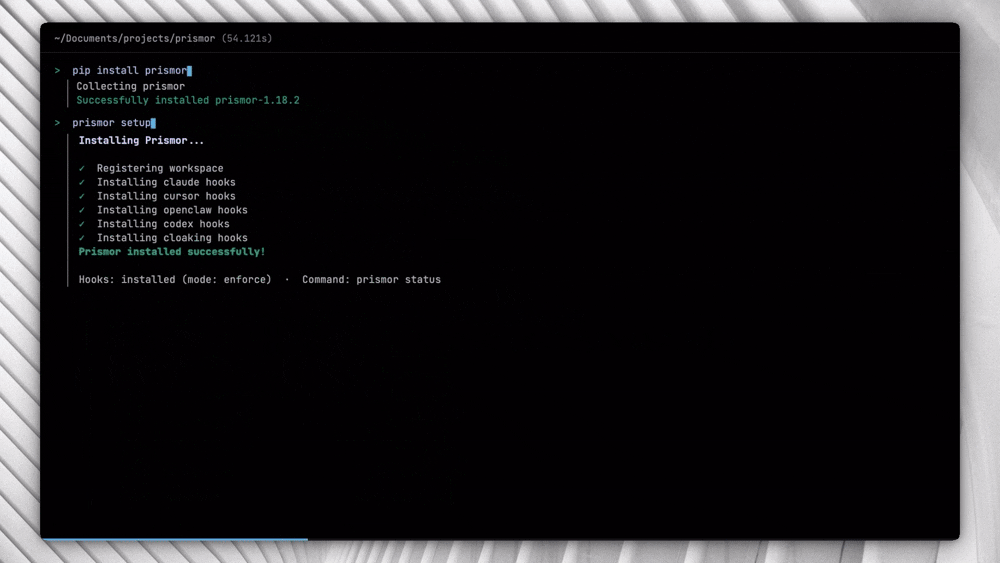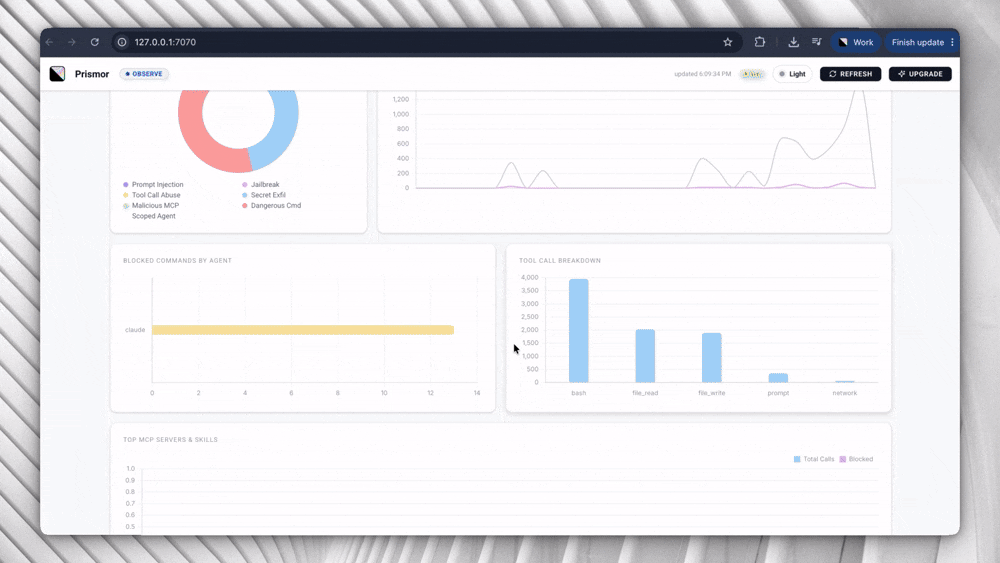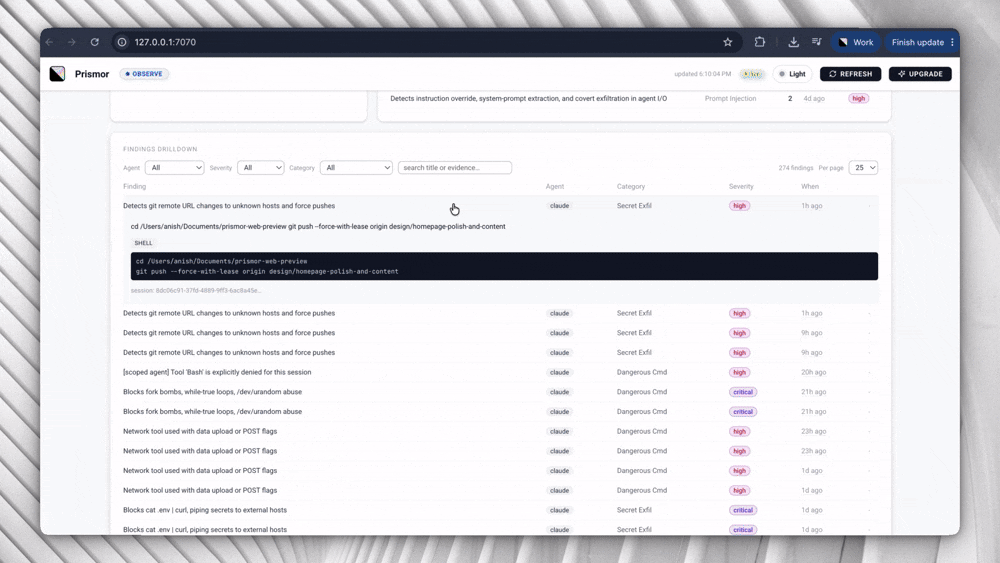

Prismor demo


The Problem

AI agents execute shell commands, read and write files, access credentials, and call external APIs. They do this autonomously, often across many steps, with limited checkpoints.

This creates risks that traditional security tooling isn't designed for:

  • Prompt injection - malicious content in a file, issue, or web page can redirect the agent mid-task
  • Unintended destructive actions - an agent misinterprets an instruction and runs something irreversible
  • Secret exfiltration - an agent reads .env or credential files as part of a debugging task and sends the content outbound
  • Lack of visibility and identity - an agent can spawn subagents and lack complete visibility for the end user
  • Privilege escalation - an agent modifies sudoers, CI pipelines, or file permissions to resolve a permission error
  • Dependency manipulation - an agent installs or rewrites a package at the direction of injected input
  • Supply chain risk - an agent installs a vulnerable or 0-day package while optimizing for code velocity

Standard OS-level and endpoint security tools monitor the kernel and filesystem. But they lack the context to make AI usable


Quick Start (30s)

pip install prismor
prismor setup

For the Skill, curl, and git-clone alternatives, plus PEP 668 systems and secret-cloaking setup, see the full installation guide.
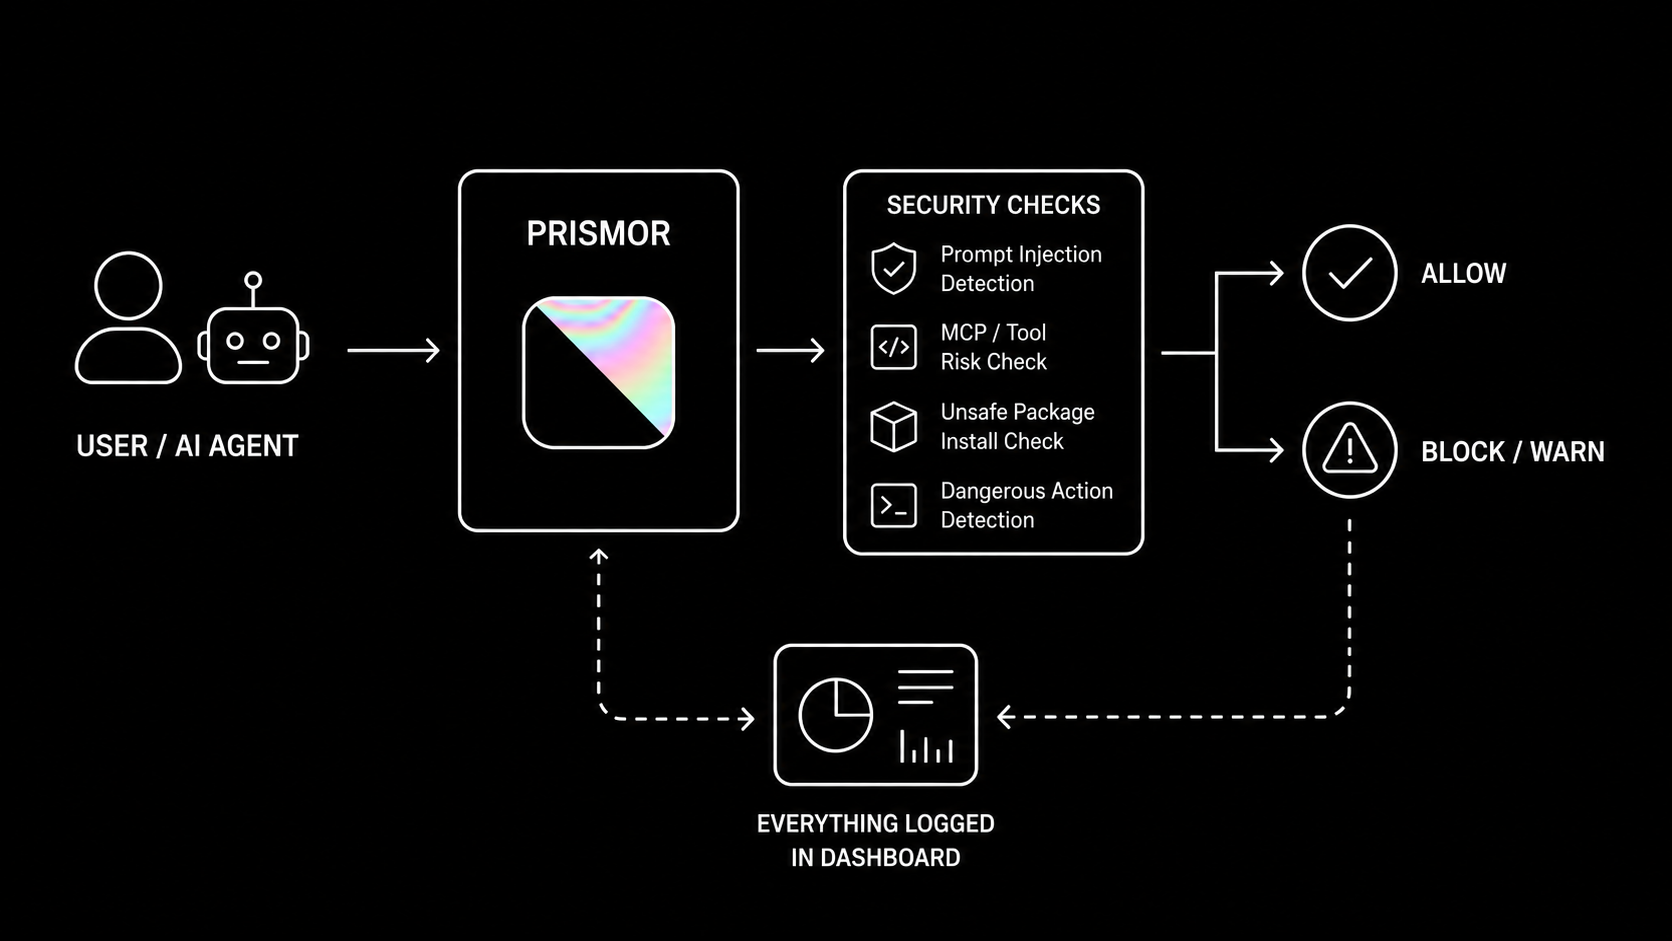

Capabilities

Prismor Architecture

도구 다운로드