

 pennacle-security/summit
오픈소스 웹 보안 테스트 플랫폼: 프록시, 스캐너, 퍼저를 하나의 CLI로 제공. Pennacle Security 제작.


웹 보안 테스트를 위한 하나의 스크립트 가능한 CLI: 스캐너, 프록시, 퍼저, 인가 테스트, WAF 분석, 링크 하이재킹 탐지 및 정찰.
동등한 기능이 유료인 곳에서 무료 - Pennacle Security 제공.
우리는 매일 Burp와 ZAP을 사용합니다. 또한 그들이 아닌 세 가지를 계속 원했습니다: CI에서 스크립트로 제어할 수 있는 스캐너, 얼마나 확실한지 알려주는 발견 사항, 그리고 한 번에 읽을 수 있을 만큼 작은 코드베이스. Summit이 바로 그 도구입니다 - v0.5, MIT, 의존성 하나(requests), 공개적으로 개발.
전체 문서: pennacle-security.github.io/summit
일반적으로 유료 도구 뒤에 숨어 있는 기능과 스캐닝 핵심:
| 기능 | Summit | 일반적인 방법 |
|---|---|---|
| 접근 제어 취약점 테스트 (BOLA/IDOR) | summit authorize | Autorize 스타일 애드온 / 유료 워크플로 |
| 숨겨진 파라미터 발견 | summit mine | Param Miner 스타일 애드온 |
| OpenAPI 기반 스캐닝 | summit scan --openapi | 애드온 |
| WAF 핑거프린팅 + 우회 탐색 | 내장 | 부분적 / 애드온 |
| 끊어진 링크 하이재킹 탐지 | 내장 | 유료 확장 |
| SQLi, XSS, 리다이렉트, 트래버설, 테이크오버, 호스트 헤더, CORS | 내장 | 핵심 스캐너 (무료) |
| 정찰 체인: subfinder -> httpx -> nmap | summit recon | 수동 연결 |
| 속도 제한, 재시도, JWT/인코더 툴킷 | 내장 | 애드온 / 유료 |
| CI 지원, 신뢰도 라벨이 붙은 발견 사항 | 핵심 목표 | 유료 자동화 |
모든 발견 사항에는 신뢰도 라벨이 붙습니다: confirmed (관찰된 사실) 또는 potential (휴리스틱). 이 구분은 도구 전체에 걸쳐 적용됩니다.
git clone https://github.com/pennacle-security/summit.git
cd summit
pip install -e .
Python 3.10+. 그런 다음 의도적으로 취약하게 만든 로컬 타깃을 대상으로 동작하는 모습을 확인하세요:
python examples/vuln_app.py        # terminal 1 - the target (127.0.0.1 only)
summit scan http://127.0.0.1:8765  # terminal 2 - the scan
실제 참여에 대한 더 완전한 패스는 다음과 같습니다:
summit recon target.com --json recon.json                 # subdomains -> hosts -> ports
summit scan https://target.com --depth 2 --rate 10        # crawl + all checks
summit scan --openapi api-spec.json                       # API: scan what the spec admits to
summit authorize https://target.com/admin?user=1 \
  --role 'admin=Cookie: session=abc' \
  --role 'user=Cookie: session=xyz'                       # BOLA/IDOR testing
이 페이지의 모든 주장은 examples/evidence.py로 재현됩니다. 이 스크립트는 데모 대상을 실제로 실행하고, 각 기능을 측정하며, 실제 수치와 함께 PASS/FAIL을 출력합니다. CI는 매 푸시마다 이를 실행하며, 더 이상 성립하지 않는 주장이 있으면 빌드가 실패합니다.
python examples/evidence.py)[PASS] full scan: 16 seeded check families detected, zero false positives
53 findings in 22.9s (344 requests), missing=none, control link flagged=no, 19 finding(s) carry confidence=confirmed
[PASS] resource takeover fingerprint detected on the target's own 404
Possible AWS S3 resource takeover | AWS S3: 'nosuchbucket'
[PASS] host header injection: marker domain echoed back by the app
Host: summit-host-probe.example -> reflected (reset-link poisoning surface)
[PASS] CORS reflects an arbitrary origin with credentials allowed
ACAO: https://summit-cors-probe.example; ACAC: true
[PASS] WAF bypass: naive filter blocks, tampered payload lands decoded
raw payload -> HTTP 403 (blocked); URL-encoded once -> HTTP 200, payload reflected decoded: True
[PASS] CAPTCHA challenge detected (reported, not solved)
/login -> reCAPTCHA via marker 'recaptcha/api.js'
[PASS] rate limiting: --rate 5 paces 12 requests to ~2.2s; unlimited runs free
12 requests at rate 5 -> 2.20s (theoretical floor: 2.2s); 12 requests unlimited -> 0.02s
[PASS] concurrency on a latency-bearing target: 8 workers vs serial
40 requests x 25ms latency: serial 1.33s -> parallel 0.18s (7.3x speedup)
[PASS] smart prioritizer ranks known-injectable parameters first
probing starts with: [('query', 'search?query=laptop'), ('id', 'user?id=1'), ('url', 'example.com')]
[PASS] toolkit decodes JWT header/payload and states the signature is unverified
signature NOT verified - decoding only
[PASS] update check compares versions numerically (0.3 < 0.10)
is_outdated('0.3.0', '0.10.0') -> True; is_outdated('1.0.0', '0.9.9') -> False
[PASS] broken access control: admin panel served identically to a low-privilege role
verdict=broken; finding=Broken access control (BOLA/IDOR candidate)
[PASS] hidden parameter mining finds the undocumented debug parameter, zero noise
1 finding(s): ['debug'] (all confirmed reflections)
[PASS] openapi-driven scan: spec alone leads the engine to seeded SQLi and XSS
2 spec target(s) scanned -> 10 findings, sqli-error=yes, xss-reflection=yes
[PASS] OS command injection: marker executed and echoed by the server
semicolon: exec marker x2, control marker x1 | CWE-78
[PASS] server-side template injection: {{7*7}} came back as 49
Jinja2/Twig: {{7*7}} -> 49 | CWE-1336
[PASS] CRLF injection: X-Summit-CRLF header materialized in the response
X-Summit-CRLF: injected | CWE-113
[PASS] sensitive file exposure: /.env confirmed by content signature
content signature: 'APP_KEY=' | CWE-538
[PASS] CVE detection: Apache/2.4.49 banner maps to known CVEs
detect_cves('Apache/2.4.49') -> ['CVE-2021-41773', 'CVE-2021-42013']
evidence summary: 19/19 claims verified
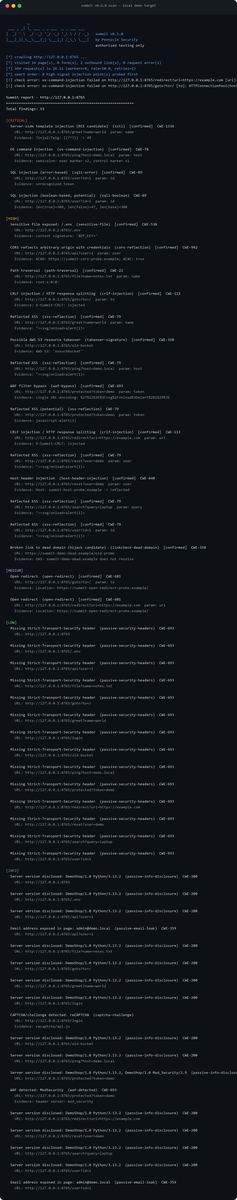
데모 대상에 대한 실제 스캔 시각 자료:
모든 것을 직접 재현하기:
python examples/vuln_app.py    # terminal 1 - the target
summit scan http://127.0.0.1:8765
python examples/evidence.py    # re-verify every claim above
데모는 정상적인 아웃바운드 링크(https://example.com)를 음성 대조군으로 시드합니다. 이 링크는 절대 보고되어서는 안 되며, CI는 시드된 탐지 결과와 함께 이를 검증합니다. 그래도 뭔가 잘못된 점을 발견하셨나요? 보고해 주세요.
