ConfluenceMemshell
Confluence CVE 2021, 2022, 2023 활용 도구, 명령 실행, Godzilla, Behinder 메모리 셸 주입 지원
- 지원 Confluence 버전: CVE-2021-26084, CVE-2022-26134, CVE_2023_22515, CVE-2023-22527
- (도움이 되셨다면, 괜찮다고 느끼셨다면, 큰 ⭐️를 눌러주세요❗️)
- Godzilla 기본 비밀번호: pass, 기본 key: key, 요청 구성 - 프로토콜 헤더에
Connection: close를 추가해야 합니다
- Behinder 기본 비밀번호: rebeyond, 기본 UA: Accept-Language:zh-CN,zh;q=0.95,n-AS,fr-RF
- CVE-2022-26134 버전만 Godzilla, Behinder 사용자 지정 비밀번호를 지원하며, 다른 버전은 모두 기본 비밀번호입니다
V1.1 버전
- CVE_2023_22515 추가, 사용자 생성, 메모리 셸 주입, CmdShell 기반 명령 실행
- table 더블 클릭으로 현재 행, shell 경로, key, ua 복사
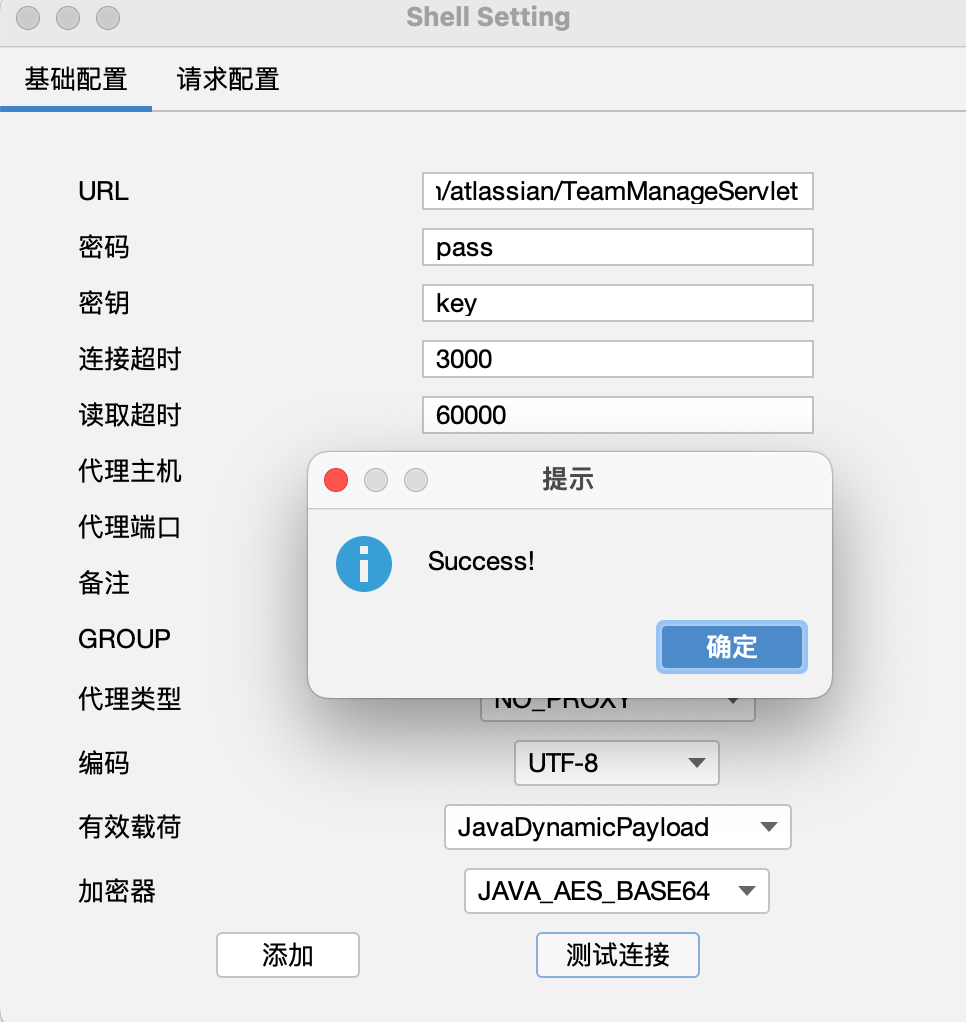
- Godzilla memshell 주소: url+/plugins/servlet/com/atlassian/TeamManageServlet
- Godzilla 기본 비밀번호: pass, 기본 key: key, 요청 구성 - 프로토콜 헤더에
Connection: close 추가 필요
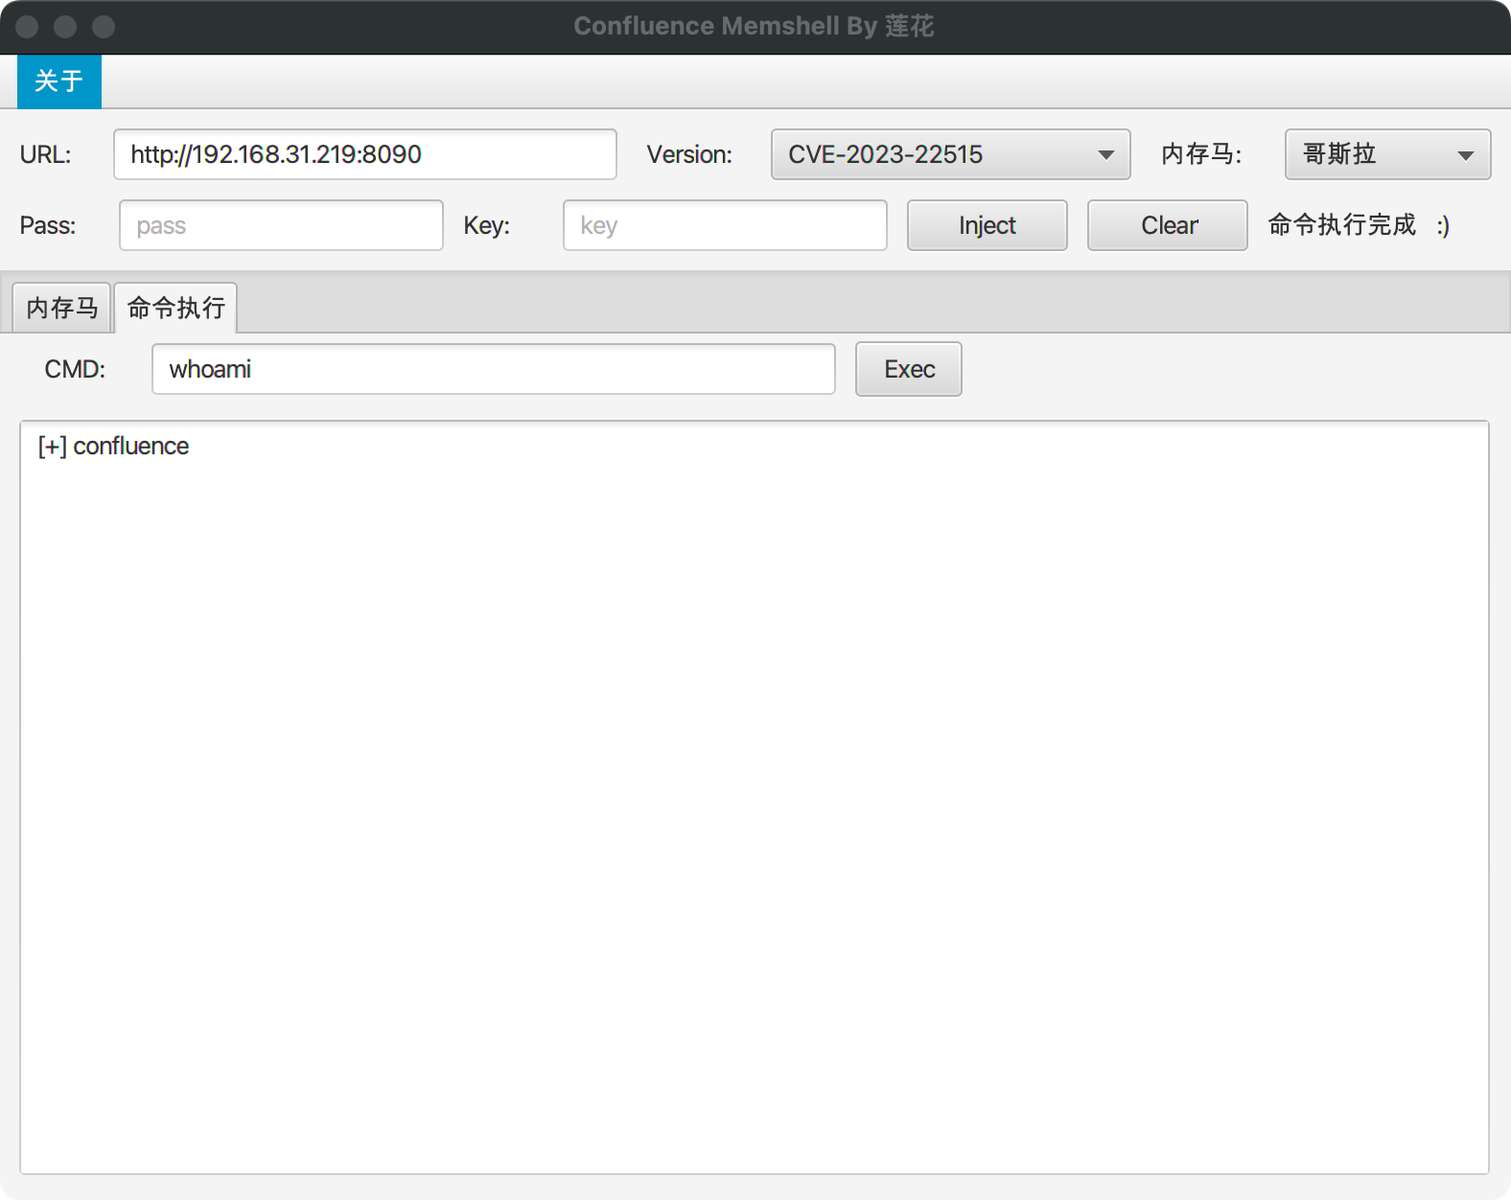
- CmdShell 주소: url+/plugins/servlet/com/atlassian/TeamManageServlet?team=whoami
- 사용자 생성
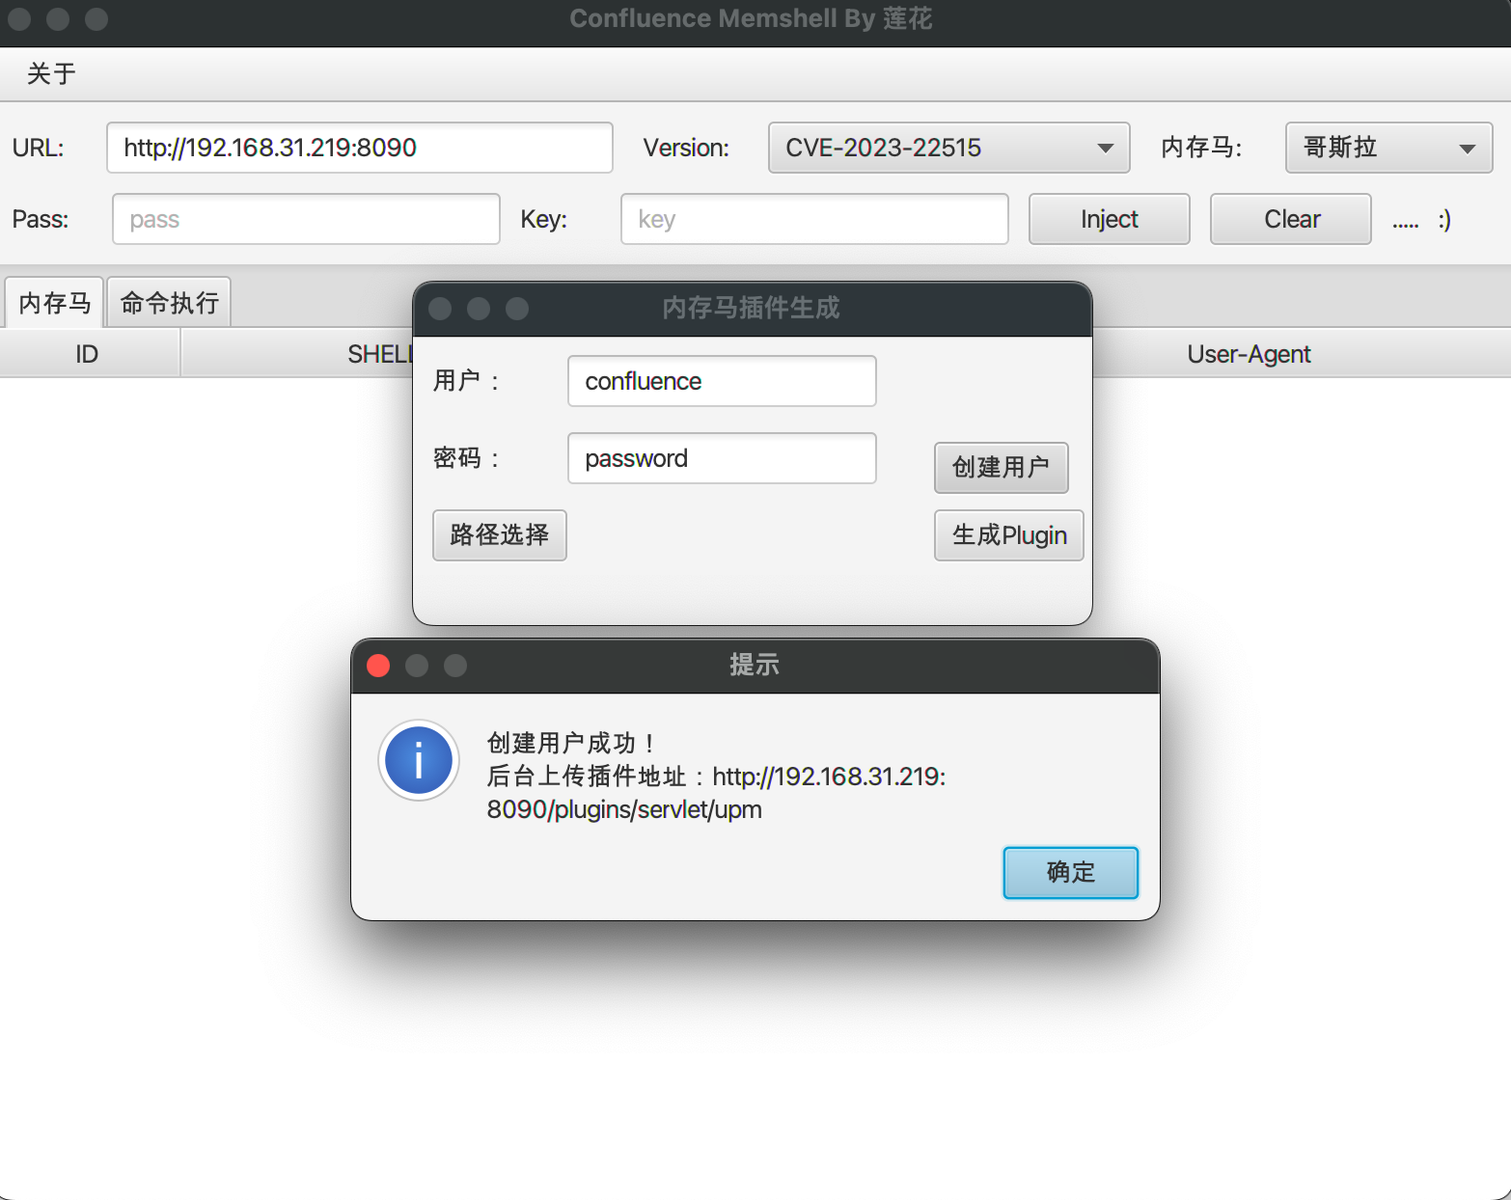
- 생성 성공
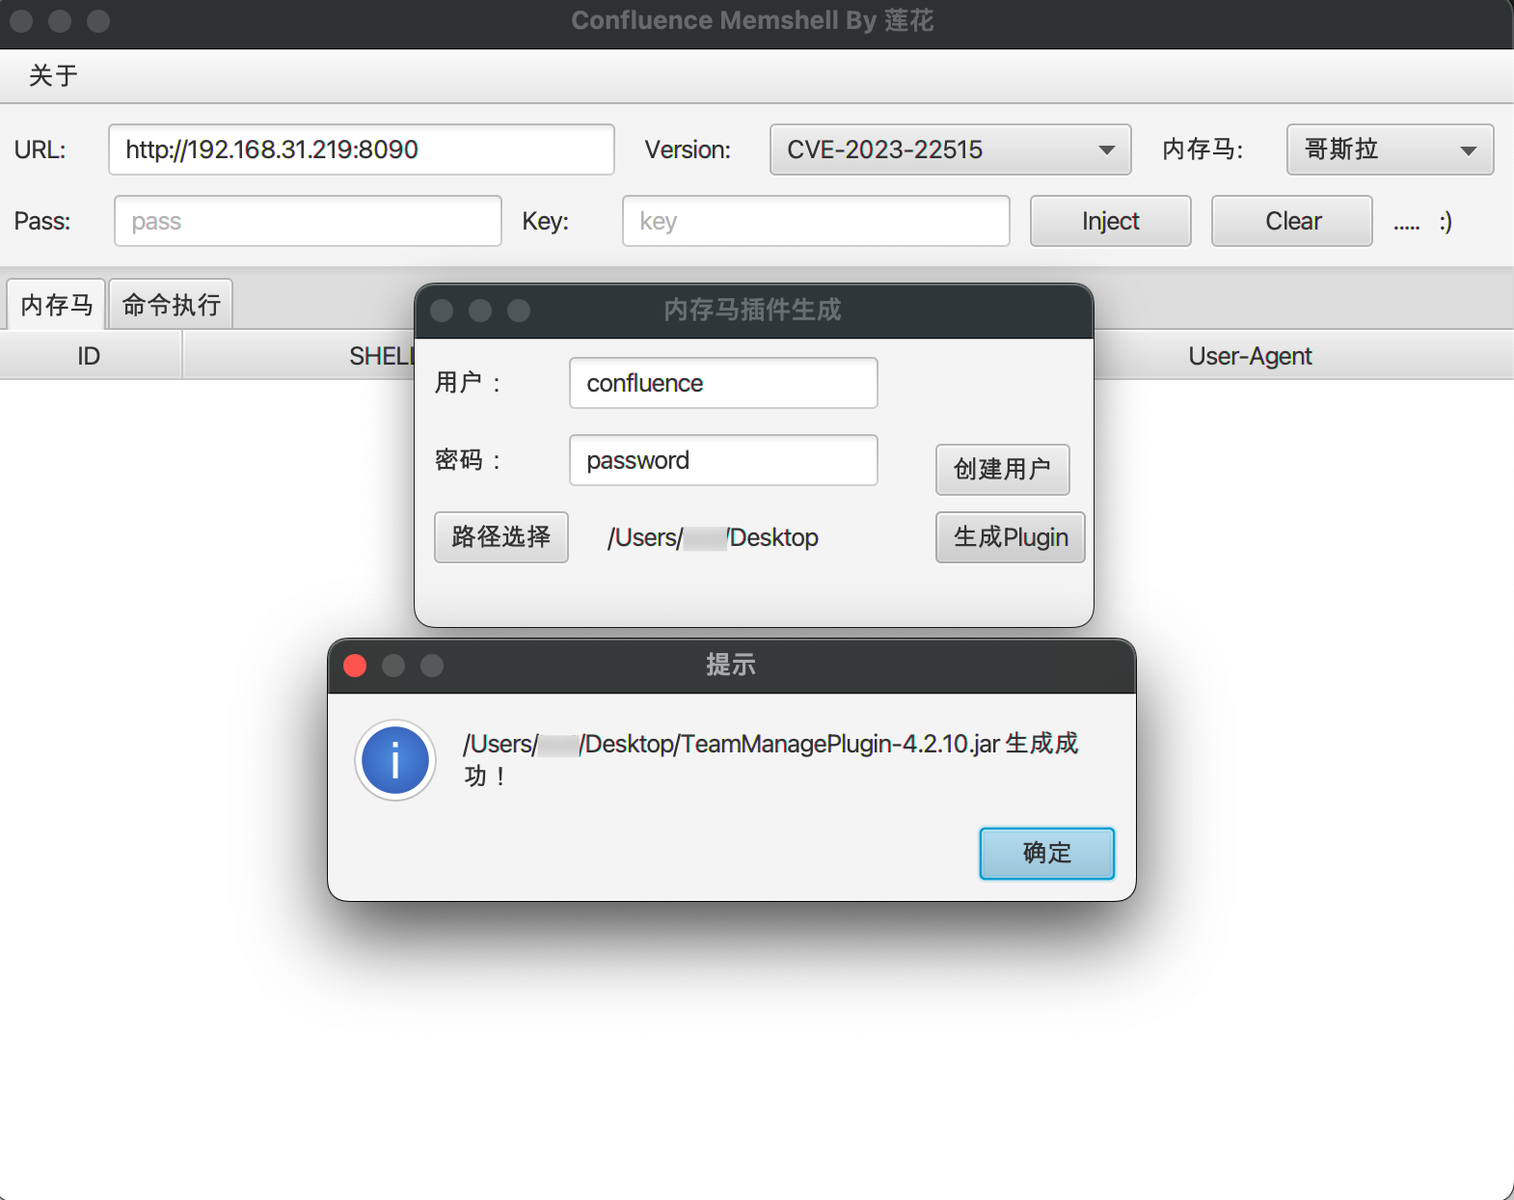
- 악성 플러그인 Jar 패키지 생성 (Godzilla 및 CmdShell 포함)
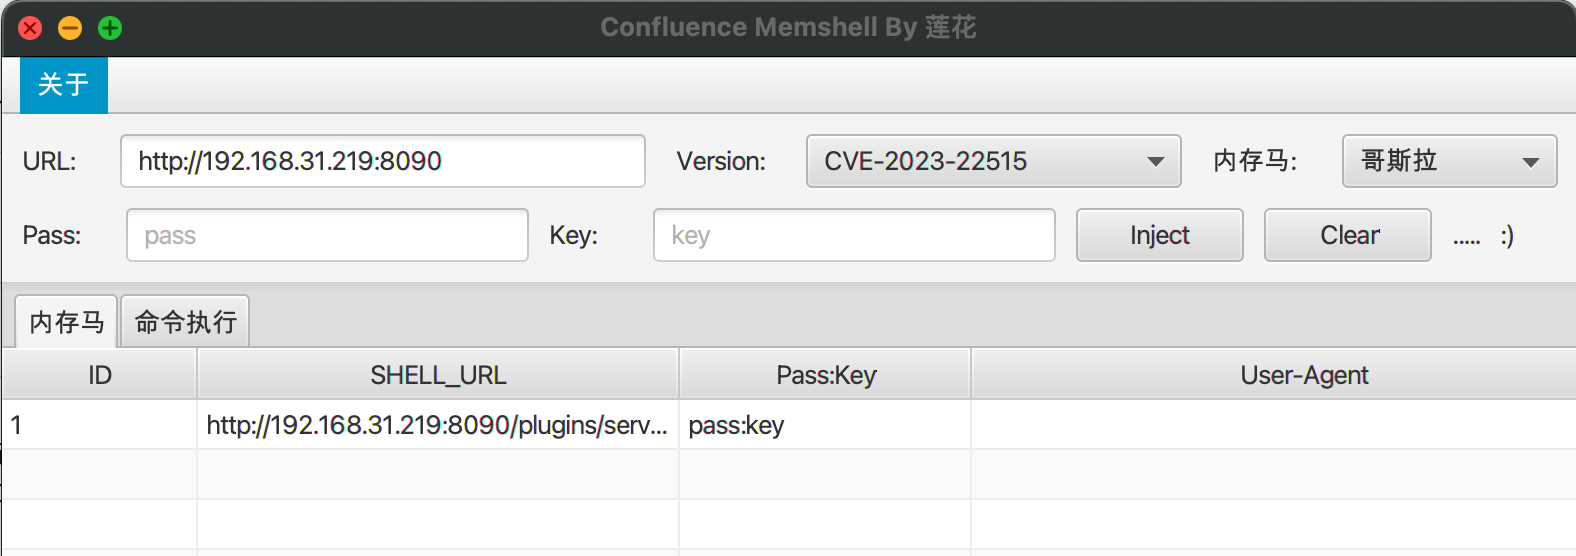
- 메모리 셸 주소 및 pass:key 표시 (더블 클릭하여 복사, shell 경로, key, ua)
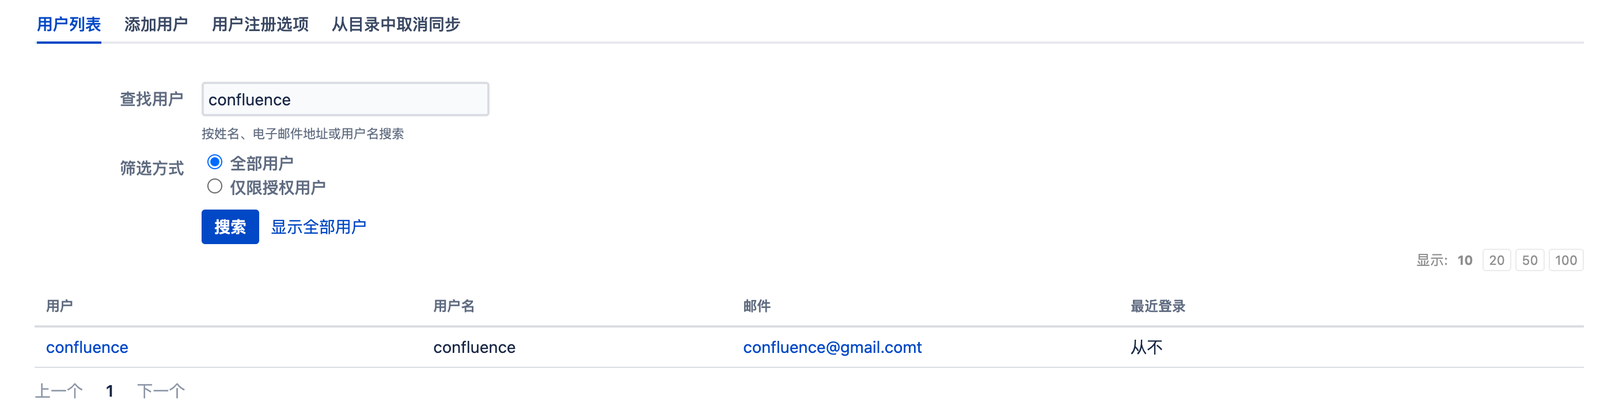
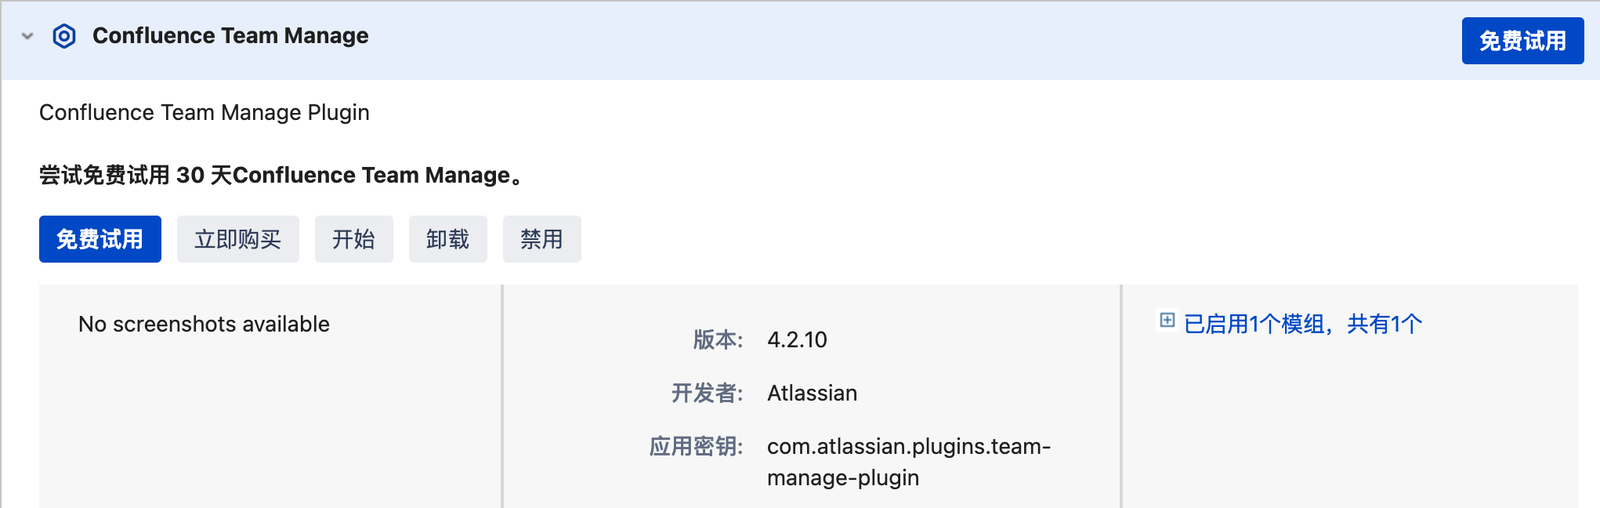
- 생성한 사용자로 백엔드에 접속한 후, 플러그인 기능 주소: url+/plugins/servlet/upm 에서 플러그인을 업로드합니다. (업로드가 완료될 때까지 기다릴 필요 없이 바로 새로고침하면 나타납니다.)
- Godzilla 연결
- 플러그인 CmdShell 기반 명령 실행
V1.0
- 명령 실행 (다른 CVE 버전도 동일)
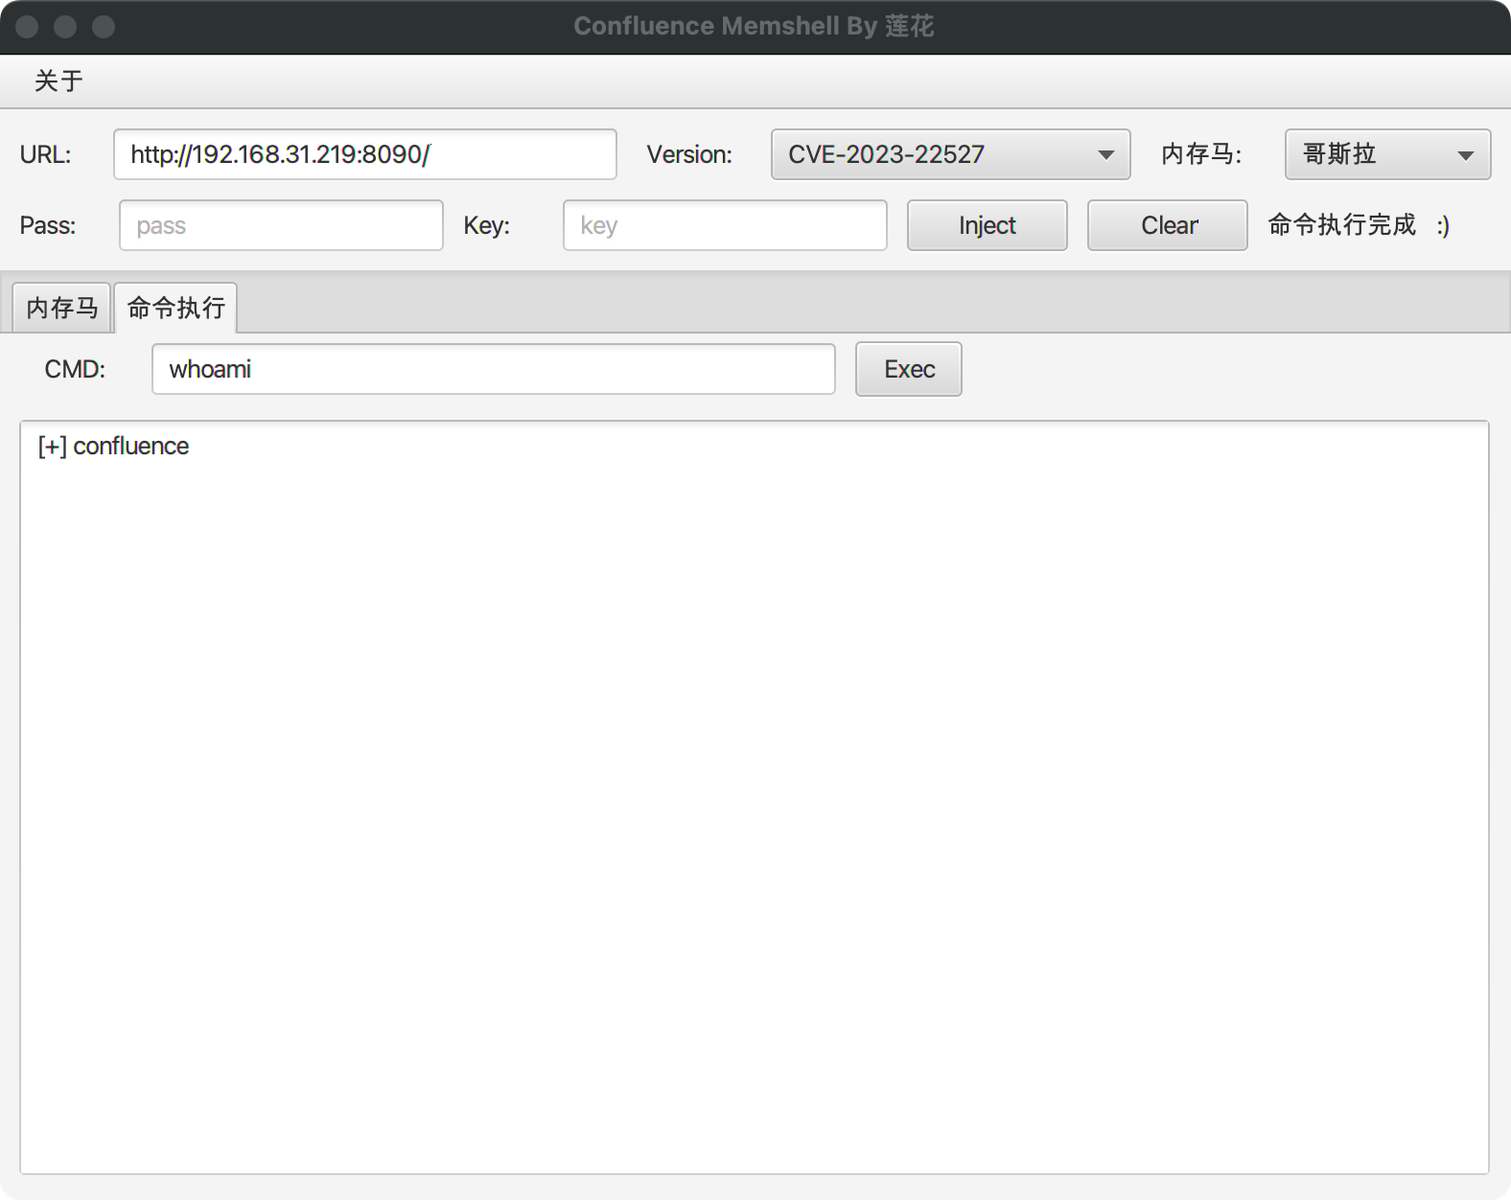
- 메모리 셸 주입 (다른 CVE 버전도 동일)
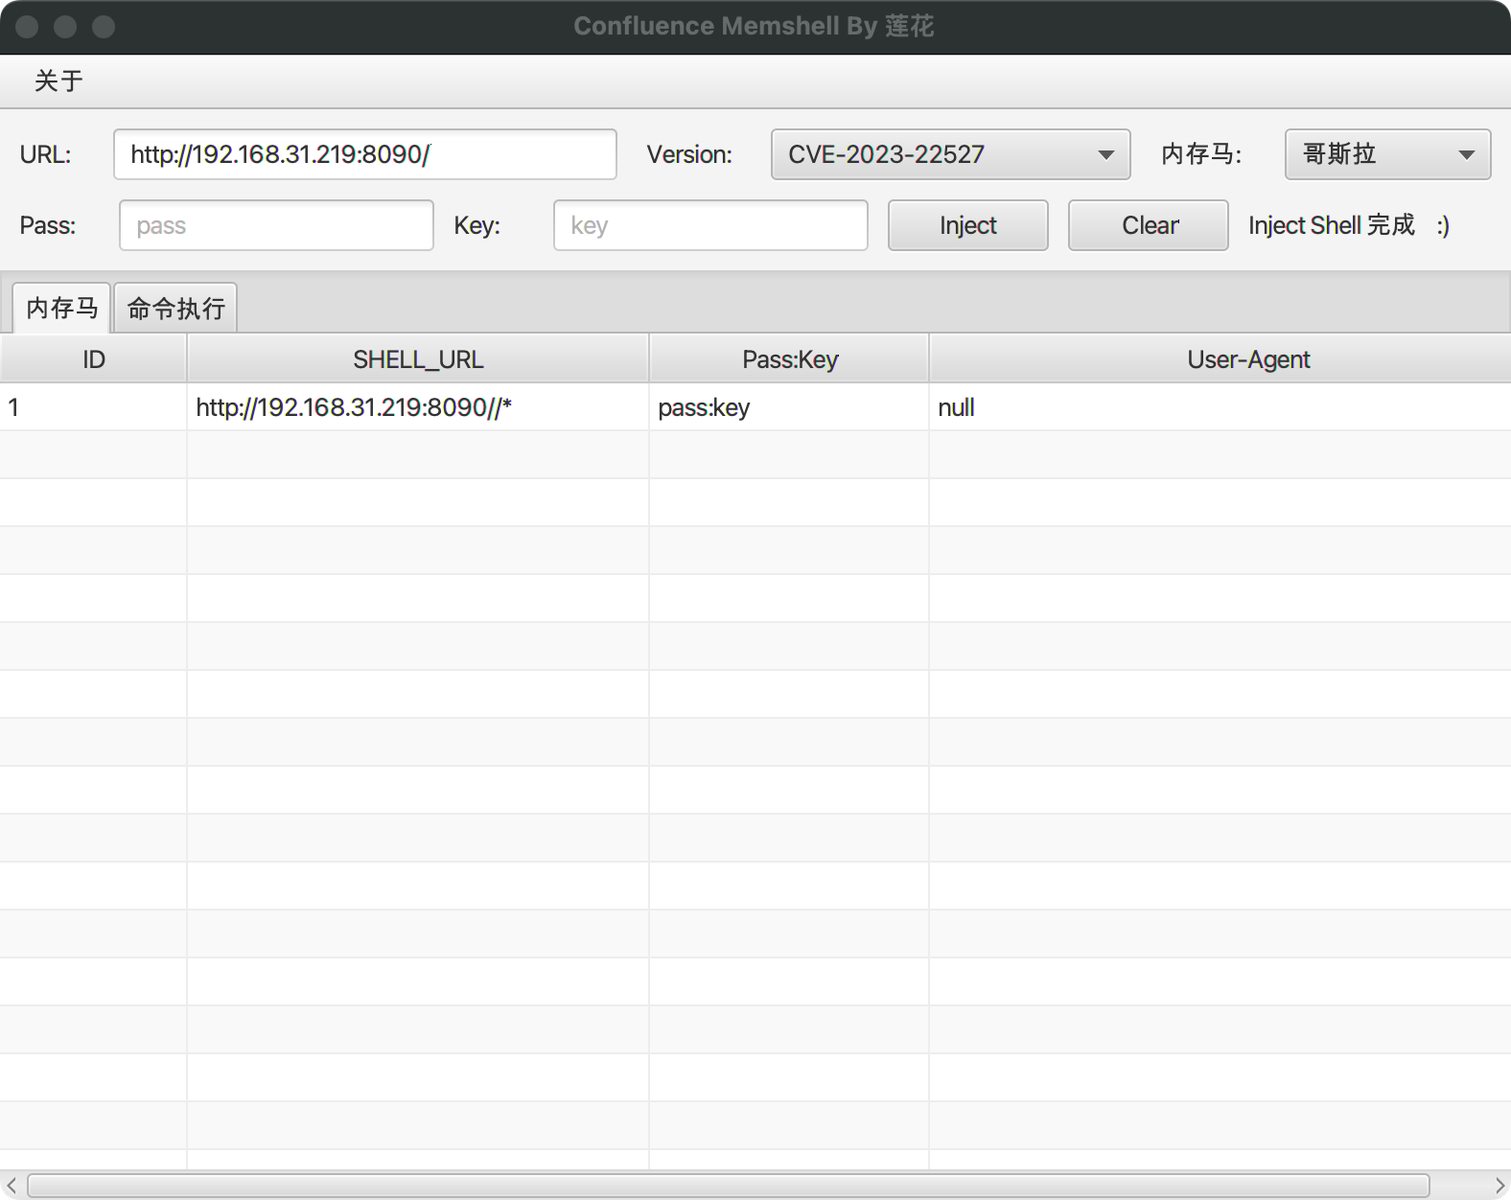
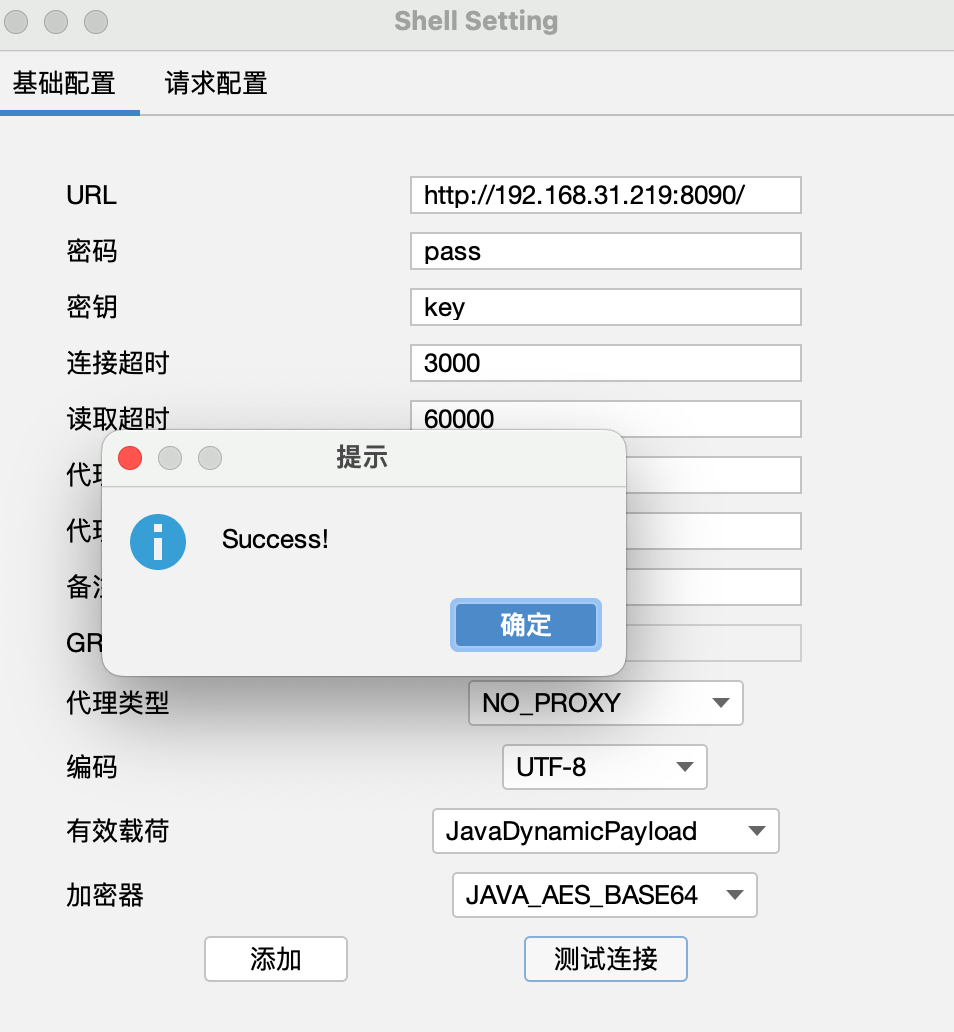
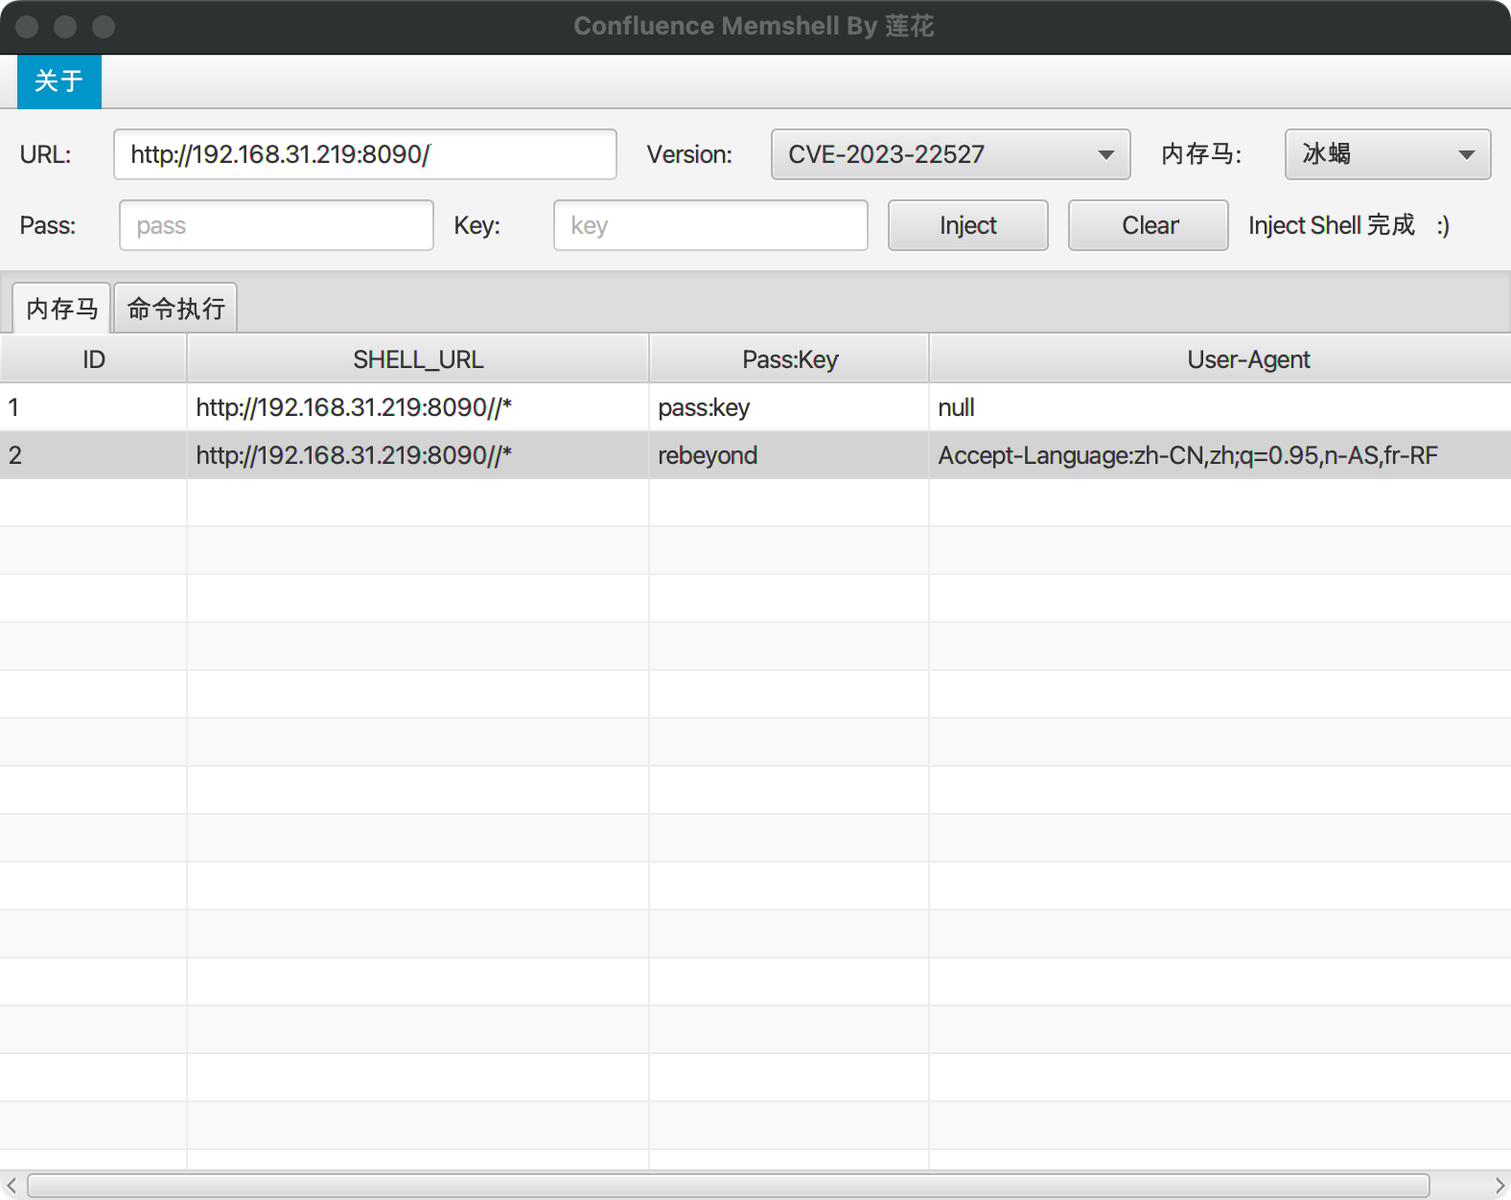
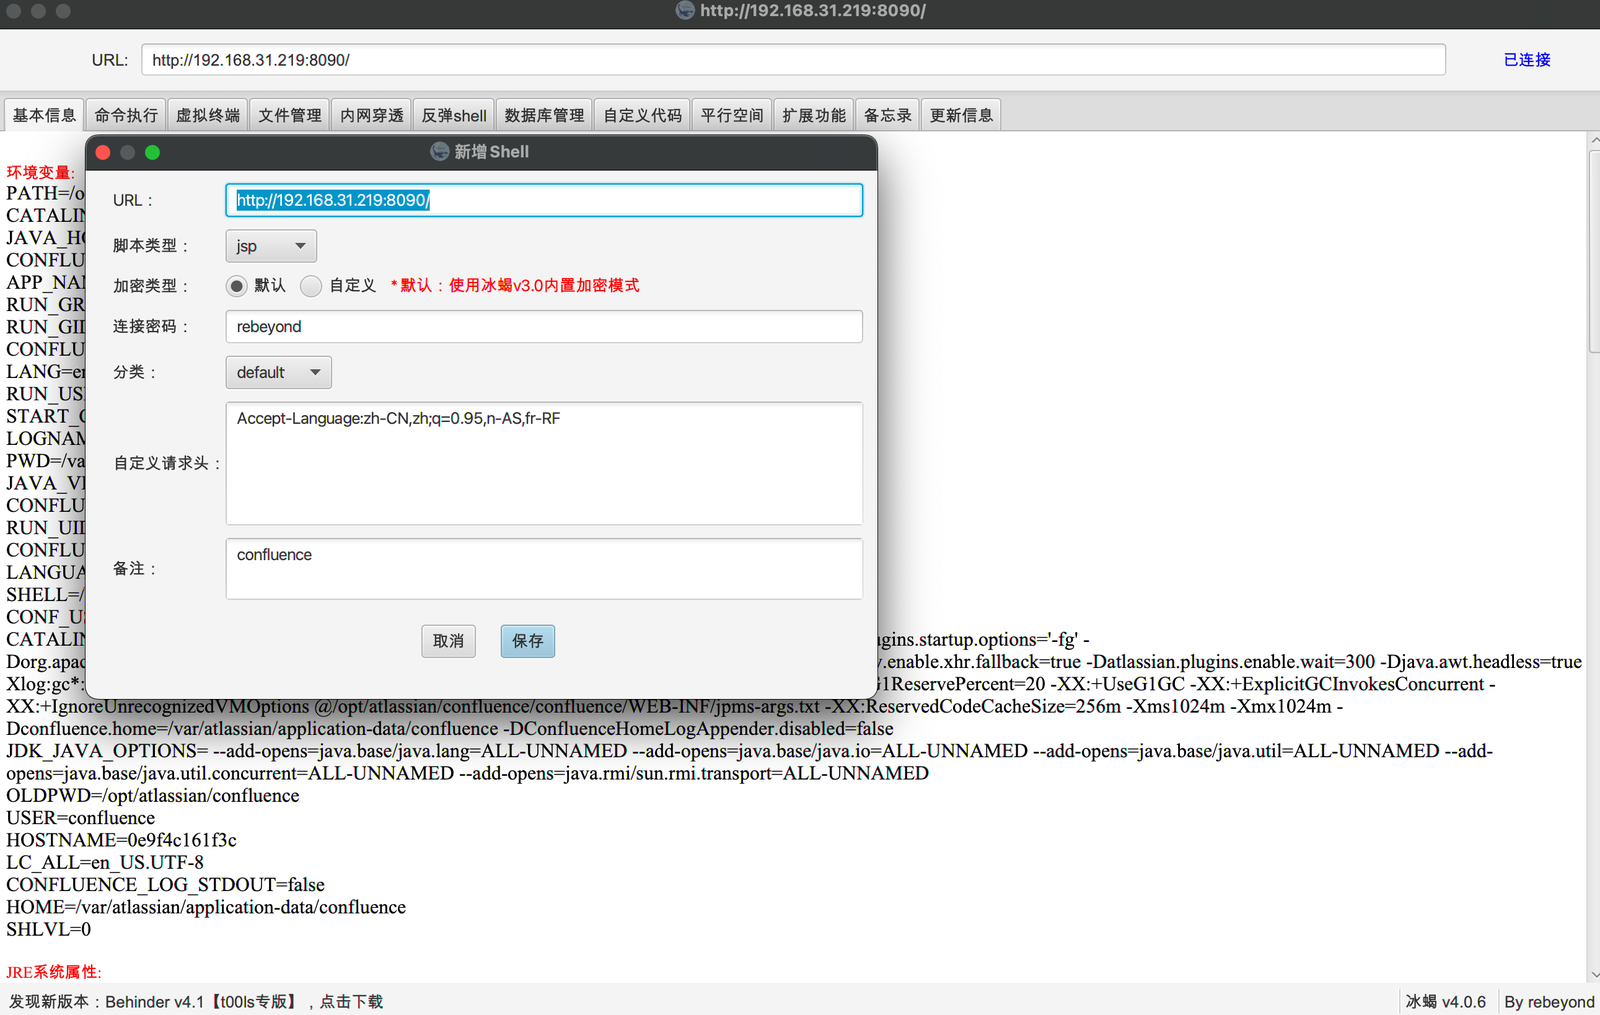
참고
https://github.com/BeichenDream/CVE-2022-26134-Godzilla-MEMSHELL
https://github.com/aaaademo/Confluence-EvilJar
면책 조항
본 도구는 충분한 합법적 권한을 획득한 기업 보안 구축에서만 사용할 수 있으며, 본 도구를 사용하는 과정에서 귀하의 모든 행위가 현지 법률 및 규정을 준수하도록 해야 합니다.
본 도구를 사용하는 과정에서 불법 행위가 존재하는 경우, 모든 결과는 귀하가 직접 부담하며, 본 도구의 모든 개발자와 모든 기여자는 어떠한 법적 및 연대 책임도 지지 않습니다.

 lotus6/confluencememshell

