
 gmh5225/ntstrace
Windows(x64)에서 frida-stalker 기반 시스템 콜 추적기.

Windows(x64)에서 frida-stalker 기반 시스템 호출 추적기.
[483]NtWaitForWorkViaWorkerFactory
test.exe!0x7ff91fbaf262
[35]NtQueryVirtualMemory
test.exe!0x7ff91fbaf262
[35]NtQueryVirtualMemory
test.exe!0x7ff91fbaf262
[35]NtQueryVirtualMemory
test.exe!0x7ff91fbb06d2
[199]NtCreateThreadEx
[+] Following thread 17876
test.exe!0x7ff91fbb06d2
[7]NtDeviceIoControlFile
[+] Unfollowing thread 17876
test.exe!0x7ff91fbaeee2
[7]NtDeviceIoControlFile
test.exe!0x7ff91fbaeee2
[7]NtDeviceIoControlFile
[+] Unfollowing thread 6344
[+] Unfollowing thread 6124
아래 프로젝트처럼 시스템 호출을 은폐하는 유형도 정확하게 식별할 수 있습니다.
https://github.com/passthehashbrowns/hiding-your-syscalls
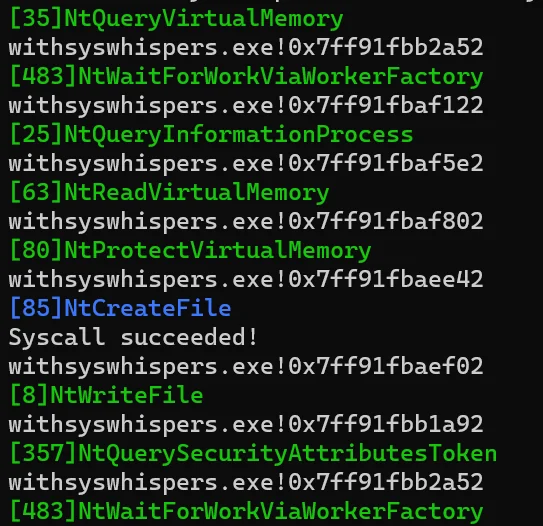
frida -l tracer.js app.exe
원본 소프트웨어는 다음에서 확인할 수 있습니다.
https://github.com/sh1ma/iostrace.
