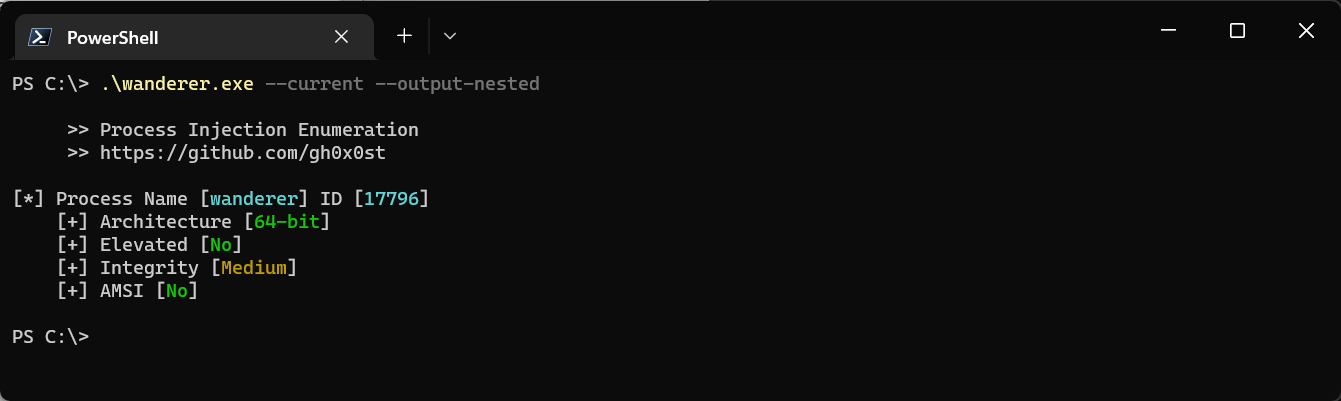

Wanderer는 실행 중인 프로세스에 대한 정보를 수집하는 오픈소스 프로그램입니다. 이 정보에는 무결성 수준, 로드된 모듈로서의 AMSI 존재 여부, 64비트 또는 32비트 실행 여부 및 현재 프로세스의 권한 수준이 포함됩니다. 이 정보는 프로세스 인젝션에 적합한 대상에 맞춰진 페이로드를 구축할 때 매우 유용합니다.
이 프로젝트는 제가 Offensive Security의 PEN-300 과정을 수강하면서 작업하기 시작한 것입니다. 과정에서 가장 마음에 들었던 모듈 중 하나는 프로세스 인젝션 및 마이그레이션 섹션으로, 이 활동을 보다 효율적으로 수행할 수 있도록 도와주는 도구를 만들도록 영감을 주었습니다. 특별히 귀중한 피드백을 제공하고 필터링 기능을 제안하여 이 유틸리티를 시각적으로 매력적으로 만들고 사용성을 향상시키는 창의적인 방향을 제시해준 ShadowKhan에게 감사드립니다.
PS C:\> .\wanderer.exe

     >> Process Injection Enumeration
     >> https://github.com/gh0x0st

Usage: wanderer [target options] <value> [filter options] <value> [output options] <value>

Target Options:

-i, --id, Target a single or group of processes by their id number
-n, --name, Target a single or group of processes by their name
-c, --current, Target the current process and reveal the current privilege level
-a, --all, Target every running process

Filter Options:

--include-denied, Include instances where process access is denied
--exclude-32, Exclude instances where the process architecture is 32-bit
--exclude-64, Exclude instances where the process architecture is 64-bit
--exclude-amsiloaded, Exclude instances where amsi.dll is a loaded process module
--exclude-amsiunloaded, Exclude instances where amsi is not loaded process module
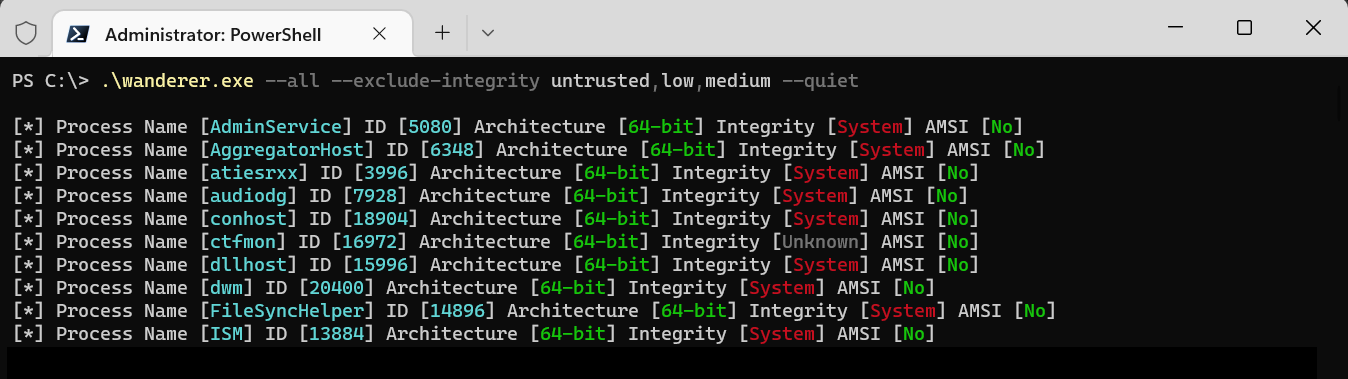
--exclude-integrity, Exclude instances where the process integrity level is a specific value

Output Options:

--output-nested, Output the results in a nested style view
-q, --quiet, Do not output the banner

Examples:

Enumerate the process with id 12345
C:\> wanderer --id 12345

Enumerate all processes with the names process1 and processs2
C:\> wanderer --name process1,process2

Enumerate the current process privilege level
C:\> wanderer --current

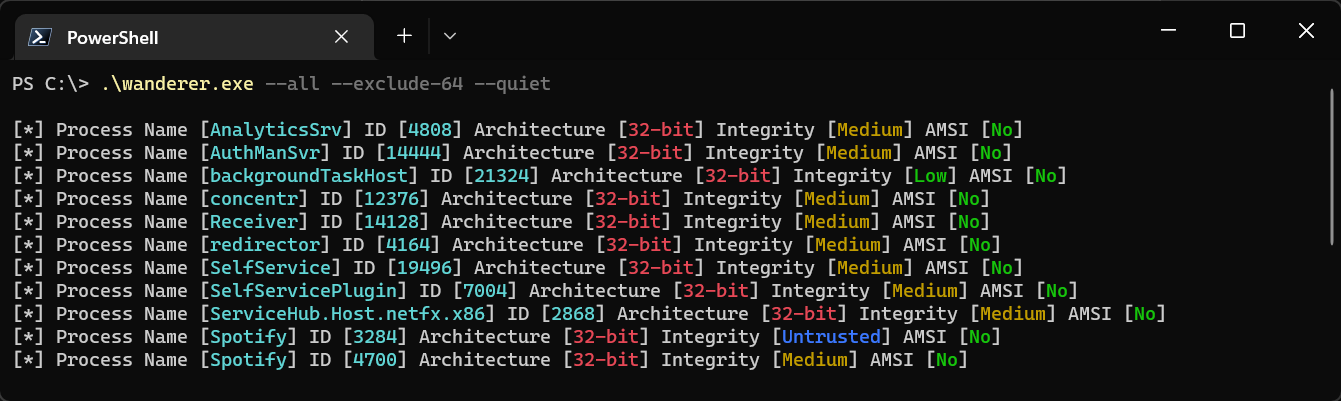
Enumerate all 32-bit processes
C:\wanderer --all --exclude-64

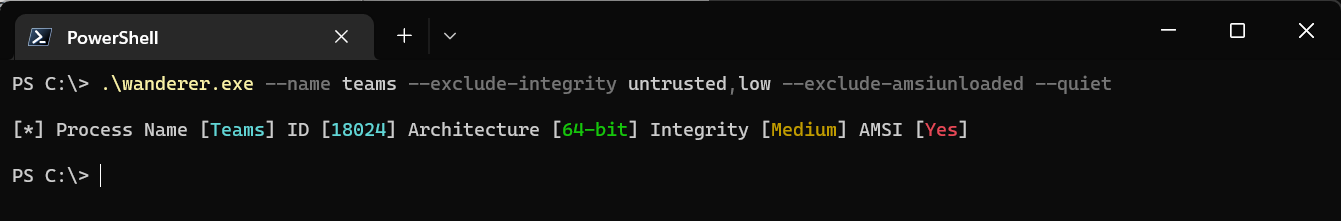
Enumerate all processes where is AMSI is loaded
C:\> wanderer --all --exclude-amsiunloaded

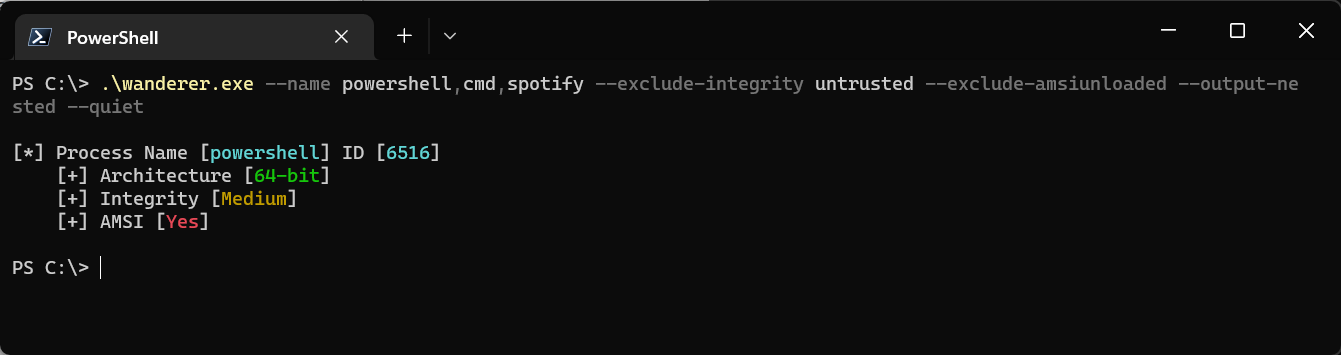
Enumerate all processes with the names pwsh,powershell,spotify and exclude instances where the integrity level is untrusted or low and exclude 32-bit processes
C:\> wanderer --name pwsh,powershell,spotify --exclude-integrity untrusted,low --exclude-32