 ayoubfaouzi/al-khaser
야생에서 사용되는 공개 악성코드 기술: 가상 머신, 에뮬레이션, 디버거, 샌드박스 탐지

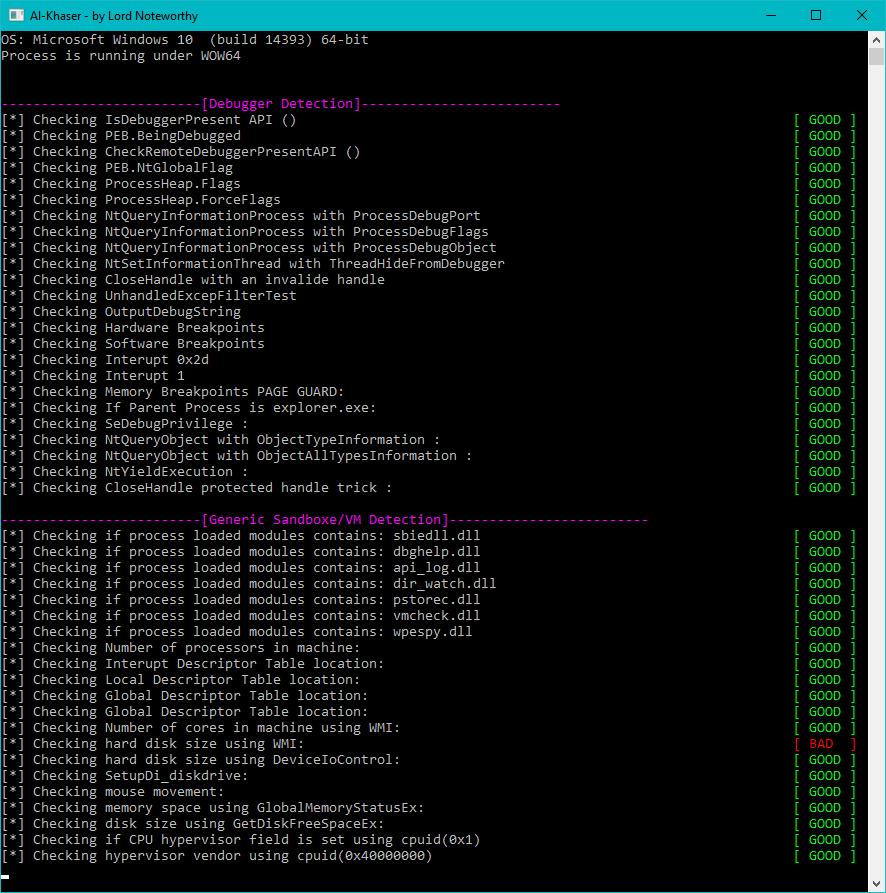
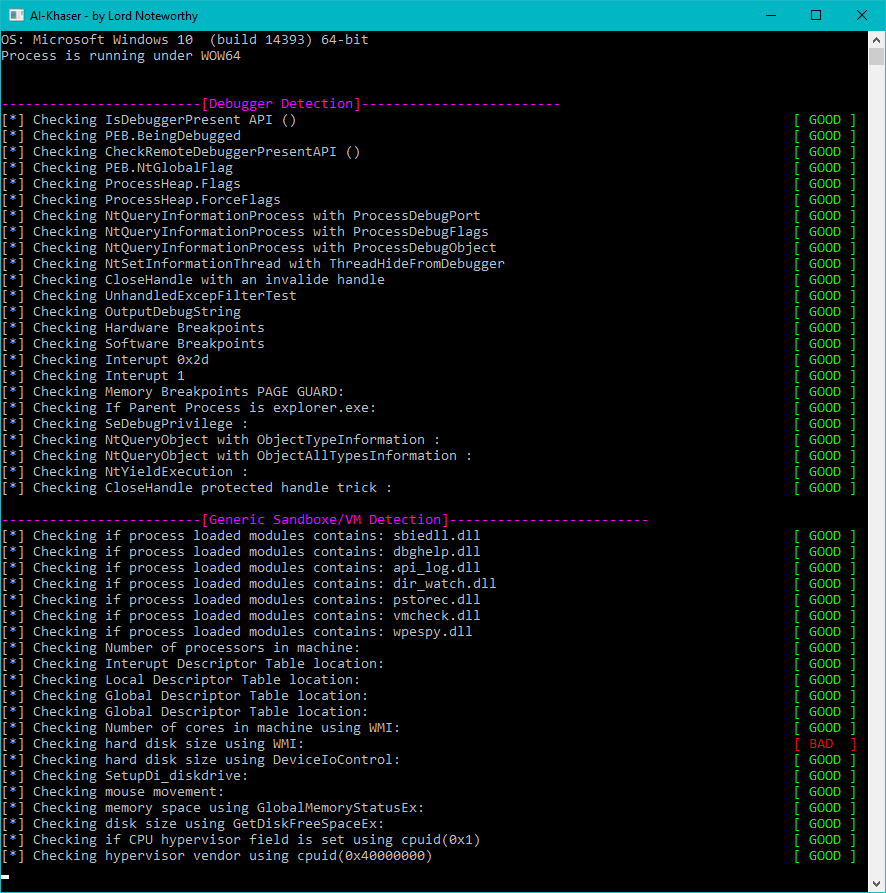
al-khaser는 좋은 의도로 만들어진 PoC "악성코드" 애플리케이션으로, 안티-악성코드 시스템을 테스트하기 위한 것입니다. 이는 일반적인 악성코드 트릭들을 수행하여 탐지되지 않는지 확인하는 것을 목표로 합니다.
$ ./al-khaser.exe -h
Usage: al-khaser.exe [OPTIONS]
Options:
  --check <type>      Enable specific check(s). Can be used multiple times. Valid types are:
                        TLS              (Thread Local Storage callback checks)
                        DEBUG            (Anti-debugging checks)
                        INJECTION        (Code injection checks)
                        GEN_SANDBOX      (Generic sandbox checks)
                        VBOX             (VirtualBox detection)
                        VMWARE           (VMware detection)
                        VPC              (Virtual PC detection)
                        QEMU             (QEMU detection)
                        KVM              (KVM detection)
                        XEN              (Xen detection)
                        WINE             (Wine detection)
                        PARALLELS        (Parallels detection)
                        HYPERV           (Hyper-V detection)
                        CODE_INJECTIONS  (Additional code injection techniques)
                        TIMING_ATTACKS   (Timing/sleep-based sandbox evasion)
                        DUMPING_CHECK    (Dumping memory/process checks)
                        ANALYSIS_TOOLS   (Analysis tools detection)
                        ANTI_DISASSM     (Anti-disassembly checks)
  --sleep <seconds>   Set sleep/delay duration in seconds (default: 600).
  --delay <seconds>   Alias for --sleep.
  -h, --help          Show this help message and exit.

Examples:
  al-khaser.exe --check DEBUG --check TIMING_ATTACKS --sleep 30
  al-khaser.exe --check VMWARE --check QEMU
  al-khaser.exe --sleep 30
빌드된 바이너리(x86, x64)는 이 프로젝트의 릴리즈 페이지에서 다운로드할 수 있습니다. 7z 파일의 비밀번호는 여기에서 확인할 수 있습니다.
만약 악성코드에서 본 적이 있는 안티-분석 트릭을 발견하셨다면, 주저하지 말고 기여해 주시기 바랍니다.
sample.exe 또는 sandbox.exe 같은 파일 이름.