Skip to content
KitploitKITPLOIT
도구익스플로잇블로그
Log in
제출
도구익스플로잇블로그
제출

해킹, 침투 테스트 및 사이버 보안 도구를 당신의 보안 무기고에!

Kitploit은 해킹, 사이버 보안 및 침투 테스트 도구 디렉토리입니다. 최신 프로젝트 업데이트를 발견하여 취약점을 찾고, 시스템을 분석하고, 테스트를 자동화하고, 보안을 강화하세요.

피드문의개인정보© 2026 Kitploit

도구 디렉토리

카테고리

모든 카테고리 보기
Loading categories
Hx0-HawkEye — 가벼운 브라우저 트래픽 캡처 및 보안 분석 확장 프로그램으로, 브라우저 사이드바에서 캡처, 차단, 수정, 재전송, 규칙 기반 탐지 및 AI 지원 분석의 전체 워크플로를 완료할 수 있습니다.(가벼운 브라우저 익스텐션으로 트래픽 캡처 및 보안 분석을 위해 브라우저 사이드바에서 캡처, 차단, 수정, 재전송, 규칙 기반 탐지 및 AI 지원 분석이 가능합니다.) | Kitploit
도구/GitHubGitHub/asaotomo/hx0-hawkeye
Packet Sniffing & AnalysisVulnerability ScannersWeb Proxies & InterceptionAPI Security TestingWeb SecurityFuzzingCTFPenetration TestingLearning & EducationAI Security
GitHubasaotomo/hx0-hawkeye
606817일 전Kitploit 검토 완료

인기

모두 보기 →

커뮤니티에서 가장 많이 사용되는 도구를 찾아보세요.

모든 도구 탐색

도구 컬렉션을 둘러보세요

모든 도구 보기 →

Hx0-HawkEye

가벼운 브라우저 트래픽 캡처 및 보안 분석 확장 프로그램으로, 브라우저 사이드바에서 캡처, 차단, 수정, 재전송, 규칙 기반 탐지 및 AI 지원 분석의 전체 워크플로를 완료할 수 있습니다.(가벼운 브라우저 익스텐션으로 트래픽 캡처 및 보안 분석을 위해 브라우저 사이드바에서 캡처, 차단, 수정, 재전송, 규칙 기반 탐지 및 AI 지원 분석이 가능합니다.)

저장소 보기웹사이트
공유
요청한 언어로 콘텐츠를 사용할 수 없습니다. 영어 버전을 표시합니다.

🦅 Hx0 HawkEye: Full-stack lightweight capture & AI security auditing extension

【中文 / English】

1. What it is

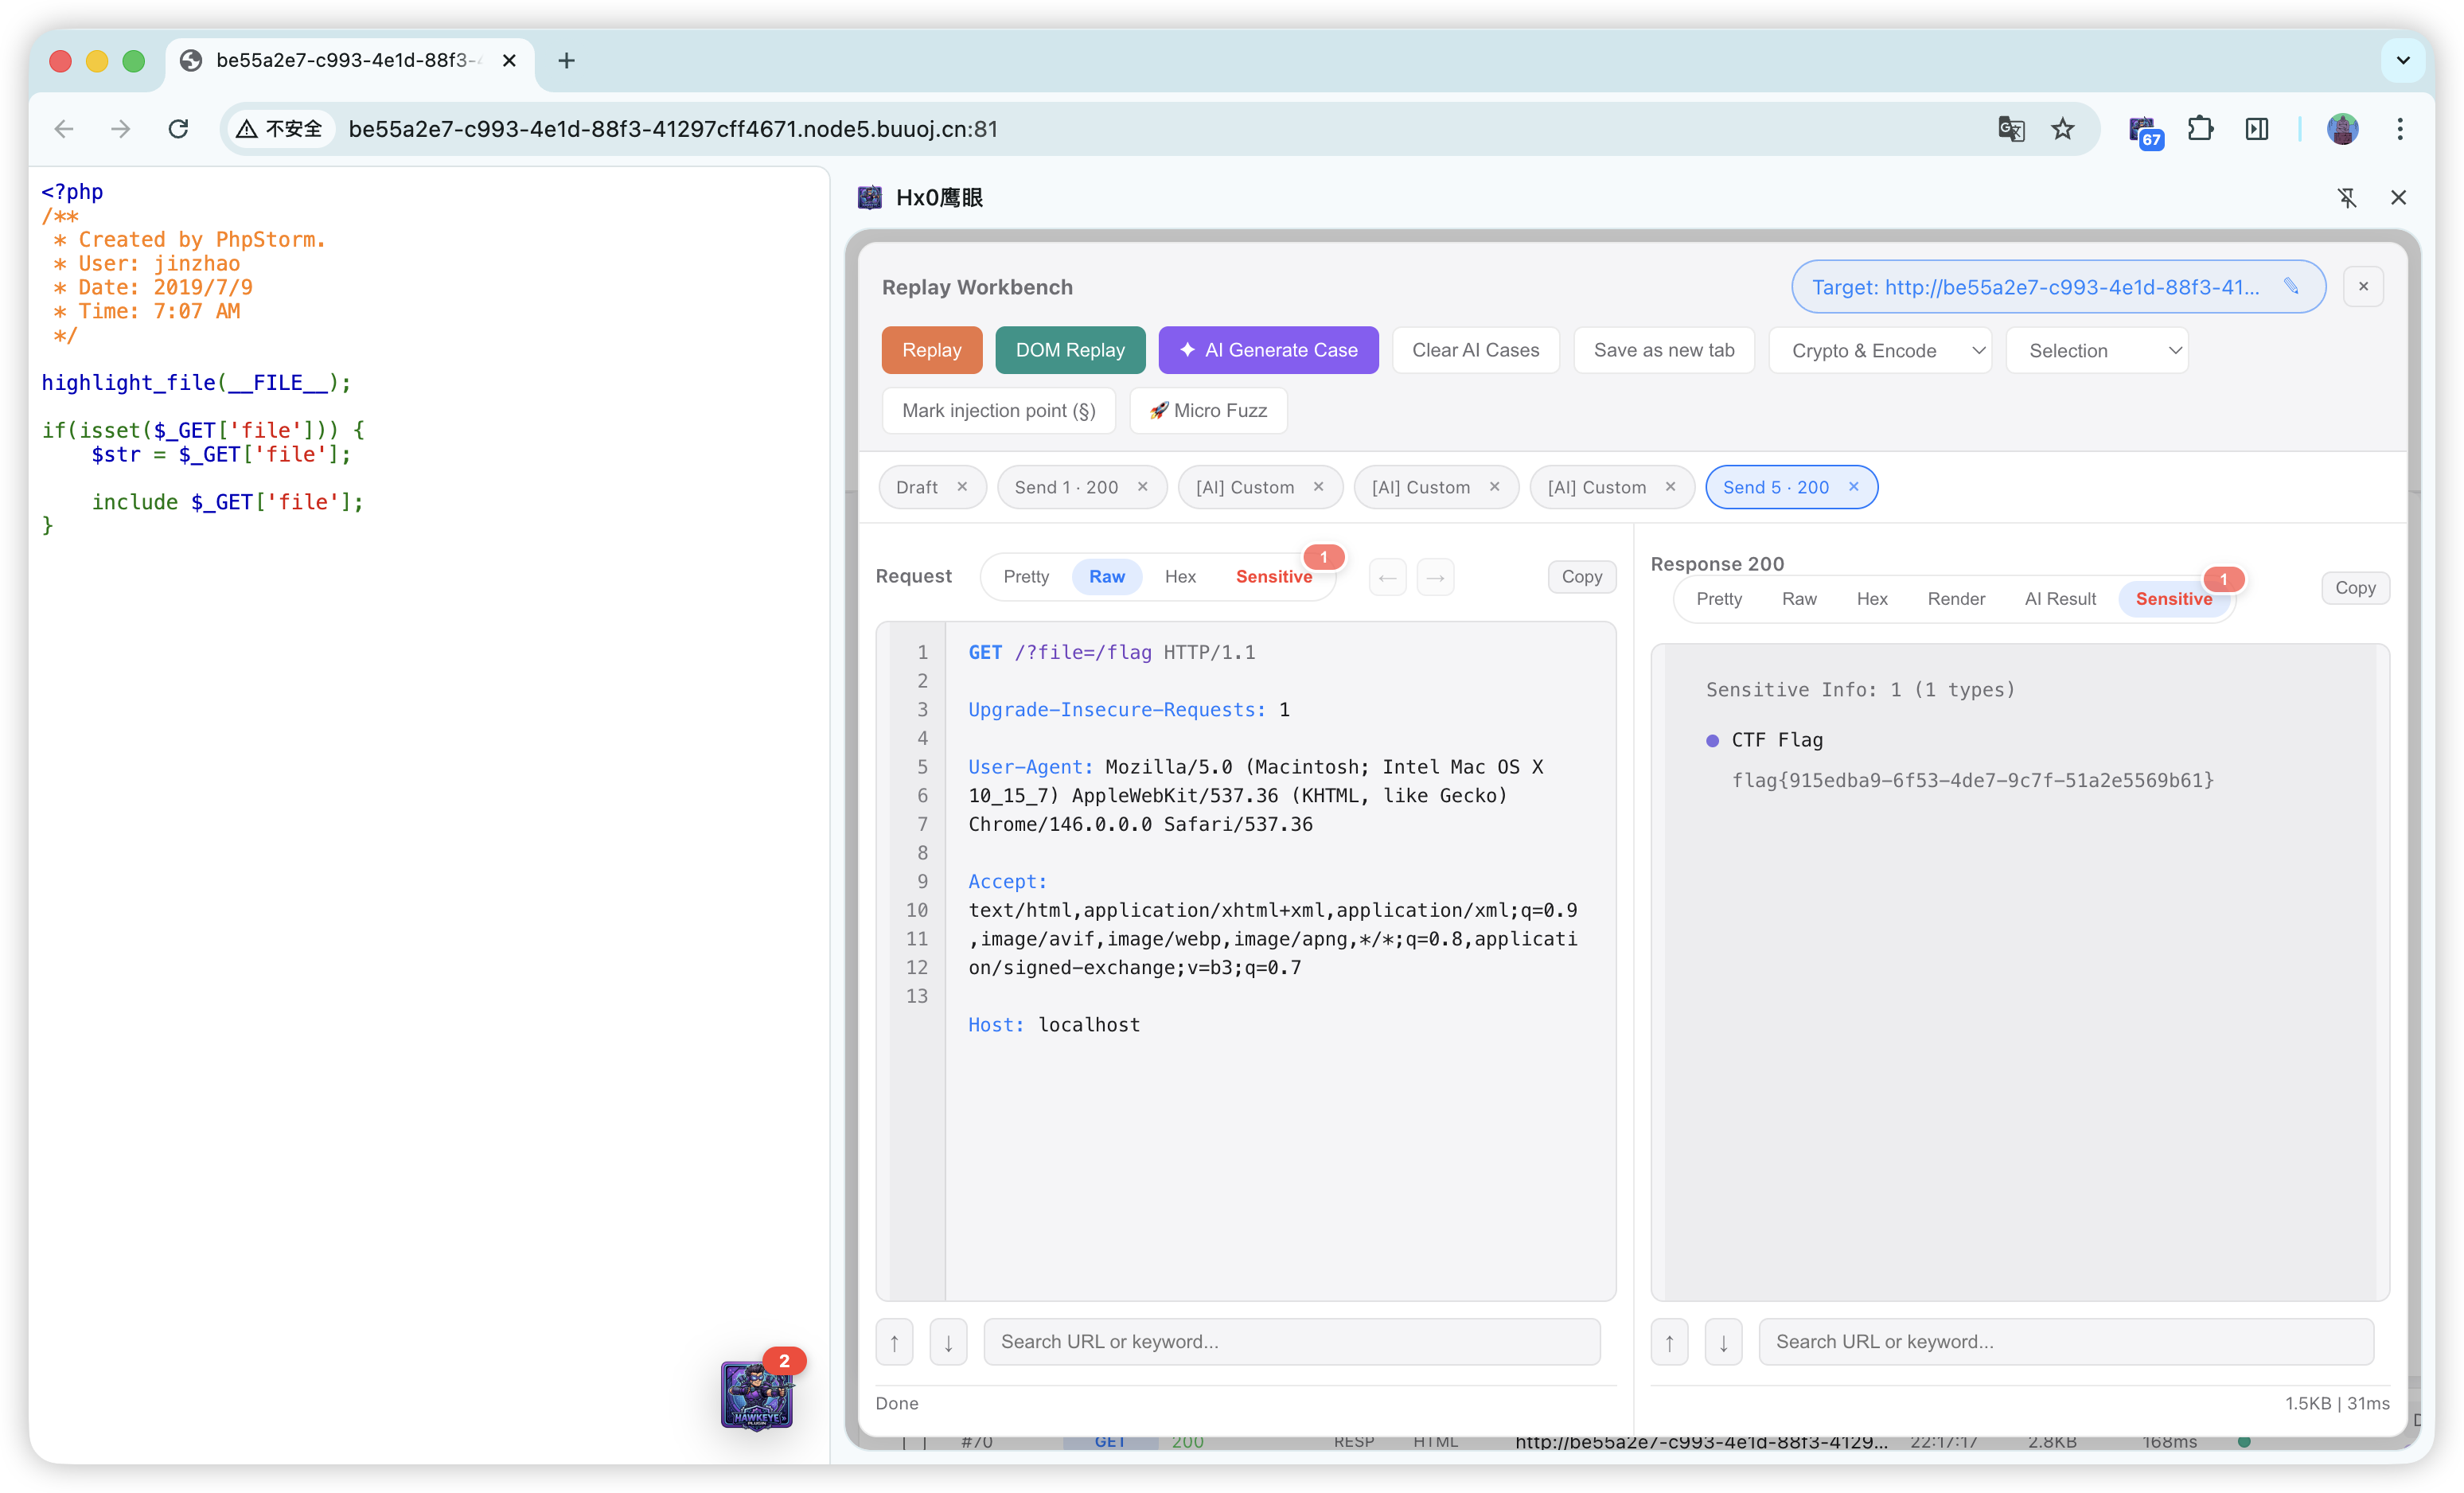
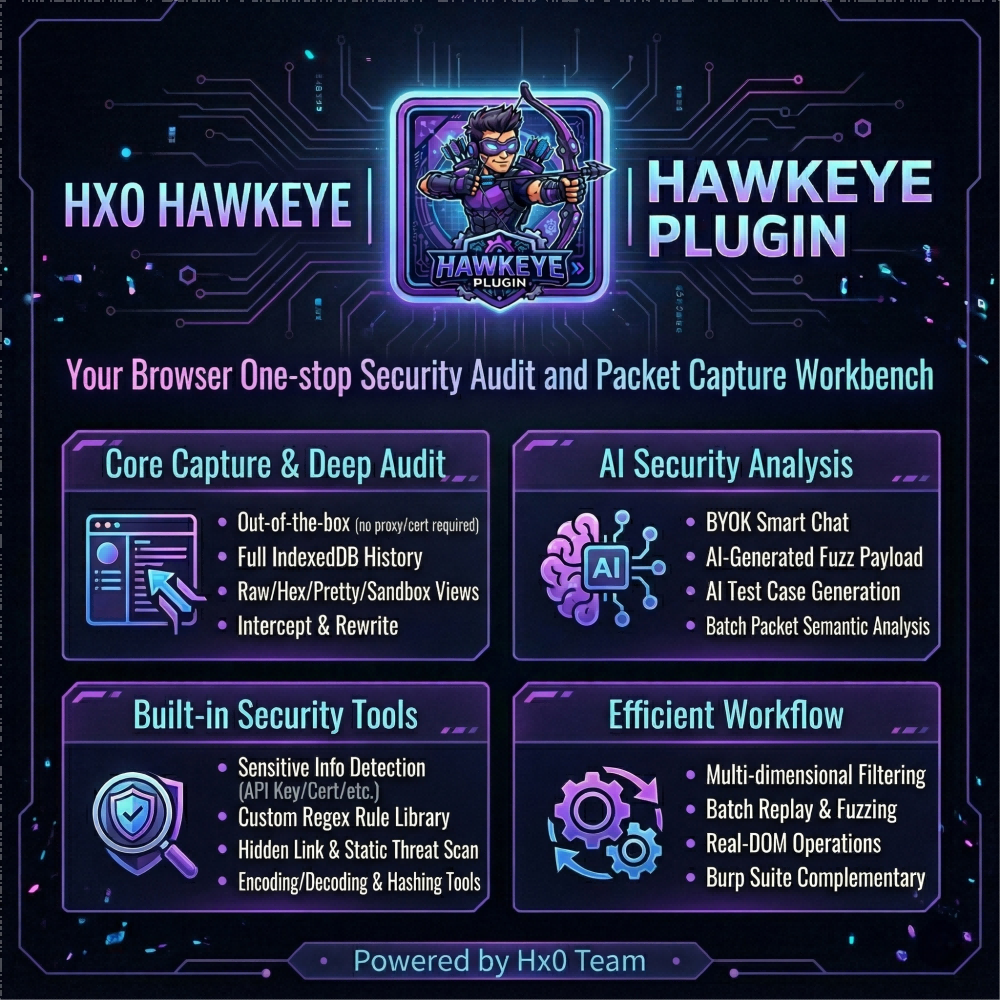
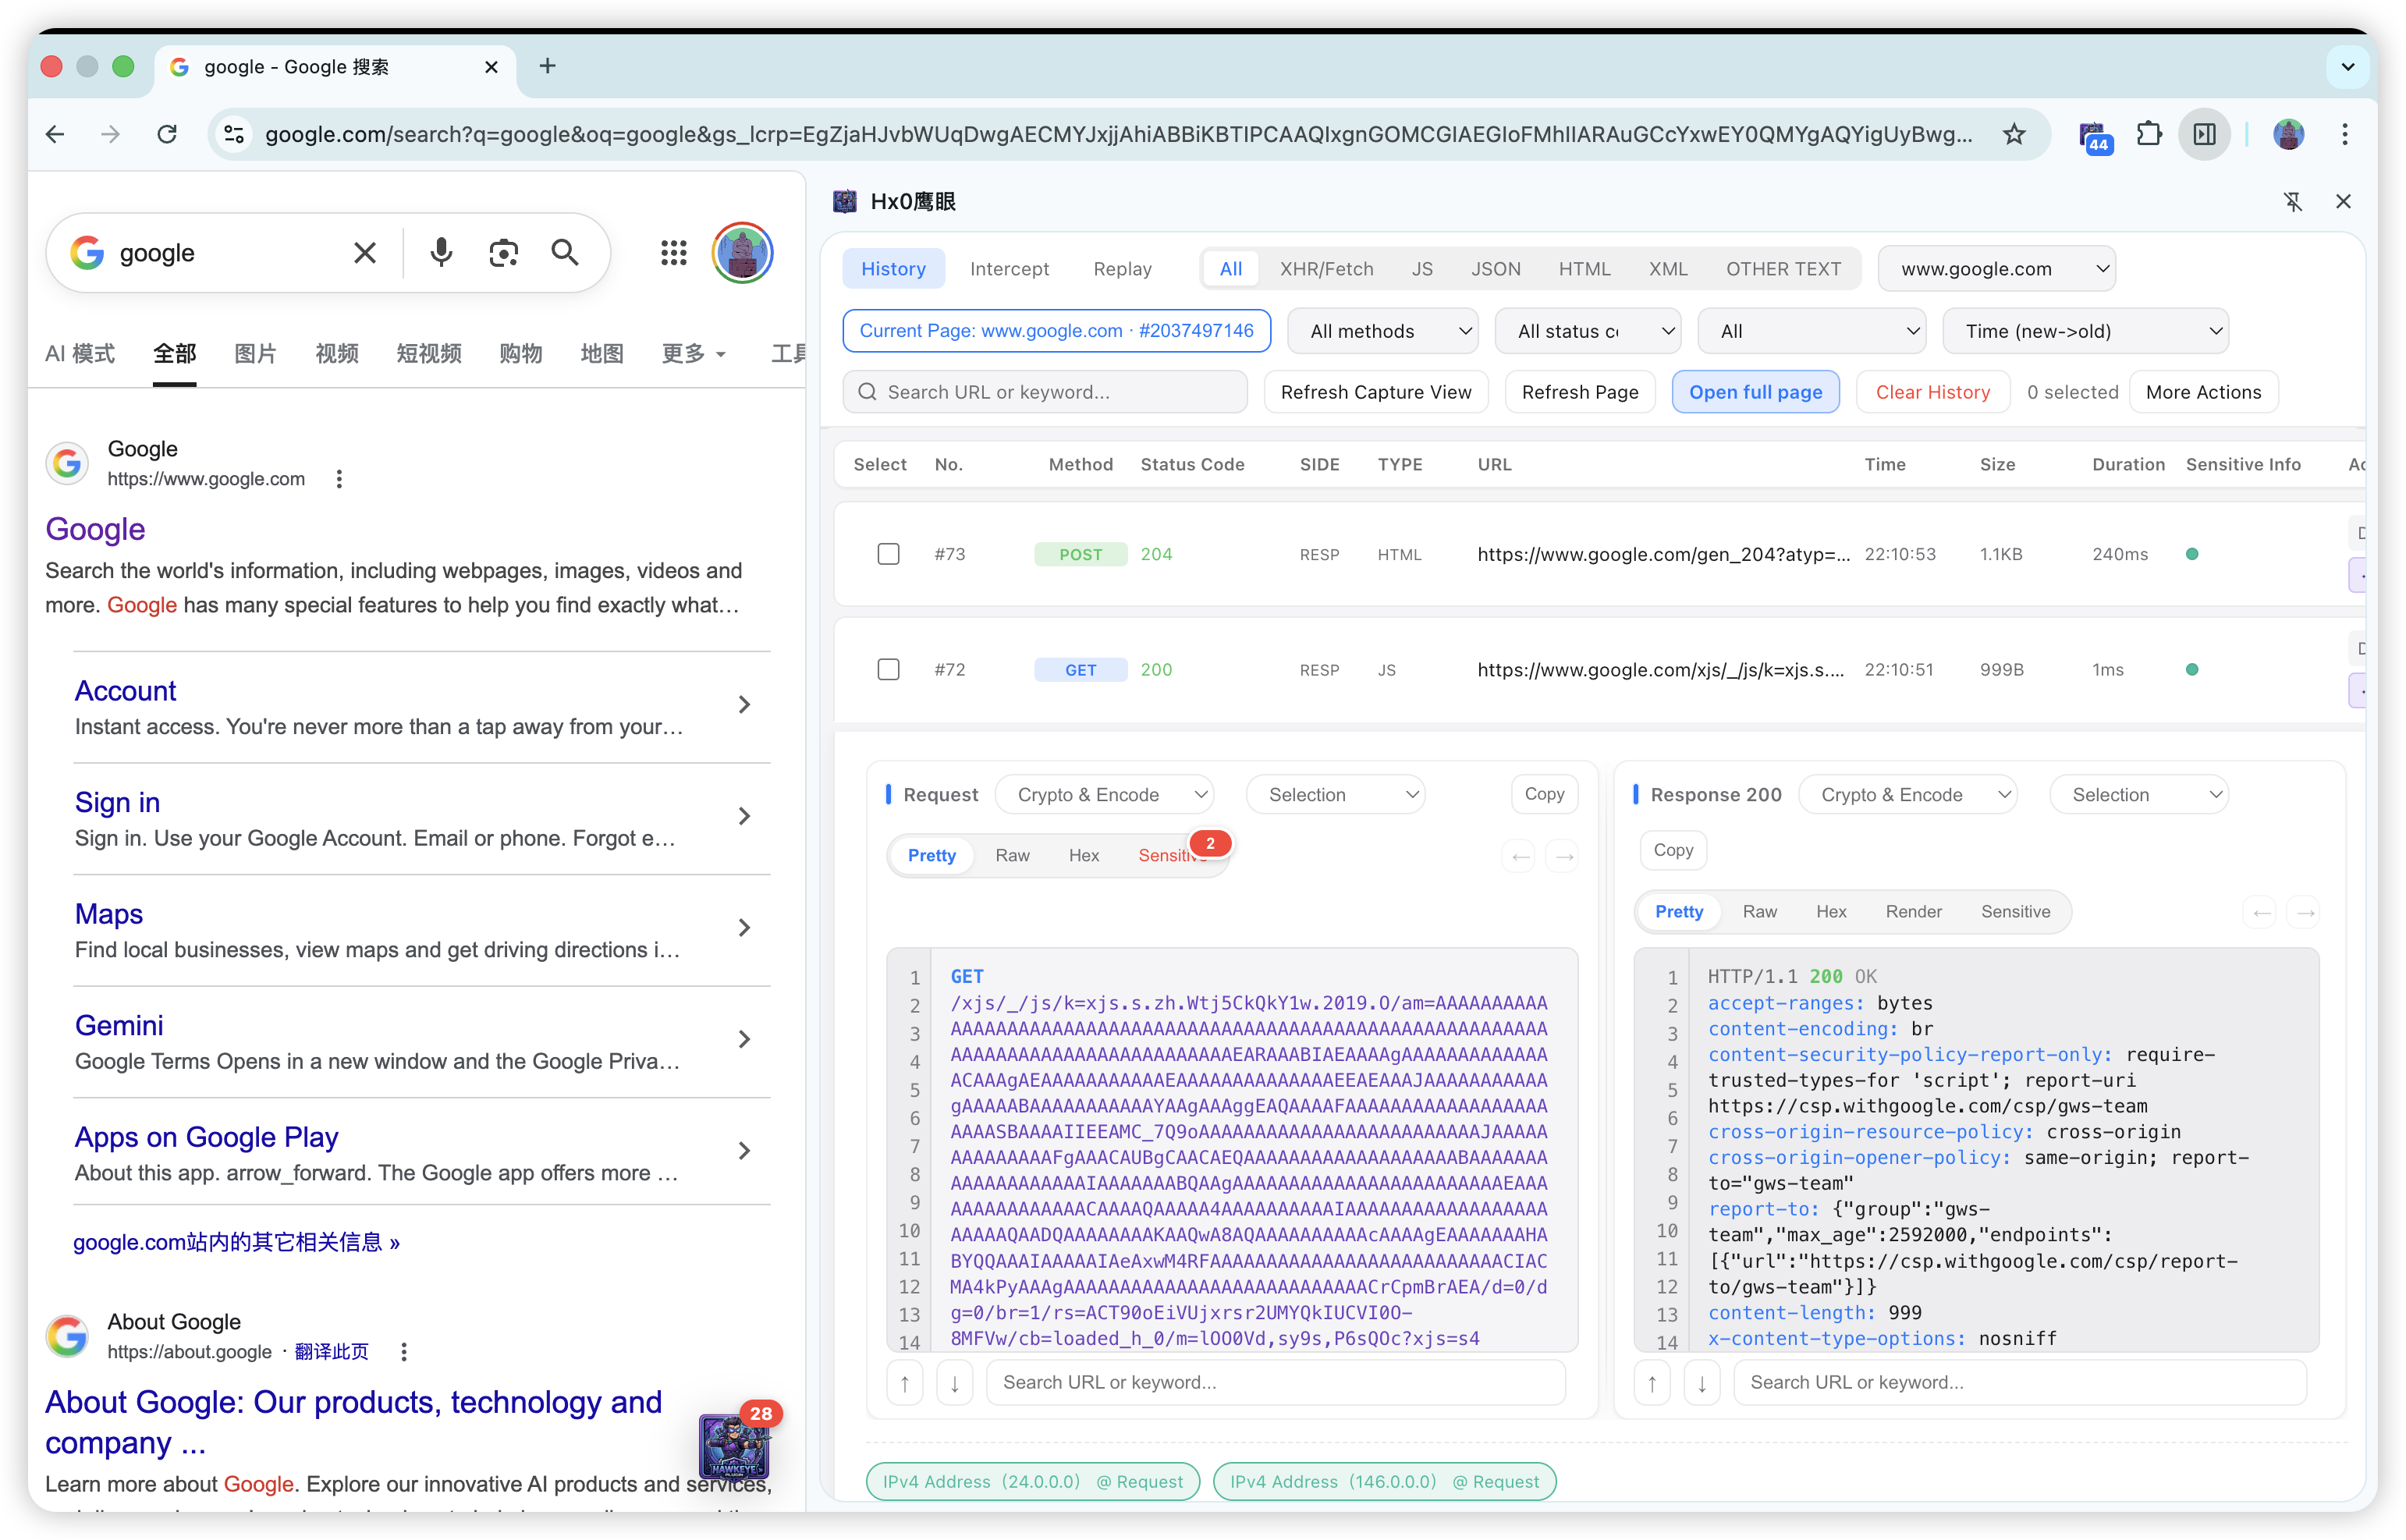
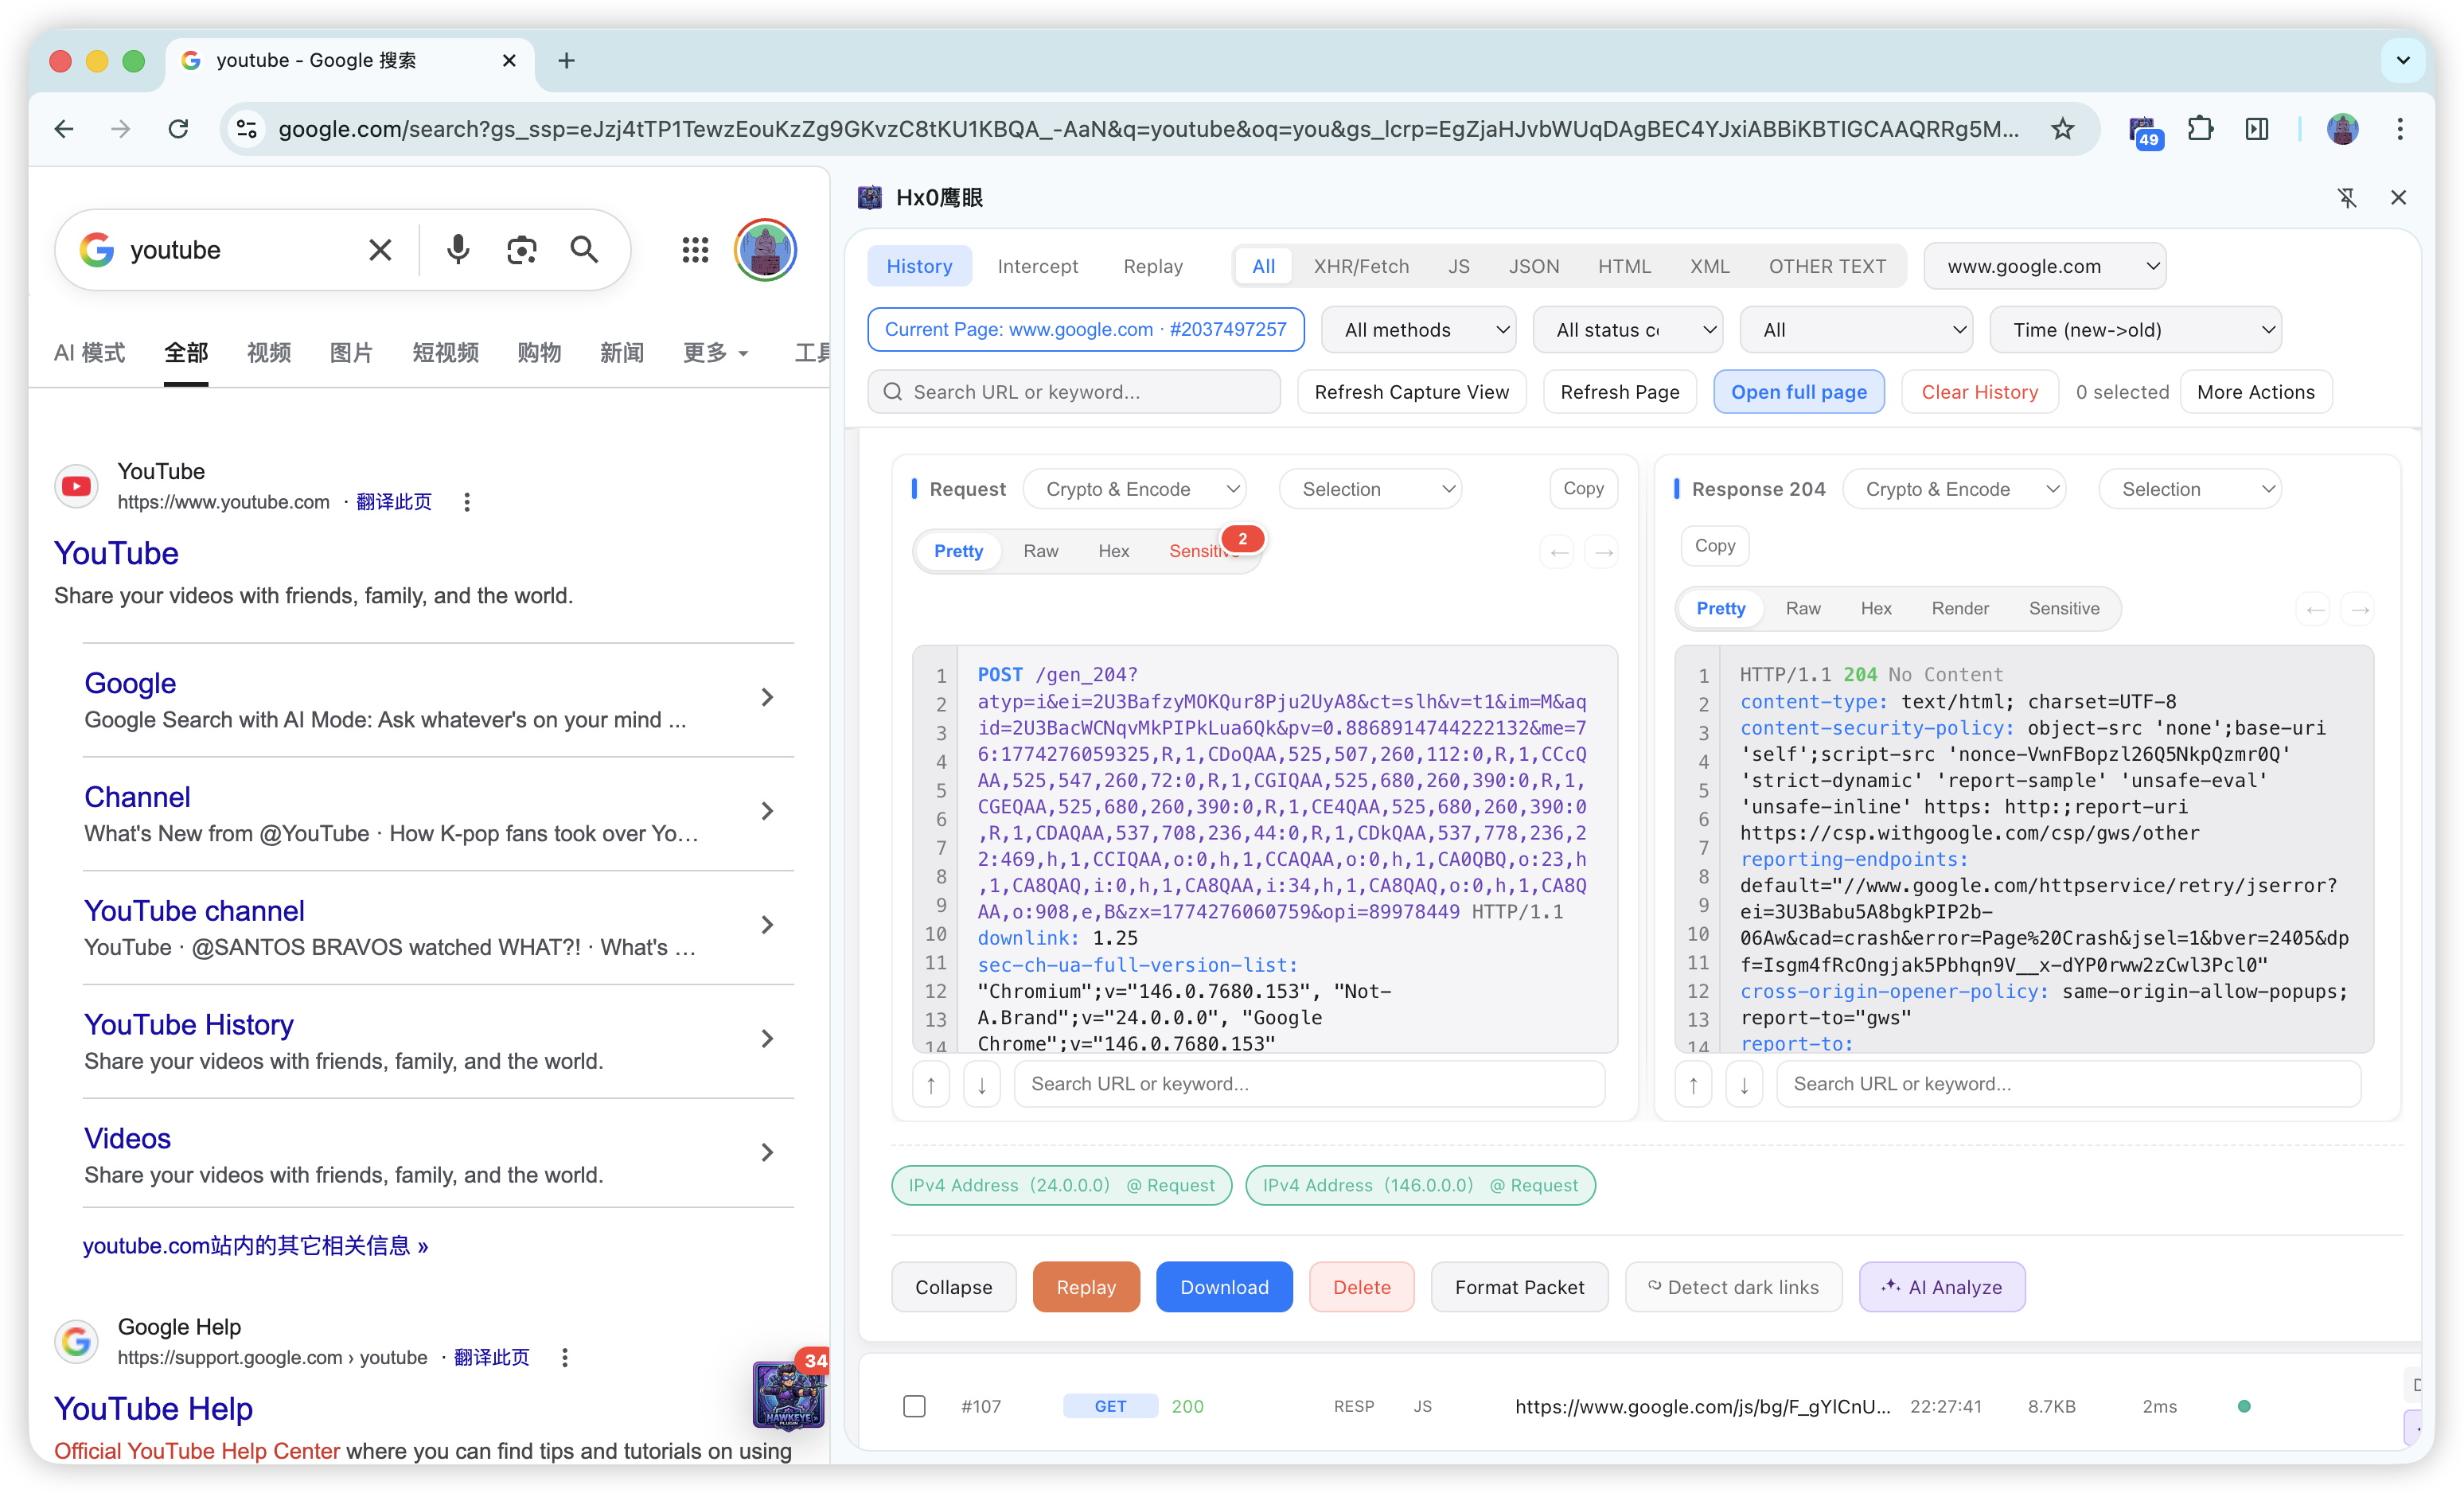
Skip the proxy hassle—truly ready out of the box. Hx0 HawkEye is a native browser extension (Chrome / Firefox and mainstream Chromium) that gives you a full capture, intercept (HTTP + WebSocket frames), replay, micro-Fuzz, and AI-assisted auditing loop directly in the sidebar.
⚡ Core advantage: why not a classic proxy?

  • Zero environment overhead: no Burp Suite required, no system proxy, no root trust or Java setup.
  • Session fidelity: sees real page XHR / Fetch / WebSocket traffic with the same origin login state as the active tab—no more “proxy ate my cookies” or constant re-auth pain.
  • Works immediately after install: ideal for day-to-day dev/debug, API triage, and authorized first-pass security review.

🤖 Differentiator: end-to-end AI (BYOK)

Bring your own model API (BYOK) and embed AI into the sidebar workflow:
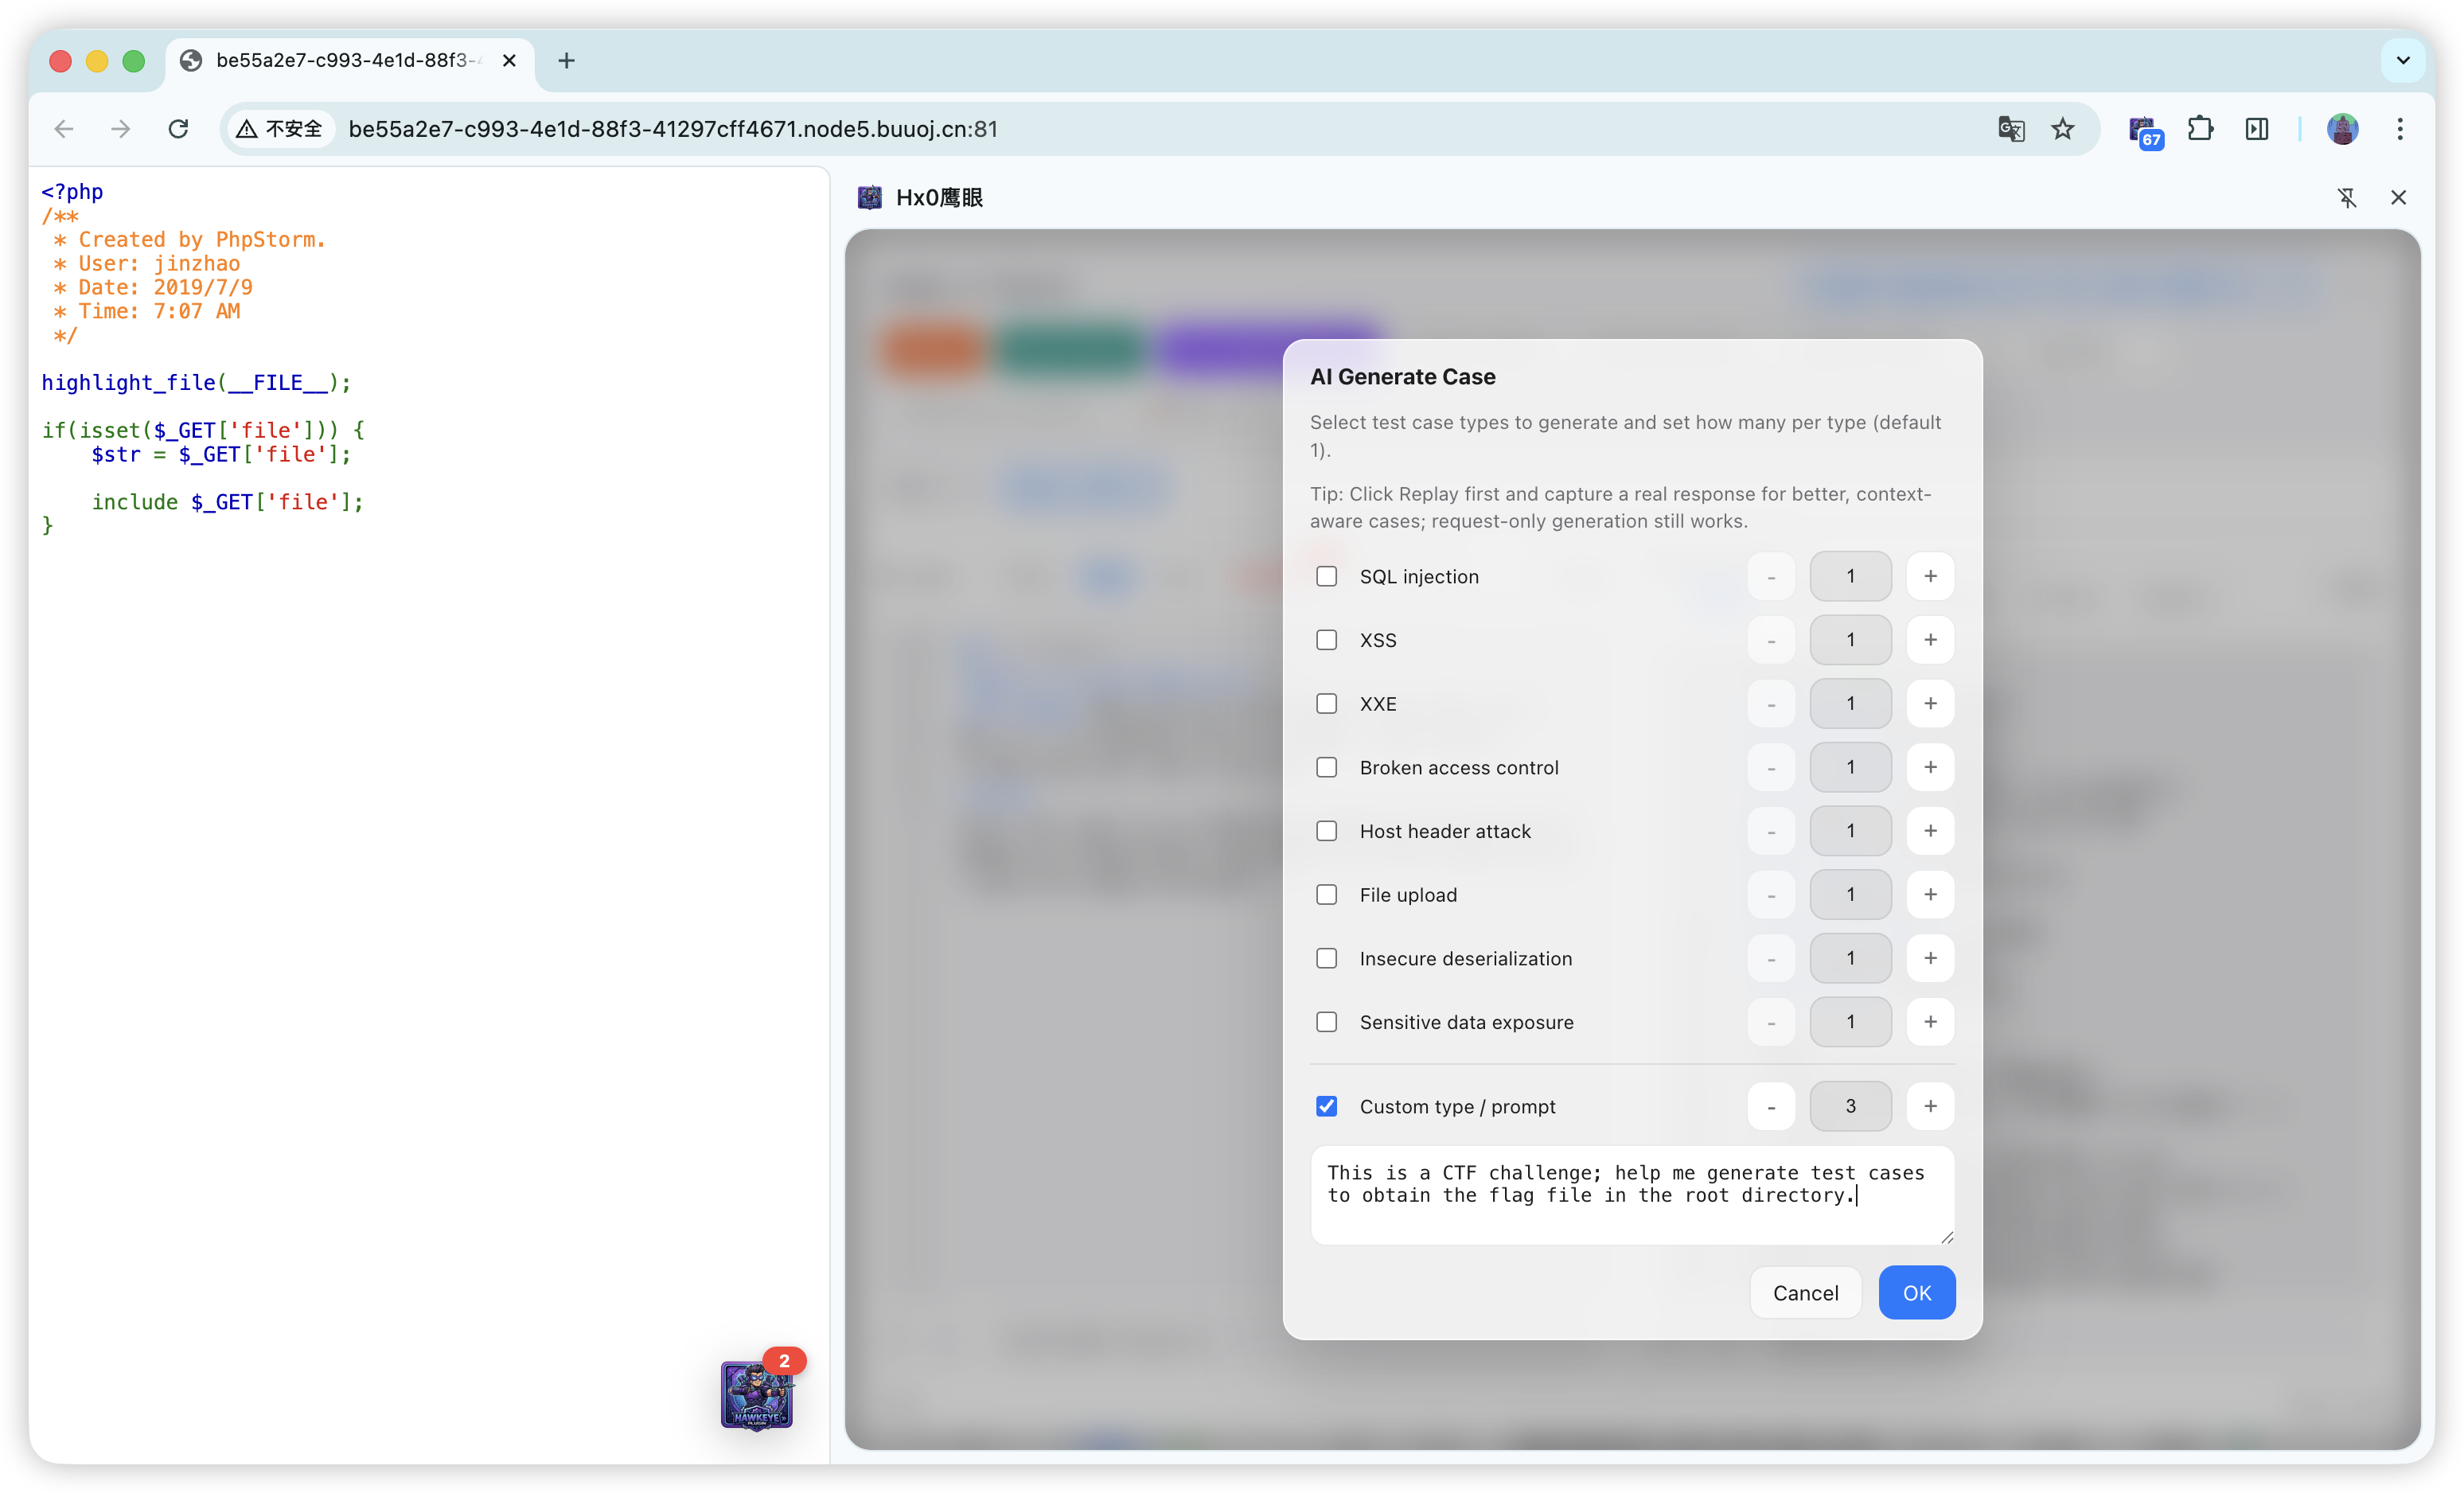
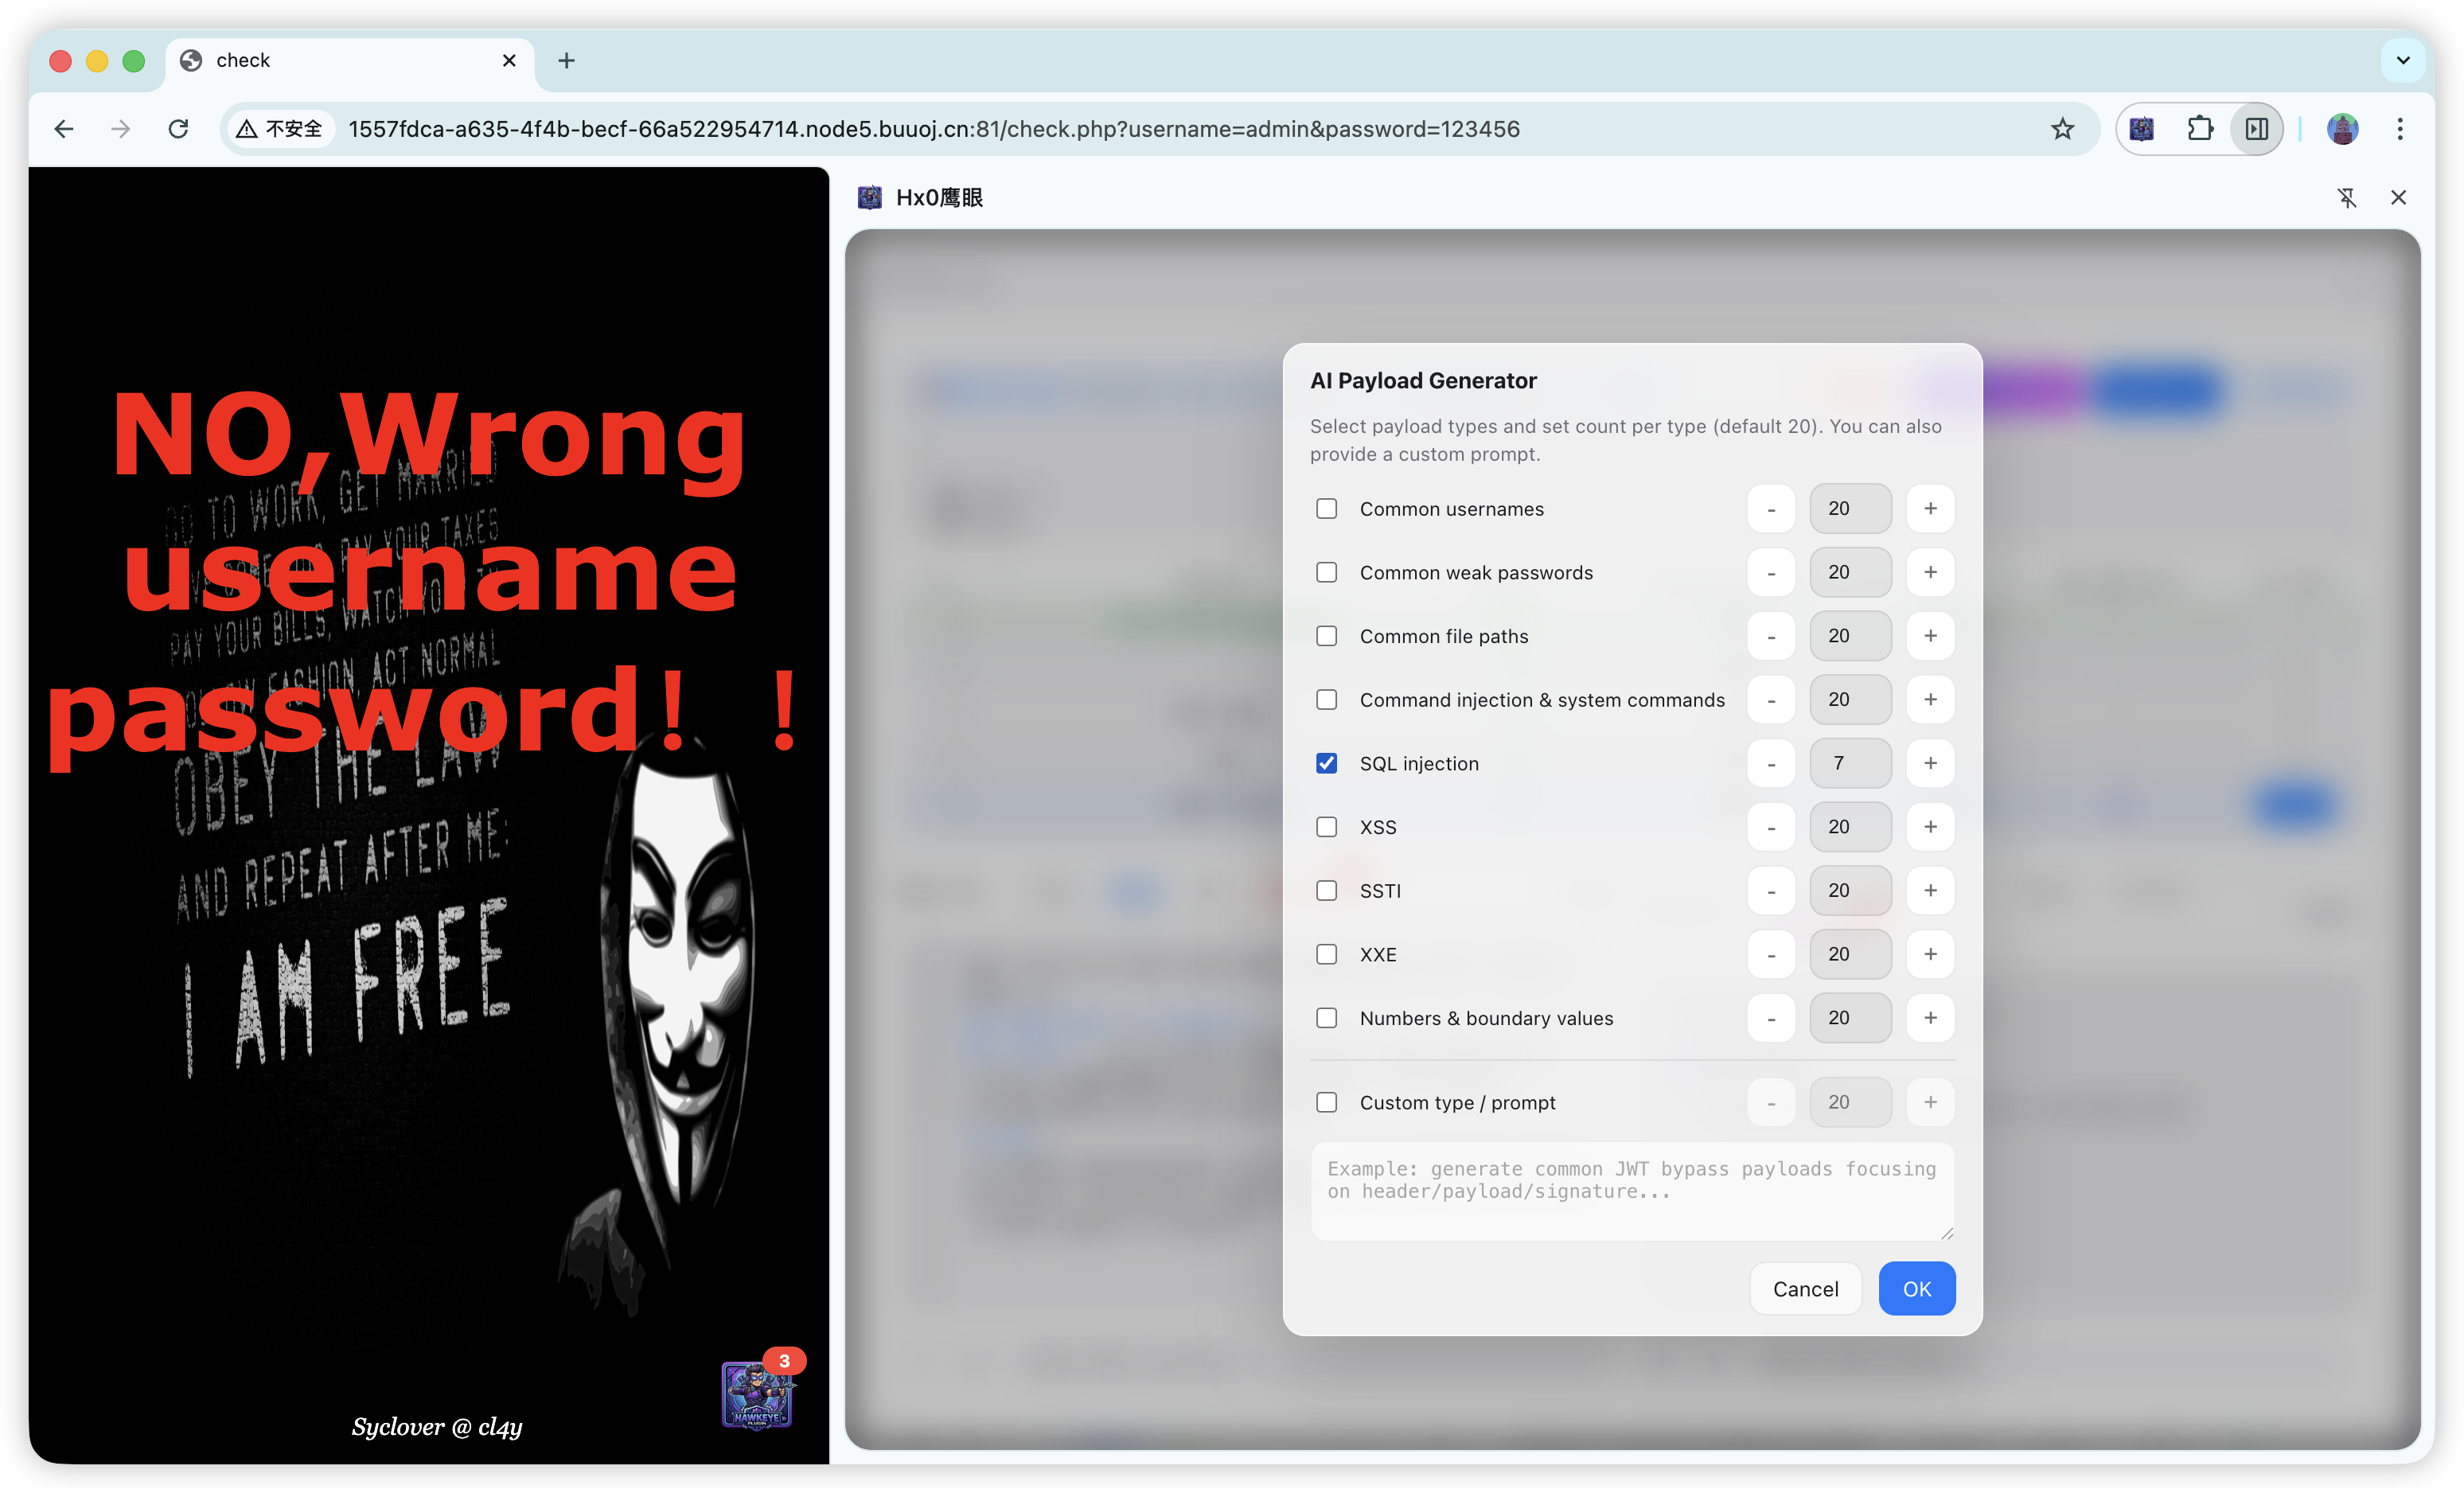
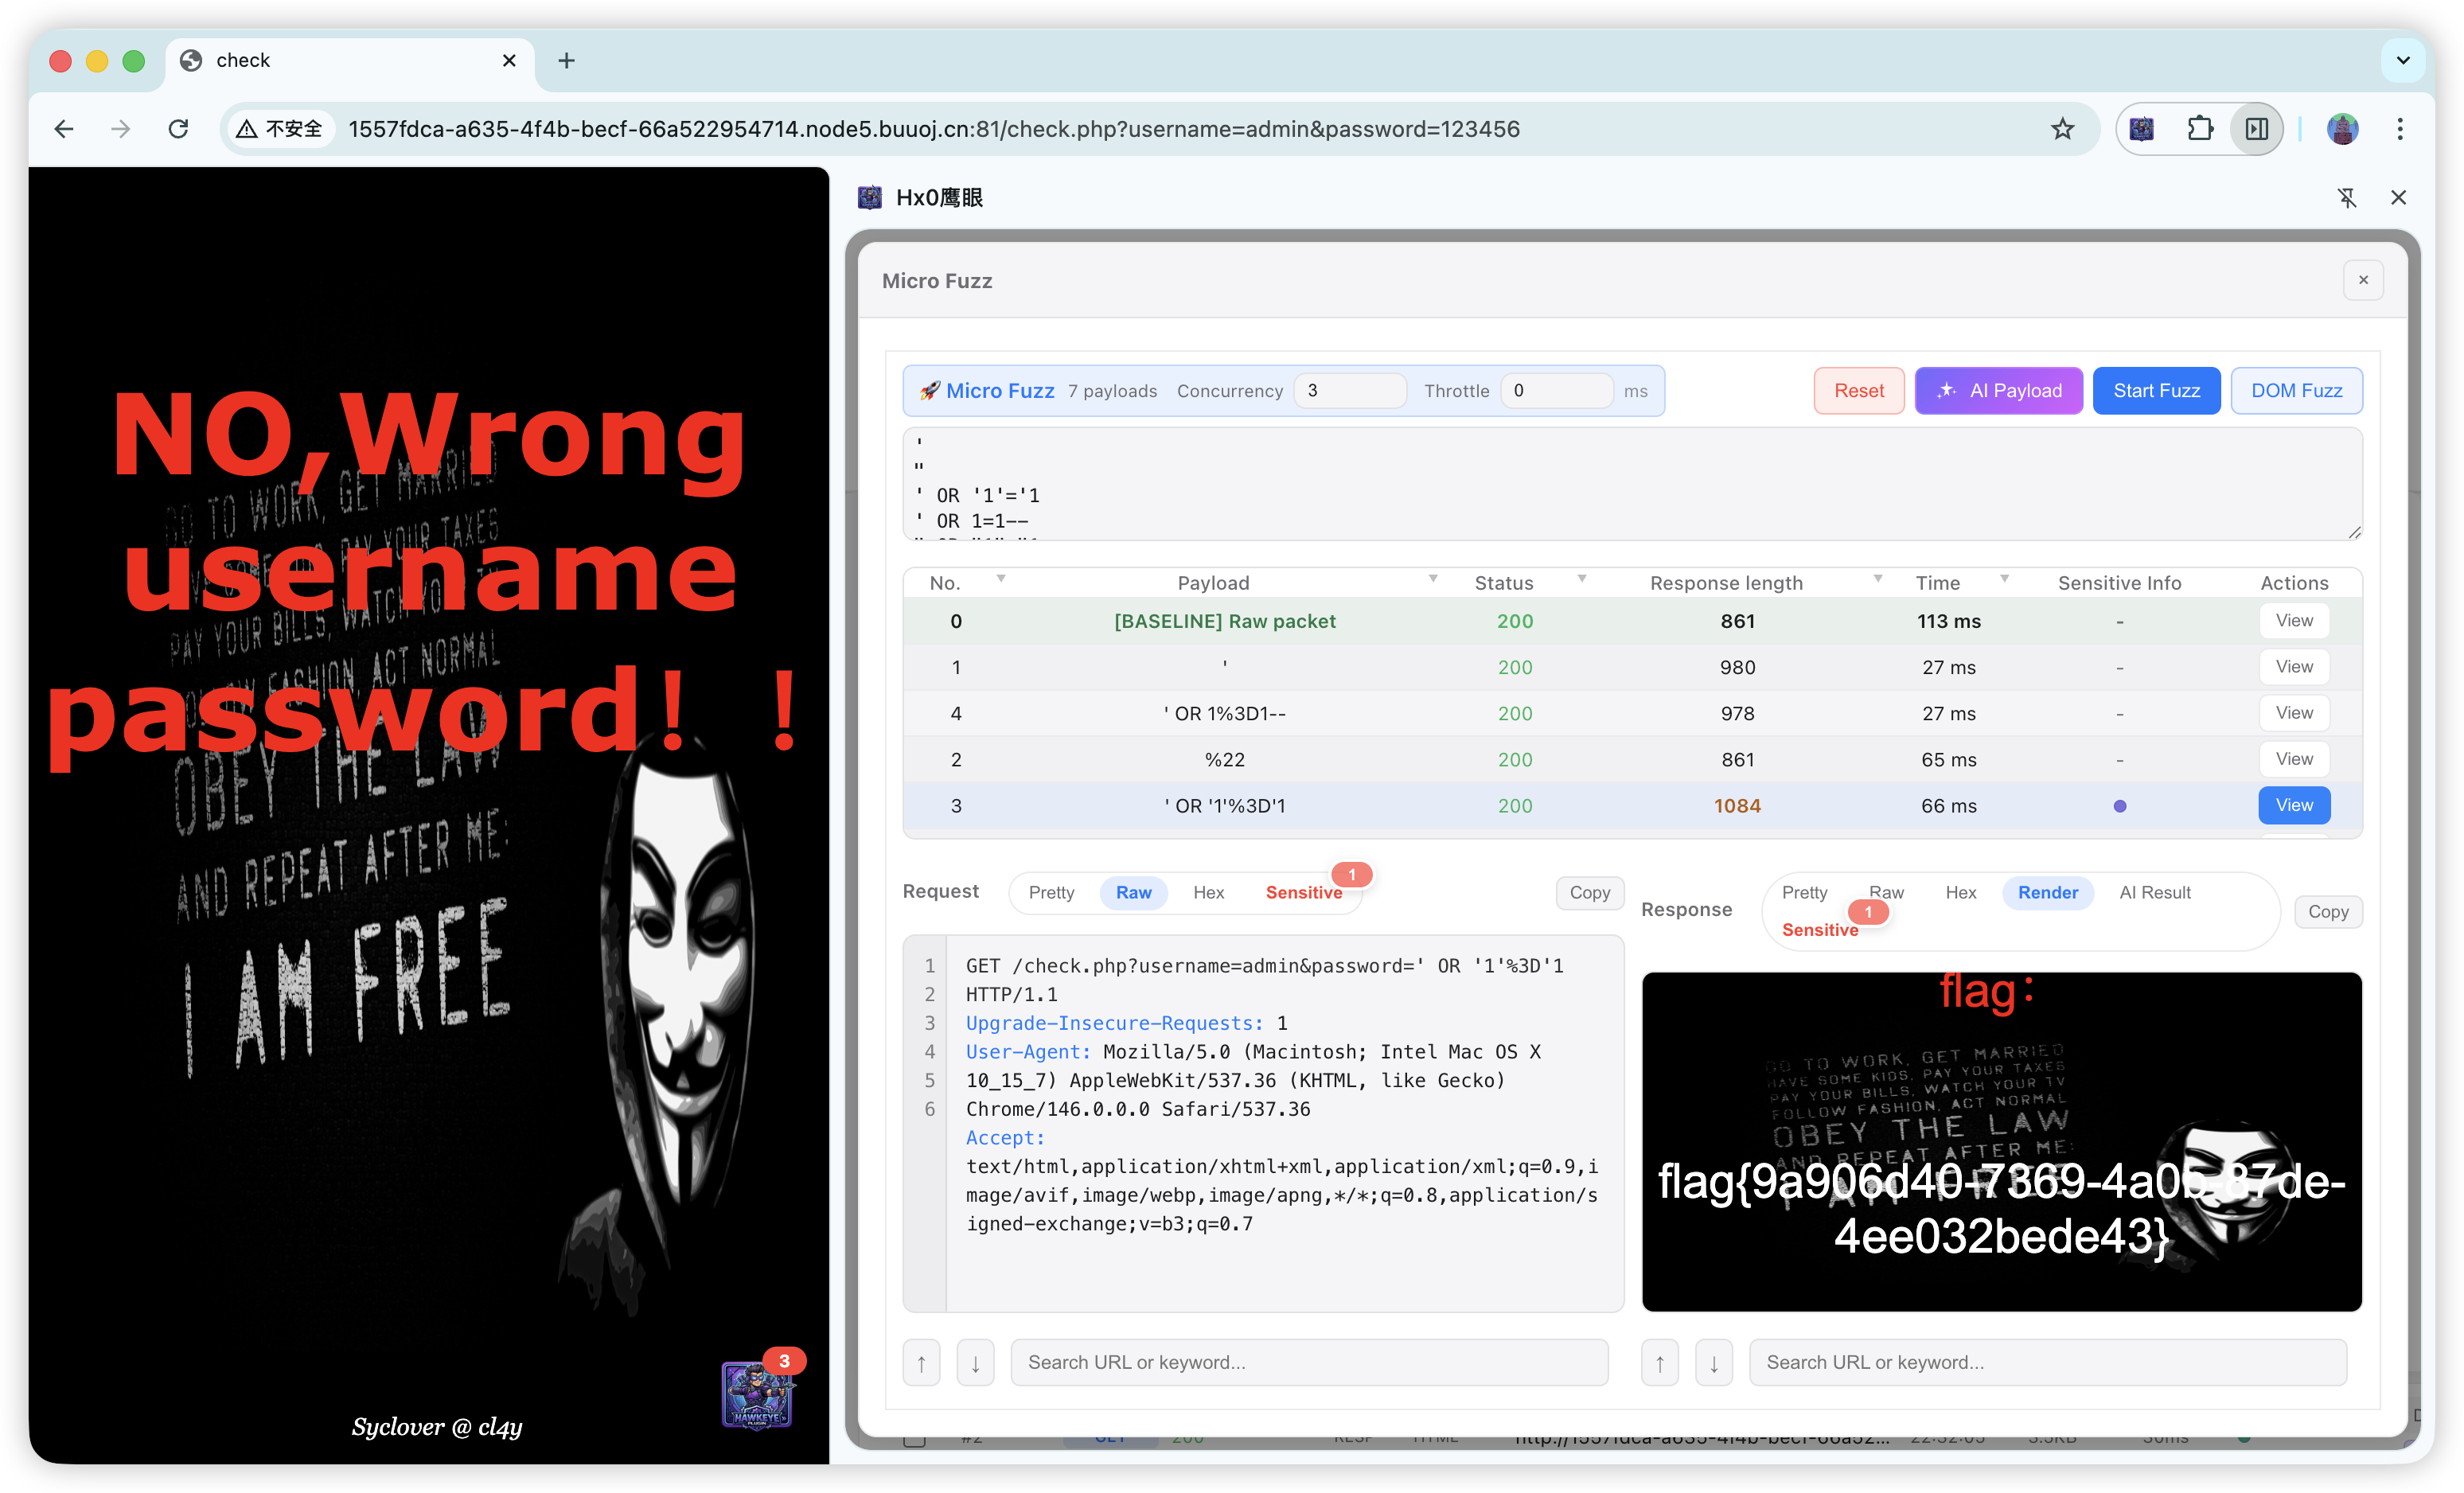
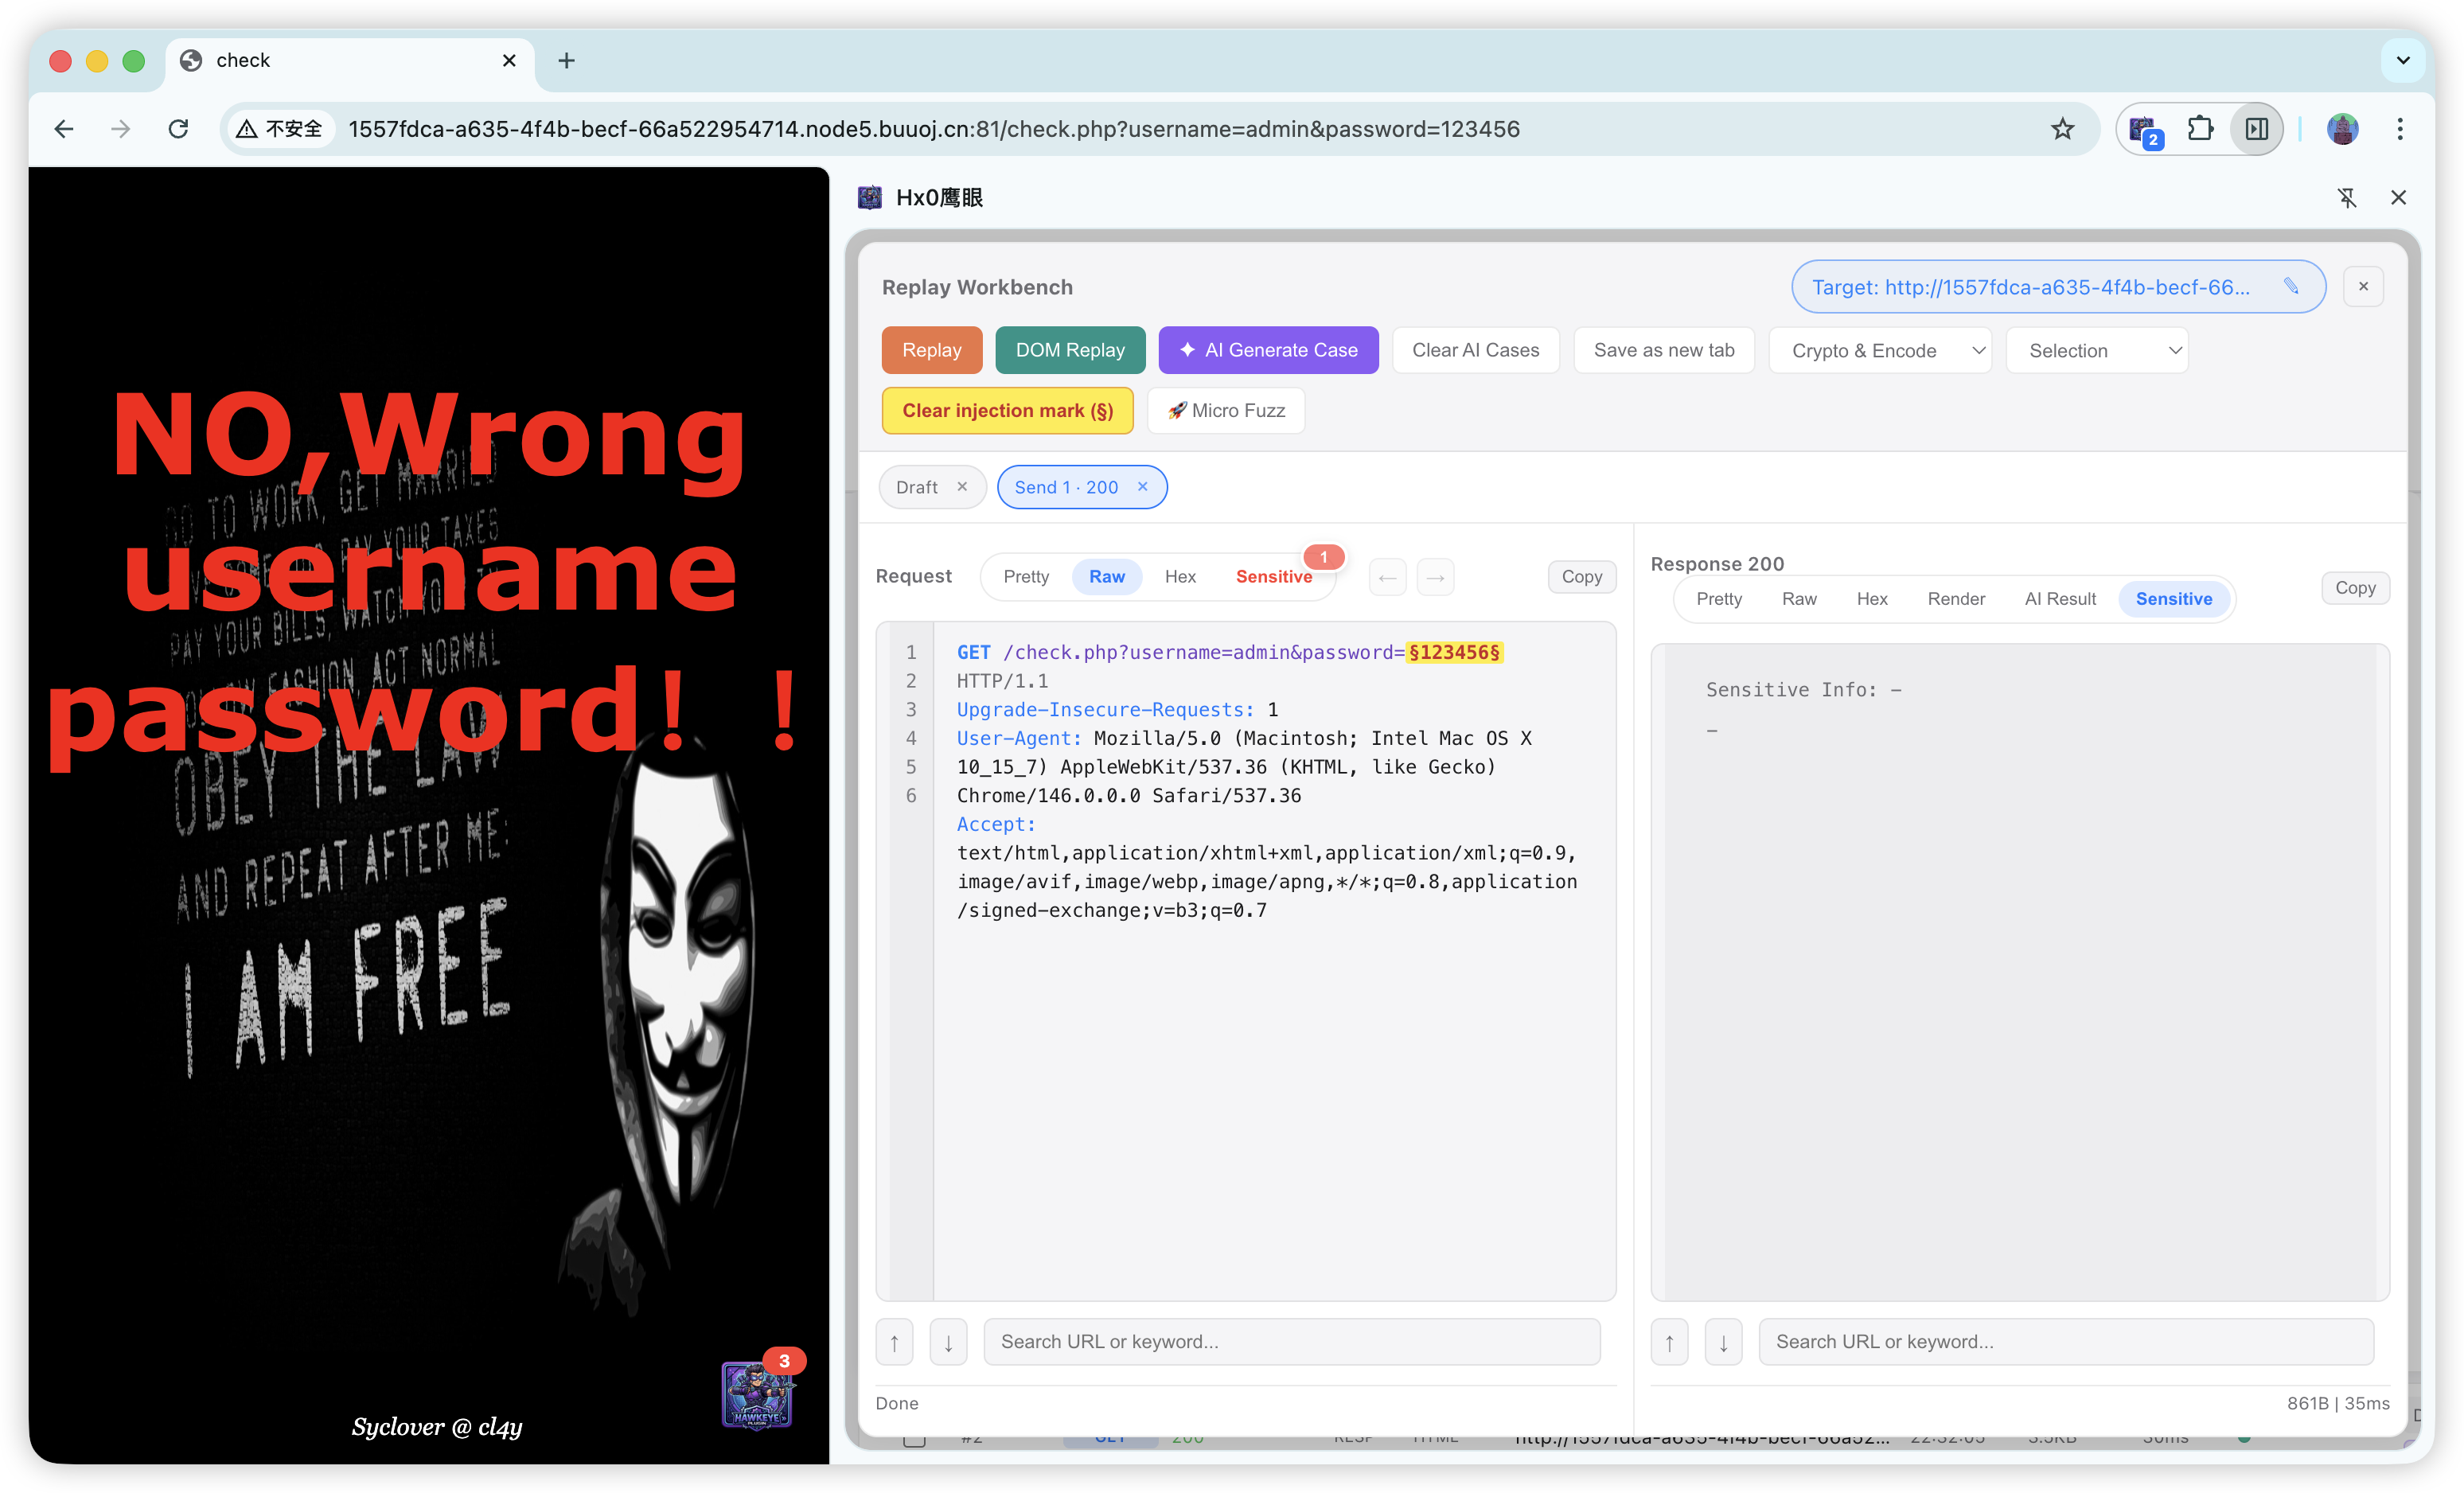
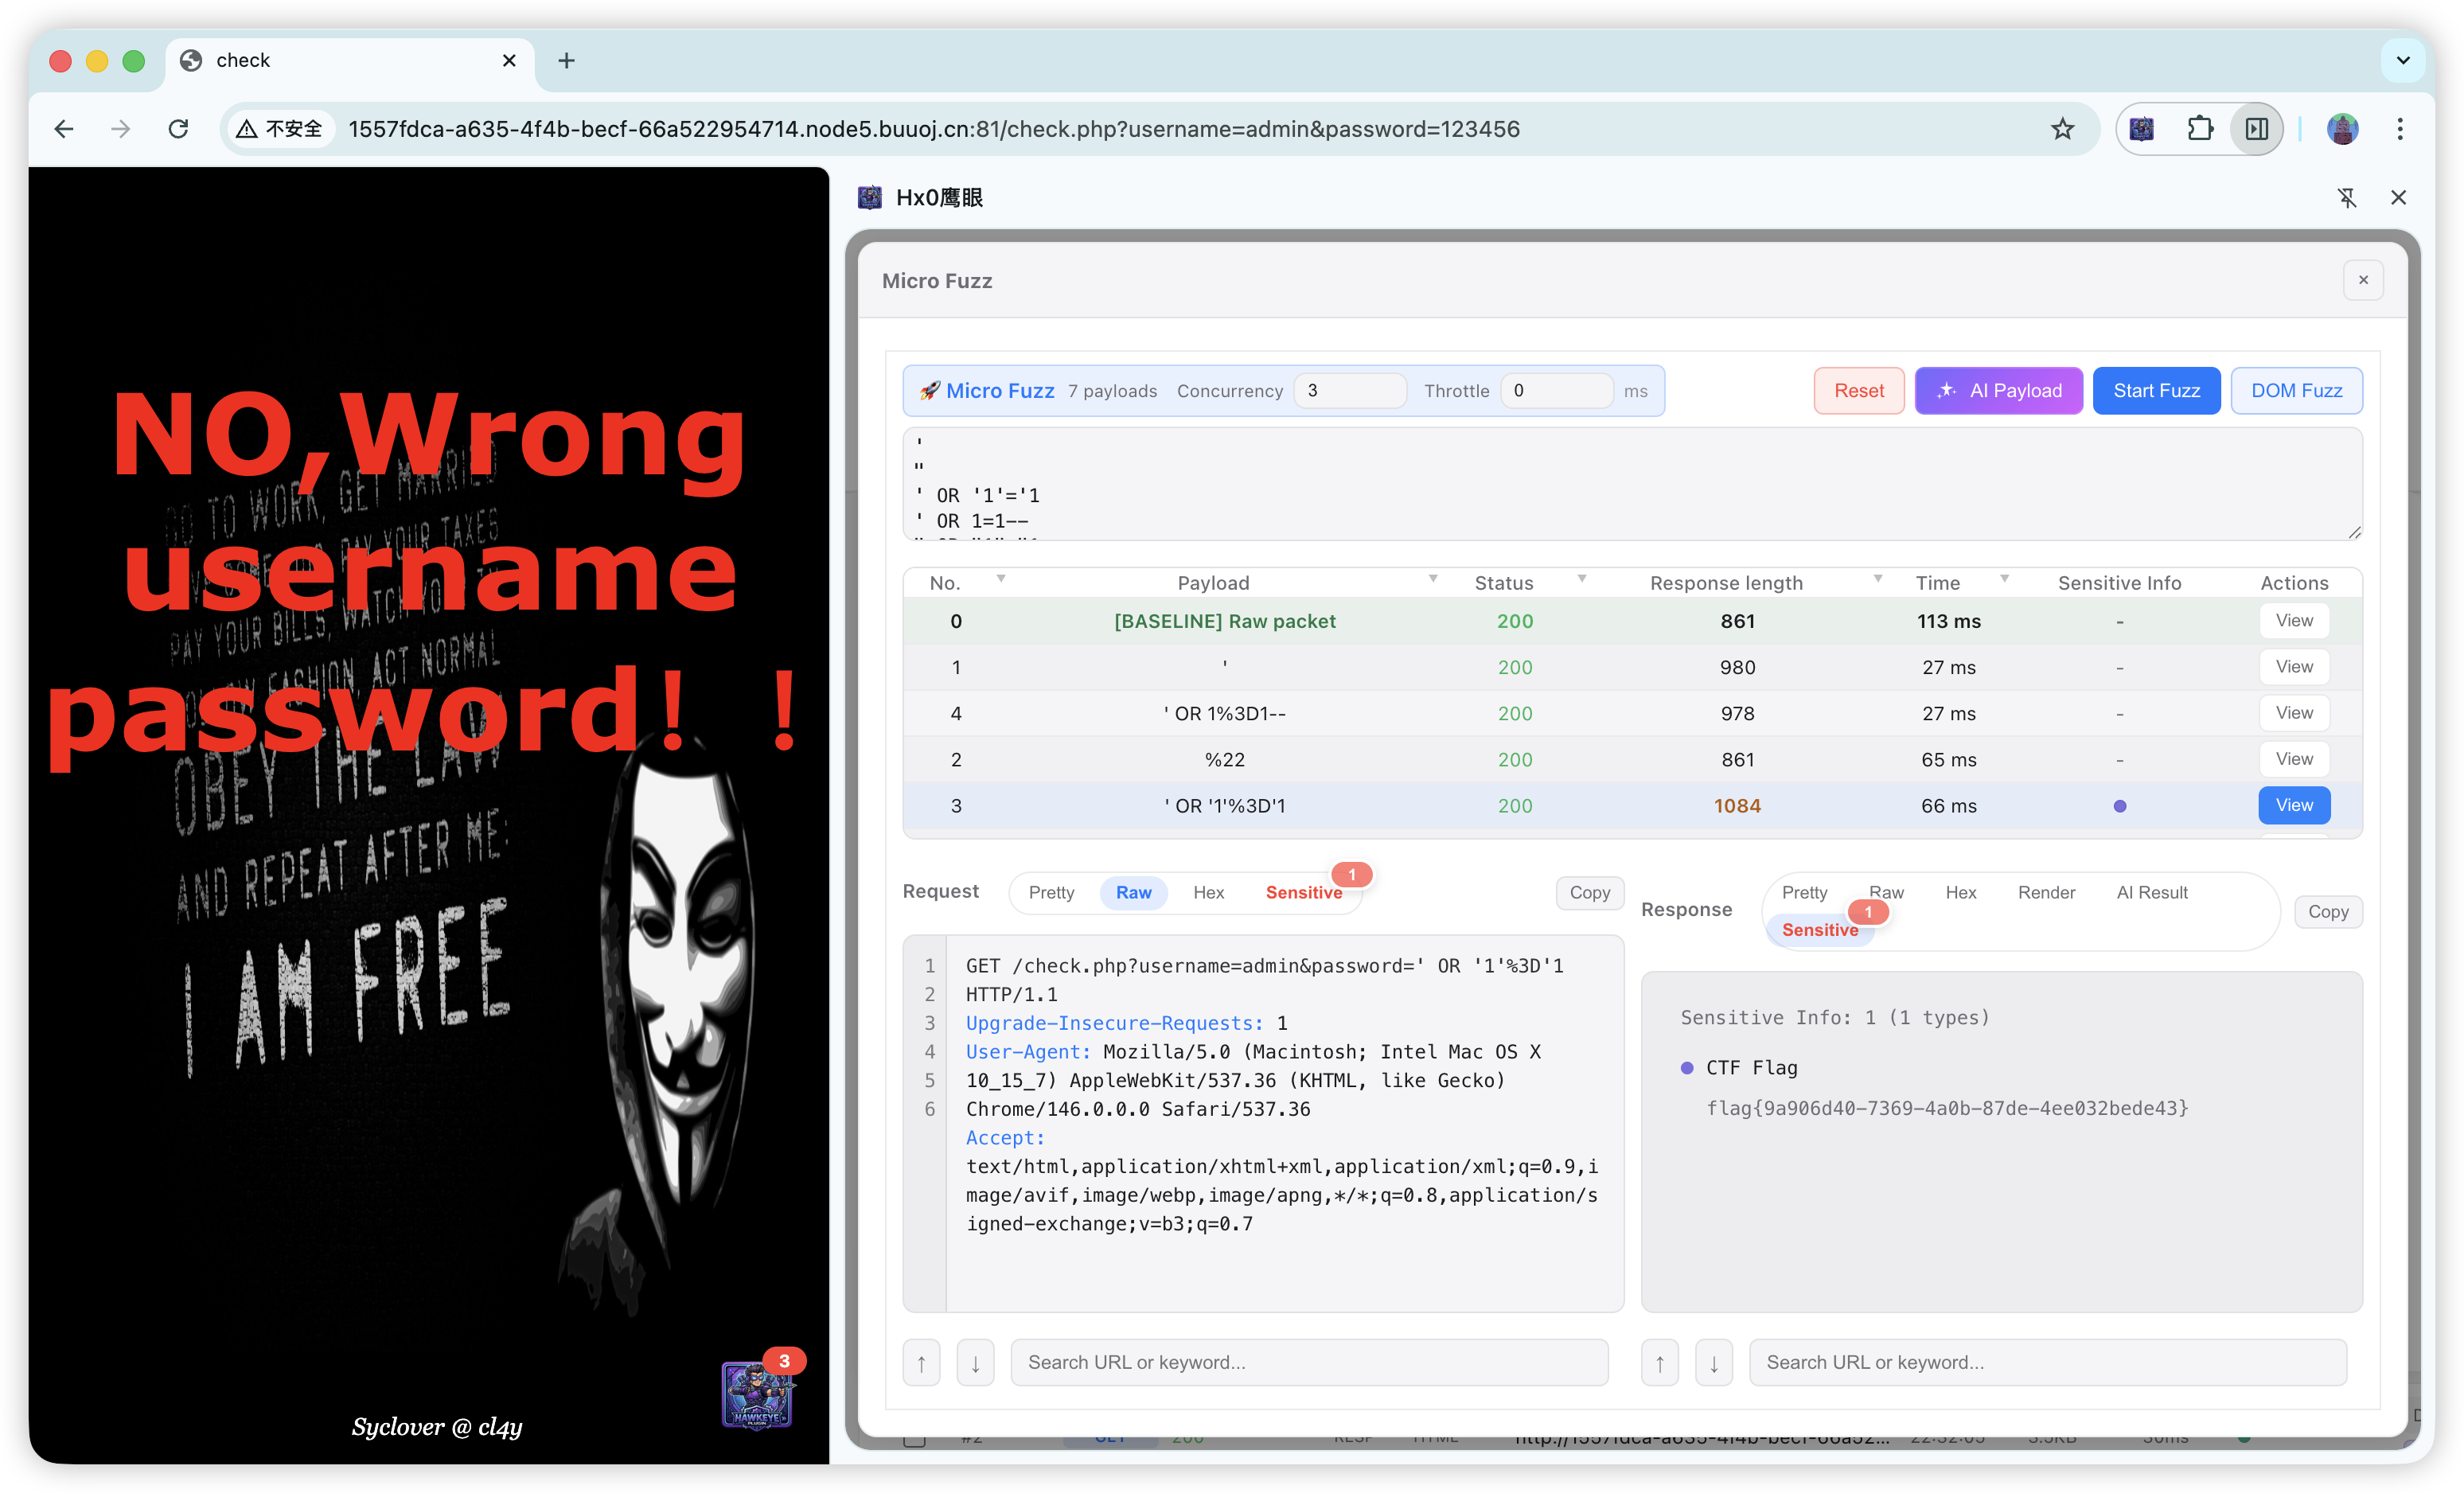
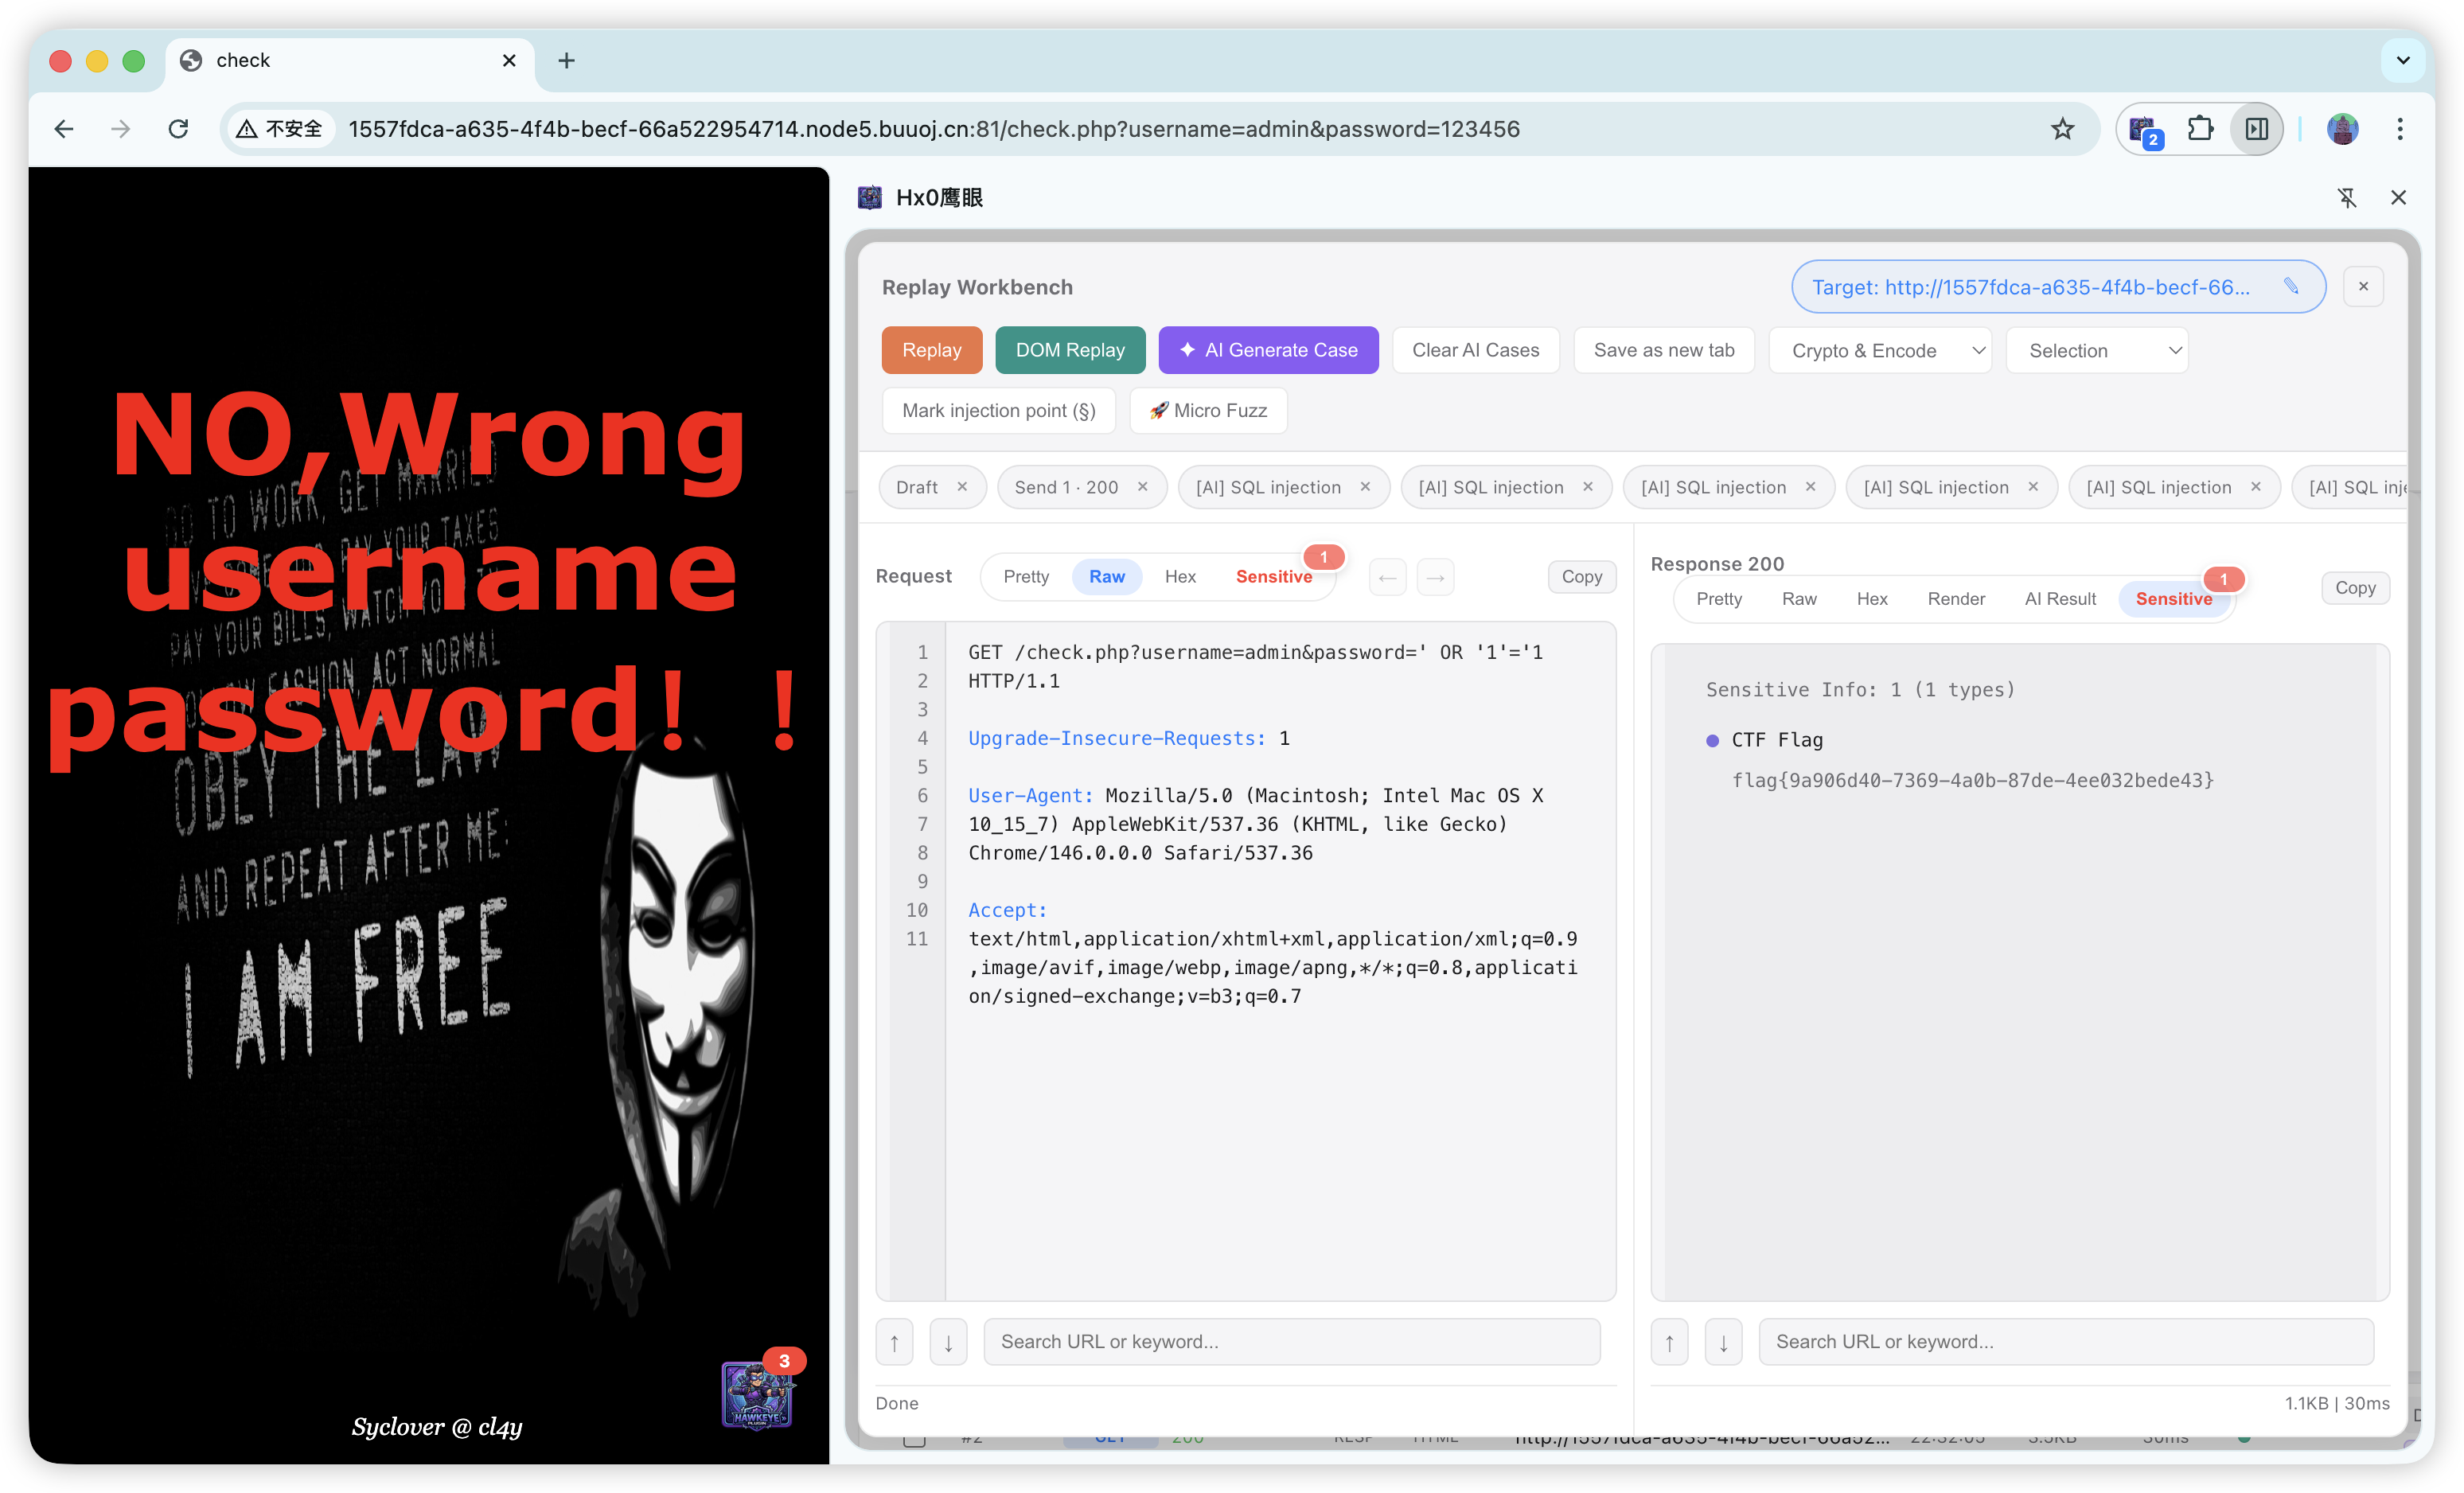
  • Smart cases & payload generation: structured test ideas in the replay workbench; context-aware mutated payloads in micro Fuzz—without bloated static wordlists.

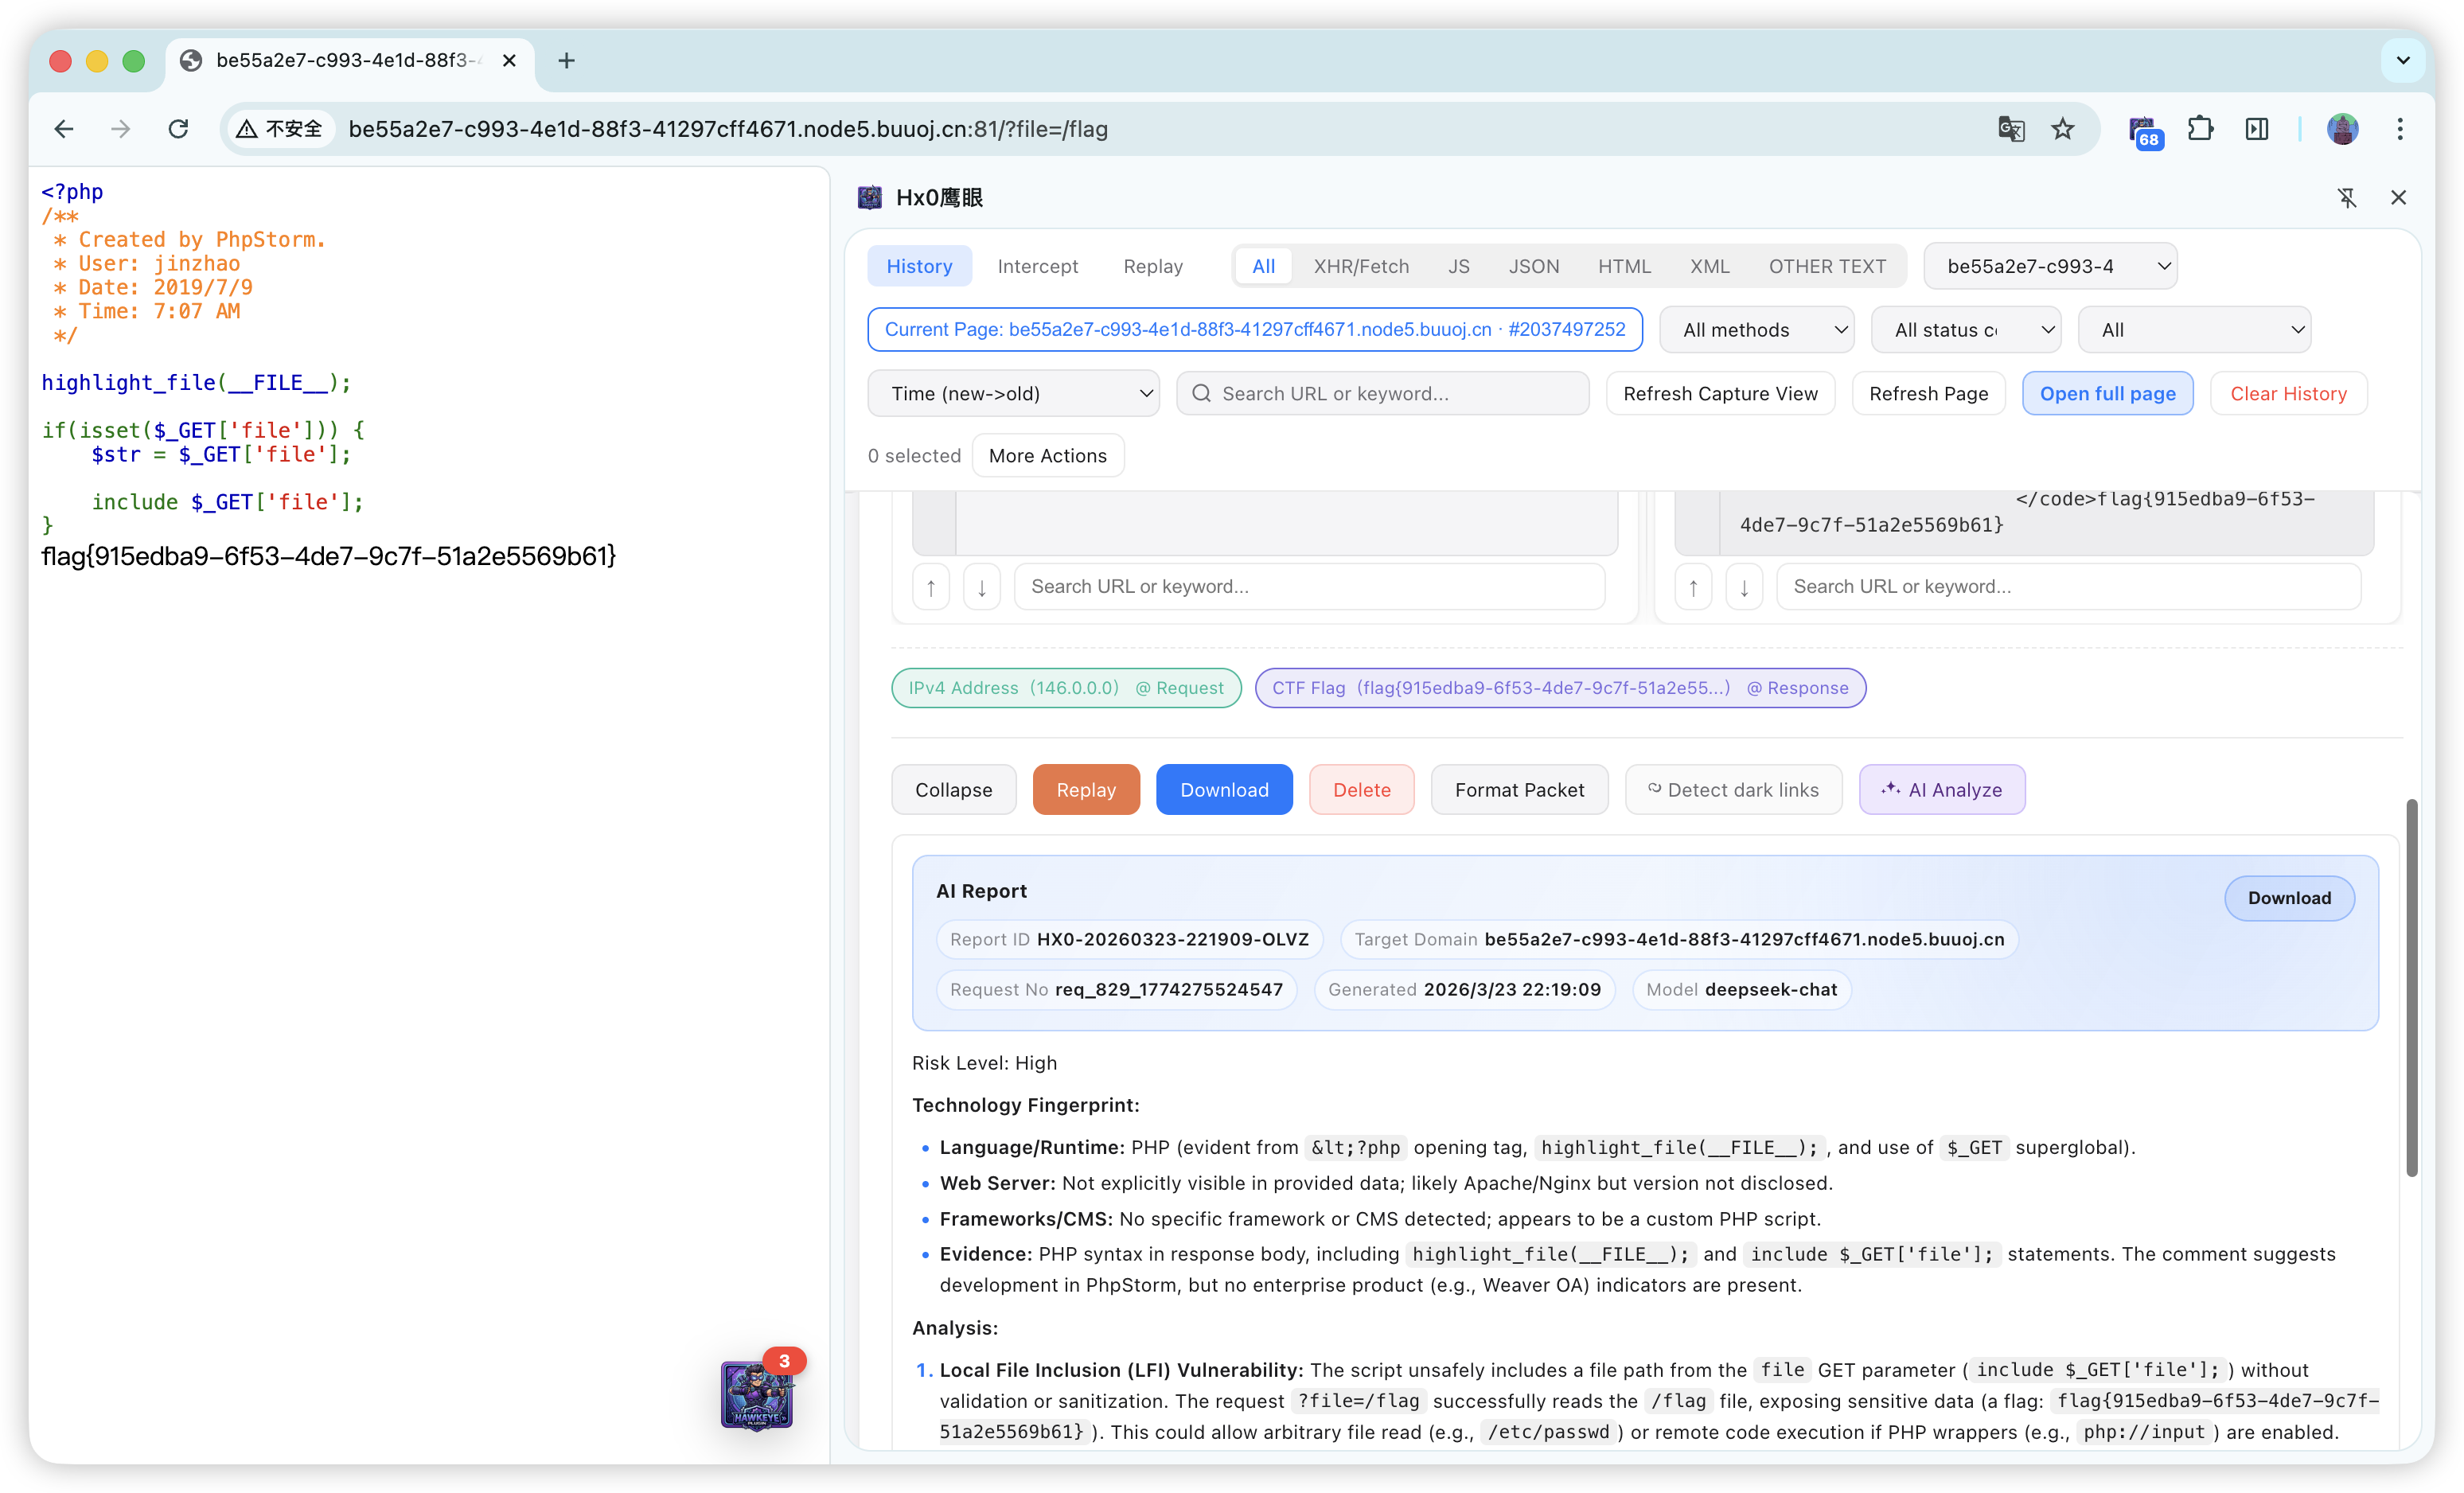
  • Deep single-request analysis: semantic AI read-through of full Request / Response for risk triage.

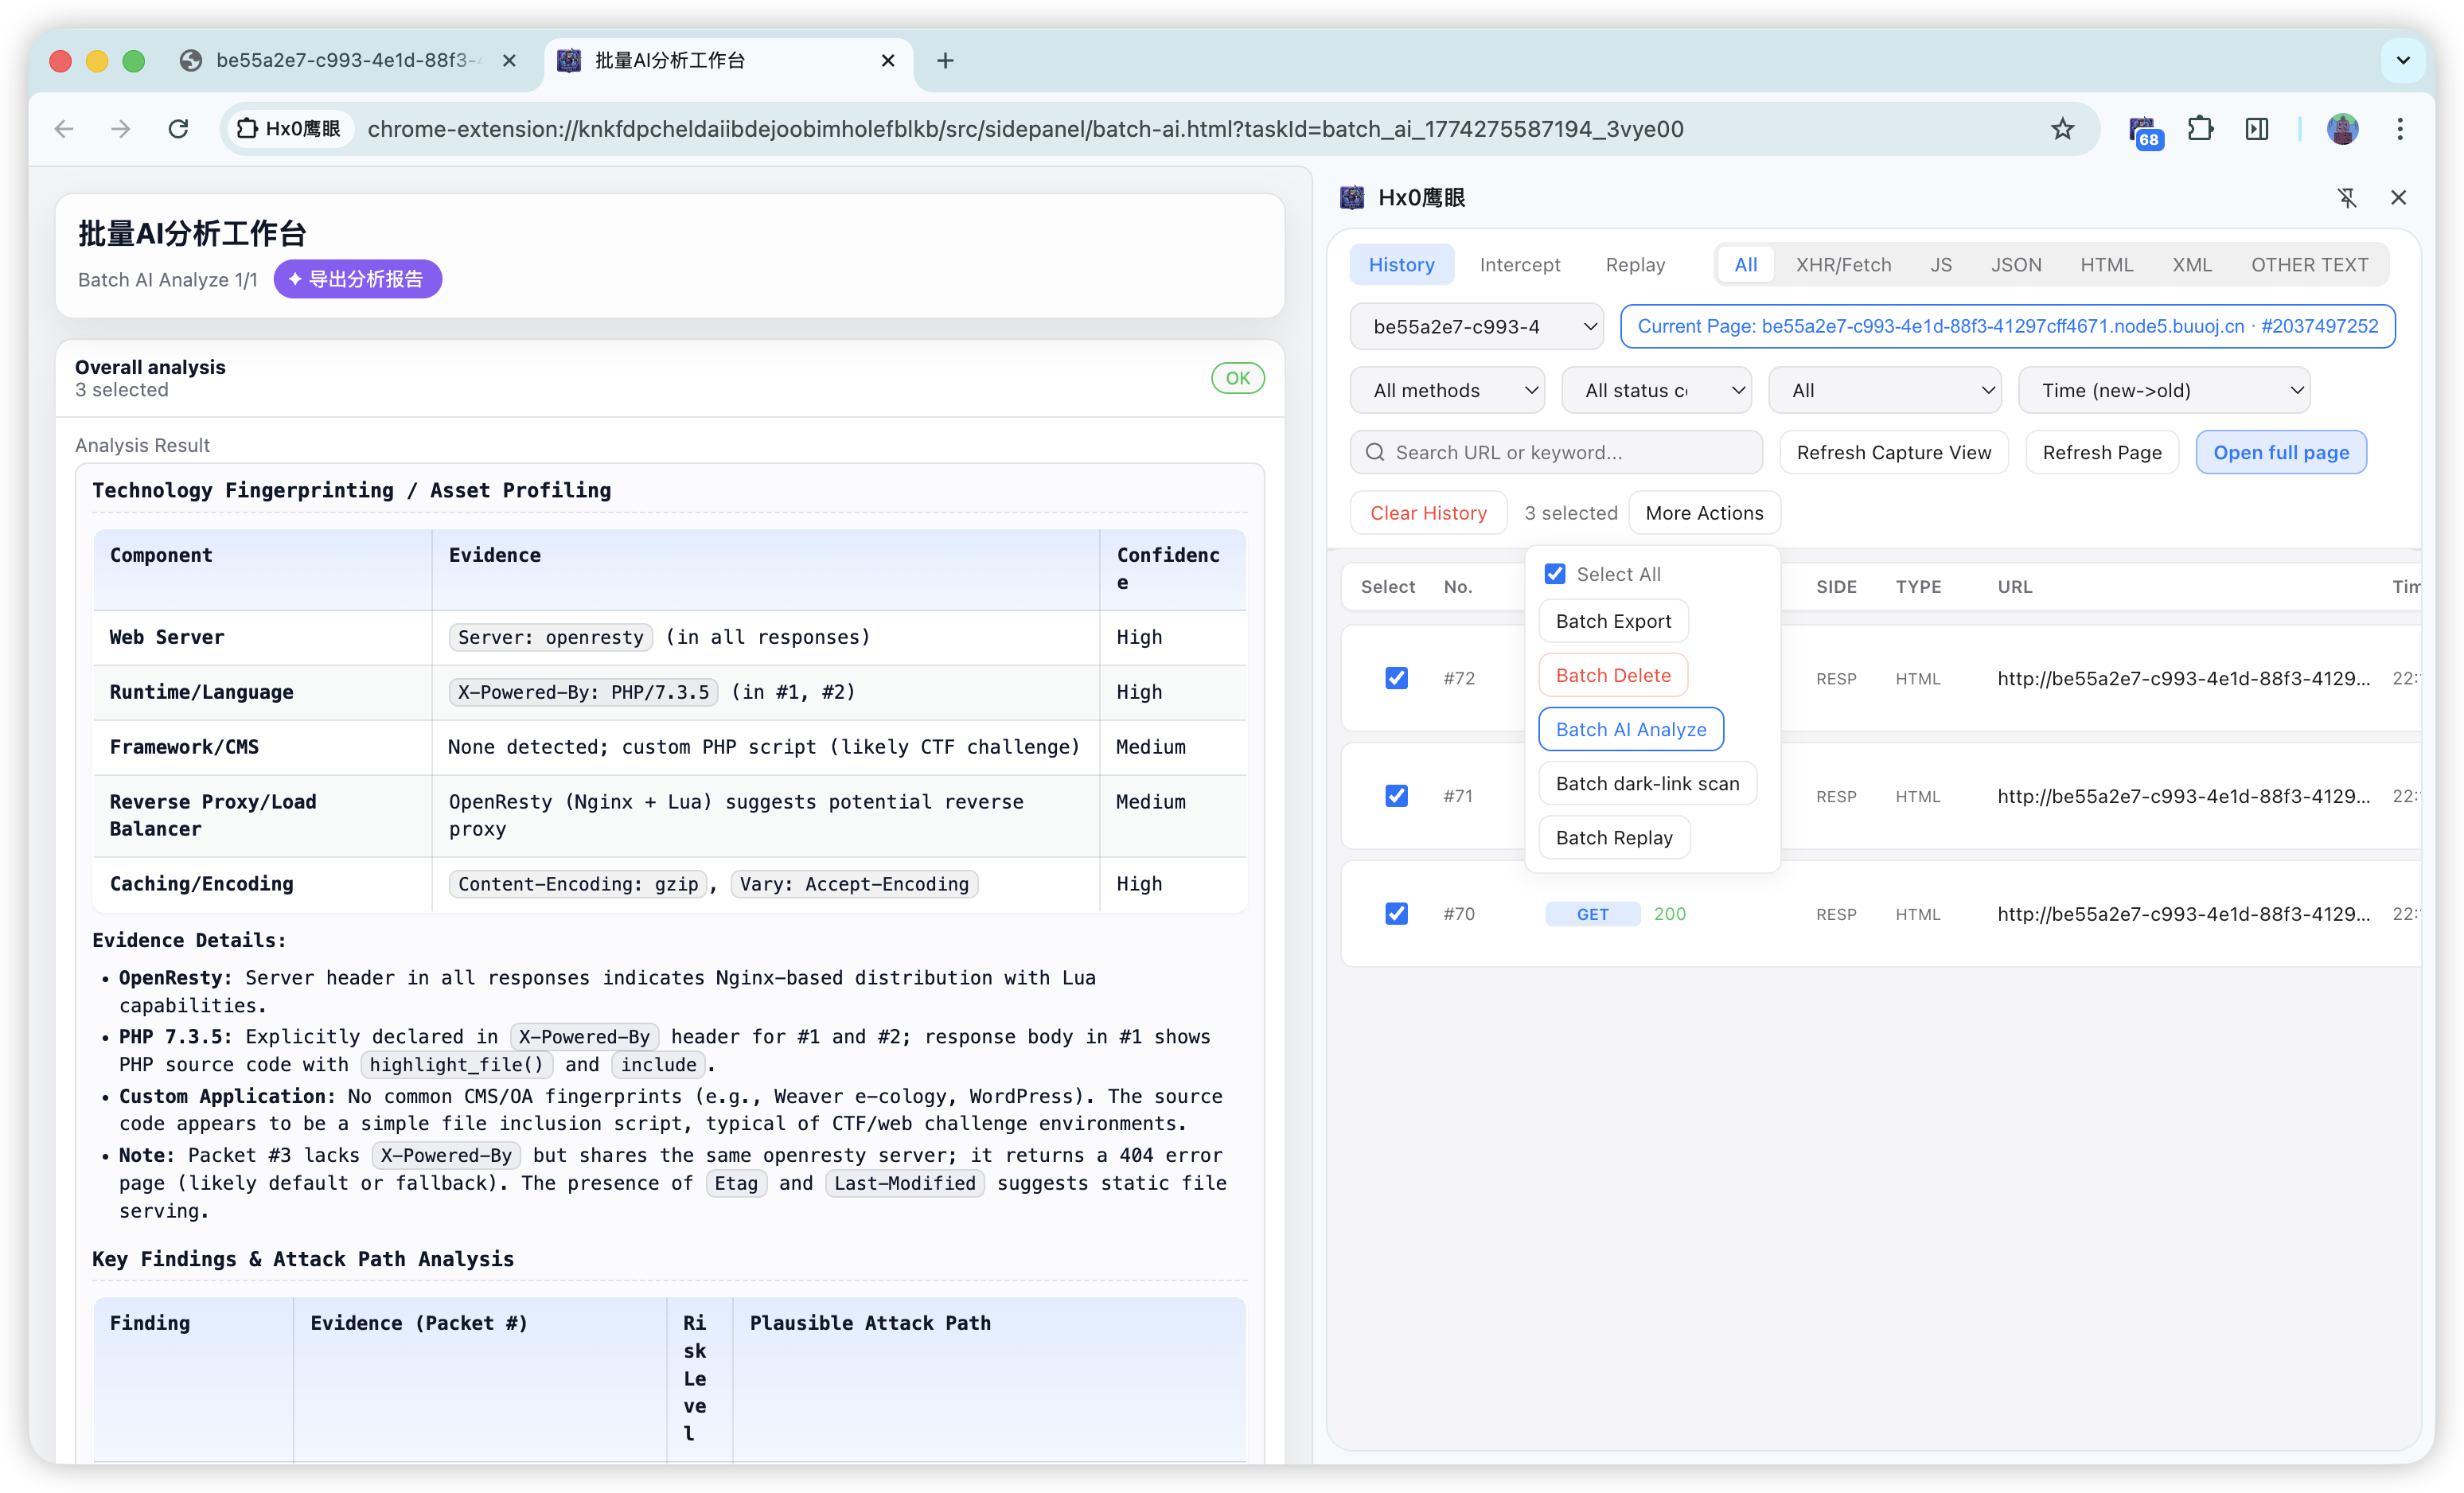
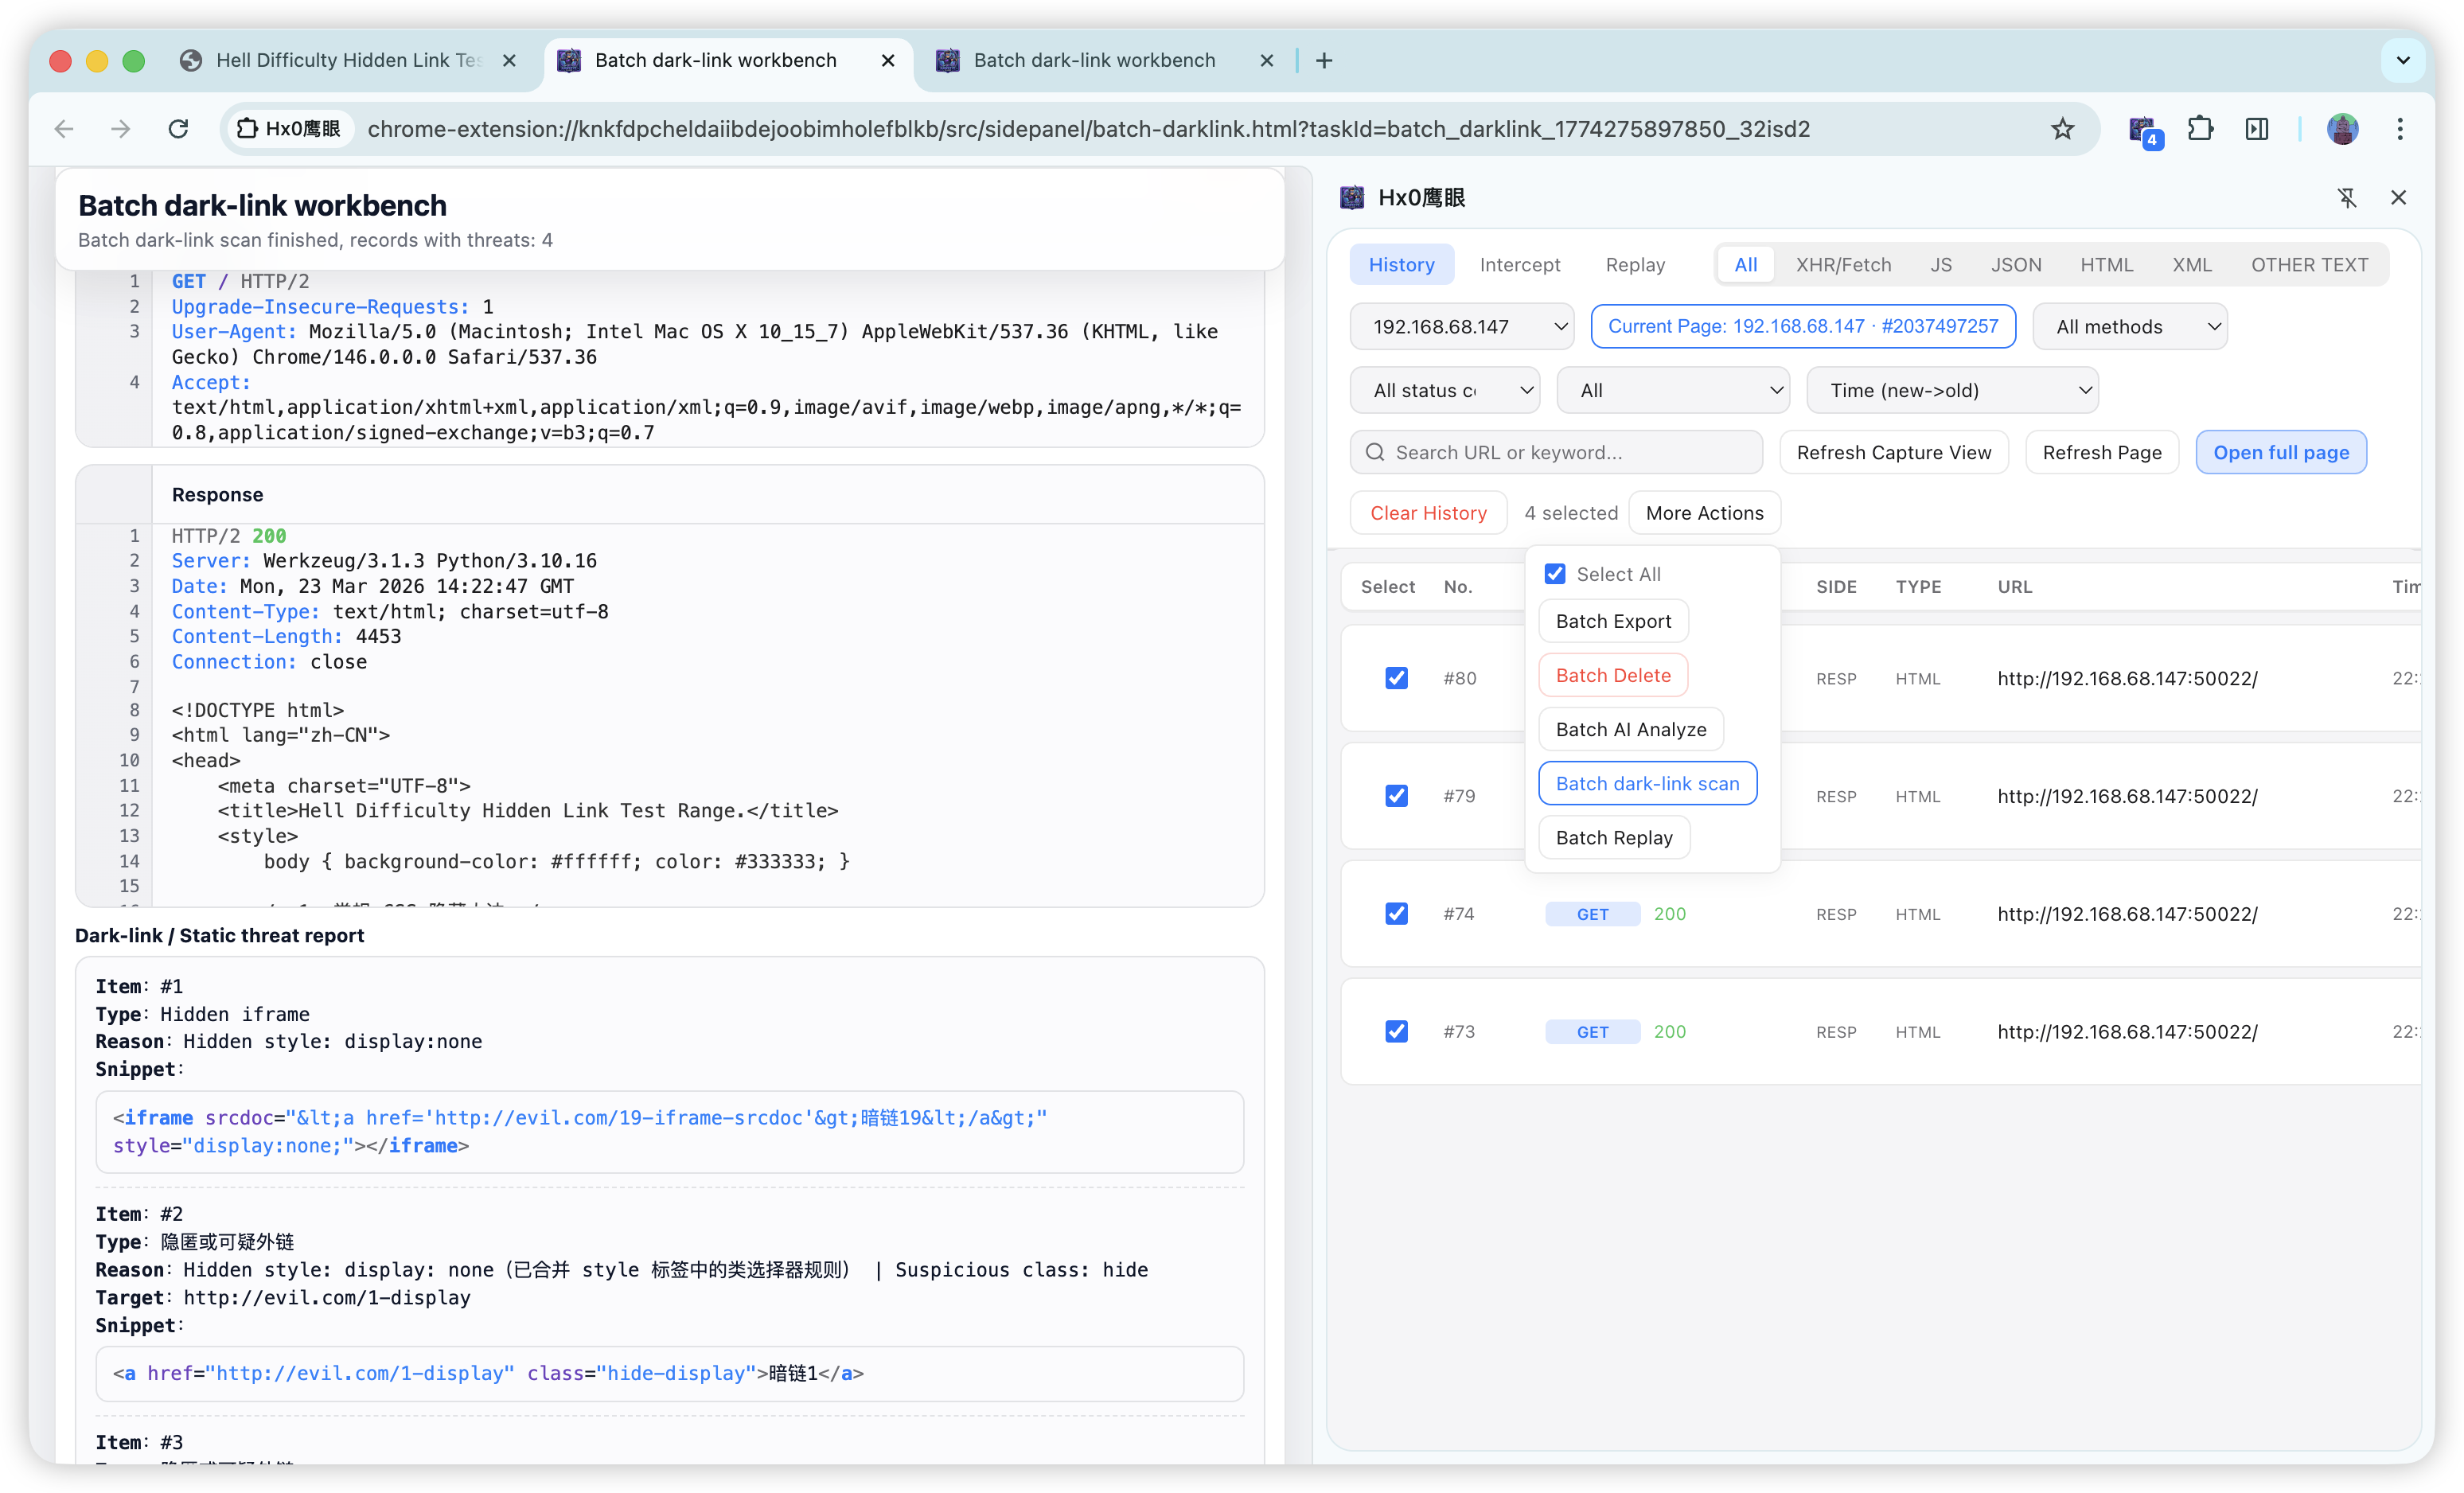
  • Batch synthesis: select multiple packets in a dedicated workbench; AI extracts patterns across APIs and third-party calls to support supply-chain / dependency-surface first-pass review.

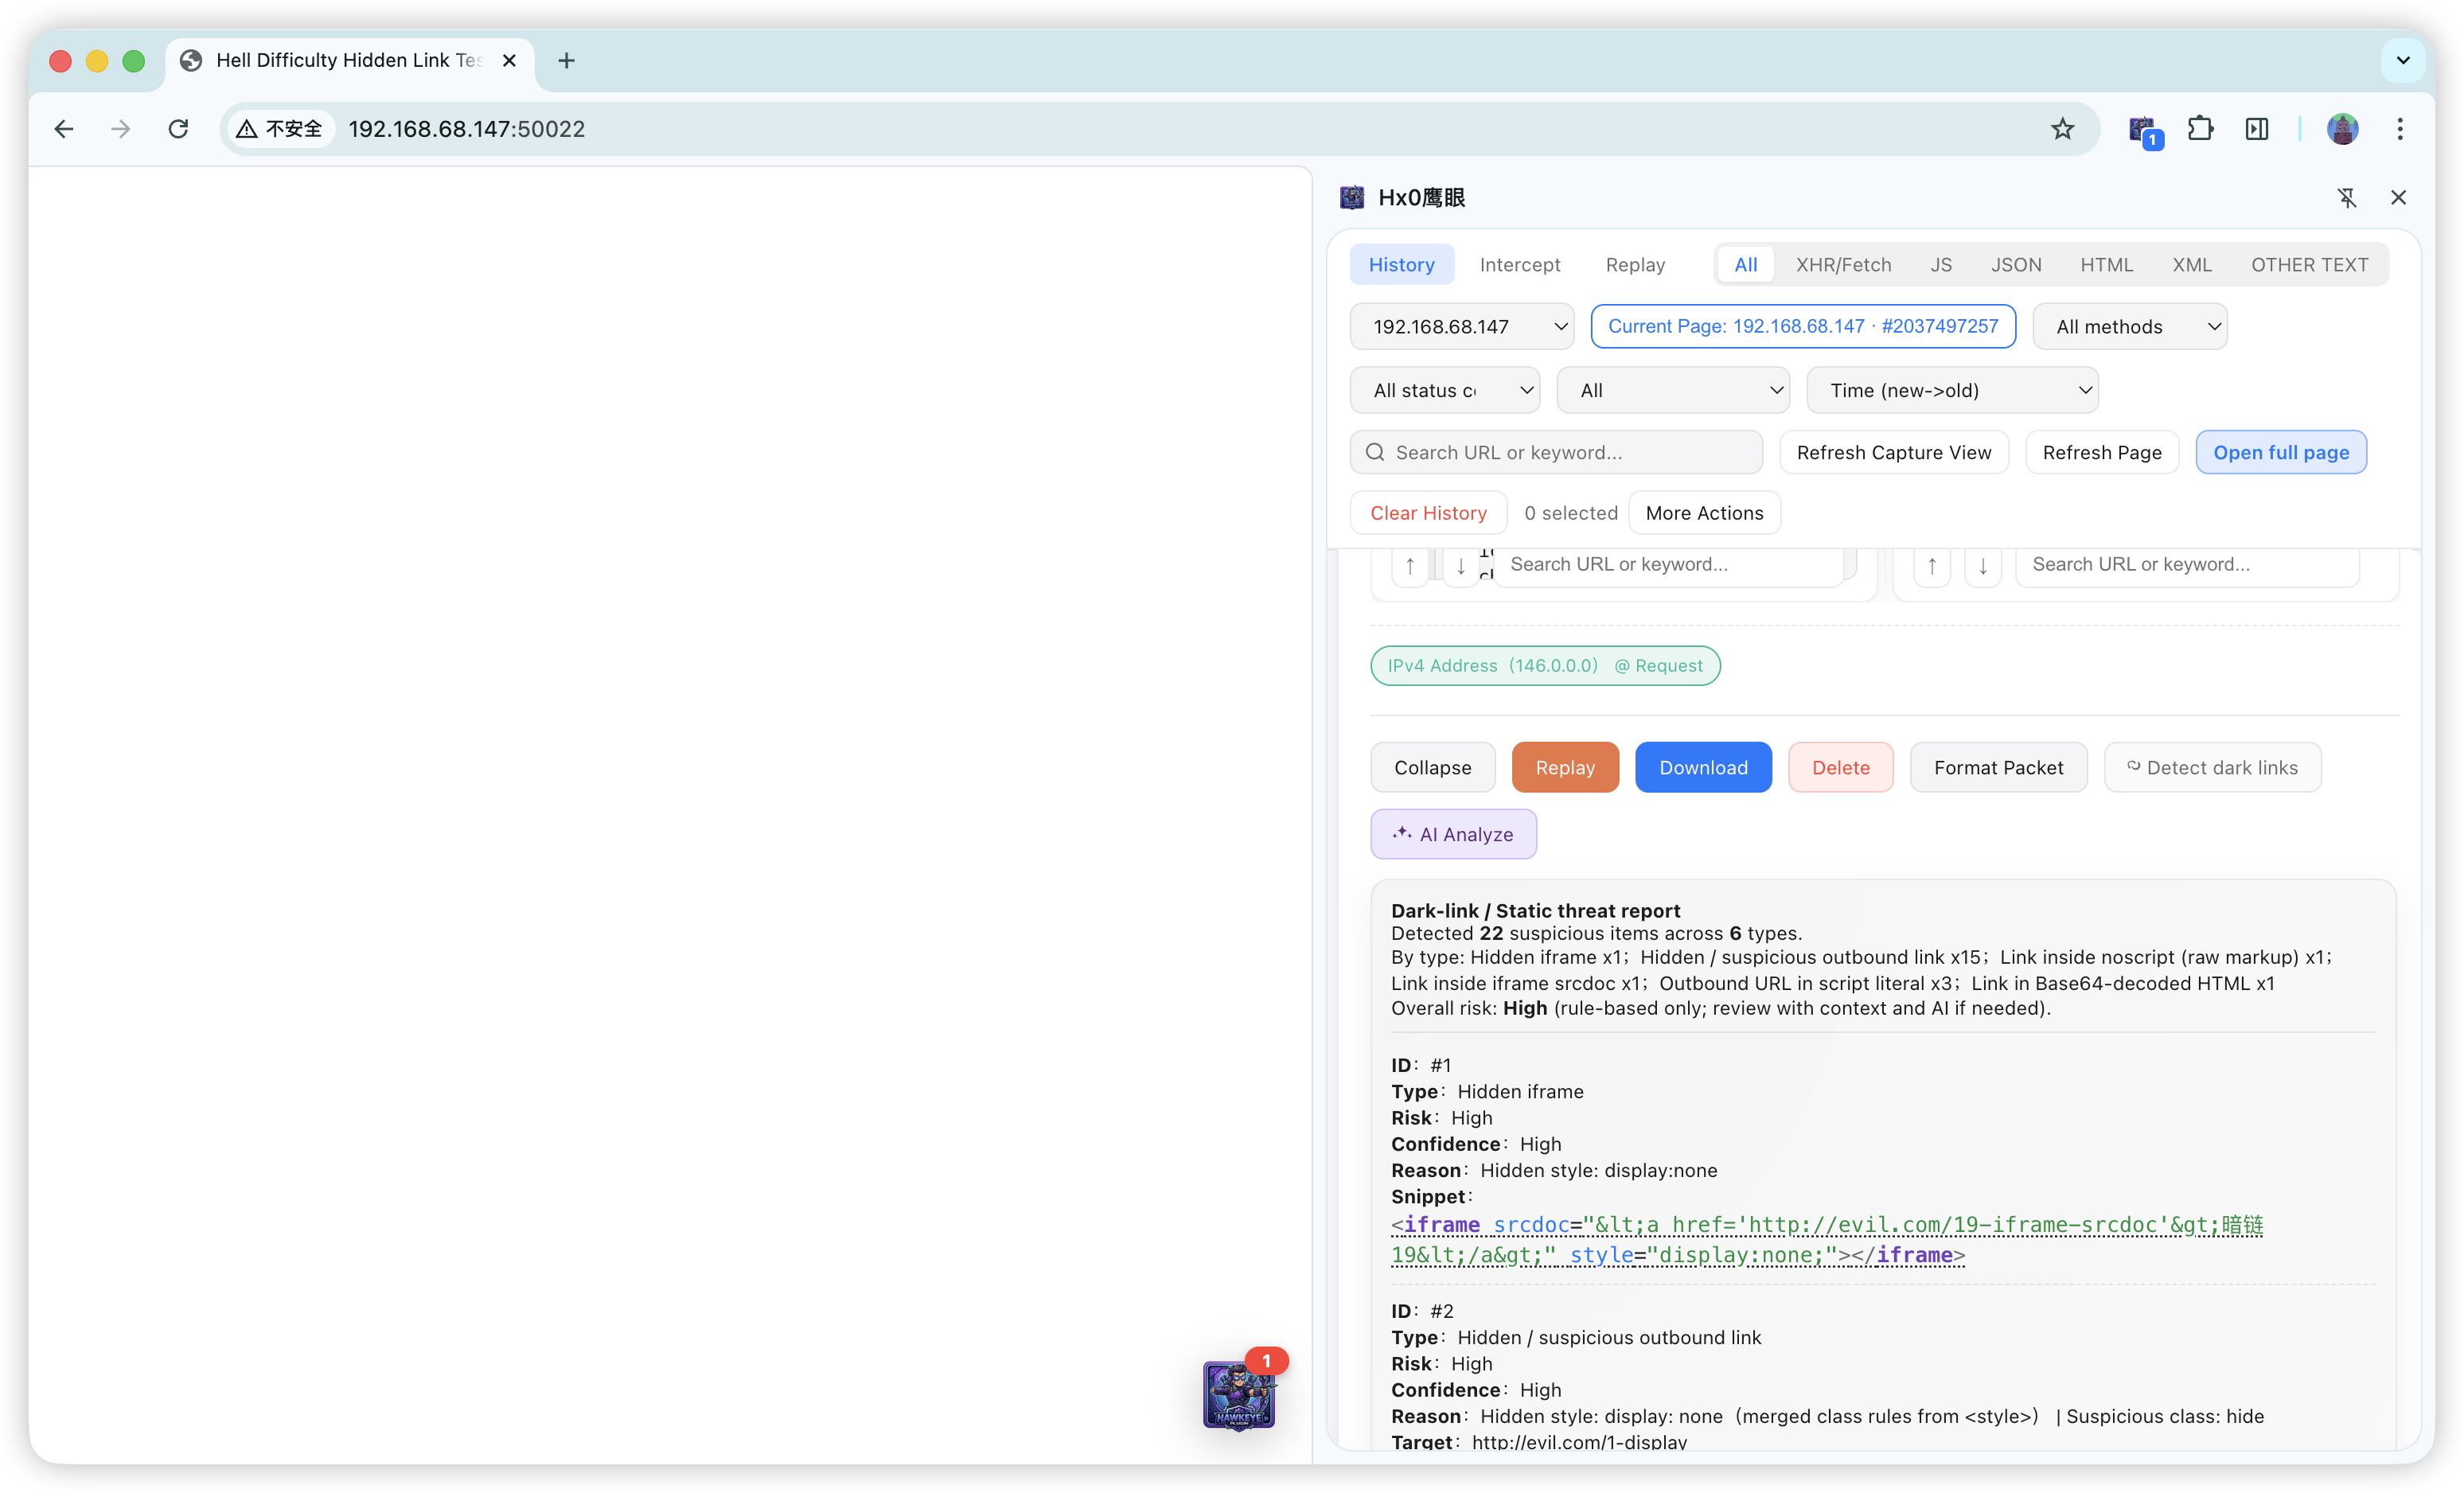
  • Dual-engine static hunting: built-in dark-link rules + AI contextual interpretation for batch replay across pages and broad static coverage.


2. Why we built it

With SPAs, heavy XHR/Fetch, and WebSocket, engineers constantly switch between “real browser session” and “capture / tamper / replay.” Classic proxies (e.g. Burp) are powerful but need system proxy and trust, and cookies / login state can diverge from the tab; lightweight toolbar extensions often lack durable history, structured detail, and a closed-loop workbench.

Hx0 HawkEye aims to keep no mandatory system proxy while folding capture (HTTP / WebSocket) → filter → detail audit → intercept → replay → micro Fuzz → sensitive & dark-link checks → optional AI into one sidebar hub, cutting context-switch cost for dev triage and authorized API review.


3. Features

Core flow: Capture (optional WebSocket) → Filter → Detail → Replay (HTTP / WebSocket frames; optional AI test cases) → Micro Fuzz (HTTP / WS; optional AI payloads) → Dark-link / AI packet analysis (including batch AI / dark-link workbenches after multi-select) → AI Task Console (Pro, multi-stage automation).
도구 다운로드