


FortinetHunter (@YogSoth0) 바이너리 크래킹 애플리케이션. FortinetHunter를 위한 CTF의 일부. ELF door: 스트립된 Nuitka onefile, XOR로 스크램블된 Argon2id 검증기, AES-GCM 무결성.
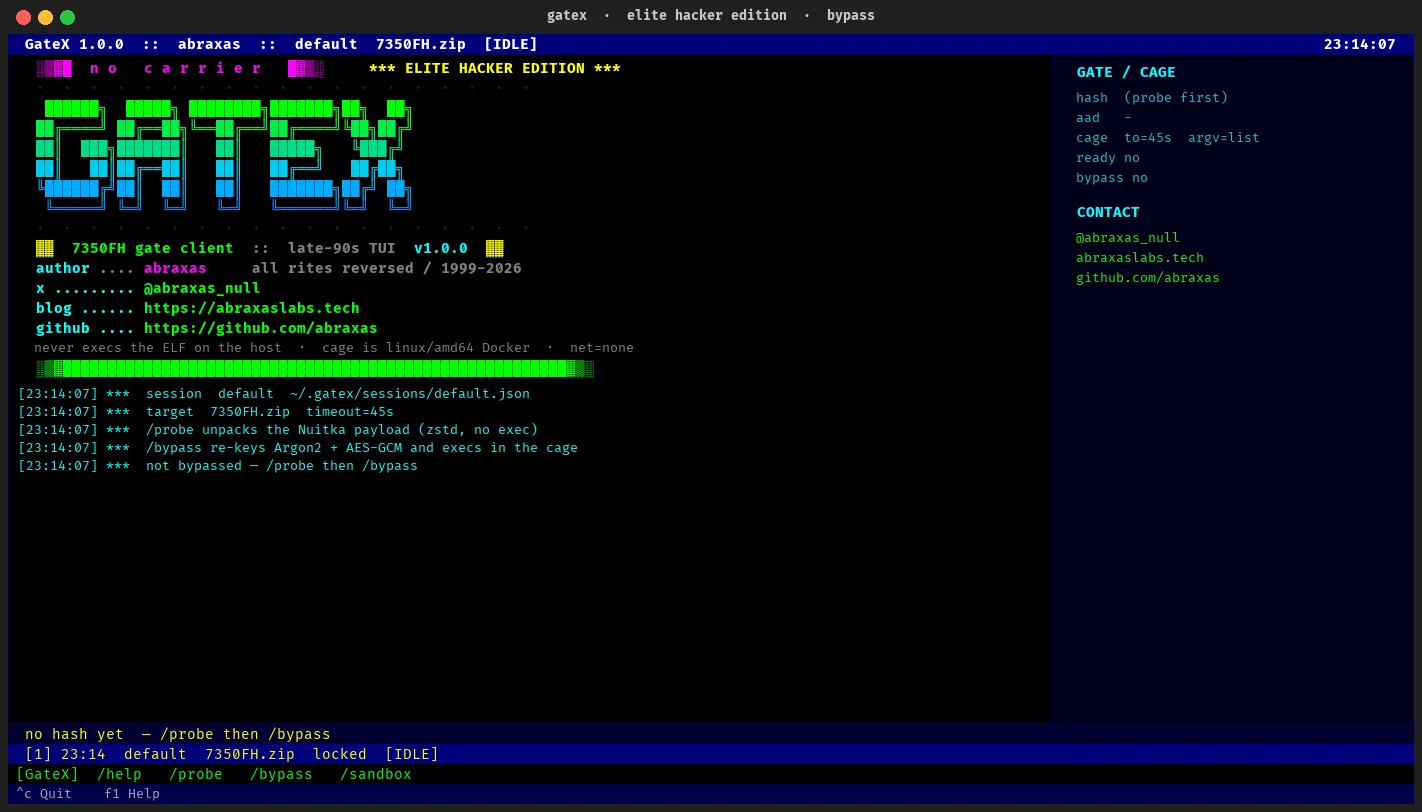
"Fortinet Hunter 2026" Nuitka 비밀번호 게이트를 재키잉(re-key) 하는 TUI. @YoSoth0의 캡처 더 플래그(capture-the-flag) 챌린지의 일부. Write-up: Hunting the Fortinet Hunter 0-day
ELF는 호스트에서 절대 실행되지 않는다. GateX는 onefile 페이로드를 정적으로 언팩하고, 뒤섞인 Argon2id 해시와 AES-GCM 배너를 XOR 언마스킹한 뒤, FH_PASS=gatex가 두 검사를 모두 통과하도록 해당 블롭을 재작성하고, 잠긴 Docker 케이지 안에서 내부 바이너리를 exec한다.
이것은 작성자의 원래 패스프레이즈를 복구하지 않는다. Argon2id(m=65536,t=3,p=4)는 제 역할을 하고 있다. 플러그인들은 이미 내부 ELF에 컴파일되어 있었고, 비밀번호는 배너를 풀어낼 뿐이다.
abraxas
7350FH.zip (제공되지 않음)페이로드는 신뢰할 수 없는 CTF 멀웨어 형태의 코드다. GateX는 다음 조건에서만 이를 exec한다:
--platform linux/amd64--network none--read-only + 언팩용 tmpfs--cap-drop ALL --security-opt no-new-privileges:true65532, 2 GiB RAM, 1 CPU, 256 pidsgit clone [email protected]:abraxas/GateX.git
cd GateX
python3 -m venv .venv
.venv/bin/pip install -r requirements.txt
챌린지 zip(또는 내부 ELF)을 GateX가 볼 수 있는 곳에 둔다:
mkdir -p files
cp /path/to/7350FH.zip files/7350FH.zip
TUI:
.venv/bin/python -m gatex --target files/7350FH.zip
TUI 내부에서:
/probe          # static zstd unpack + assemble the Argon2id hash (no exec)
/sandbox up     # start Docker, build gatex-cage:noble
/bypass         # re-key to FH_PASS=gatex and exec list in the cage
/cmd --help     # argv against the patched inner ELF
/cmd --version
/cmd score --ml
헤드리스:
# unpack + print the assembled argon2id hash (no TUI, no exec)
.venv/bin/python -m gatex --target files/7350FH.zip --probe

# re-key + exec list in the cage
.venv/bin/python -m gatex --target files/7350FH.zip --bypass
선택 사항인 --session name은 상태를 ~/.gatex/sessions/ 아래에 유지한다 (mode 0600).
| Command | What it does |
|---|---|
/help | Command list |
/probe | Static unpack + assemble Argon2id hash (no exec) |
/bypass [password] | Re-key gate blobs (default gatex) and exec in the cage |
/cmd [args…] | argv passed to the patched ELF (list, --help, --version, …) |
/sandbox /sandbox up /sandbox down | Docker status / build / destroy |
/target <zip|elf> | Switch binary |
/session name | Switch reusable session |
/timeout <seconds> | Cage exec timeout |
/quit | Save and leave |
F1 = help.
KAY + zstd)이다. 내부 이미지는 7350FH.bin이다.BYTES 상수 c + fh-slim-hardened-v2 앞에 위치한다.utf-8(xor(b64decode(ct), cycle(b64decode(key))))이다. 세 개의 조각이 실제 PHC를 조립한다. 바이너리 안의 평문 Argon2 문자열은 argon2-cffi doctest 미끼다 — 무시하라.fh-slim-v2-salt-2026 / fh-slim-v2-core) → 79바이트 배너의 AES-256-GCM. 그런 다음 cli.main(). 익스플로잇은 암호문 안에 있지 않다./bypass는 당신이 아는 비밀번호의 새 PHC를 작성하고, AAD b"fh-slim-hardened-v2"(바이트 값이며, 디스크상의 cfh-… 니들이 아님) 아래에서 대체 배너를 암호화한 뒤, 패치된 내부를 LD_LIBRARY_PATH=$ORIGIN과 함께 /opt/fh/7350FH.bin으로 실행한다.원본 내부 + FH_PASS=gatex는 여전히 [!] access denied를 출력한다. 그것이 이 실험이다.
재키잉된 내부에 대한 라이브 docker exec, linux/amd64, net none, caps dropped, uid 65532. 2026-08-26 캡처.
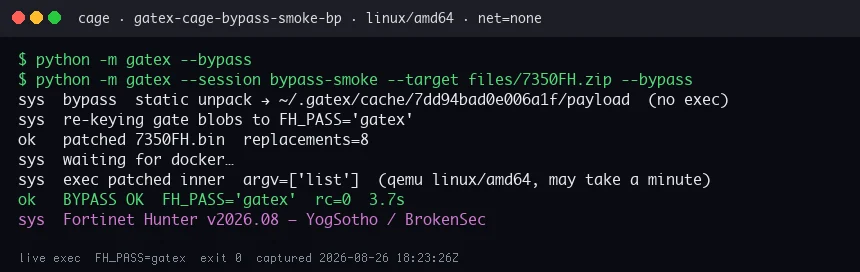
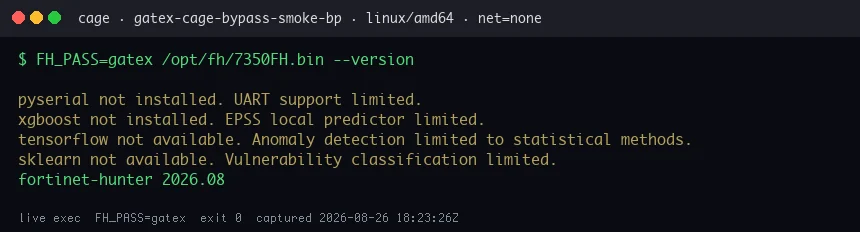
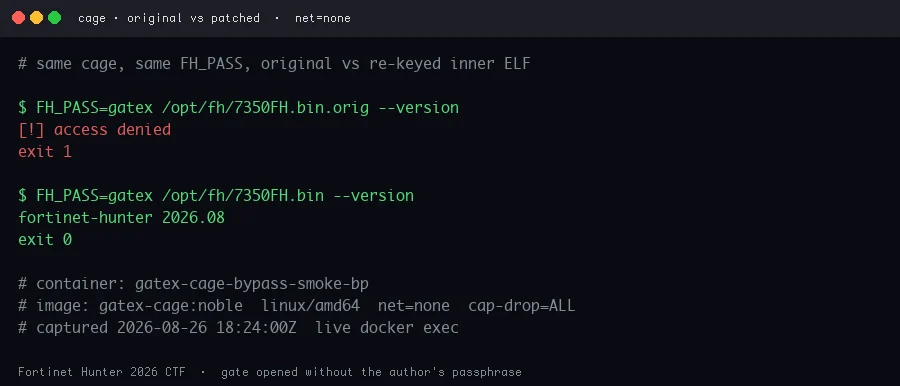
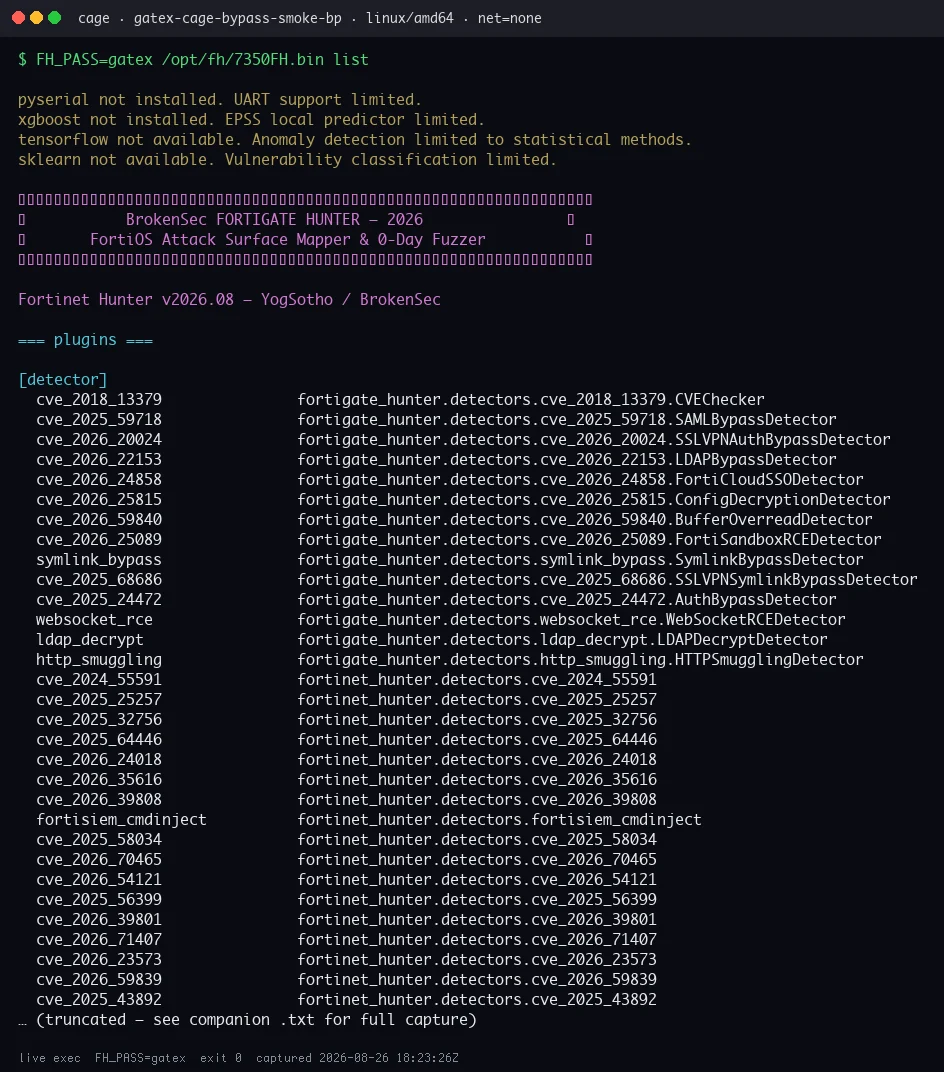
전체 트랜스크립트: files/evidence/*.txt 및 files/hunter-cli/.
.venv/bin/pip install pytest
.venv/bin/python -m pytest tests/test_offline.py -q
files/7350FH.zip이 필요한 패치/언팩 테스트는 zip이 없으면 건너뛴다.
작성자가 허가한 CTF를 위해 작성되었다. 소유하지 않은 시스템에 이것을 겨누지 마라. GateX는 익스플로잇도, 7350FH의 사본도 제공하지 않는다.
