
 0xblackash/cve-2026-20253
CVE-2026-20253

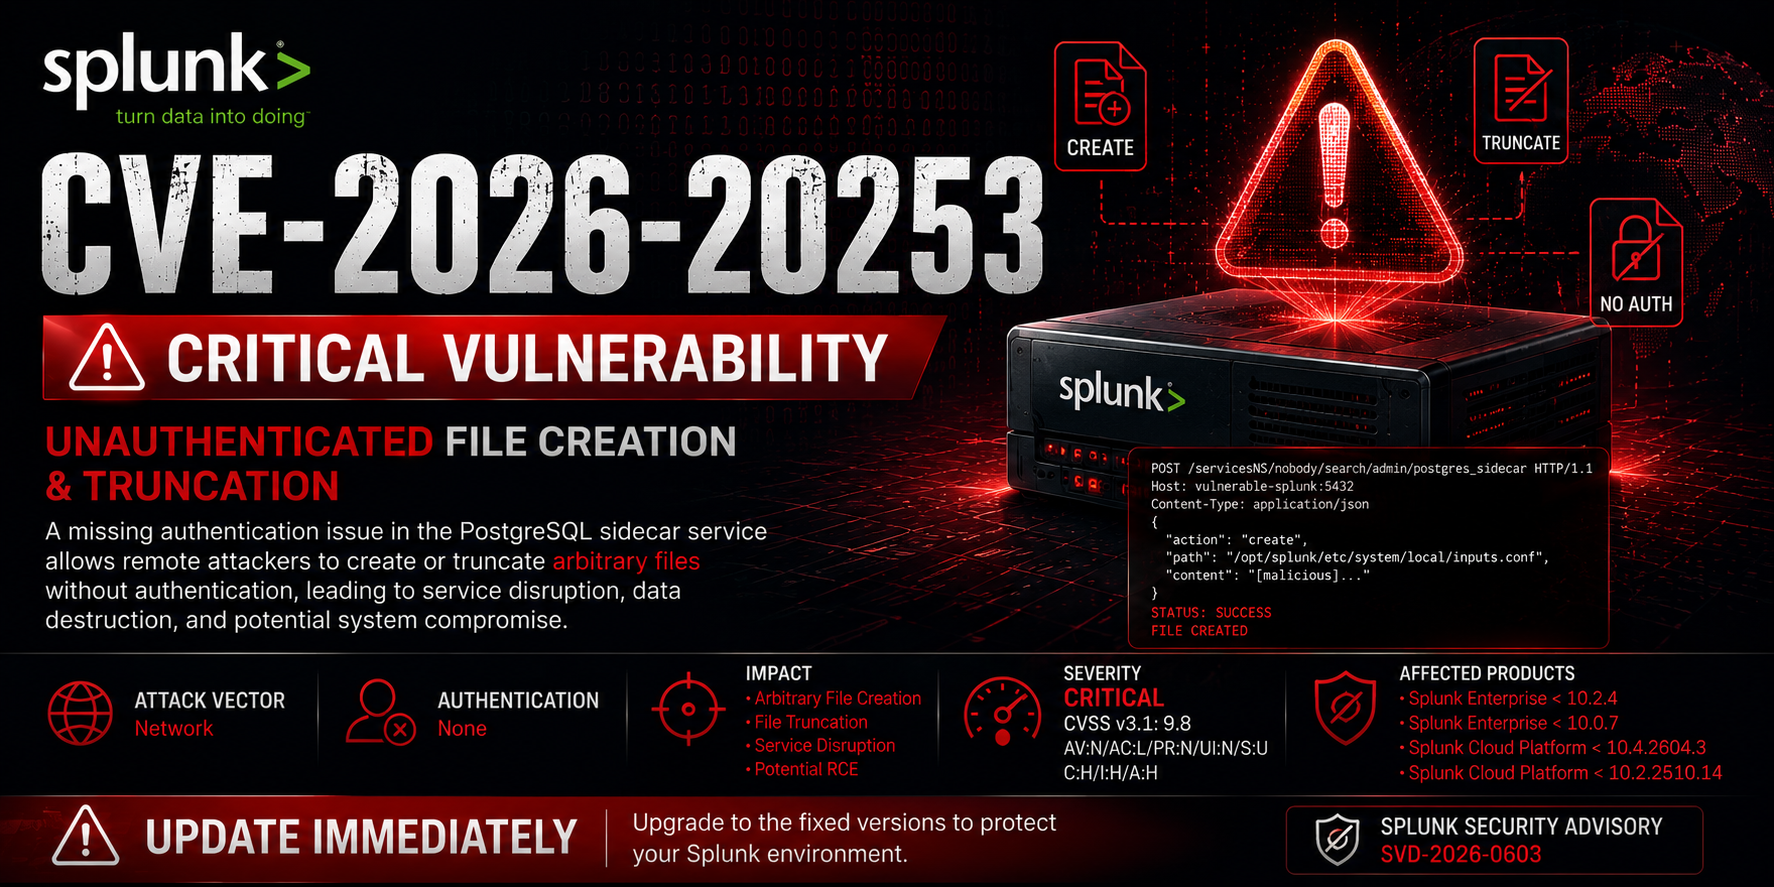


Splunk Enterprise 및 Splunk Cloud Platform에 영향을 미치는 무인증 임의 파일 생성 및 잘라내기 취약점
CVE-2026-20253은 Splunk Enterprise 및 Splunk Cloud Platform의 중요한 취약점으로, 노출된 PostgreSQL 사이드카 서비스 엔드포인트를 통해 인증되지 않은 원격 공격자가 임의 파일을 생성하거나 잘라낼 수 있습니다.
취약한 기능에 인증 제어가 없기 때문에 공격자는 유효한 자격 증명 없이 파일 작업을 수행할 수 있습니다.
성공적인 악용은 다음을 초래할 수 있습니다:
| 속성 | 값 |
|---|---|
| CVE | CVE-2026-20253 |
| 공급업체 | Splunk |
| 심각도 | Critical |
| CVSS v3.1 | 9.8 |
| CWE | CWE-306 |
| 취약점 유형 | 인증 누락 |
| 공격 경로 | 네트워크 |
| 인증 | 없음 |
| 사용자 상호작용 | 없음 |
| 영향 | 파일 생성 / 파일 자르기 |

취약점은 민감한 파일 작업 기능을 노출하는 PostgreSQL 사이드카 서비스 구성 요소에 존재합니다.
인증 확인 누락으로 인해:
Remote User
        │
        ▼
Accessible Sidecar Endpoint
        │
        ▼
Create Arbitrary Files
        │
        ▼
Truncate Existing Files
        │
        ▼
System Impact
공격자는 노출된 서비스에 대한 네트워크 액세스만 있으면 됩니다.
Attacker
    │
    ▼
Locate Exposed Splunk Service
    │
    ▼
Connect To PostgreSQL Sidecar
    │
    ▼
Unauthenticated Request
    │
    ▼
Create/Overwrite Files
    │
    ▼
Service Disruption
    │
    ▼
Potential Escalation
Potential exposure of sensitive operational data.
Arbitrary file modification can compromise system integrity.
Critical files may be truncated, causing outages.
SIEM infrastructure may become unreliable or unavailable.
| 버전 | 상태 |
|---|---|
| < 10.2.4 | 취약 |
| < 10.0.7 | 취약 |
| 버전 | 상태 |
|---|---|
| < 10.4.2604.3 | 취약 |
| < 10.2.2510.14 | 취약 |
| 제품 | 안전한 버전 |
|---|---|
| Splunk Enterprise | 10.2.4+ |
| Splunk Enterprise | 10.0.7+ |
| Splunk Cloud Platform | 10.4.2604.3+ |
| Splunk Cloud Platform | 10.2.2510.14+ |
CVSS:3.1/AV:N/AC:L/PR:N/UI:N/S:U/C:H/I:H/A:H
| 측정 항목 | 값 |
|---|---|
| 공격 경로 | 네트워크 |
| 공격 복잡성 | 낮음 |
| 필요 권한 | 없음 |
| 사용자 상호작용 | 없음 |
| 기밀성 | 높음 |
| 무결성 | 높음 |
| 가용성 | 높음 |
일반 포트:
8000
8089
8191
5432
http.title:"Splunk"
product:"Splunk"
http.html:"Splunk"
title="Splunk"
body="Splunk"
app="Splunk"
app:"Splunk"
예상치 못한 사항:
File creation events
File truncation events
Service failures
Configuration changes
Database sidecar access
find /opt/splunk -mtime -1
find /opt/splunk -size 0
journalctl -xe
grep -Ri "postgres" /opt/splunk/var/log/
찾을 항목:
Unexpected empty files
Modified configuration files
Splunk restart anomalies
Unauthorized service access
Network connections to sidecar components
잠재적 대상:
server.conf
inputs.conf
outputs.conf
authentication.conf
web.conf
1. Discover vulnerable Splunk instance
2. Reach PostgreSQL sidecar endpoint
3. Submit crafted request
4. Create or truncate target file
5. Observe system impact
⚠️ 무기화된 익스플로잇 코드는 의도적으로 생략되었습니다.
10.2.4+
10.0.7+
VPN-only access
Internal management network
ACL restrictions
Firewall filtering
File creation activity
Configuration modifications
Unexpected service restarts
Management Interfaces
        │
        ├── Internal VLAN
        ├── VPN Access
        └── Zero Trust Controls
활성화:
Auditd
Sysmon for Linux
EDR telemetry
Network monitoring
이 취약점이 중요한 이유:
Splunk가 손상되면 조직의 공격 탐지 능력이 크게 영향을 받을 수 있습니다.
CVE-2026-20253/
│
├── README.md
│
├── assets/
│   ├── CVE-2026-20253.png
│   └── screenshots/
│
├── advisory/
│   ├── technical-analysis.md
│   ├── attack-surface.md
│   └── patch-guidance.md
│
├── detection/
│   ├── sigma/
│   ├── yara/
│   ├── splunk-searches/
│   └── hunting-guide.md
│
├── iocs/
│   └── indicators.md
│
└── references/
    └── links.md
이 저장소는 다음 목적으로만 사용됩니다:
모든 테스트는 귀하가 소유하거나 명시적으로 평가 권한을 부여받은 시스템에서만 수행해야 합니다.
Splunk Enterprise • Critical • CVSS 9.8


