
foxguard v0.13.0
빠른 범용 코드 보안 스캐너로, Rust로 작성되었습니다. 모든 기능이 포함되어 있습니다: 14개 언어 지원, 분류를 위한 TUI, 비밀 정보, 양자 이후 감사, 차이 인식 스캔 등 𓃥
foxguard
Fast local security scanning for code, secrets, dependencies, and crypto risk.
Integrated into 0sec, the open cybersecurity harness.


npx foxguard .
Why
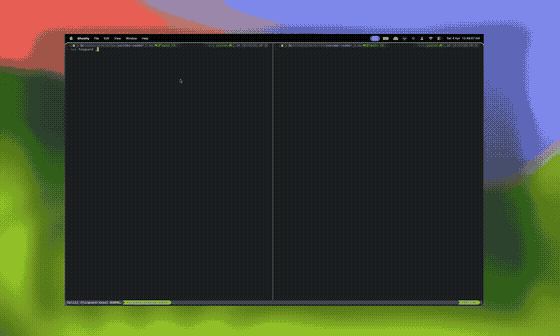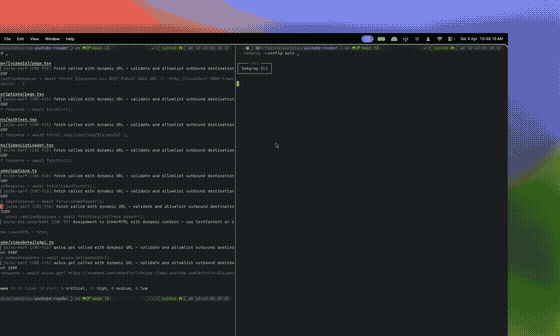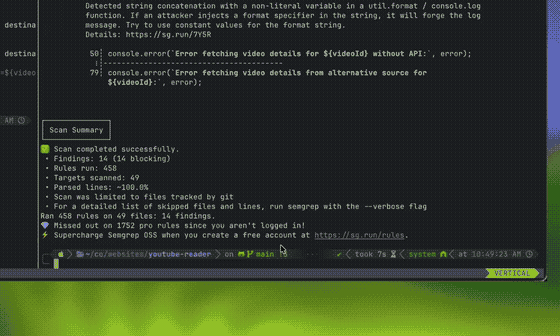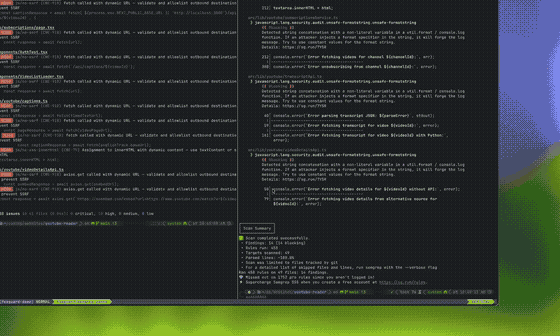
 200+ built-in rules across 12 source languages, plus config and manifest checks
 Taint tracking for 14 languages, with cross-file analysis for Python, JavaScript, Go, Java, Ruby, PHP, C#, and Kotlin
 Fast local and CI scans, with diff mode for “what did this branch add?”
 Secrets scanning, OSV-backed dependency scanning, and post-quantum crypto audit
 Semgrep/OpenGrep-compatible YAML bridge that loads ~98% of the public registry (coverage report)
 Terminal, JSON, SARIF, CycloneDX 1.6 CBOM, and Semgrep-compatible JSON output
Install
npx foxguard .                                      # zero install
pipx install foxguard                               # prebuilt CLI from PyPI
curl -fsSL https://foxguard.dev/install.sh | sh     # prebuilt binary (macOS/Linux)
cargo install foxguard                              # from source
Standalone binary installers verify GitHub release binaries against checksums.txt. Release binaries also publish GitHub artifact attestations; use gh attestation verify for manual verification, or see release provenance.
PyPI wheels support Python 3.9+ on Linux glibc 2.28+ (x86_64/ARM64), macOS
(Intel/Apple Silicon), and Windows x86_64. In an existing Python virtual
environment, use python -m pip install foxguard instead. These install the native
CLI without a Rust compiler or a runtime binary download; no Python API is
provided. Alpine/musl users should use the standalone Linux release binaries.
GitHub Action:
- uses: 0sec-labs/foxguard/[email protected]
  with:
    path: .
    severity: medium
    fail-on-findings: "true"
    upload-sarif: "true"
pre-commit:
repos:
  - repo: https://github.com/0sec-labs/foxguard
    rev: v0.14.1
    hooks:
      - id: foxguard
Integrations: GitHub App, VS Code, Claude Code plugin, and MCP server.
Hosted GitHub App operations
foxguard-github-app writes newline-delimited JSON logs. Completed and failed
scans use event=foxguard.scan.completed and event=foxguard.scan.failed, with
delivery, installation, repository, PR, commit, duration, and usage_scope
fields for correlation. Keep identifiers as log fields, not metric labels.
Set FOXGUARD_INTERNAL_ACCOUNTS to a comma-separated list of your own GitHub
accounts and organizations. Matching is case-insensitive. Other owners are
classified as external; an unset list or missing owner produces unknown.
External activity is not proof of a paying customer, and scans are not people.
The installation registry is reconciled against all pages of GitHub's App installation API at startup and hourly. Failed refreshes retain existing state; concurrent webhooks take precedence. Sparse webhook metadata preserves known account details and observed repository names. Those names are not a complete inventory of an installation's accessible repositories.
Persist FOXGUARD_INSTALLATIONS_PATH and FOXGUARD_PULL_REQUEST_JOBS_PATH on
durable storage. Monitor foxguard.installations.reconcile_failed alongside
scan failures; foxguard.installations.reconciled reports the total and
internal/external/unknown installation counts after a successful refresh.
Size FOXGUARD_PR_WORKERS against measured scanner peak memory and the
container memory limit: child-process OOM kills can occur without restarting
the hosted application.
Quick Start
foxguard .                              # scan everything
foxguard diff main .                    # only new findings vs main
foxguard tui .                          # interactive terminal review
foxguard secrets .                      # leaked credentials and keys
foxguard sca .                          # dependency vulnerabilities from OSV
foxguard pqc .                          # post-quantum crypto audit
foxguard --format sarif . > results.sarif
foxguard --format semgrep-json .        # Semgrep CLI-compatible JSON
Use foxguard --fix src/ or foxguard --fix src/app.py to apply supported taint
fixes in place. Targets are checked against the canonical scan directory or the
selected file; findings outside that scope are skipped. Python command-injection
fixes add import subprocess when needed, preserving module docstrings and future
imports. Review generated changes before committing.