Skip to content
KitploitKITPLOIT
도구블로그
제출
도구블로그
제출

해킹, 침투 테스트 및 사이버 보안 도구를 당신의 보안 무기고에!

Kitploit은 해킹, 사이버 보안 및 침투 테스트 도구 디렉토리입니다. 최신 프로젝트 업데이트를 발견하여 취약점을 찾고, 시스템을 분석하고, 테스트를 자동화하고, 보안을 강화하세요.

··피드·문의·개인정보·© 2026 Kitploit

도구 디렉토리

카테고리

모든 카테고리 보기
Loading categories
카테고리

Reconnaissance

Tools for gathering information about targets and identifying attack surfaces.

Kitploit 추천
추천 도구

10 선택됨
amass preview#1

amass

GitHubowasp-amass/amass
15.0k5개월 전
subfinder preview#2

subfinder

GitHubprojectdiscovery/subfinder
14.2k3일 전
reconftw preview#3

reconftw

GitHubsix2dez/reconftw
8.0k13일 전
spiderfoot preview#4

spiderfoot

GitHubsmicallef/spiderfoot
20.1k2년 전
recon-ng preview#5

recon-ng

GitHublanmaster53/recon-ng
5.8k1년 전
httpx preview#6

httpx

GitHubprojectdiscovery/httpx
10.3k3일 전
naabu preview#7

naabu

GitHubprojectdiscovery/naabu
6.2k6일 전
nmap preview#8

nmap

GitHubnmap/nmap
13.3k2일 전
theHarvester preview#9

theHarvester

GitHublaramies/theharvester
17.0k6일 전
FinalRecon preview#10

FinalRecon

GitHubthewhiteh4t/finalrecon
2.9k3개월 전
최신관련성인기최근 업데이트
7417 결과
CVE-2026-30081 preview

CVE-2026-30081

GitHubrakeshelamaran98/cve-2026-30081

# CVE-2026-30081 문서 Quantum Networks QN-I-470 라우터 펌웨어 6.1.1.B1에서 발견된 높은 심각도의 평문 전송 취약점으로, 인접한 공격자가 관리자 자격 증명을 가로챌 수 있습니다.
vulnerability-analysisexploitationinformation-gathering+2
5개월 전
CVE-2026-29597 preview

CVE-2026-29597

GitHubpadayali-jd/cve-2026-29597

DDSN Interactive cm3 Acora CMS 10.7.1의 부적절한 접근 제어 취약점을 시연하며, 편집자 권한을 가진 사용자가 강제 브라우징 및 매개변수 조작을 통해 민감한 구성 파일을 검색할 수 있도록 허용합니다.
vulnerability-analysisexploitationinformation-gathering+2
5개월 전
thermoptic preview

thermoptic

GitHubmandatoryprogrammer/thermoptic

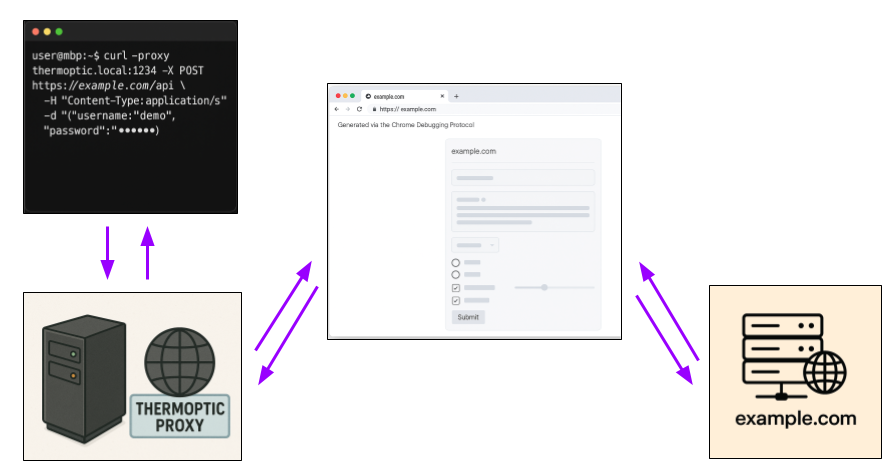
스택의 모든 계층에서 요청을 Chrome 브라우저로 완벽하게 위장하는 차세대 HTTP 스텔스 프록시입니다.
web-proxies-interceptionimpersonation-toolsinformation-gathering+5
1.0k5개월 전
tenda-hg10-rce preview

tenda-hg10-rce

GitHube76f01z/tenda-hg10-rce

CVE-2026-1689 Tenda HG10 무인증 원격 코드 실행 (RCE)
reconnaissancevulnerability-analysisexploitation+2
5개월 전
PYDNS-Scanner preview

PYDNS-Scanner

GitHubxullexer/pydns-scanner

현대적이고 고성능의 DNS 스캐너로, Textual로 구축된 아름다운 터미널 사용자 인터페이스(TUI)를 갖추고 있습니다. 이 도구는 수백만 개의 IP 주소를 스캔하여 작동하는 DNS 서버를 찾을 수 있으며, 선택적 Slipstream 프록시 테스트와 자동 멀티…

reconnaissancenetwork-mappingvulnerability-analysis+3
4035개월 전
bashacks preview

bashacks

GitHubmerces/bashacks

Bash로 해킹하며 생산성을 높이기 위한 함수 모음
general-purpose-utilitiesencryption-decryption-toolshash-analysis+3
2115개월 전
wpx preview

wpx

GitHubgreg-randall/wpx

헤드리스 브라우저를 통한 WAF 우회 기능을 갖춘 비동기 WordPress 보안 스캐너입니다. 플러그인, 테마, 사용자 및 멀티사이트 설치를 열거하며, 스텔스 핑거프린팅과 WPScan 취약점 통합을 제공합니다.
reconnaissanceweb-vulnerability-scannersvulnerability-analysis+6
105개월 전
S3BucketList preview

S3BucketList

GitHubalecblance/s3bucketlist

Amazon S3 버킷을 탐색 중에 나열해주는 Chrome 및 Firefox 확장 프로그램
vulnerability-analysisinformation-gatheringcloud-security
1325개월 전
CVE-2026-3055 preview

CVE-2026-3055

GitHub0xblackash/cve-2026-3055

CVE-2026-3055

reconnaissancevulnerability-analysisexploitation+3
5개월 전
Samuraizer preview

Samuraizer

GitHubzomry1/samuraizer

NotebookLM을 강화한 버전 — 보안 연구자를 위해 특별히 설계됨.
osintinformation-gatheringutilities-frameworks+5
295개월 전
CVE-2022-46364-Proof-of-the-concept preview

CVE-2022-46364-Proof-of-the-concept

GitHubcybermaksx/cve-2022-46364-proof-of-the-concept

이 취약점을 통해 공격자는 MTOM/XOP 요청을 수락하는 Apache CXF 웹 서비스에 SSRF(서버 측 요청 위조) 공격을 수행할 수 있습니다. 문제는 xop:Include의 href 속성이 구문 분석되는 방식에 존재하며, 서버가 임의의 URL을 요청할 수 있게…
vulnerability-analysisexploitationweb-application-exploitation+3
25개월 전
CVE-2022-46364-Poc preview

CVE-2022-46364-Poc

GitHubkasem545/cve-2022-46364-poc

Python용 CVE-2022-46364 익스플로잇(Apache CXF의 MTOM XOP:Include를 통한 SSRF). 취약한 엔드포인트에서 내부 메타데이터, 자격 증명 및 마이크로서비스 데이터를 유출하기 위해 조작된 SOAP 요청을 전송합니다.

reconnaissancevulnerability-analysisexploitation+3
75개월 전
CVE-2026-21643 preview

CVE-2026-21643

GitHub0xblackash/cve-2026-21643

CVE-2026-21643
vulnerability-analysisexploitationweb-application-exploitation+3
185개월 전
React2Shell-PoC-CVE-2025-55182 preview

React2Shell-PoC-CVE-2025-55182

GitHubeagle-nett/react2shell-poc-cve-2025-55182

# CVE-2025-55182 (React2Shell) RCE 취약점에 대한 개념 증명 익스플로잇 React Server Components의 원격 코드 실행(RCE) 취약점입니다. 취약한 호스트를 탐지하는 스캐너와 원격 명령 실행을 위한 셸 스크립트를 포함합니다.…
reconnaissancevulnerability-scannersexploitation+4
5개월 전
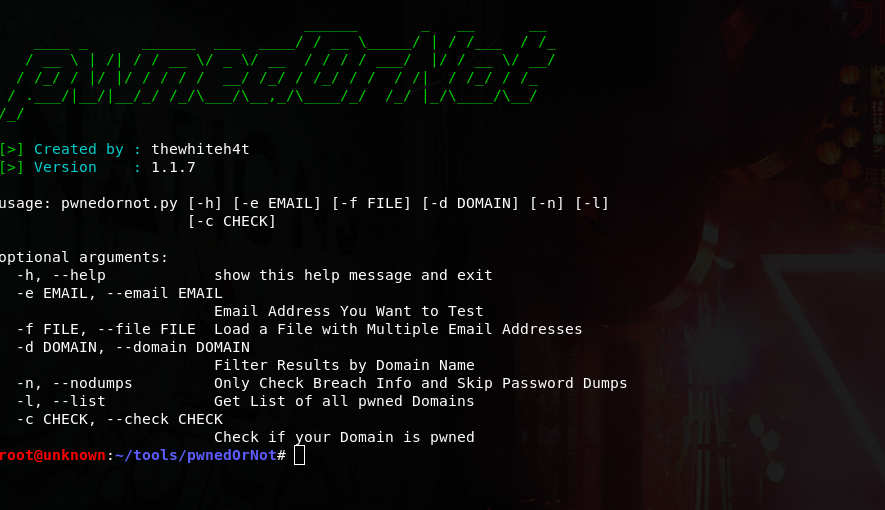
pwnedOrNot preview

pwnedOrNot

GitHubthewhiteh4t/pwnedornot

손상된 이메일 주소의 비밀번호를 찾는 OSINT 도구
osintpassword-crackingvulnerability-analysis+1
2.6k5개월 전
CVE-2023-35813 preview

CVE-2023-35813

GitHubher3ticavi/cve-2023-35813

취약한 Sitecore 인스턴스를 탐지하기 위한 개념 증명 스크립트로, 특정 수정 사항에 대해 서버 응답 헤더를 분석하여 취약성 평가를 지원합니다.
reconnaissancevulnerability-analysisexploitation+2
35개월 전
BridgeHead preview

BridgeHead

GitHubzakipedio/bridgehead

ADWS를 통한 Active Directory에 대한 네이티브 C++ 접근, .NET, WCF, HTTP 스택 불필요.
authentication-authorizationscripting-automationinformation-gathering+5
825개월 전
CVE-2025-67906 preview

CVE-2025-67906

GitHubfranckferman/cve-2025-67906

MISP <= 2.5.27 - 저장형 크로스 사이트 스크립팅 (Workflow Engine을 통한 doT.js 템플릿 인젝션)

vulnerability-analysisexploitationweb-application-exploitation+5
25개월 전
이전1…929394…100다음