
Skip to content
KitploitKITPLOIT
도구익스플로잇블로그
Log in
제출
도구익스플로잇블로그
제출

해킹, 침투 테스트 및 사이버 보안 도구를 당신의 보안 무기고에!

Kitploit은 해킹, 사이버 보안 및 침투 테스트 도구 디렉토리입니다. 최신 프로젝트 업데이트를 발견하여 취약점을 찾고, 시스템을 분석하고, 테스트를 자동화하고, 보안을 강화하세요.

피드문의개인정보© 2026 Kitploit

도구 디렉토리

카테고리

모든 카테고리 보기
Loading categories
Misconfiguration — 47페이지 | Kitploit
카테고리

Misconfiguration

Configuration auditing, compliance scanning, hardening benchmarks, and drift detection tools.

Kitploit 추천
추천 도구

10 선택됨
lynis preview#1

lynis

GitHubcisofy/lynis
16.1k1개월 전
content preview#2

content

GitHubcomplianceascode/content
2.8k7시간 42분 전
prowler preview#3

prowler

GitHubprowler-cloud/prowler
14.3k1일 전
trivy preview#4

trivy

GitHubaquasecurity/trivy
37.4k7시간 42분 전
checkov preview#5

checkov

GitHubbridgecrewio/checkov
8.9k17시간 28분 전
kics preview#6

kics

GitHubcheckmarx/kics
2.7k1일 전
cloud-custodian preview#8

cloud-custodian

GitHubcloud-custodian/cloud-custodian
6.0k18시간 16분 전
kubescape preview#9

kubescape

GitHubkubescape/kubescape
11.6k6시간 8분 전
kube-bench preview#10

kube-bench

GitHubaquasecurity/kube-bench
8.1k16일 전
kube-linter preview#11

kube-linter

GitHubstackrox/kube-linter
3.5k15시간 7분 전
최신관련성인기최근 업데이트
963 결과
CVE-2021-27187 preview

CVE-2021-27187

GitHubjet-pentest/cve-2021-27187

CVE-2021-27187에 대한 개념 증명: FX Aggregator 터미널 클라이언트의 login.sav 파일에 저장된 평문 자격 증명으로, 로컬 자격 증명 탈취 및 무단 접근을 가능하게 합니다.
password-attacksvulnerability-analysisexploitation+3
15년 전
CVE-2024-12535 preview

CVE-2024-12535

GitHubrandomrobbiebf/cve-2024-12535

Host PHP Info <= 1.0.4 - 인가 누락으로 인한 비인증 민감 정보 노출
vulnerability-analysisinformation-gatheringweb-security+1
1년 전
Digisol-DG--GR1321-s-Password-Storage-in-Plaintext--CVE-2024-4232 preview

Digisol-DG--GR1321-s-Password-Storage-in-Plaintext--CVE-2024-4232

GitHubredfox-security/digisol-dg--gr1321-s-password-storage-in-plaintext--cve-2024-4232

CVE-2024-4232를 대상으로 하는 개념 증명 익스플로잇으로, Digisol DG-GR1321 라우터의 평문 비밀번호 저장을 공격합니다. 웹 인터페이스에서 자격 증명 추출을 시연합니다.
iot-securitypassword-attacksvulnerability-analysis+3
2년 전
ingressnightmare-detection-poc preview

ingressnightmare-detection-poc

GitHubm-q-t/ingressnightmare-detection-poc

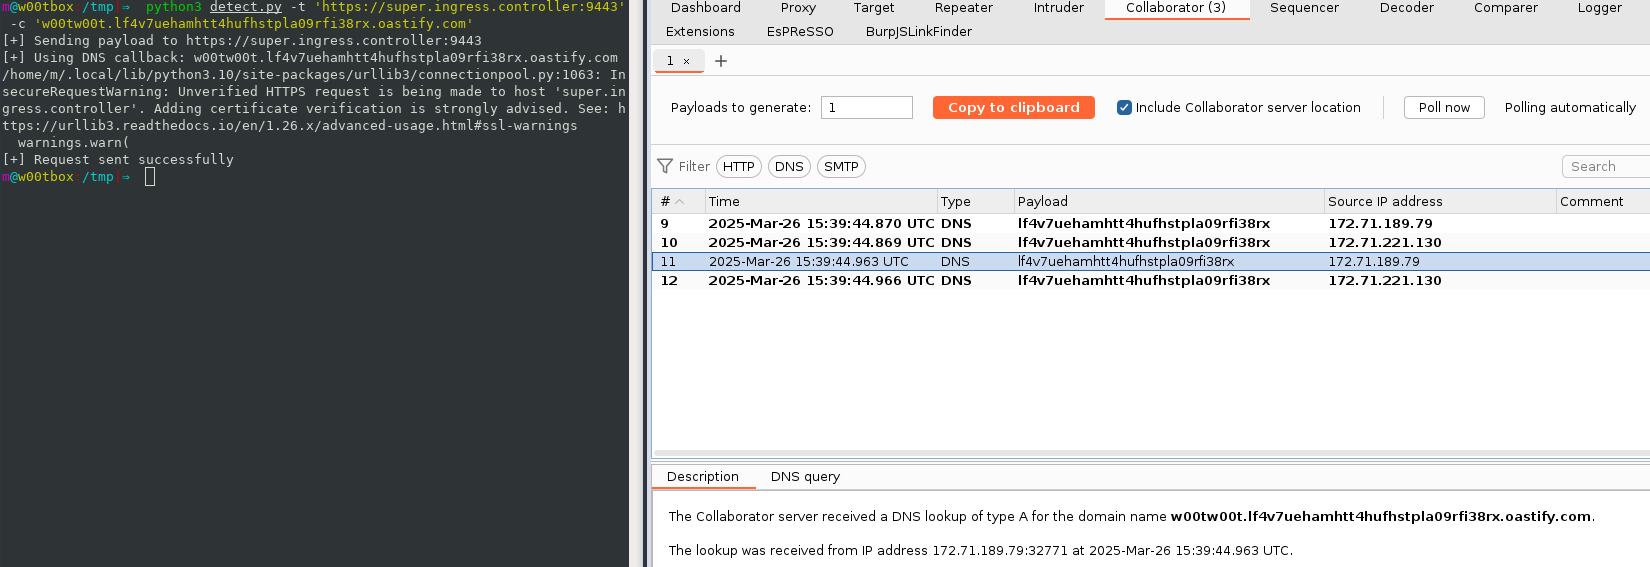
IngressNightmare(CVE-2025-1974)를 (비침습적) 능동적 수단을 통해 탐지하는 PoC 도구
vulnerability-scannersexploitationweb-security+3
1년 전
CVE-2024-5737 preview

CVE-2024-5737

GitHubafine-com/cve-2024-5737

AdmirorFrames Joomla! 확장 < 5.0 - HTML 인젝션
vulnerability-analysisexploitationweb-application-exploitation+2
2년 전
CVE-2020-10130 preview

CVE-2020-10130

GitHubinfosec4fun/cve-2020-10130

CVE-2020-10130 - V-9.1 이전의 SearchBlox 제품은 비즈니스 로직 우회에 취약합니다.
authentication-authorizationvulnerability-analysisexploitation+2
3년 전
FluentD-TD-agent-Exploit-CVE-2020-28169 preview

FluentD-TD-agent-Exploit-CVE-2020-28169

GitHubzubrahzz/fluentd-td-agent-exploit-cve-2020-28169

권한 상승으로 이어지는 안전하지 않은 폴더 권한
privilege-escalationvulnerability-analysisexploitation+1
5년 전
CVE-2023-47668 preview

CVE-2023-47668

GitHubrandomrobbiebf/cve-2023-47668

Restrict Content <= 3.2.7 - 레거시 로그 파일을 통한 정보 노출
vulnerability-analysisinformation-gatheringweb-security+2
2년 전
CVE-2025-25614 preview

CVE-2025-25614

GitHubarmaansidana2003/cve-2025-25614

CVE-2025-25614용 개념 증명 익스플로잇으로, Unifiedtransform v2.0의 잘못된 접근 제어 취약점으로 교사가 동료 교사의 데이터를 수정하여 권한 상승을 유발할 수 있습니다.
privilege-escalationvulnerability-analysisexploitation+3
1년 전
iconvfix preview

iconvfix

GitHubabsolutedesignltd/iconvfix

CVE-2024-2961 패치를 위한 Bash 스크립트
general-purpose-utilitiesvulnerability-analysisscripting-automation+1
2년 전
CVE-2021-41078 preview

CVE-2021-41078

GitHubs-index/cve-2021-41078

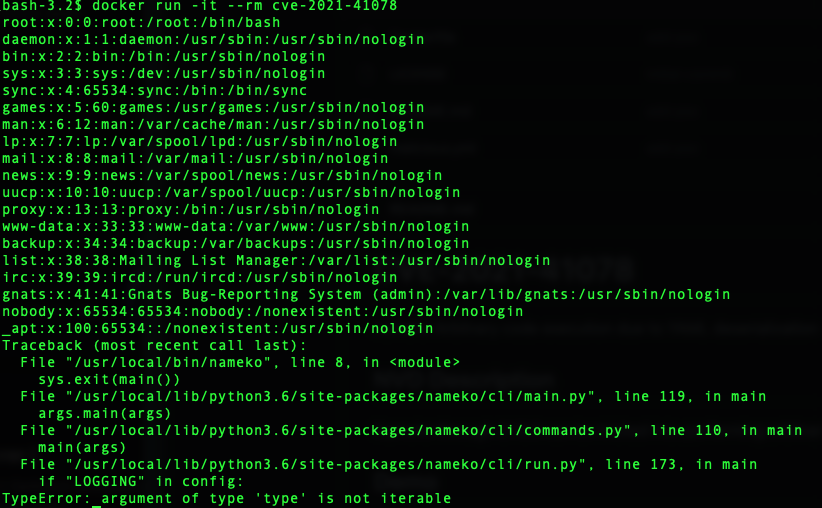
nameko YAML 역직렬화로 인한 임의 코드 실행
payload-generationvulnerability-analysiscode-analysis+3
4년 전
Digisol-DG-GR1321-s-Password-Storage-in-Plaintext-CVE-2024-4232 preview

Digisol-DG-GR1321-s-Password-Storage-in-Plaintext-CVE-2024-4232

GitHubredfox-security/digisol-dg-gr1321-s-password-storage-in-plaintext-cve-2024-4232

개념 증명(PoC)으로, Digisol DG-GR1321 라우터의 평문 비밀번호 저장 취약점을 시연하여 자격 증명 노출 및 무단 접근을 가능하게 합니다.
iot-securitypassword-attacksvulnerability-analysis+3
2년 전
CVE-2024-10449-patch preview

CVE-2024-10449-patch

GitHubg-u-i-d/cve-2024-10449-patch

CVE-2024-10449 패치: 취약한 loginAction.php를 강화된 버전으로 교체하여 보안 인증을 위해 데이터베이스 구성이 필요합니다.
vulnerability-analysiscode-analysisweb-security+2
1년 전
CVE-2023-37755---Hardcoded-Admin-Credential-in-i-doit-Pro-25-and-below preview

CVE-2023-37755---Hardcoded-Admin-Credential-in-i-doit-Pro-25-and-below

GitHubleekenghwa/cve-2023-37755---hardcoded-admin-credential-in-i-doit-pro-25-and-below

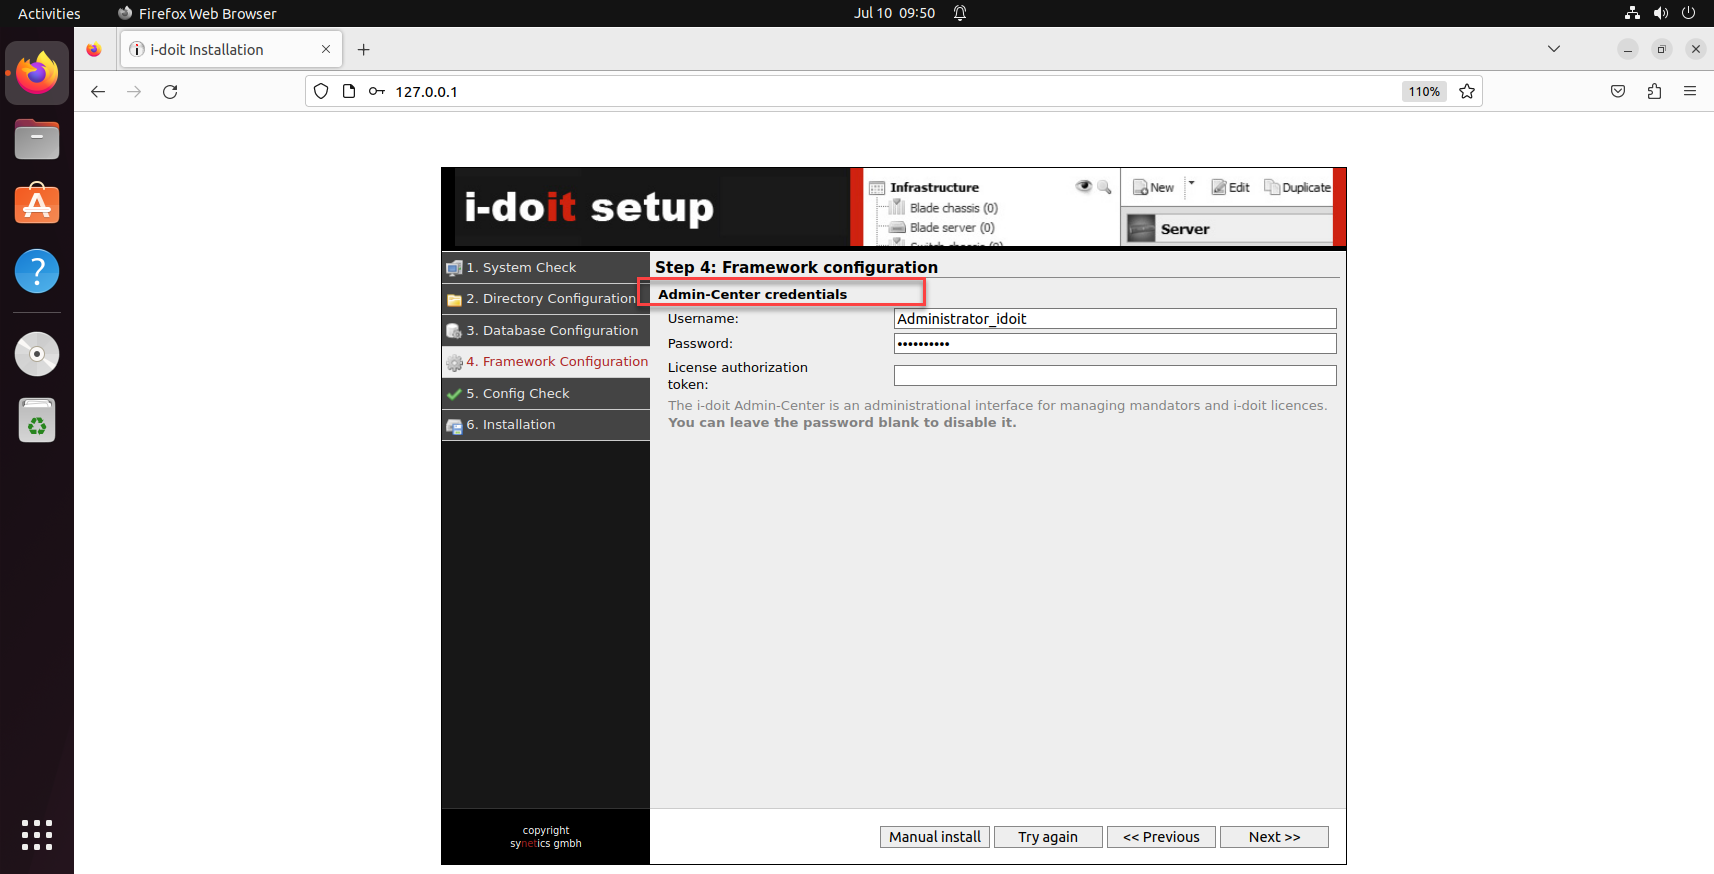
CVE-2023-37755에 대한 개념 증명: i-doit Pro 25 이하의 하드코딩된 관리자 자격 증명(admin/admin)으로, 기본 웹 인터페이스를 통해 무단 관리자 로그인이 가능합니다.
password-attacksvulnerability-analysisexploitation+3
3년 전
CVE-2020-23590 preview

CVE-2020-23590

GitHubhuzaifahussain98/cve-2020-23590

CSRF로 "WLAN SSID"의 비밀번호를 변경할 수 있음
embedded-systems-securityiot-securityvulnerability-analysis+3
3년 전
CVE-2023-49978 preview

CVE-2023-49978

GitHubgeraldoalcantara/cve-2023-49978

고객 지원 시스템 1.0 - 부적절한 접근 제어
privilege-escalationvulnerability-analysisexploitation+3
2년 전
CVE-2024-34223 preview

CVE-2024-34223

GitHubdovankha/cve-2024-34223

CVE-2024-34223용 개념 증명: /hrm/leaverequest.php를 통한 무단 휴가 티켓 승인/거부를 허용하는 SourceCodester HRMS 1.0의 안전하지 않은 권한 취약점.

vulnerability-analysisweb-securitypenetration-testing+2
2년 전
CVE-2025-46078 preview

CVE-2025-46078

GitHubyggcwhat/cve-2025-46078

취약점 설명

vulnerability-analysiscode-analysisexploitation+3
1년 전
이전1…464748…54다음








