Skip to content
KitploitKITPLOIT
도구익스플로잇블로그
Log in
제출
도구익스플로잇블로그
제출

해킹, 침투 테스트 및 사이버 보안 도구를 당신의 보안 무기고에!

Kitploit은 해킹, 사이버 보안 및 침투 테스트 도구 디렉토리입니다. 최신 프로젝트 업데이트를 발견하여 취약점을 찾고, 시스템을 분석하고, 테스트를 자동화하고, 보안을 강화하세요.

피드문의개인정보© 2026 Kitploit

도구 디렉토리

카테고리

모든 카테고리 보기
Loading categories
카테고리

Firmware Analysis

Firmware extraction, unpacking, emulation, vulnerability discovery, and binary analysis tools.

Kitploit 추천

추천 도구

10 선택됨
binwalk preview#1

binwalk

GitHubrefirmlabs/binwalk
14.2k2개월 전
emba preview#2

emba

GitHube-m-b-a/emba
3.6k4시간 43분 전
FACT_core preview#3

FACT_core

GitHubfkie-cad/fact_core
1.5k6일 전
FirmAE preview#4

FirmAE

GitHubpr0v3rbs/firmae
8943개월 전
firmadyne preview#5

firmadyne

GitHubfirmadyne/firmadyne
2.1k2년 전
embark preview#6

embark

GitHube-m-b-a/embark
3962개월 전
fwhunt-scan preview#7

fwhunt-scan

GitHubbinarly-io/fwhunt-scan
2431년 전
ghidra preview#8

ghidra

GitHubnationalsecurityagency/ghidra
71.1k1일 전
radare2 preview#9

radare2

GitHubradareorg/radare2
24.5k2시간 28분 전
angr preview#10

angr

GitHubangr/angr
9.0k4시간 58분 전
최신관련성인기최근 업데이트
473 결과
powerg-tools preview

powerg-tools

GitHubnccgroup/powerg-tools

PowerG 무선 프로토콜의 리버스 엔지니어링 및 상호작용을 위한 도구

embedded-systems-securityreverse-engineeringwireless-security+3
56개월 전
CVE-2026-79298 preview

CVE-2026-79298

GitHubthemalwareguardian/cve-2026-79298

CVE-2026-79298을 문서화한 연구 저장소로, Howyar SysReturn의 IA-32 부팅 경로에서 불완전하게 수정된 UEFI Secure Boot 우회 취약점에 대한 리버스 엔지니어링 및 PoC 자료를 포함합니다.
vulnerability-analysisexploitationreverse-engineering+4
21개월 전
CVE-2019-17147 preview

CVE-2019-17147

GitHubimnot-ye/cve-2019-17147

CVE-2019-17147에 대한 종합적인 리버스 엔지니어링 및 익스플로잇으로, TP-Link TL-WR841N 라우터의 스택 버퍼 오버플로우 취약점입니다. 펌웨어 분석, 하드웨어 디버깅, 인증되지 않은 RCE를 위한 단계적 쉘코드 주입 익스플로잇을 포함합니다.
embedded-systems-securityiot-securityvulnerability-analysis+9
48개월 전
CVE-2024-48705 preview

CVE-2024-48705

GitHubl41kaa/cve-2024-48705

Wavlink AC1200 펌웨어 버전 M32A3_V1410_230602 및 M32A3_V1410_240222는 비밀번호 재설정 중 인증 후 명령 주입(post-authentication command injection)에 취약합니다. 이 취약점은 구체적으로…
embedded-systems-securityiot-securityvulnerability-analysis+7
21년 전
CVE-2022-24693 preview

CVE-2022-24693

GitHublukejenkins/cve-2022-24693

문서화 및 재현 단계 for CVE-2022-24693: Baicells Nova436Q 및 Neutrino 430 펌웨어의 하드코딩된 자격 증명으로, 원격 SSH 접근 및 권한 상승을 가능하게 함.
embedded-systems-securitypassword-crackingreconnaissance+6
31년 전
CVE-2026-43499_HW-CLT-AL01 preview

CVE-2026-43499_HW-CLT-AL01

GitHubzychen027/cve-2026-43499_hw-clt-al01

boot.img에서 기기별 커널 오프셋을 생성하고 프리로드 라이브러리를 컴파일하여 CVE-2026-43499 Android arm64 로컬 권한 상승을 악용합니다.
android-securityprivilege-escalationexploitation+4
2개월 전
attestos preview

attestos

GitHubplunder707/attestos

Bazzite에 TPM 부팅 증명 계층을 더한 것입니다. 진행 중인 작업: 빌드는 검증되지 않았고, UKI 메커니즘은 미해결 상태입니다. 사양: github.com/plunder707/attested-gaming
defensive-toolscryptographyhardware-security+2
22개월 전
zyxel-p870hn-hardware-hacking preview

zyxel-p870hn-hardware-hacking

GitHubdanyw24/zyxel-p870hn-hardware-hacking

베어 PCB에서 루트 권한까지: 내 하드웨어에서 UART로 ZyXEL P-870HN (BCM6368) 하드웨어 해킹 — CVE-2025-0890 + CVE-2024-40891
embedded-systems-securitypassword-crackingiot-security+6
2개월 전
the-key-ships-with-the-lock-cve-2026-82876-phison-s11-ssd-firmware-signature-bypass preview

the-key-ships-with-the-lock-cve-2026-82876-phison-s11-ssd-firmware-signature-bypass

GitHubhunt-benito/the-key-ships-with-the-lock-cve-2026-82876-phison-s11-ssd-firmware-signature-bypass

개념 증명(PoC)으로, Phison S11 SSD의 펌웨어 서명 검증 우회를 시연하며, 공격자가 자체 RSA 모듈러스를 삽입하여 변조된 펌웨어에 재서명할 수 있게 한다.
embedded-systems-securityvulnerability-analysisexploitation+4
1개월 전
nec_aterm_tools preview

nec_aterm_tools

GitHubinfobyte/nec_aterm_tools

NEC Aterm 라우터 펌웨어 이미지 및 QR 코드에서 하드웨어 임의 키를 추출하여 셸 액세스 권한을 얻기 위한 유효한 비밀번호를 생성합니다.

embedded-systems-securitypassword-crackingreconnaissance+4
34년 전
CVE-2025-4275 preview

CVE-2025-4275

GitHubthemalwareguardian/cve-2025-4275

CVE-2025-4275(Hydr0ph0bia)에 대한 분석 및 익스플로잇으로, 펌웨어 변수를 사용하여 이후 부팅 구성 요소에서 신뢰하는 공격자 제어 인증서를 도입하는 Secure Boot 신뢰 체인의 취약점입니다.

persistence-mechanismsvulnerability-analysisexploitation+5
2개월 전
CVE-2022-34303 preview

CVE-2022-34303

GitHubthemalwareguardian/cve-2022-34303

CryptoPro 서명 UEFI Shell을 통한 CVE-2022-34303 Secure Boot 우회를 시연하며, mm 명령을 사용하여 gSecurity2를 무효화하고 서명되지 않은 UEFI 애플리케이션을 로드합니다.
persistence-mechanismsvulnerability-analysisexploitation+7
1개월 전
go-without-bounds-cve-2026-67822-stack-overflow-in-tenda-w6-s-wifissidset preview

go-without-bounds-cve-2026-67822-stack-overflow-in-tenda-w6-s-wifissidset

GitHubhunt-benito/go-without-bounds-cve-2026-67822-stack-overflow-in-tenda-w6-s-wifissidset

Tenda W6-S /goform/wifiSSIDset의 CVE-2026-67822 스택 오버플로우에 대한 PoC: DoS 재현기, QEMU MIPS 심(shim), 및 개념적 RCE 페이로드 스켈레톤.
embedded-systems-securitydynamic-analysis-sandboxingiot-security+6
2개월 전
CVE-2021-26258 preview

CVE-2021-26258

GitHubzwclose/cve-2021-26258

CVE-2021-26258용 파일 및 도구
packet-sniffing-analysisvulnerability-analysisexploitation+3
33년 전
CVE-2025-0324-axis-vapix-privesc preview

CVE-2025-0324-axis-vapix-privesc

GitHubkemrec/cve-2025-0324-axis-vapix-privesc

CVE-2025-0325에 대한 근본 원인 분석 및 안전 게이트 검증 도구로, AXIS OS VAPIX의 권한 상승 취약점으로 인증된 모든 사용자가 조작된 Host 헤더를 통해 관리자 권한을 획득할 수 있는 문제를 다룹니다.

privilege-escalationvulnerability-analysisexploitation+4
1개월 전
CVE-2022-34302 preview

CVE-2022-34302

GitHubthemalwareguardian/cve-2022-34302

CVE-2022-34302를 시연한다. 이는 New Horizon Datasys가 서명한 부트로더의 내장 커스텀 PE/COFF 로더가 서명되지 않은 UEFI 애플리케이션을 실행함으로써 발생하는 Secure Boot 우회 취약점이다.
embedded-systems-securitypersistence-mechanismsvulnerability-analysis+7
1개월 전
vankyo-s30-bootloader-unlock preview

vankyo-s30-bootloader-unlock

GitHubgadorach/vankyo-s30-bootloader-unlock

Vankyo MatrixPad S30 (Unisoc SC9863A) — Bootloader unlock via CVE-2022-38694 FDL1 method
embedded-systems-securityexploitationreverse-engineering+3
1개월 전
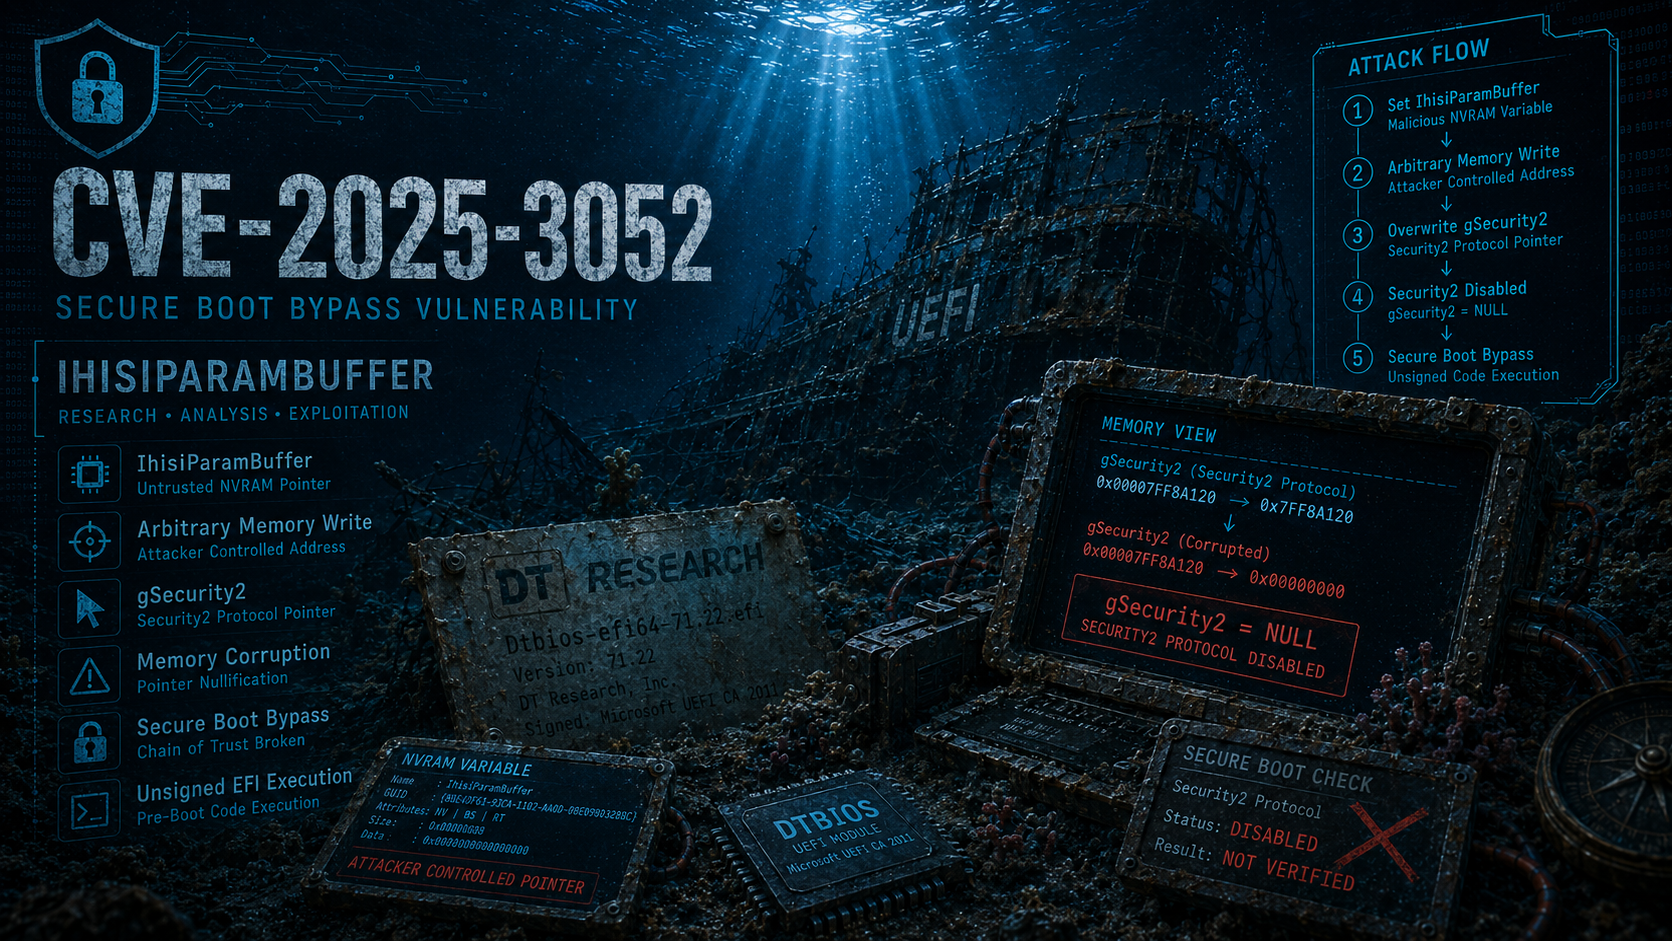
CVE-2025-3052 preview

CVE-2025-3052

GitHubthemalwareguardian/cve-2025-3052

CVE-2025-3052에 대한 연구로, 보안에 중요한 포인터를 수정할 수 있는 임의 쓰기 프리미티브를 노출하는 Insyde 펌웨어 취약점입니다.

embedded-systems-securityvulnerability-analysisexploitation+5
2개월 전
이전1…192021…27다음
Firmware Analysis — 20페이지 | Kitploit