Skip to content
KitploitKITPLOIT
도구익스플로잇블로그
Log in
제출
도구익스플로잇블로그
제출

해킹, 침투 테스트 및 사이버 보안 도구를 당신의 보안 무기고에!

Kitploit은 해킹, 사이버 보안 및 침투 테스트 도구 디렉토리입니다. 최신 프로젝트 업데이트를 발견하여 취약점을 찾고, 시스템을 분석하고, 테스트를 자동화하고, 보안을 강화하세요.

피드문의개인정보© 2026 Kitploit

도구 디렉토리

카테고리

모든 카테고리 보기
Loading categories
Embedded Systems Security — 35페이지 | Kitploit
카테고리

Embedded Systems Security

Tools for analyzing and securing firmware, microcontrollers, and low-level hardware components.

Kitploit 추천

추천 도구

10 선택됨
binwalk preview#1

binwalk

GitHubrefirmlabs/binwalk
14.2k2개월 전
emba preview#2

emba

GitHube-m-b-a/emba
3.6k3일 전
FACT_core preview#3

FACT_core

GitHubfkie-cad/fact_core
1.5k1개월 전
FirmAE preview#4

FirmAE

GitHubpr0v3rbs/firmae
8944개월 전
firmadyne preview#5

firmadyne

GitHubfirmadyne/firmadyne
2.1k2년 전
angr preview#6

angr

GitHubangr/angr
9.0k5시간 29분 전
ghidra preview#8

ghidra

GitHubnationalsecurityagency/ghidra
71.1k12시간 5분 전
radare2 preview#9

radare2

GitHubradareorg/radare2
24.5k11시간 35분 전
rizin preview#10

rizin

GitHubrizinorg/rizin
4.1k1일 전
unicorn preview#11

unicorn

GitHubunicorn-engine/unicorn
9.2k8개월 전
최신관련성인기최근 업데이트
976 결과
CVE-2022-34302 preview

CVE-2022-34302

GitHubthemalwareguardian/cve-2022-34302

CVE-2022-34302를 시연한다. 이는 New Horizon Datasys가 서명한 부트로더의 내장 커스텀 PE/COFF 로더가 서명되지 않은 UEFI 애플리케이션을 실행함으로써 발생하는 Secure Boot 우회 취약점이다.
embedded-systems-securitypersistence-mechanismsvulnerability-analysis+7
1개월 전
vankyo-s30-bootloader-unlock preview

vankyo-s30-bootloader-unlock

GitHubgadorach/vankyo-s30-bootloader-unlock

Vankyo MatrixPad S30 (Unisoc SC9863A) — CVE-2022-38694 FDL1 방식을 통한 부트로더 잠금 해제
embedded-systems-securityexploitationreverse-engineering+3
2개월 전
CVE-2026-56718 preview

CVE-2026-56718

GitHubhellkkid/cve-2026-56718

AJCloud AJY IPC 펌웨어의 jdbhttpd를 통한 경로 탐색 취약점
embedded-systems-securityreconnaissanceiot-security+3
2개월 전
CVE-2025-3052 preview

CVE-2025-3052

GitHubthemalwareguardian/cve-2025-3052

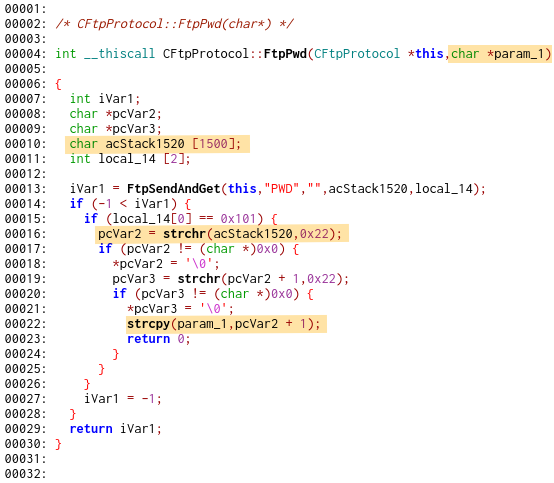
CVE-2025-3052에 대한 연구로, 보안에 중요한 포인터를 수정할 수 있는 임의 쓰기 프리미티브를 노출하는 Insyde 펌웨어 취약점입니다.
embedded-systems-securityvulnerability-analysisexploitation+5
2개월 전
accfly preview

accfly

GitHubtezeb/accfly

Accfly 카메라 취약점 공개: CVE-2020-25782, CVE-2020-25783, CVE-2020-25784, CVE-2020-25785.
embedded-systems-securityiot-securityvulnerability-analysis+6
35년 전
CVE-2026-38577 preview

CVE-2026-38577

GitHubpoxsky/cve-2026-38577

Tenda HG21 XPON 모뎀 펌웨어에 하드코딩된 루트 자격 증명(admin/system)을 보여주는 Proof-of-concept로, telnet 또는 FTP를 통한 무단 루트 접근을 가능하게 합니다.
embedded-systems-securityiot-securityvulnerability-analysis+5
2개월 전
huawei-p10-cve-2017-8890-unlock preview

huawei-p10-cve-2017-8890-unlock

GitHubsweatyrocket/huawei-p10-cve-2017-8890-unlock

Huawei P10 VTR-L29C432B151 CVE-2017-8890 익스플로잇 연구 및 부트로더 잠금 해제 여정
android-securityembedded-systems-securityprivilege-escalation+4
3개월 전
cve-2026-86547-mrubyc-op-enter preview

cve-2026-86547-mrubyc-op-enter

GitHubharshrajsinghania/cve-2026-86547-mrubyc-op-enter

CVE-2026-86547에 대한 독립 실행형 개념 증명으로, mrubyc op_enter()의 4.0.0까지의 NULL 포인터 역참조 취약점입니다.
embedded-systems-securitymemory-forensicsvulnerability-analysis+3
1개월 전
Poc-CVE-2024-57040 preview

Poc-CVE-2024-57040

GitHubabsholi7ly/poc-cve-2024-57040

CVE-2024-57040는 특정 TP-Link TL-WR845N 라우터 모델에서 발견된 보안 취약점입니다. 구체적으로, 라우터의 루트 계정에 대한 "하드코딩된" 비밀번호와 관련이 있습니다. 이는 변경할 수 없는 기본 비밀번호가 라우터의 소프트웨어에 내장되어 있음을…
embedded-systems-securityiot-securitypassword-attacks+3
21년 전
CVE-2026-6789-Stack-Buffer-Overflow-in-Embedded-TLS-Certificate-Parser preview

CVE-2026-6789-Stack-Buffer-Overflow-in-Embedded-TLS-Certificate-Parser

GitHubgeorge0papasotiriou/cve-2026-6789-stack-buffer-overflow-in-embedded-tls-certificate-parser

조작된 X.509 SAN 확장을 사용하여 임베디드 TLS 인증서 파서에서 스택 버퍼 오버플로를 유발하는 PoC로, IoT 및 산업용 기기에서 원격 코드 실행을 가능하게 합니다.

embedded-systems-securityiot-securityvulnerability-analysis+3
3개월 전
CVE-2017-13672 preview

CVE-2017-13672

GitHubdavidbuchanan314/cve-2017-13672

CVE-2017-13672에 대한 PoC (VGA Cirrus QEMU 드라이버의 OOB 읽기로 DoS 유발)
embedded-systems-securityvulnerability-analysisexploitation+3
38년 전
WiFi-SpiderWeb preview

WiFi-SpiderWeb

GitHubbadrrx/wifi-spiderweb

USB 드라이브에서 실행되는 OpenWrt 라우터용 능동적 사이버 방어 및 허니팟 시스템.
defensive-toolsembedded-systems-securityphishing-tools+7
35개월 전
GhostLock_MT6983V_5.10 preview

GhostLock_MT6983V_5.10

GitHubsetsuneko/ghostlock_mt6983v_5.10

고위험 취약점 CVE-2026-43499, 5.10 커널 및 MediaTek MT6983V에서의 구현
android-securityembedded-systems-securityvulnerability-analysis+3
2개월 전
isa_recovery preview

isa_recovery

GitHubinfobyte/isa_recovery

ISA Recovery

embedded-systems-securityreverse-engineeringhardware-security+5
25개월 전
tapo-c260-rce preview

tapo-c260-rce

GitHubl0lsec/tapo-c260-rce

PoC 익스플로잇 체인 — TP-Link Tapo C260 카메라용 CVE-2026-0651/0652/0653. @spaceraccoon의 연구.
embedded-systems-securityiot-securityvulnerability-analysis+7
28개월 전
CVE-2023-40459 preview

CVE-2023-40459

GitHubmajidmc2/cve-2023-40459

CVE-2023-40459의 PoC (ACEmanager에 대한 DoS)
embedded-systems-securityiot-securityvulnerability-analysis+2
42년 전
CVE-2026-21014-CAN-Bus-Frame-Replay-Attack-on-Automotive-ECU preview

CVE-2026-21014-CAN-Bus-Frame-Replay-Attack-on-Automotive-ECU

GitHubgeorge0papasotiriou/cve-2026-21014-can-bus-frame-replay-attack-on-automotive-ecu

CVE-2026-21014을 시연하기 위해 캡처된 CAN 버스 프레임을 재생하여, 인증 및 신선도(freshness) 검사 누락이 허가되지 않은 자동차 ECU 동작을 가능하게 하는 방식을 보여줍니다.
embedded-systems-securityvulnerability-analysisexploitation+2
3개월 전
CVE-2026-8888-Printer-Firmware-Unsigned-Update-via-HTTP preview

CVE-2026-8888-Printer-Firmware-Unsigned-Update-via-HTTP

GitHubgeorge0papasotiriou/cve-2026-8888-printer-firmware-unsigned-update-via-http

HTTP를 통한 서명되지 않은 프린터 펌웨어 업데이트인 CVE-2026-8888을 시연하며, 업데이트 무결성 테스트를 위한 악성 업데이트 서버와 취약한 프린터 에뮬레이터를 포함합니다.

embedded-systems-securityiot-securityvulnerability-analysis+4
3개월 전
이전1…343536…55다음