
Skip to content
KitploitKITPLOIT
도구익스플로잇블로그
Log in
제출
도구익스플로잇블로그
제출

해킹, 침투 테스트 및 사이버 보안 도구를 당신의 보안 무기고에!

Kitploit은 해킹, 사이버 보안 및 침투 테스트 도구 디렉토리입니다. 최신 프로젝트 업데이트를 발견하여 취약점을 찾고, 시스템을 분석하고, 테스트를 자동화하고, 보안을 강화하세요.

··피드·문의·개인정보·© 2026 Kitploit

도구 디렉토리

카테고리

모든 카테고리 보기
Loading categories
Adversarial Attack | Kitploit
카테고리

Adversarial Attack

Adversarial ML attack frameworks, evasion techniques, and model robustness evaluation tools.

Kitploit 추천

추천 도구

10 선택됨
adversarial-robustness-toolbox preview#1

adversarial-robustness-toolbox

GitHubtrusted-ai/adversarial-robustness-toolbox
6.3k10개월 전
foolbox preview#2

foolbox

GitHubbethgelab/foolbox
3.0k2년 전
cleverhans preview#3

cleverhans

GitHubcleverhans-lab/cleverhans
6.5k3년 전
robustbench preview#5

robustbench

GitHubrobustbench/robustbench
7871년 전
robustness preview#6

robustness

GitHubmadrylab/robustness
9474년 전
garak preview#7

garak

GitHubnvidia/garak
8.8k13일 전
PyRIT preview#8

PyRIT

GitHubmicrosoft/pyrit
4.6k6시간 27분 전
promptfoo preview#9

promptfoo

GitHubpromptfoo/promptfoo
24.1k6시간 29분 전
PurpleLlama preview#10

PurpleLlama

GitHubmeta-llama/purplellama
4.4k20시간 51분 전
giskard-oss preview#11

giskard-oss

GitHubgiskard-ai/giskard-oss
5.8k1일 전
최신관련성인기최근 업데이트
346 결과
caldera preview

caldera

GitHubapache/caldera

Automated Adversary Emulation Platform

penetration-testing-frameworksexploit-frameworksctf+7
7.1k1개월 전
Awesome-MoAI-Security preview

Awesome-MoAI-Security

GitHubjinxhy/awesome-moai-security

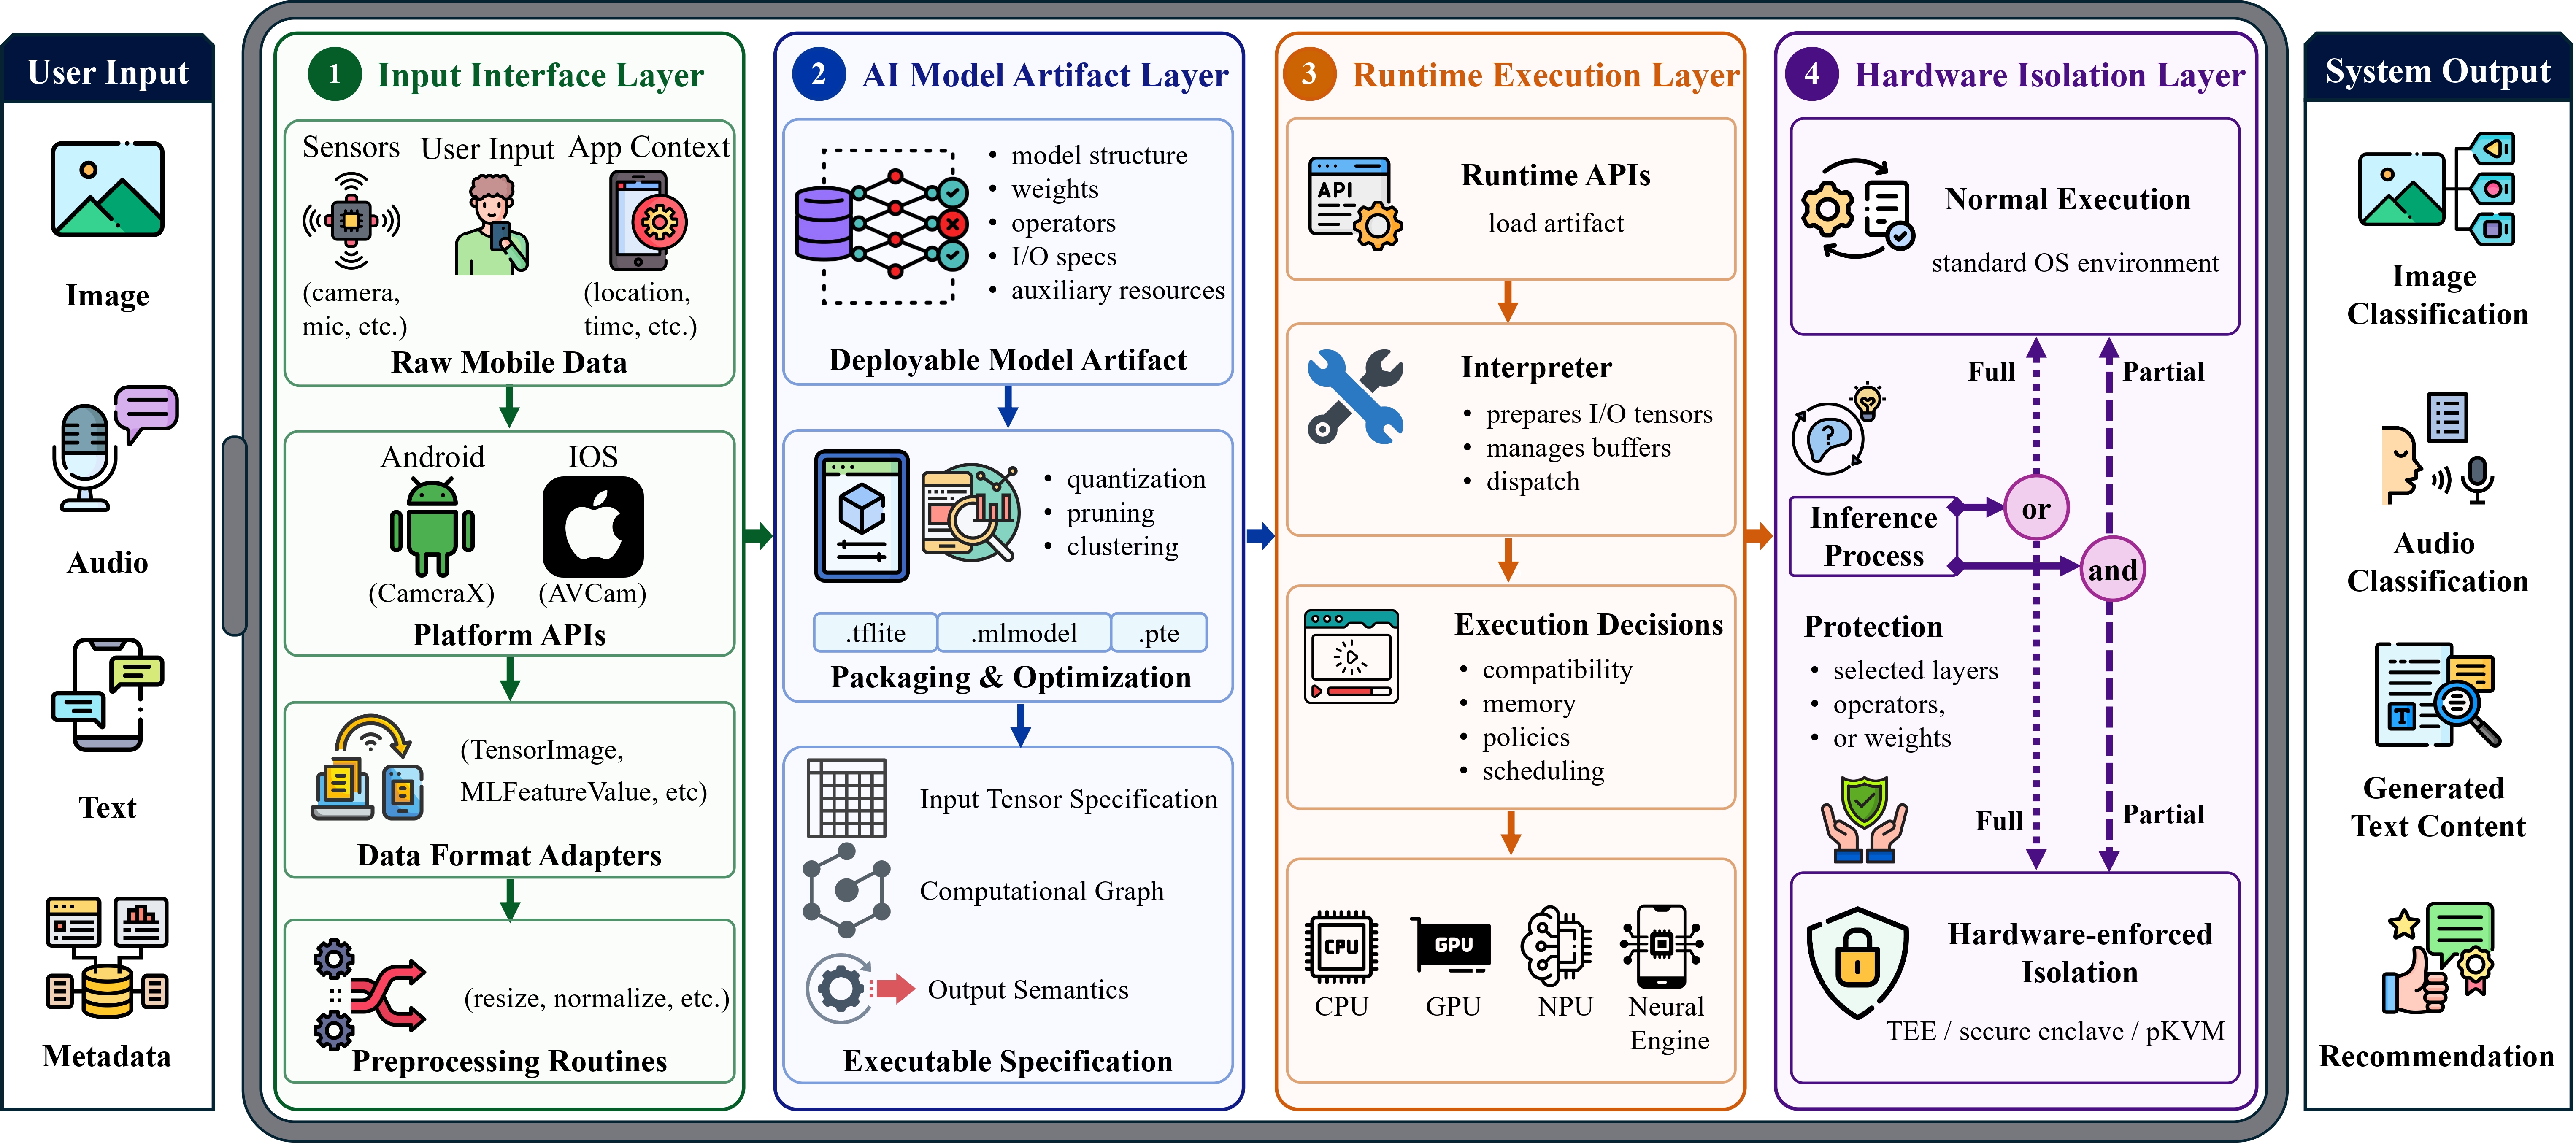
모바일 온디바이스 AI 시스템을 위한 공격 및 방어 연구의 엄선된 읽기 목록 및 분류 체계로, 적대적 공격, 백도어 공격, 모델 도난 공격, 에너지-지연 공격을 비롯해 난독화, TEE, 워터마킹 방어를 다룹니다.
android-securityios-securityreverse-engineering+9
21개월 전
SkeletonKey preview

SkeletonKey

GitHubdefineid/skeletonkey

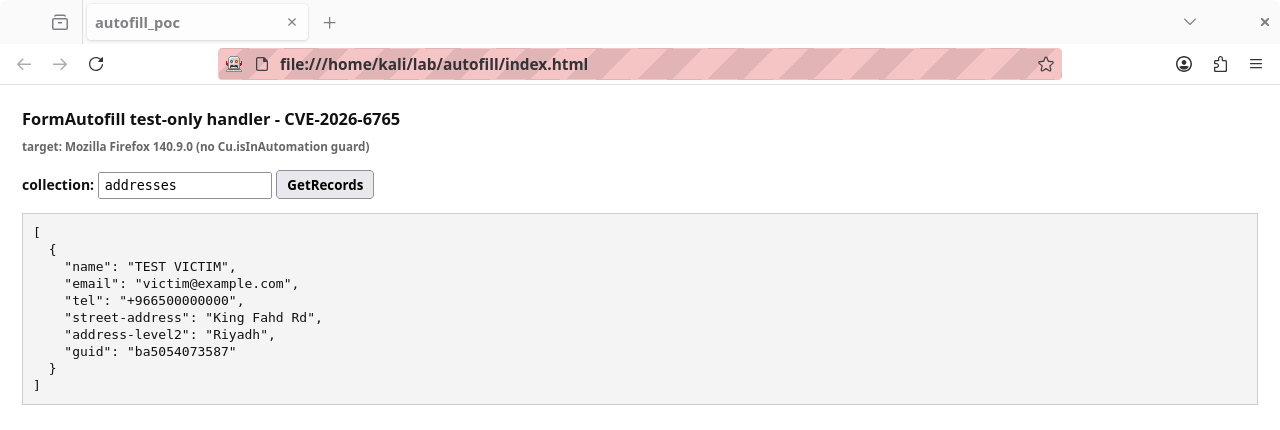
CVE-2026-6765, Test only FormAutofill handlers exposed in Firefox
vulnerability-analysisexploitationdata-exfiltration+3
1개월 전
SecOPD preview

SecOPD

GitHubpppyb/secopd

적응형 프롬프트 인젝션을 on-policy distillation을 통해 완화하는 연구 구현물로, SEP, PISmith, AgentDojo 벤치마크를 위한 학습 레시피와 평가기를 포함합니다.
machine-learningpapers-researcheducation+2
91개월 전
pgm-attack preview

pgm-attack

GitHubatsukisato/pgm-attack

PGM-인덱스에 대한 포이즈닝 공격 연구 코드로, 학습된 인덱스 성능을 저하시키기 위해 적대적 데이터를 구성하는 방법을 시연합니다.
machine-learningpapers-researchai-security+1
11개월 전
gradient-untangler preview

gradient-untangler

GitLabwattocyber/gradient-untangler

Local white-box gradient attacks for open-weight LLMs: GCG/PEZ suffix search, layer saliency, weight snapshots, and rank-1 suffix-to-delta fitting…
machine-learningred-teamingai-security+1
1개월 전
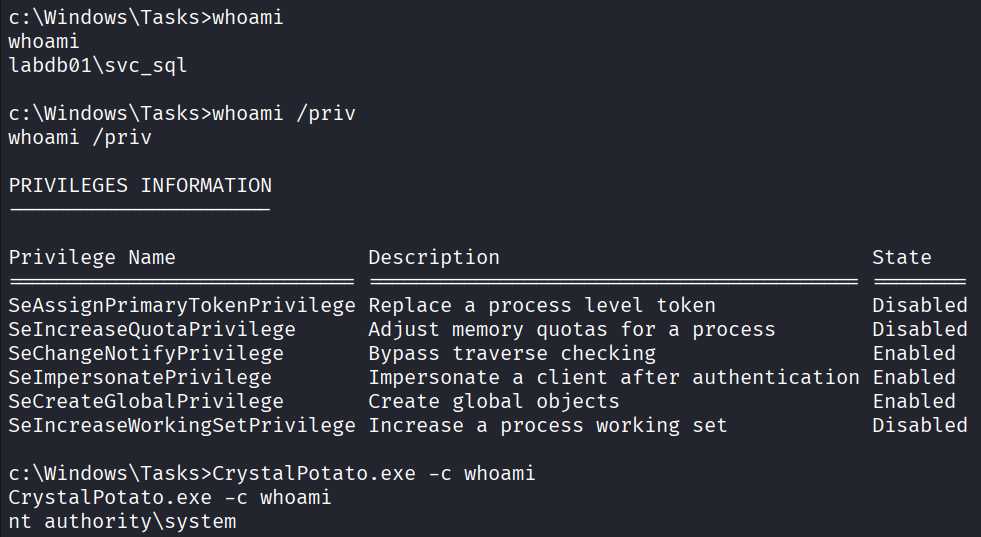
CrystalPotato preview

CrystalPotato

GitHubricardojoserf/crystalpotato

간접 시스템 콜, 동적 API 해석, 컴파일 타임 문자열 난독화를 통해 SeImpersonatePrivilege를 악용하는 GodPotato의 Crystal 포팅 버전입니다. 명령 실행, 리버스 셸 또는 사용자 추가를 지원합니다.
privilege-escalationexploitationpost-exploitation+3
1241개월 전
NoiseHound preview

NoiseHound

GitHubwarpedatom/noisehound

Detection-aware BloodHound attack-path scoring - the quietest route to your objective, calibrated across five detection tiers…
defensive-toolsprivilege-escalationlateral-movement+4
671개월 전
CVE-2026-44578 preview

CVE-2026-44578

GitHublxxexxbxx/cve-2026-44578

CVE-2026-44578에 대한 개념 증명 익스플로잇으로, 취약한 상태를 재현하여 보안 연구자들이 영향을 받는 시스템을 검증하고 완화 조치를 평가할 수 있게 해줍니다.
vulnerability-analysisexploitationadversarial-attack
11개월 전
DB_Audit_Research preview

DB_Audit_Research

GitHubmthamil107/db_audit_research

자가 무력화 감사: 낮은 권한의 PostgreSQL 역할이 트리거 기반 감사자를 가역적으로 눈멀게 하고 귀속을 오염시키는 것을 보여주는 재현 가능한 랩(PG14/16) 및 방어 기법. 합성 데이터 사용, CVE-2018-1058 프리미티브 인용.
defensive-toolsexploitationpapers-research+4
1개월 전
lldp preview

lldp

GitHubwhispergate/lldp

Mythic용 C2 프로파일로, 암호화된 피어 투 피어 에이전트 트래픽을 IEEE 802.1AB LLDP 조직별 TLV를 통해 터널링하여 은밀한 Layer 2 명령 및 제어를 수행합니다.
ids-ips-evasioncommand-and-controlred-teaming+1
231개월 전
DutchOven preview

DutchOven

GitHubloosehose/dutchoven

Application-scoped Windows network brownouts in native C and BOF form
post-exploitationnetwork-securityred-teaming+2
231개월 전
CVE-2026-73292 preview

CVE-2026-73292

GitHubcamillegr/cve-2026-73292

CVE-2026-73292에 대한 개념 증명 익스플로잇: Semaphore UI 비밀번호 변경 엔드포인트를 대상으로 하는 CSRF 공격으로, 인증된 사용자의 비밀번호를 사용자 모르게 재설정하는 악성 페이지를 제공합니다.
vulnerability-analysisexploitationweb-application-exploitation+3
1개월 전
xspawn preview

xspawn

GitHubcenobyte-vincit/xspawn

launchd의 비공개 XPC 인터페이스를 통해 macOS 프로그램을 스폰하며 exec를 사용하지 않으므로, EDR이 launchd를 부모 프로세스로 기록하게 됩니다. 일회성(one-shot), KeepAlive, plist 기반 작업을 지원합니다.
persistence-mechanismsids-ips-evasionpost-exploitation+2
1개월 전
nullorigin preview

nullorigin

GitHubrakib-nyc/nullorigin

연구 전용 AI 워터마크 견고성 툴킷: 로컬 리버스 프록시가 C2PA/EXIF/XMP, Unicode, 이미지/오디오 스테가노그래피, OOXML/PDF 메타데이터를 제거하고 Trojan Source를 스캔합니다.

static-code-analysisweb-proxies-interceptionsteganography+4
41개월 전
TTPForge preview

TTPForge

GitHubfacebookincubator/ttpforge

TTPForge는 공격자의 전술, 기법, 절차(TTP)를 개발, 자동화, 실행하기 위한 사이버 보안 프레임워크입니다.
penetration-testing-frameworksscripting-automationred-teaming+2
4371개월 전
the-sanitizer-is-the-weapon-cve-2026-68749-cve-2026-68750-quadratic-dos-in-elixir-html-sanitize-ex preview

the-sanitizer-is-the-weapon-cve-2026-68749-cve-2026-68750-quadratic-dos-in-elixir-html-sanitize-ex

GitHubhunt-benito/the-sanitizer-is-the-weapon-cve-2026-68749-cve-2026-68750-quadratic-dos-in-elixir-html-sanitize-ex

조작된 HTML을 통해 Elixir html_sanitize_ex의 이차(quadratic) DoS를 입증하는 PoC; 타이밍 벤치마크, 원격 악용 curl, 패치된 버전에 대한 검증을 포함합니다.
payload-generationvulnerability-analysisexploitation+3
1개월 전
agent-opfor preview

agent-opfor

GitHubkeyvaluesoftwaresystems/agent-opfor

AI 에이전트 및 MCP 서버를 위한 오픈소스 적대자 모의

vulnerability-scannersapi-security-testingweb-security+5
5711개월 전
이전1…345…20다음