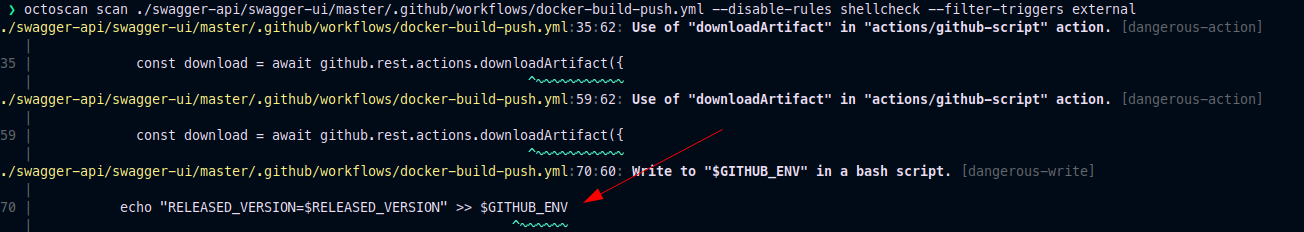
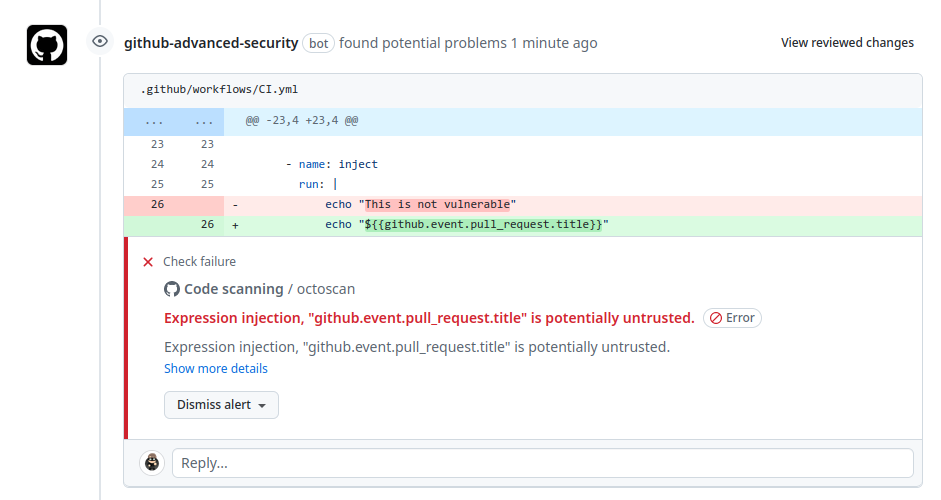
Octoscan は GitHub Action ワークフロー用の静的脆弱性スキャナです。

$ go mod tidy
$ go build
または docker を使用する場合:
$ docker pull ghcr.io/synacktiv/octoscan:latest
Octoscan はローカルの git リポジトリに対して実行できます。また、dl アクションを使用してすべてのワークフローをダウンロードすることもできます:
$ octoscan dl -h
Octoscan.

Usage:
	octoscan dl [options] --org <org> [--repo <repo> --token <pat> --default-branch --max-branches <num> --path <path> --output-dir <dir> --include-archives]

Options:
	-h, --help  						Show help
	-d, --debug  						Debug output
	--verbose  						Verbose output
	--org <org>  						Organizations to target
	--repo <repo>  						Repository to target
	--token <pat>  						GHP to authenticate to GitHub
	--default-branch  					Only download workflows from the default branch
	--max-branches <num>  					Limit the number of branches to download
	--path <path>  						GitHub file path to download [default: .github/workflows]
	--output-dir <dir>  					Output dir where to download files [default: octoscan-output]
	--include-archives  					Also download archived repositories
./octoscan dl --token ghp_<token> --org apache --repo incubator-answer
何を実行すればよいかわからない場合は、以下を実行してください:
./octoscan scan path/to/repos/ --disable-rules shellcheck,local-action --filter-triggers external
これにより誤検知が減り、より興味深い結果が得られます。
dl コマンドでワークフローをダウンロードした場合、既定では octoscan がすべてのブランチのすべてのワークフローをダウンロードするため、ワークフローが重複している可能性があります。重複したワークフローを削除して分析を高速化するには、分析の実行前に fdupes コマンドを使用できます:
fdupes -n -r -N -d path/to/repo
$ octoscan scan -h
octoscan

Usage:
	octoscan scan [options] --list-rules
	octoscan scan [options] <target>
	octoscan scan [options] <target> [--debug-rules --filter-triggers=<triggers> --filter-run --ignore=<pattern> ((--disable-rules | --enable-rules ) <rules>) --config-file <config>]

Options:
	-h, --help
	-v, --version
	-d, --debug
	--verbose
	--format <format>  				Output format, json, sarif or custom template to format error messages in Go template syntax. See https://github.com/rhysd/actionlint/tree/main/docs/usage.md#format
	--oneline 					Use one line per one error. Useful for reading error messages from programs

Args:
	<target>					Target File or directory to scan
	--filter-triggers <triggers>			Scan workflows with specific triggers (comma separated list: "push,pull_request_target" or pre-configured: external/allnopr)
	--filter-run					Search for expression injection only in run shell scripts.
	--ignore <pattern>				Regular expression matching to error messages you want to ignore.
	--disable-rules <rules>				Disable specific rules. Split on ","
	--enable-rules <rules>				Enable specific rules, this will disable all other rules. Split on ","
	--debug-rules					Enable debug rules.
	--config-file <config>				Config file.

Examples:
	$ octoscan scan ci.yml --disable-rules shellcheck,local-action --filter-triggers external
このツールは、push/pull_request イベントでリポジトリをスキャンする GitHub Action として直接使用することもできます。詳細についてはこのリポジトリを確認してください。
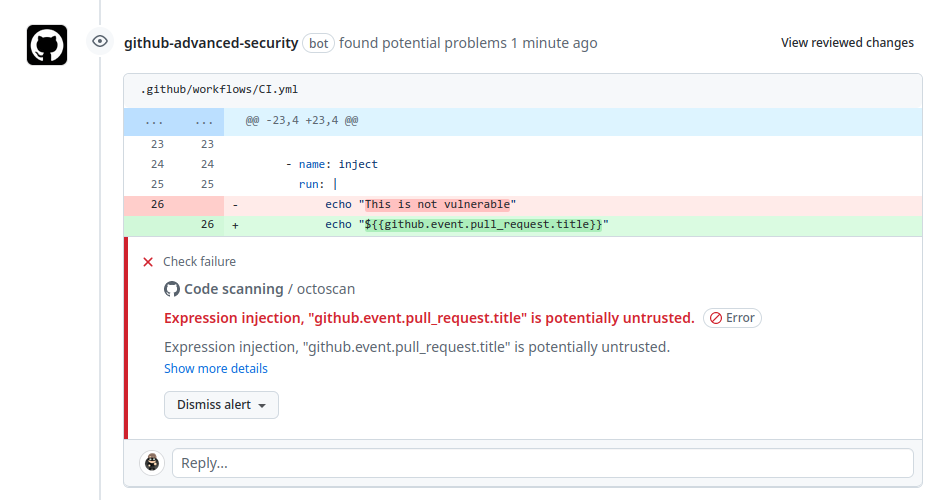
ルールの完全なリストは、次のコマンドで確認できます:
$ octoscan scan --list-rules
2024/08/07 16:50:48 [INFO] Available rules
- shellcheck
	Checks for shell script sources in "run:" using shellcheck
- credentials
	Checks for credentials in "services:" configuration
- dangerous-action
	Check for dangerous actions.
- dangerous-checkout
	Check for dangerous checkout.
- expression-injection
	Check for expression injection.
- dangerous-write
	Check for dangerous write operation on $GITHUB_OUTPUT or $GITHUB_ENV.
- local-action
	Check for local actions.
- runner-label
	Checks for GitHub-hosted and preset self-hosted runner labels in "runs-on:"
- unsecure-commands
	Check 'ACTIONS_ALLOW_UNSECURE_COMMANDS' env variable.
- known-vulnerability
	Check for known vulnerabilities.
- bot-check
	Check for if statements that are based on a bot identity.
- dangerous-artefact
	Check for workflow that upload artefacts containing sensitive files.
- debug-external-trigger
	Check for workflow that can be externally triggered.
- debug-artefacts
	Check for workflow that upload artefacts.
- debug-js-exec
	Check for workflow that execute system commands in JS scripts.
- debug-oidc-action
	Check for OIDC actions.
- repo-jacking
	Verify that external actions are pointing to a valid GitHub user or organization.
workflow_run や pull_request_target などのトリガーは、シークレットへの読み取りアクセス権を持ち、対象リポジトリへの書き込みアクセス権を持つ可能性があるため、特権コンテキストで実行されます。信頼できないコードに対して明示的なチェックアウトを実行すると、そのようなコンテキストで攻撃者のコードがダウンロードされることになります。

このルールは、危険なアクションが使用されている場合にユーザーに警告します。主に信頼できないアーティファクトに焦点を当てています。
異なるワークフロー間でデータを渡すためにアーティファクトを使用するのは一般的な慣行です。これは workflow_run トリガーでよく見られ、トリガー元のワークフローがデータを準備し、それがトリガー先のワークフローに送信されます。このアーティファクトデータは信頼できない性質を持つため、注意して扱い、潜在的な脅威として認識することが重要です。この脆弱性は、悪意のある攻撃者などの外部エンティティがアーティファクトデータの内容に影響を与えられるという事実から生じます。

GitHub は、ワークフロー内のすべてのステップで使用できる既定の環境変数を作成します。特に GITHUB_ENV と GITHUB_OUTPUT 変数は重要です。あるステップで環境変数を定義し、その変数を別のステップで使用することが可能です。これは、関連する変数に書き込むことで実現できます。設定される変数の内容をユーザーが制御できる場合、任意のコード実行につながる可能性があります。