日々の管理業務で特定のメールが SPAM/迷惑メールに振り分けられた理由を理解したい場合でも、Red-Team のフィッシングシミュレーションの目的であっても、このスクリプトは役立ちます!
このアイデアは、MS Defender for Office365 を備えた商用 MS Office365 E5 環境を対象に、商用フィッシングシミュレーション演習を実施した際に生まれました。想像がつくと思いますが、フィッシングシミュレーションの観点から見ると、かなり強固なセキュリティスタックです。 手作業でこれらすべての Office365 SMTP ヘッダーを調べ、SCL 値を選り分けようとした後、SMTP ヘッダー用の適切なパーサーを作成する時が来ました。
時が経つにつれ、私はさらに多くの SMTP ヘッダーへの対応を追加していき、そしてここに完成形があります。現在では数十種類の異なるヘッダーを解釈するツールです。
このツールは、すべての SMTP ヘッダーを含む *.EML または *.txt ファイルを入力として受け取ります。次に、興味深いヘッダーのサブセットを抽出し、105+ のテストを使用して、それらを可能な限りデコードしようとします。
このスクリプトはまた、すべての IPv4 アドレスとドメイン名を抽出し、それらの完全な DNS 解決を実行します。
結果として得られる出力には、このメールがブロックされた可能性がある理由に関する有用な情報が含まれます。
クライアントに送信する前にフィッシング HTML コードを装飾したい場合は、私の phishing-HTML-linter.py に通すこともできます。このツールは、メールのスパムスコアを上昇させる HTML 内の 悪い匂い を見つけるのにかなり優れた仕事をします。
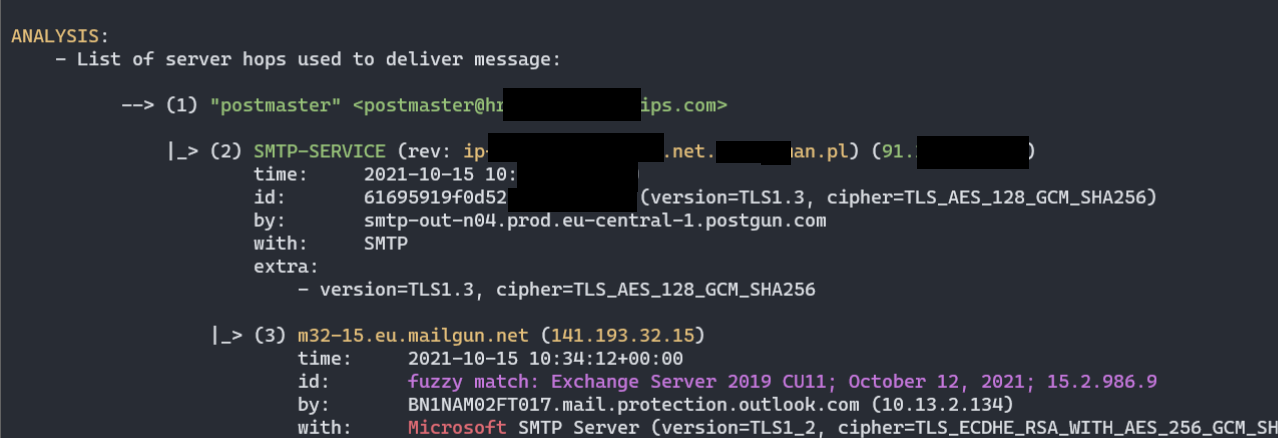
Received ヘッダーを見やすく解析):
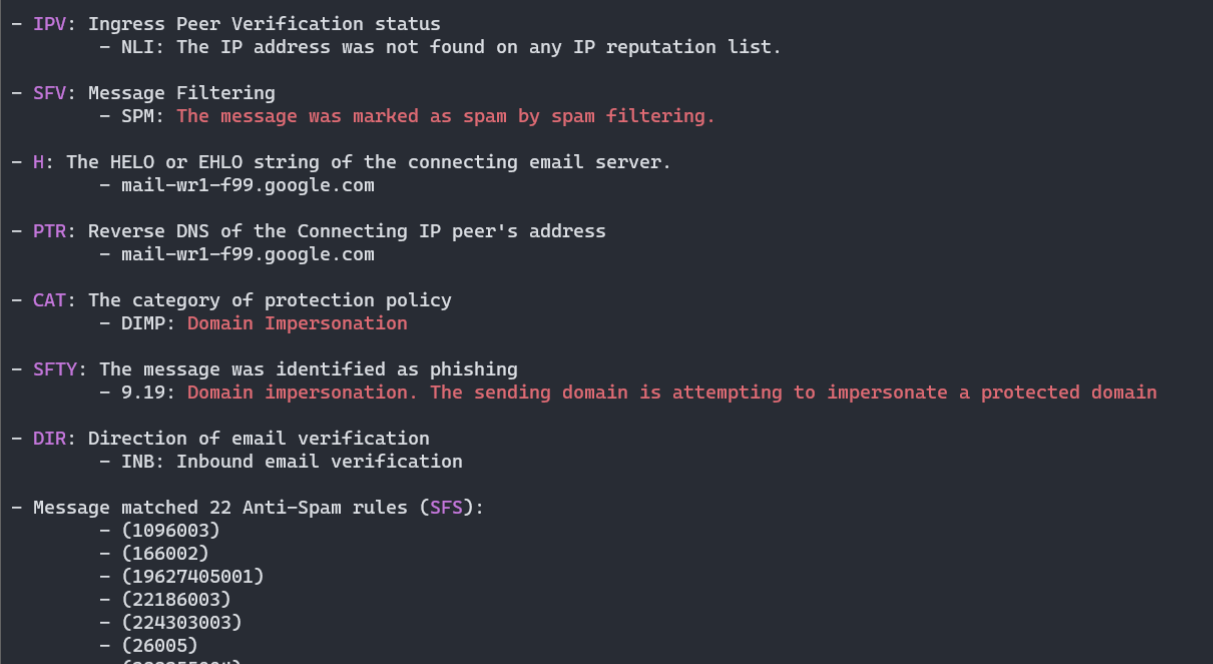
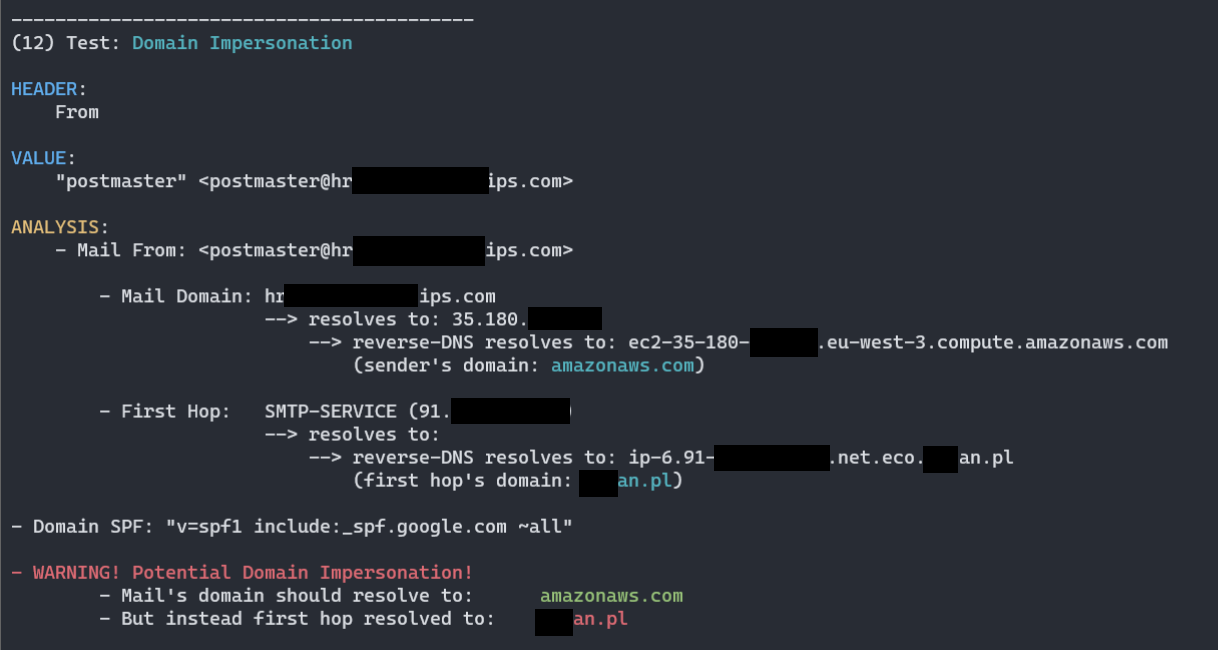

py decode-spam-headers.py headers.txt -f html -o report.html):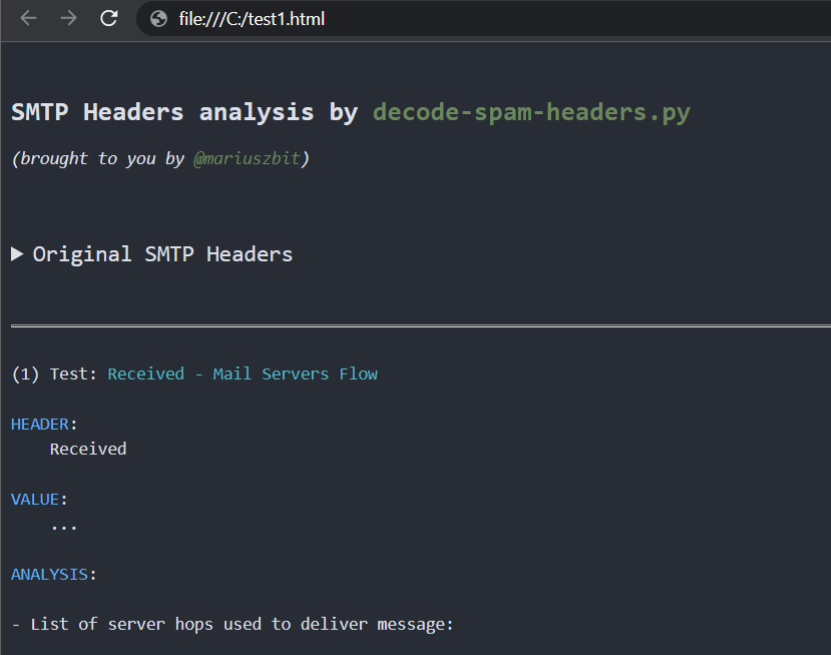
処理されるヘッダー (85+ 以上のヘッダーが解析されます):
X-forefront-antispam-reportX-exchange-antispamX-exchange-antispam-mailbox-deliveryX-exchange-antispam-message-infoX-microsoft-antispam-report-cfa-testReceivedFromToSubjectThread-topicReceived-spfX-mailerX-originating-ipUser-agentX-forefront-antispam-reportX-microsoft-antispam-mailbox-deliveryX-microsoft-antispamX-exchange-antispam-report-cfa-testX-spam-statusX-spam-levelX-spam-flagX-spam-reportX-vr-spamcauseX-ovh-spam-reasonX-vr-spamscoreX-virus-scannedX-spam-checker-versionX-ironport-avX-ironport-anti-spam-filteredX-ironport-anti-spam-resultX-mimecast-spam-scoreSpamdiagnosticmetadataX-ms-exchange-atpmessagepropertiesX-msfblX-ms-exchange-transport-endtoendlatencyX-ms-oob-tlc-oobclassifiersX-ip-spam-verdictX-amp-resultX-ironport-remoteipX-ironport-reputationX-sbrsX-ironport-sendergroupX-policyX-ironport-mailflowpolicyX-remote-ipX-sea-spamX-fireeyeX-antiabuseX-tmase-versionX-tm-as-product-verX-tm-as-resultX-imss-scan-detailsX-tm-as-user-approved-senderX-tm-as-user-blocked-senderX-tmase-resultX-tmase-snap-resultX-imss-dkim-white-listX-tm-as-result-xfilterX-tm-as-smtpX-scanned-byX-mimecast-spam-signatureX-mimecast-bulk-signatureX-sender-ipX-forefront-antispam-report-untrustedX-microsoft-antispam-untrustedX-sophos-senderhistoryX-sophos-rescanX-MS-Exchange-CrossTenant-IdX-OriginatorOrgIronPort-DataIronPort-HdrOrdrX-DKIMDKIM-FilterX-SpamExperts-ClassX-SpamExperts-EvidenceX-Recommended-ActionX-AppInfoX-SpamX-TM-AS-MatchedIDX-MS-Exchange-EnableFirstContactSafetyTipX-MS-Exchange-Organization-BypassFocusedInboxX-MS-Exchange-SkipListedInternetSenderX-MS-Exchange-ExternalOriginalInternetSenderX-CNFS-AnalysisX-Authenticated-SenderX-Apparently-FromX-Env-SenderSenderこれらのヘッダーのほとんどは完全には文書化されていないため、スクリプトはすべての詳細を正確に特定することはできませんが、少なくとも見つけられたすべての情報を収集します。
(5) Test: X-Forefront-Antispam-Report
HEADER: X-Forefront-Antispam-Report
VALUE: CIP:209.85.167.100;CTRY:US;LANG:de;SCL:5;SRV:;IPV:NLI;SFV:SPM;H:mail-lf1-f100.google.com;PTR:mail-l f1-f100.google.com;CAT:DIMP;SFTY:9.19;SFS:(4636009)(956004)(166002)(6916009)(356005)(336012)(19 625305002)(22186003)(5660300002)(4744005)(6666004)(35100500006)(82960400001)(26005)(7596003)(7636003)(554460 02)(224303003)(1096003)(58800400005)(86362001)(9686003)(43540500002);DIR:INB;SFTY:9.19;
[...]
    - Message matched 24 Anti-Spam rules (SFS):           <============ opaque anti-spam rules
            - (1096003)
            - (166002)
            - (19625305002)
            - (22186003)
            - (224303003)
            - (26005)
            - (336012)
            - (356005)
            - (35100500006)         - (SPAM) Message contained embedded image.
このプロセスは完全に手動であり、特別に設計されたメールをOffice365メールサーバーに送信し、その後、収集したルールを手動でレビューして関連付けます。

すでに60通以上のメールを送信しましたが、現時点でMicrosoftのルールについて言えることは次のとおりです。```py

    #
    # Below rules were collected solely in a trial-and-error manner or by scraping any
    # pieces of information from all around the Internet.
    #
    # They do not represent the actual Anti-Spam rule name or context and surely represent
    # something close to what is understood (or they may have totally different meaning).
    #
    # Until we'll be able to review anti-spam rules documention, there is no viable mean to map
    # rule ID to its meaning.
    #

    Anti_Spam_Rules_ReverseEngineered = \
    {
        '35100500006' : logger.colored('(SPAM) Message contained embedded image.', 'red'),

        # https://docs.microsoft.com/en-us/answers/questions/416100/what-is-meanings-of-39x-microsoft-antispam-mailbox.html
        '520007050' : logger.colored('(SPAM) Moved message to Spam and created Email Rule to move messages from this particular sender to Junk.', 'red'),

        # triggered on an empty mail with subject being: "test123 - viagra"
        '162623004' : 'Subject line contained suspicious words (like Viagra).',

        # triggered on mail with subject "test123" and body being single word "viagra"
        '19618925003' : 'Mail body contained suspicious words (like Viagra).',

        # triggered on mail with empty body and subject "Click here"
        '28233001' : 'Subject line contained suspicious words luring action (ex. "Click here"). ',

        # triggered on a mail with test subject and 1500 words of http://nietzsche-ipsum.com/
        '30864003' : 'Mail body contained a lot of text (more than 10.000 characters).',

        # mails that had simple message such as "Hello world" triggered this rule, whereas mails with
        # more than 150 words did not.
        '564344004' : 'HTML mail body with less than 150 words of text (not sure how much less though)',

        # message was sent with a basic html and only one <u> tag in body.
        '67856001' : 'HTML mail body contained underline <u> tag.',

        # message with html,head,body and body containing simple text with no b/i/u formatting.
        '579124003' : 'HTML mail body contained text, but no text formatting (<b>, <i>, <u>) was present',

        # This is a strong signal. Mails without <a> doesnt have this rule.
        '166002' : 'HTML mail body contained URL <a> link.',