#1

 lore-hex/quill-router
安全なLLMプロキシングのためのTrustedRouter.comリポジトリ
 mondoohq/cnspec
ビルドからランタイムまでのすべてを保護する、オープンソースのクラウドネイティブセキュリティ
 lxc/incus-os
不変のLinux OSイメージ。Incusコンテナおよび仮想マシンの実行に最適化されており、UEFIセキュアブート、TPM 2.0ディスク暗号化、および安全なインフラストラクチャデプロイメントのための自動イメージビルドを備えています。
 trufflesecurity/trufflehog
Find, verify, and analyze leaked credentials
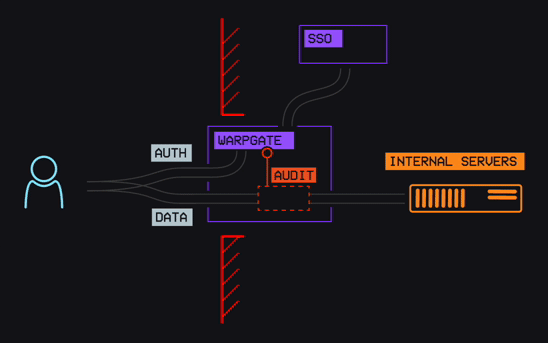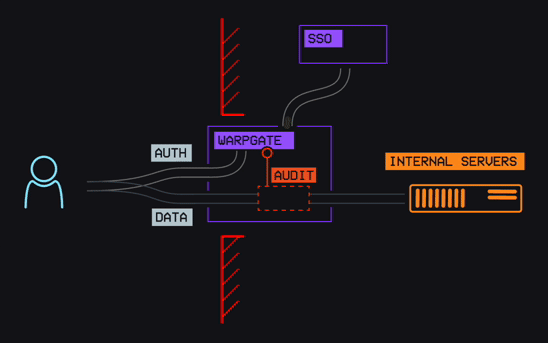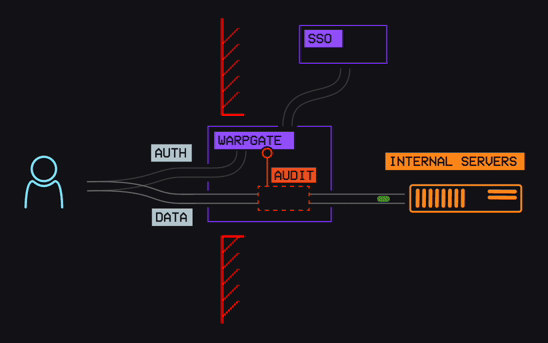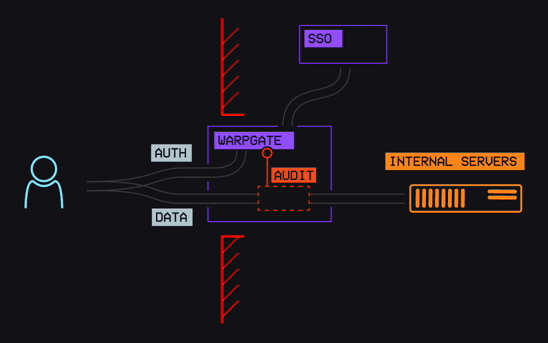 warp-tech/warpgate
Fully transparent SSH, HTTPS, Kubernetes, database and RDP/VNC bastion/PAM that doesn't need additional client-side software
 ariesq/gh-safe-repo
Python CLI that creates GitHub repos with safe defaults — branch protection, Dependabot, secret scanning, and pre-flight security scanning — applied…
 nvidia/openshell
自律型AIエージェント向けのサンドボックス化されたランタイム。ファイルシステム、ネットワーク、プロセスの制約を強制する宣言型YAMLポリシーと、エンドポイントに紐付けられた認証情報の注入機能を備えています。
 kyverno/kyverno
アドミッションコントロール、リソースミューテーション、バックグラウンドスキャン、コンテナイメージの署名検証を通じて、Kubernetesクラスターにセキュリティとコンプライアンスを強制します。
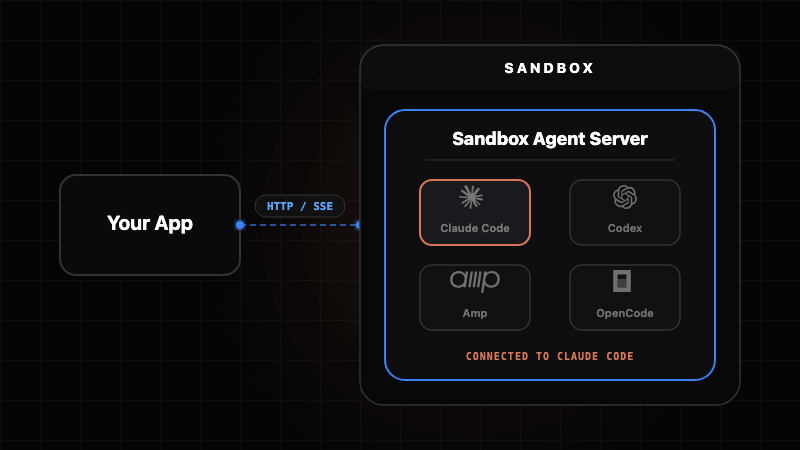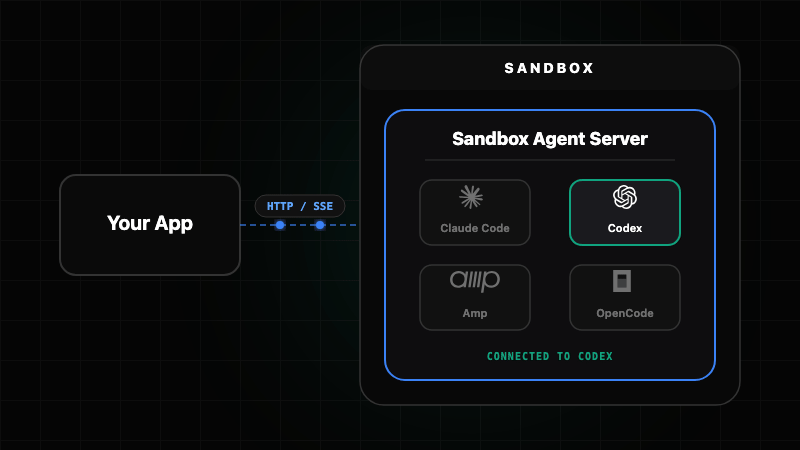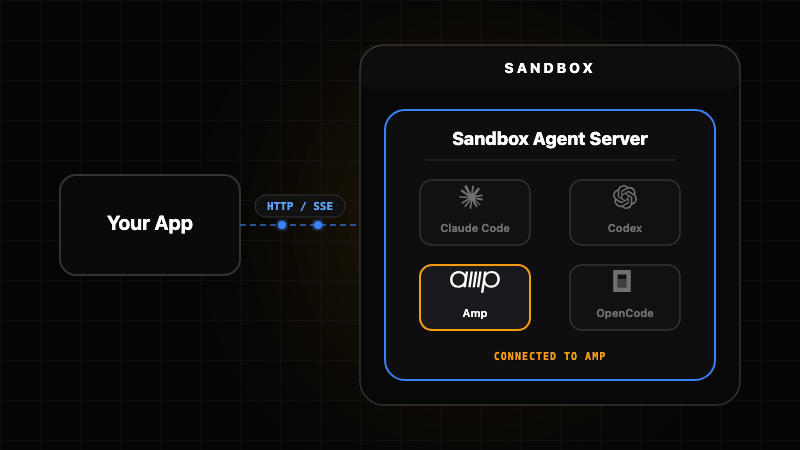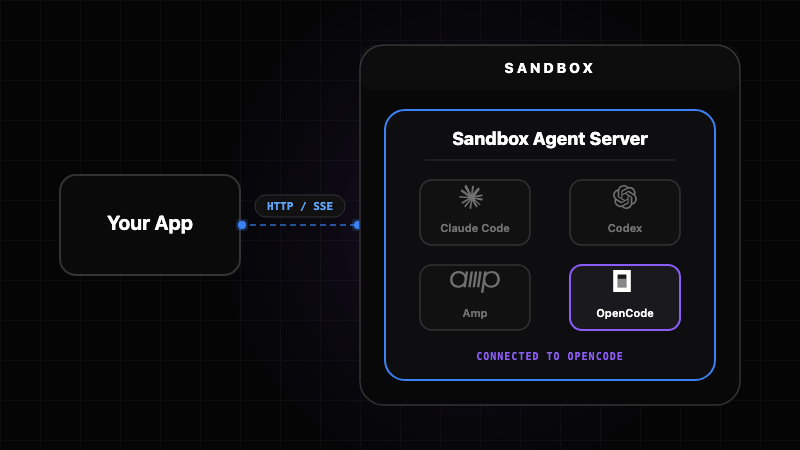 rivet-dev/sandbox-agent
エージェントごとの永続プロセス、再起動後も保持されるメモリを備える
 cisco-ai-defense/defenseclaw
Security Governance for Agentic AI
 canyonroad/agentsh
AIエージェント向けの実行層セキュリティ(ELS) — 監査機能付きポリシー強制シェル。
 wazuh/wazuh
Open-source XDR and SIEM platform for threat detection, log analysis, file integrity monitoring, vulnerability assessment, and compliance management…
 google/osv-scanner
Goで書かれた脆弱性スキャナーで、https://osv.dev が提供するデータを使用します。
 cybersecsi/raudi
DockerイメージをGitHub Actionsを通じて自動生成し、最新に保つためのリポジトリ。
 cartography-cncf/cartography
30以上のクラウド、ID、SaaSプラットフォームからインフラ資産とその関係性をNeo4jグラフに取り込み、セキュリティクエリとルールベース分析を可能にします。
 cicd-sensor/cicd-sensor
eBPF-powered runtime security sensor for CI/CD pipelines. Detects supply-chain attacks, logs process ancestry and file access, and provides forensic…
 prismorsec/prismor
Self-hosted runtime control plane for AI agents. Observe or HITL approve or Block rogue tool calls before it executes: secret leaks, prompt…