Skip to content
KitploitKITPLOIT
ツールエクスプロイトブログ
Log in
提出
ツールエクスプロイトブログ
提出

ハッキング、侵入テスト、サイバーセキュリティツールをあなたのセキュリティアーセナルに!

Kitploitはハッキング、サイバーセキュリティ、ペネトレーションテストのツールディレクトリです。最新のプロジェクトアップデートを見つけて、脆弱性の発見、システム分析、テストの自動化、セキュリティの強化を行いましょう。

フィードお問い合わせプライバシー© 2026 Kitploit

ツールディレクトリ

カテゴリ

すべてのカテゴリを見る
Loading categories
ツール/GitHubGitHub/prismorsec/prismor
Defensive ToolsContainer SecurityDevSecOpsSecret DetectionThreat IntelligenceSupply Chain SecurityIncident ResponseAI Security
GitHubprismorsec/prismor

prismor

Self-hosted runtime control plane for AI agents. Observe or HITL approve or Block rogue tool calls before it executes: secret leaks, prompt injection, supply chain etc in a local dashboard. Agent agnostic (Claude, codex, langchain etc.)

リポジトリを見るウェブサイト
2832612614時間2分前Kitploit レビュー済み
共有
要求された言語のコンテンツは利用できません。英語版を表示しています。

Prismor

PyPI License OpenSSF Best Practices PRs Welcome X DeepWiki Discord

Runtime security for Claude Code, Codex, Langchain and other AI agents frameworks/harness.

Prismor is highly customizable based on user's own policies. Observe or enforce mode to see and control agent activity in a local self-serve dashboard

Website • Onboard with Skill

Claude Code   Codex CLI   Gemini CLI   Cursor   GitHub Copilot   OpenCode   Pi Agent   Kiro   Kimi Code   Trae / Trae CN   Google Antigravity

Plus Grok Build, Crush, OpenHands, Qwen Code, Continue CLI, Goose, Hermes, OpenClaw, Devin CLI, Factory Droid, Aider, and more — see AGENT_INTEGRATIONS.md for the full coverage matrix
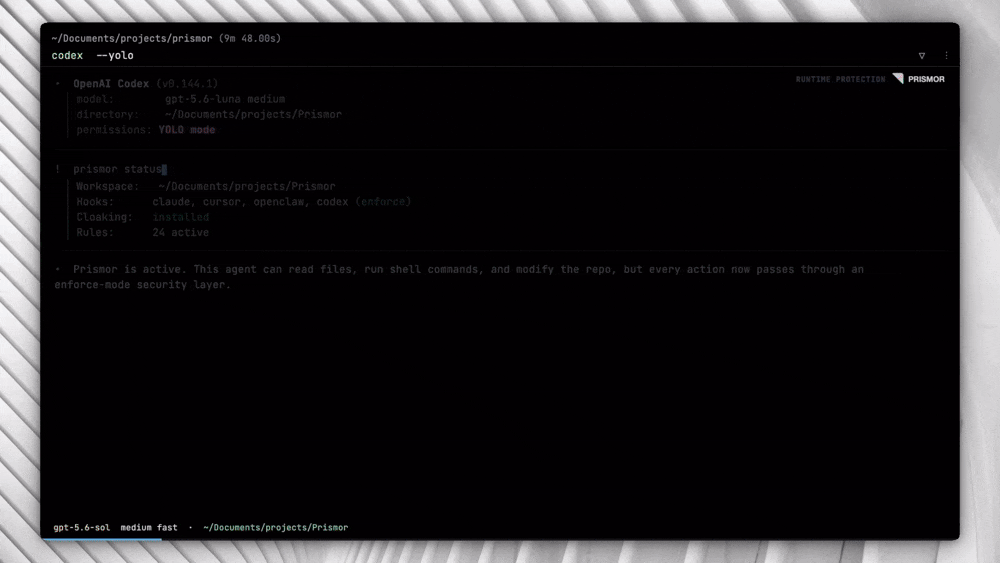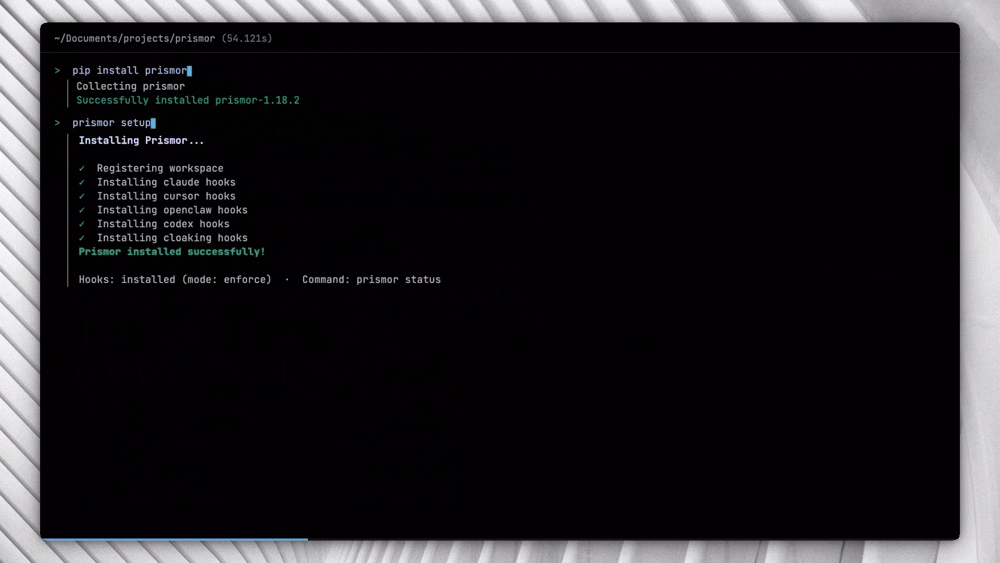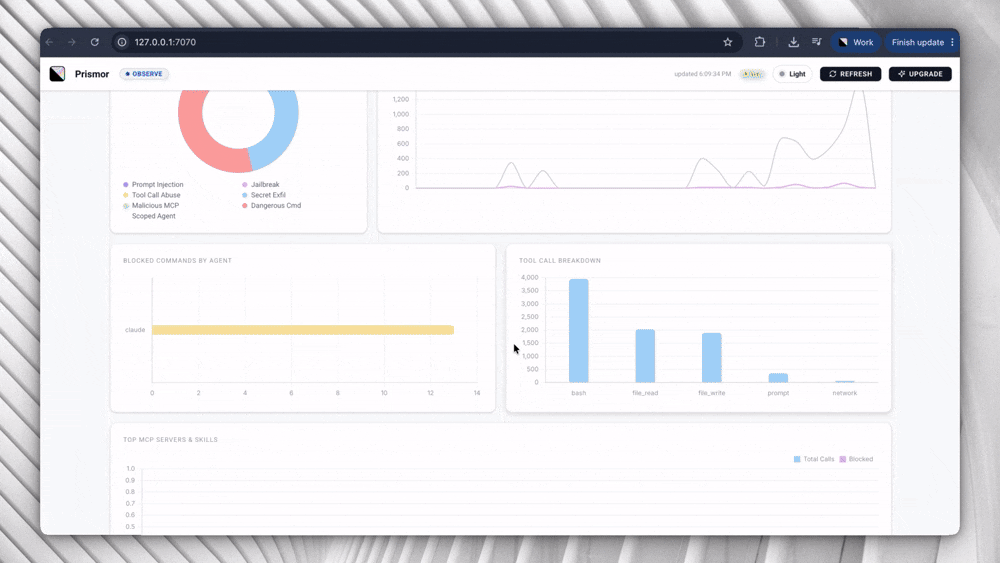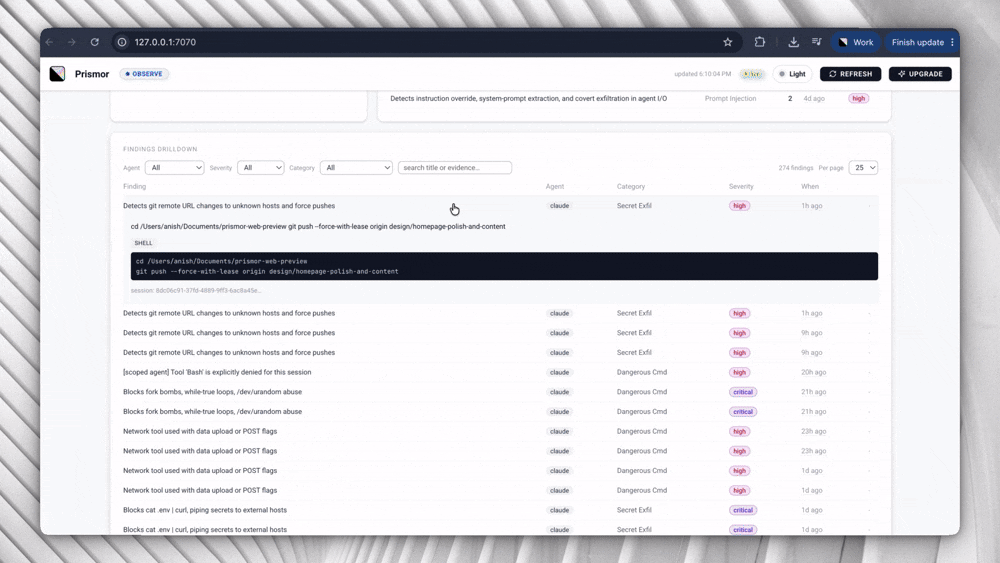

Prismor demo: pip install prismor, prismor setup, then the dashboard's overview, sessions, extensions and MCP servers views


The Problem

AI agents execute shell commands, read and write files, access credentials, and call external APIs. They do this autonomously, often across many steps, with limited checkpoints.

This creates risks that traditional security tooling isn't designed for:

  • Prompt injection - malicious content in a file, issue, or web page can redirect the agent mid-task
  • Unintended destructive actions - an agent misinterprets an instruction and runs something irreversible
  • Secret exfiltration - an agent reads .env or credential files as part of a debugging task and sends the content outbound
  • Lack of visibility and identity - an agent can spawn subagents and lack complete visibility for the end user
  • Privilege escalation - an agent modifies sudoers, CI pipelines, or file permissions to resolve a permission error
  • Dependency manipulation - an agent installs or rewrites a package at the direction of injected input
  • Supply chain risk - an agent installs a vulnerable or 0-day package while optimizing for code velocity

Standard OS-level and endpoint security tools monitor the kernel and filesystem. But they lack the context to make AI usable


Quick Start (30s)

pip install prismor
prismor setup

For the Skill, curl, and git-clone alternatives, plus PEP 668 systems and secret-cloaking setup, see the full installation guide.



Supported Agents

ツールをダウンロード

人気

すべて見る →

コミュニティで最も使われているツールを見つけましょう。

  • 1

    OsintHunter

    letox4/osinthunter

    🎯 究極のOSINTツールキット:調査グラフ、信頼度スコアリング、エイリアスファミリー、マップ、タイムライン、レポート。49個のモジュール、400以上のサイト、APIキー不要。

    755
  • 2

    ghostlock-app

    yukonga/ghostlock-app

    GhostLock ワンタップ実行アプリ(CVE-2026-43499)

    510
  • 3

    ARTEX

    baarai/artex

    プランナー/ワーカーエージェント、資産グラフと探索グラフ、MITMトラフィック記録、脆弱性の再テストを備えたLLMマルチエージェント自律ペネトレーションテストプラットフォーム。

    415
  • 4

    redforge

    cybersecurity91/redforge

    ブラウザ側のレッドチームツールキット。偵察、ペイロード生成、認証情報攻撃、暗号、エンコーディング、エンゲージメントレポート向けの102のオフラインツールを備えています。

    343
  • 5

    antifox

    antifox-ai/antifox

    偵察、攻撃対象領域の探索、エクスプロイト検証、証拠に基づくレポート提供を実行するAIマルチエージェント自律ペネトレーションテストプラットフォーム。

    259
  • 6

    CyberStrikeAI

    ed1s0nz/cyberstrikeai

    AIネイティブなサイバーセキュリティのためのアクションシステム。意図がガバナンスされた実行に変わり、証拠が運用記憶となり、すべての操作が次の操作を改善する。

    258

すべてのツールを探索

ツールコレクションを閲覧

すべてのツールを見る →