

Autonomous AI red team framework that chains reconnaissance, exploitation, and post-exploitation into a single pipeline, then triages findings, implements code fixes, and opens pull requests.

Unmask the hidden before the world does
An autonomous AI framework that chains reconnaissance, exploitation, and post-exploitation into a single pipeline, then goes further by triaging every finding, implementing code fixes, and opening pull requests on your repository. From first packet to merged patch, with human oversight at every critical step.









LEGAL DISCLAIMER: This tool is intended for authorized security testing, educational purposes, and research only. Never use this system to scan, probe, or attack any system you do not own or have explicit written permission to test. Unauthorized access is illegal and punishable by law. By using this tool, you accept full responsibility for your actions. Read Full Disclaimer
🏆 Flagship result: RedAmon solves 101 / 104 (97.1%) of the XBOW web-security benchmark fully black-box. Every solve ships a complete, unedited raw agent session and a reproducible, step-by-step walkthrough: open any row and read exactly how the flag fell, tool call by tool call. Auditable, line by line. See the XBOW Validation Benchmark scorecard.
📊 Coverage, measured and self-scored: the Bug Bounty Coverage — The Full Taxonomy Audit (PDF, 124 pages) audits RedAmon against all 397 classes of web bug-bounty finding, one line at a time, naming the exact module, skill or scanner behind every verdict, and scoring the recon pipeline and the agentic system separately against their own remit. It is deliberately self-critical, it records what is missing as plainly as what is covered: 134 classes complete, 210 in the build backlog, 44 deliberately excluded, with one explicit decision for every class.
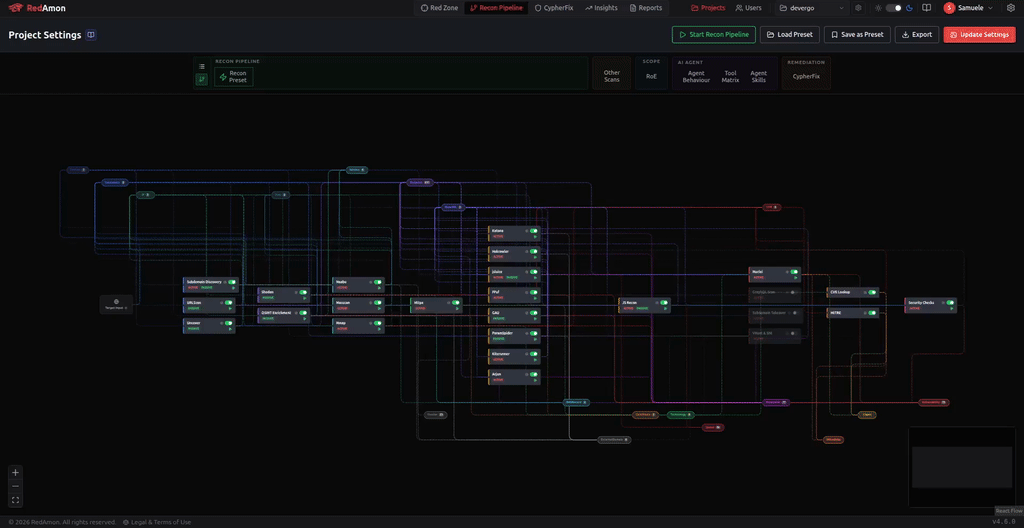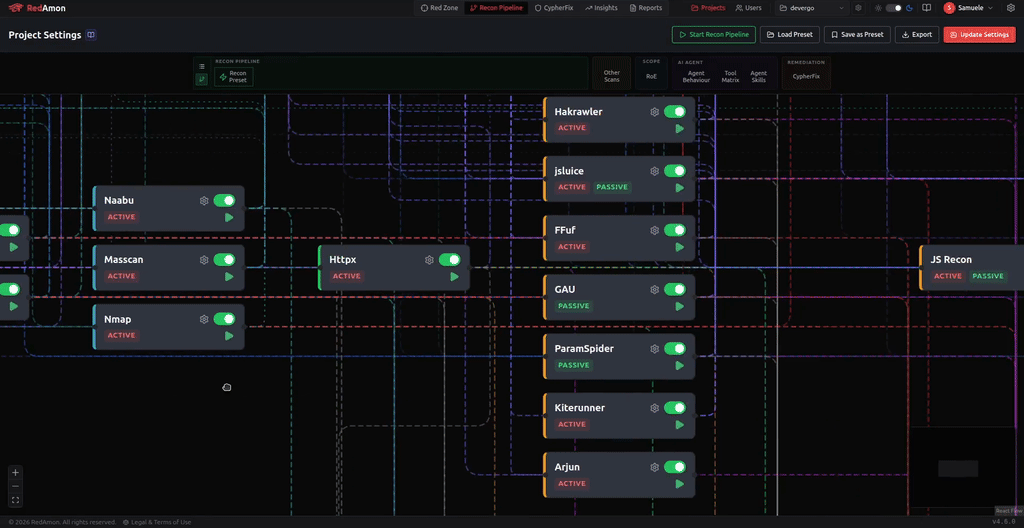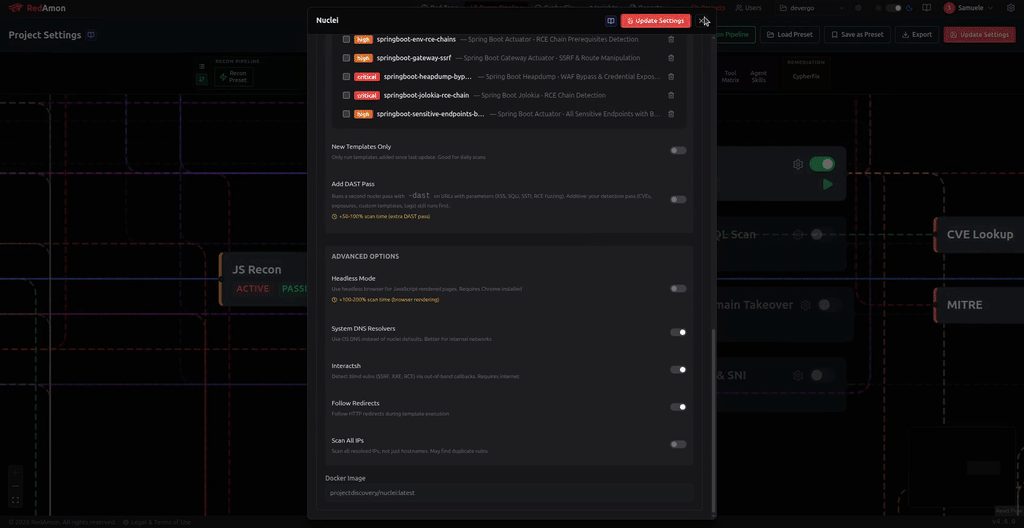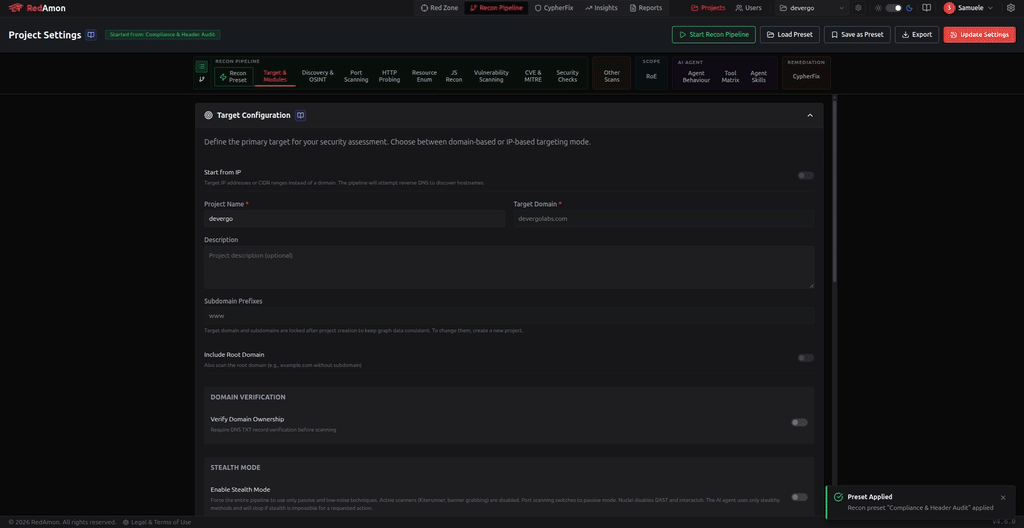
RedAmon launches multiple reconnaissance tools in parallel, each feeding results into a shared knowledge graph in real time. Tools spin up, adapt their scope based on live discoveries, and coordinate without manual intervention. The entire attack surface -- subdomains, ports, endpoints, parameters -- materializes in minutes, not hours.
