
 md-thalal/cve-2023-29489
CVE-2023-29489 è una vulnerabilità sfruttabile in cross-site scripting ( xss ) riflesso in cPanel


È stata scoperta una vulnerabilità di cross-site scripting (XSS) riflesso sfruttabile in alcune versioni di cPanel, alla quale è stato assegnato l'ID CVE-2023-29489. Questa vulnerabilità consente agli aggressori di eseguire codice JavaScript arbitrario senza richiedere autenticazione. La vulnerabilità XSS può essere sfruttata anche se le porte di gestione di cPanel non sono esposte esternamente. Anche i siti web sulle porte 80 e 443 sono suscettibili a questa vulnerabilità se gestiti tramite cPanel.
È stato riscontrato un problema in cPanel precedente alla versione 11.109.9999.116. Il Cross-Site Scripting può verificarsi nella pagina di errore di cpsrvd tramite un ID di webcall non valido.
pip install CVE-2023-29489
CVE-2023-29489 -h
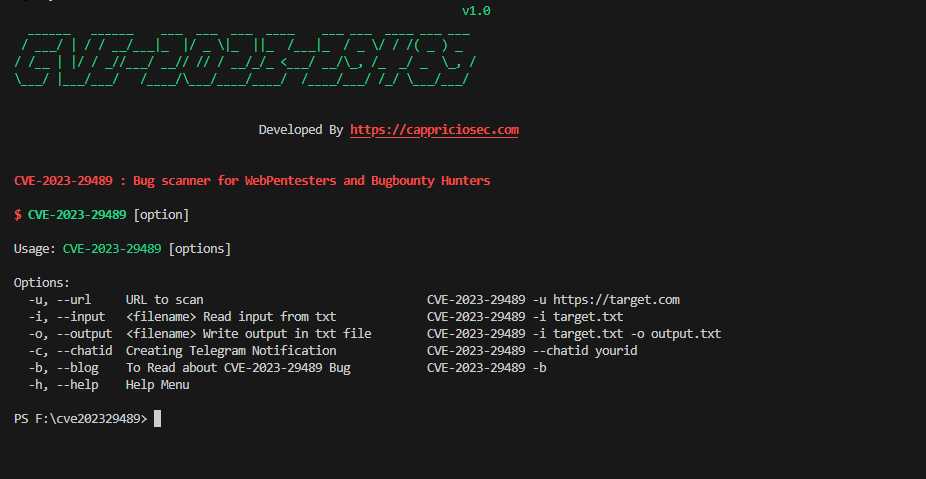
| Opzioni | Descrizione | Esempi |
|---|---|---|
| -u, --url | URL da scansionare | CVE-2023-29489 -u https://target.com |
| -i, --input | Leggi input da txt | CVE-2023-29489 -i target.txt |
| -o, --output | Scrivi output in file txt | CVE-2023-29489 -i target.txt -o output.txt |
| -c, --chatid | Crea notifica Telegram | CVE-2023-29489 --chatid yourid |
| -b, --blog | Per leggere informazioni sulla vulnerabilità CVE-2023-29489 | CVE-2023-29489 -b |
| -h, --help | Menu di aiuto |
                                                                           v1.0
   _______    ________    ___   ____ ___  ___       ___  ________________
  / ____/ |  / / ____/   |__ \ / __ \__ \|__ \     |__ \<  /__  /__  <  /
 / /    | | / / __/________/ // / / /_/ /__/ /_______/ // / /_ <  / // /
/ /___  | |/ / /__/_____/ __// /_/ / __// __/_____/ __// /___/ / / // /
\____/  |___/_____/    /____/\____/____/____/    /____/_//____/ /_//_/

                              Developed By https://cappriciosec.com


CVE-2022-21371 : Bug scanner for WebPentesters and Bugbounty Hunters

$ CVE-2022-21371 [option]

Usage: CVE-2022-21371 [options]

Options:
  -u, --url     URL to scan                                CVE-2022-21371 -u https://target.com
  -i, --input   <filename> Read input from txt             CVE-2022-21371 -i target.txt
  -o, --output  <filename> Write output in txt file        CVE-2022-21371 -i target.txt -o output.txt
  -c, --chatid  Creating Telegram Notification             CVE-2022-21371 --chatid yourid
  -b, --blog    To Read about CVE-2022-21371 Bug           CVE-2022-21371 -b
  -h, --help    Help Menu


Sito web : https://cappriciosec.com/
Email : [email protected]
