 joxeankoret/diaphora
Diaphora, the most advanced Free and Open Source program diffing tool.

Install with the Hex-Rays plugin manager:
hcli plugin install https://github.com/joxeankoret/diaphora/archive/refs/tags/3.5.0.zip
Manual install: download the code and place it into your plugins/ directory.
Diaphora (διαφορά, Greek for 'difference') version 3.5 is the most advanced program diffing tool (working as an IDA plugin) available as of today (2026). It was released in 2015 and has been actively maintained ever since: Diaphora has been ported for 11 years already to every single minor version of IDA since 6.8 to 9.5.
Diaphora supports versions of IDA >= 7.4 because the code only runs in Python 3.X (Python 3.11 was the last version being tested).
Diaphora has many of the most common program diffing (bindiffing) features you might expect, like:
However, Diaphora has also many features that are unique, not available in any other public tool. The following is a non extensive list of unique features:
You can help (or thank) the author of Diaphora by making a donation. If you feel like doing so you can use one of the following links:

Feel free to open issues in Github if you have any problem or need help. If you prefer to chat interactively, you can use the following Discord channel: https://discord.gg/atg34w2xjV
If your company does not allow using the AGPL license you can get commercial licenses of Diaphora to use it in your company or to use it as a particular in any company you work (similar concept as IDA's named licenses). For more details, please contact me at [email protected].
Please remember that it isn't me preventing you from using Diaphora: it's your company. Thank you for your understanding.
If you are looking how to automate the export or diffing process, or you want to speed operations, etc... You might want to take a look to the wiki where such questions are answered.
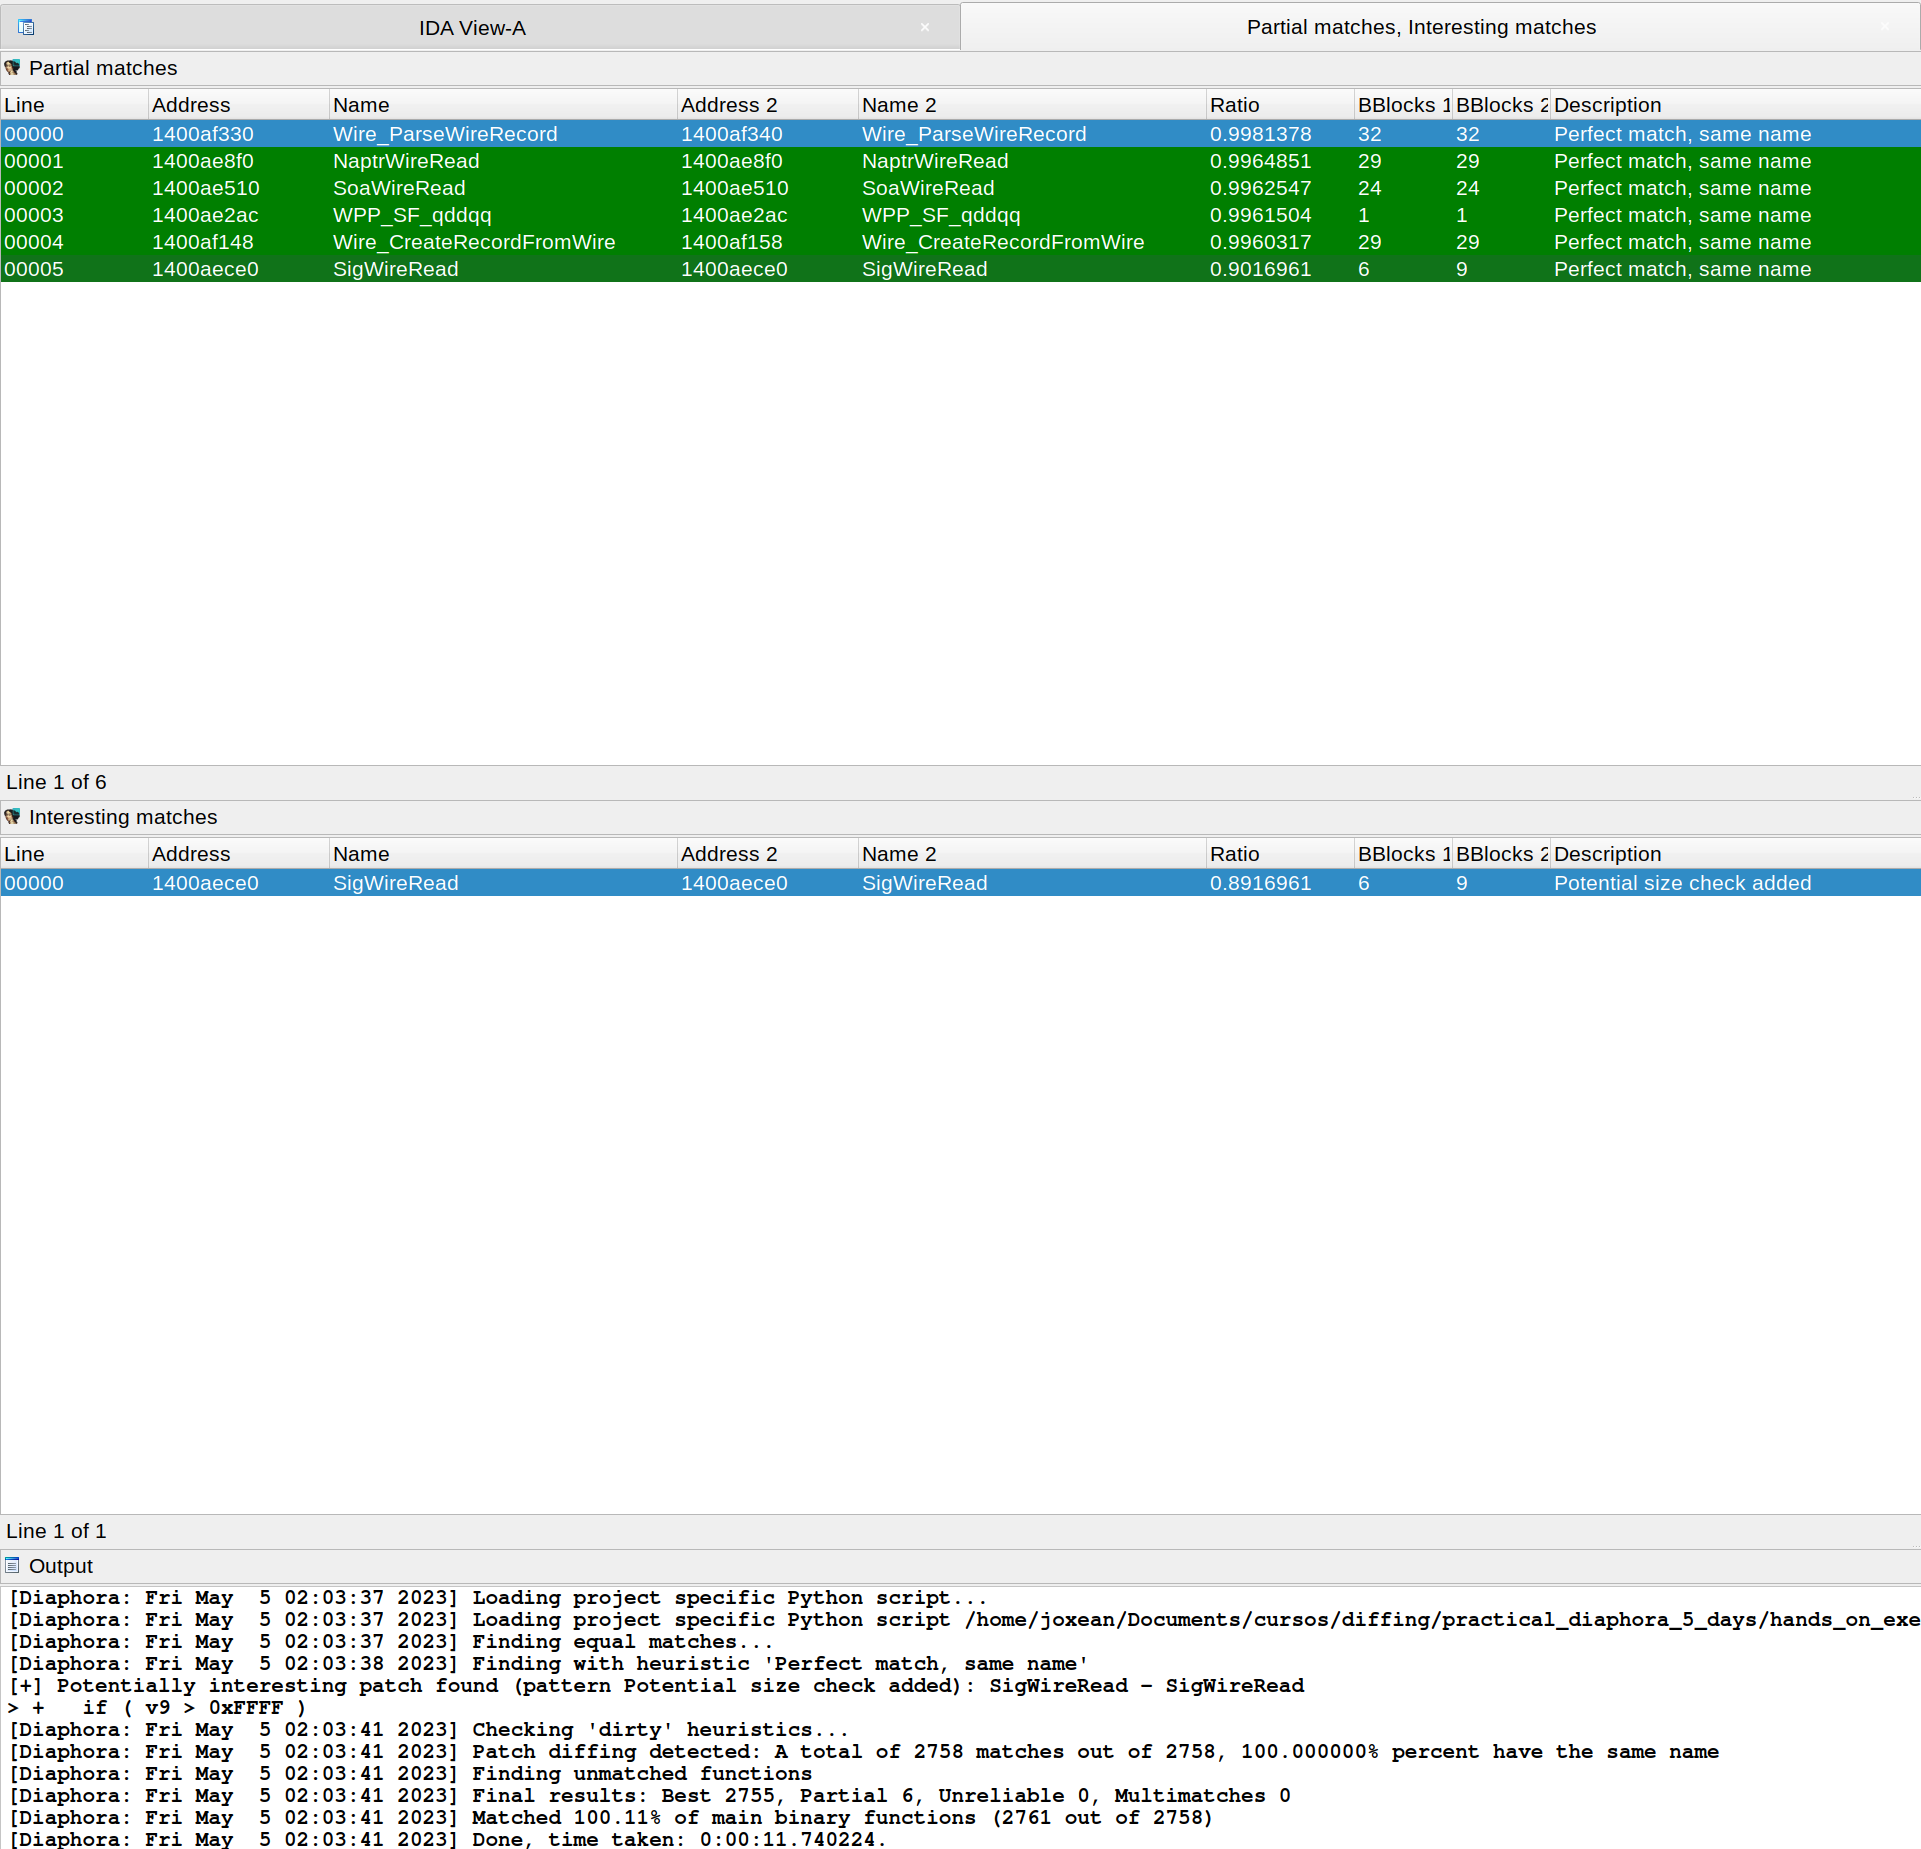
Diaphora finding the exact function where a vulnerability was patched in CVE-2020-1350:
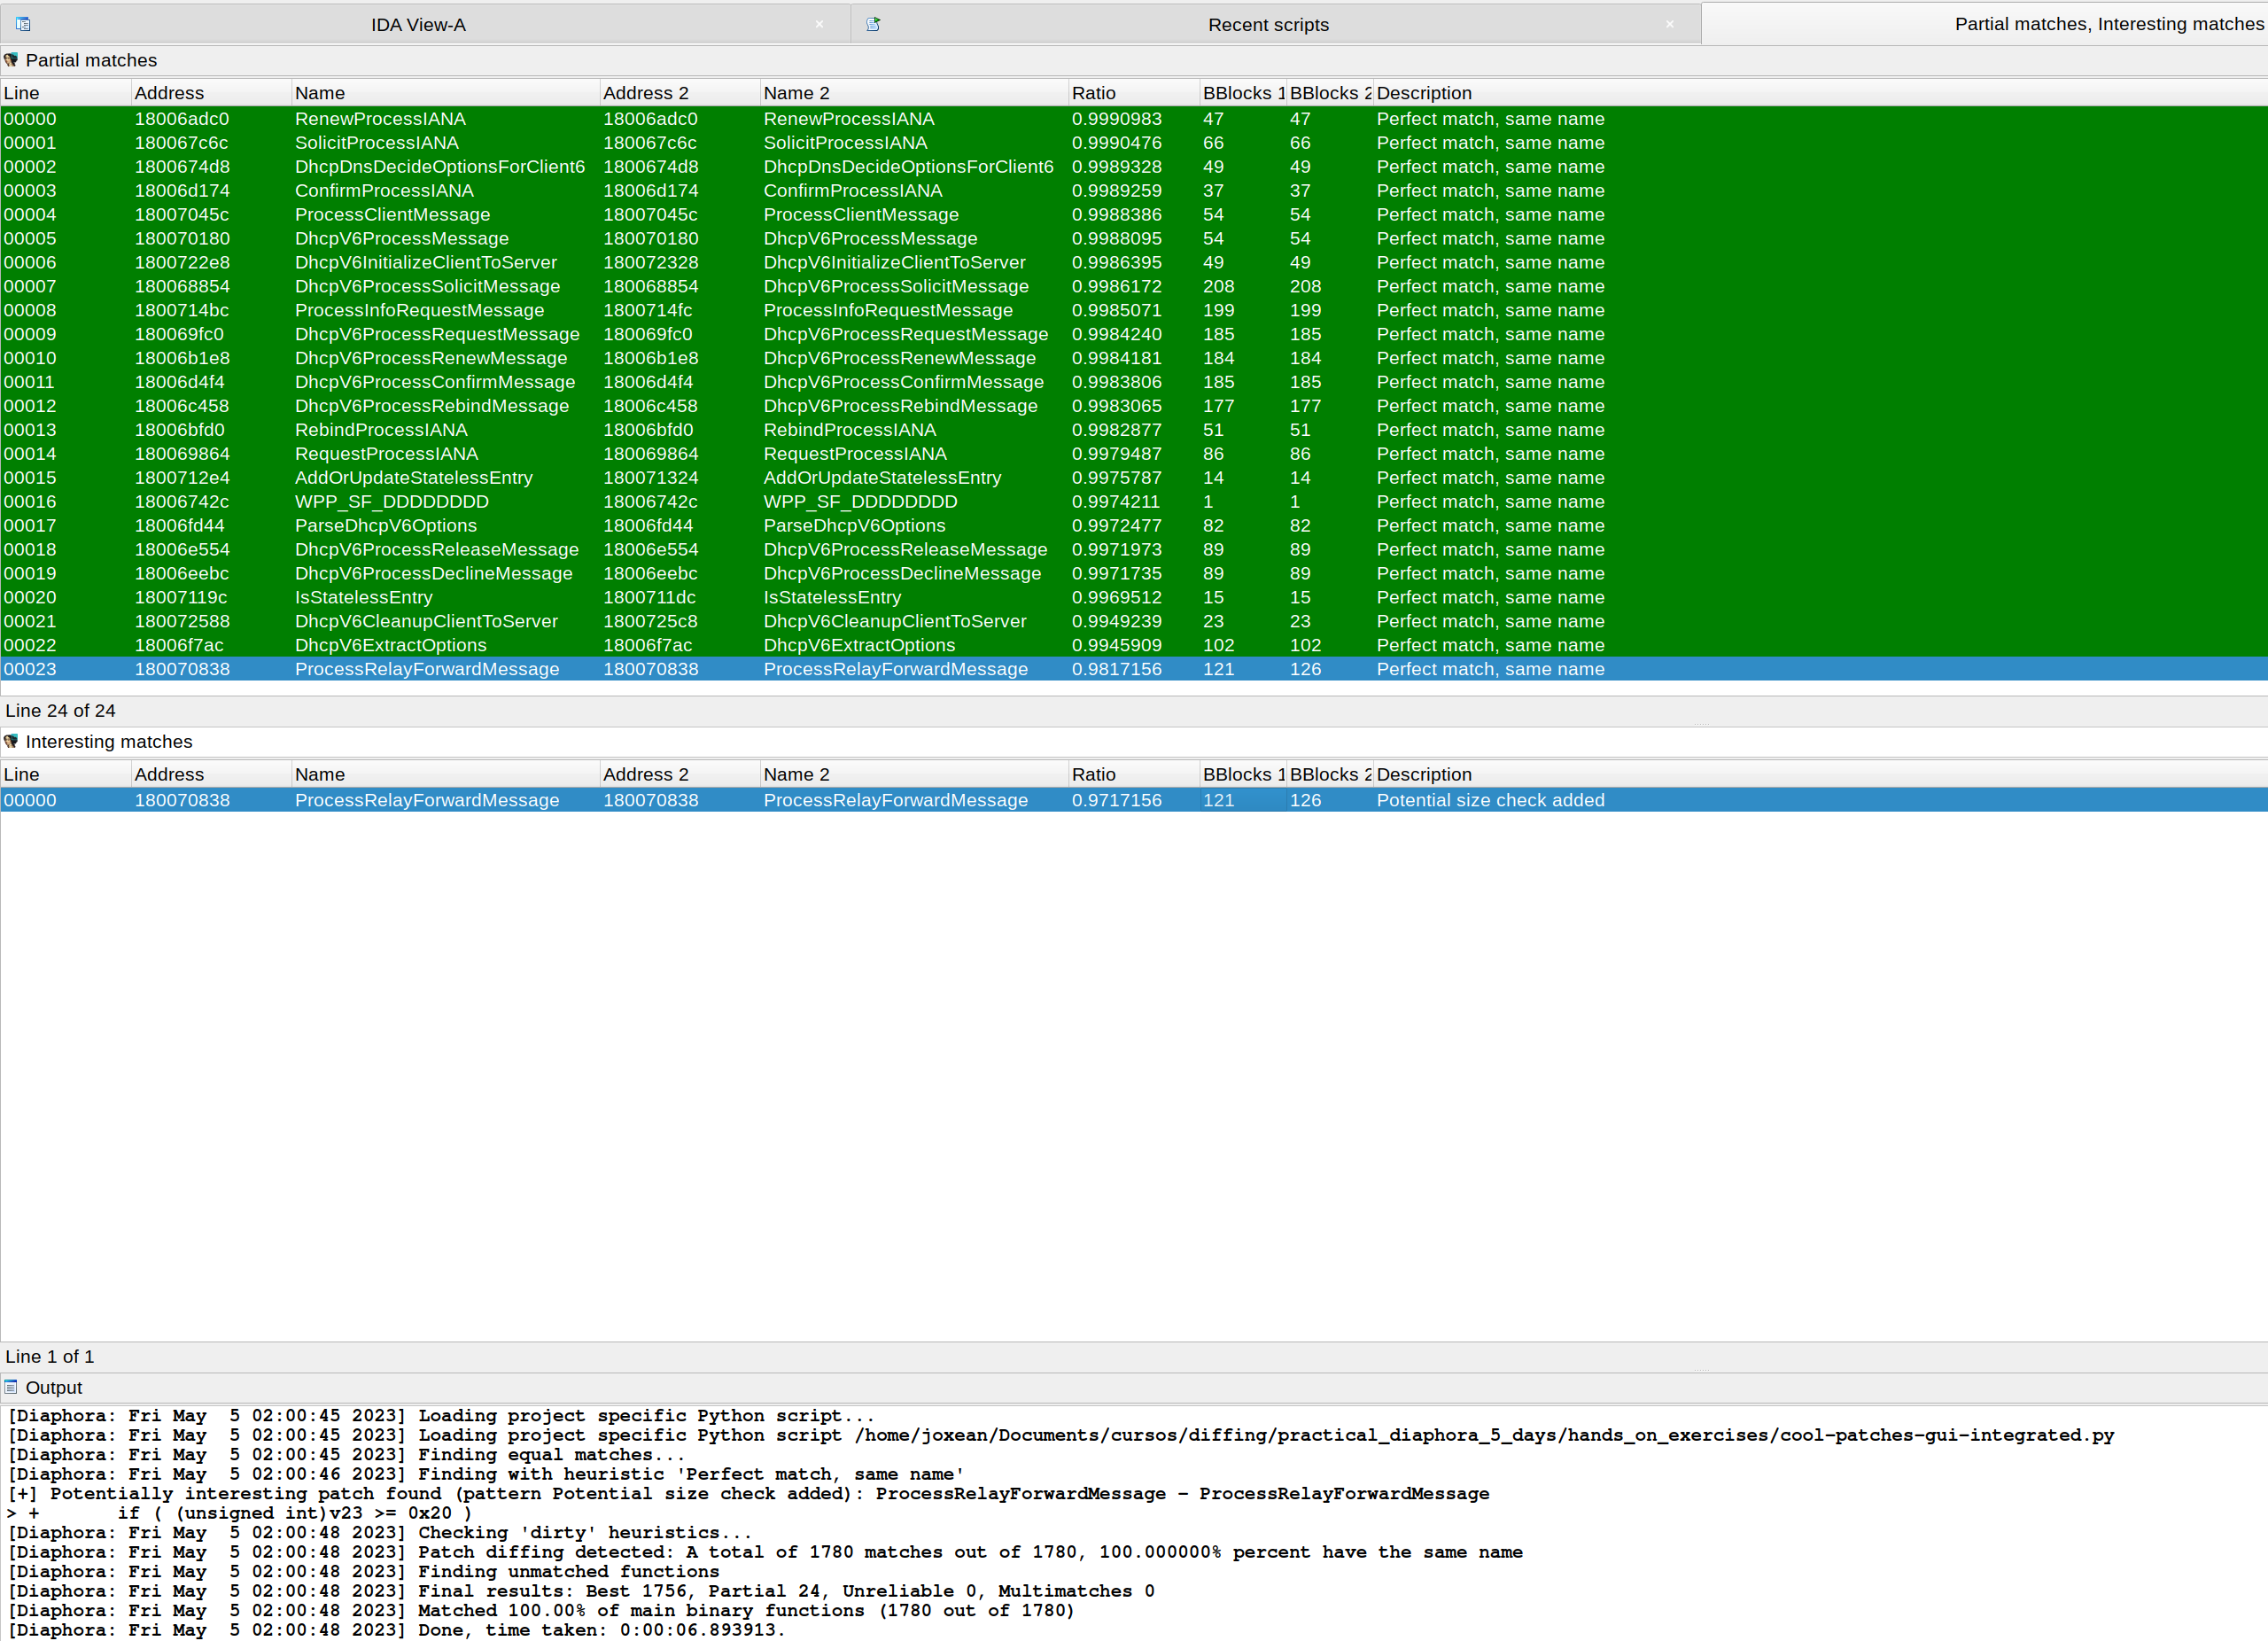
Diaphora, again, finding the exact function where CVE-2023-28231 was fixed:
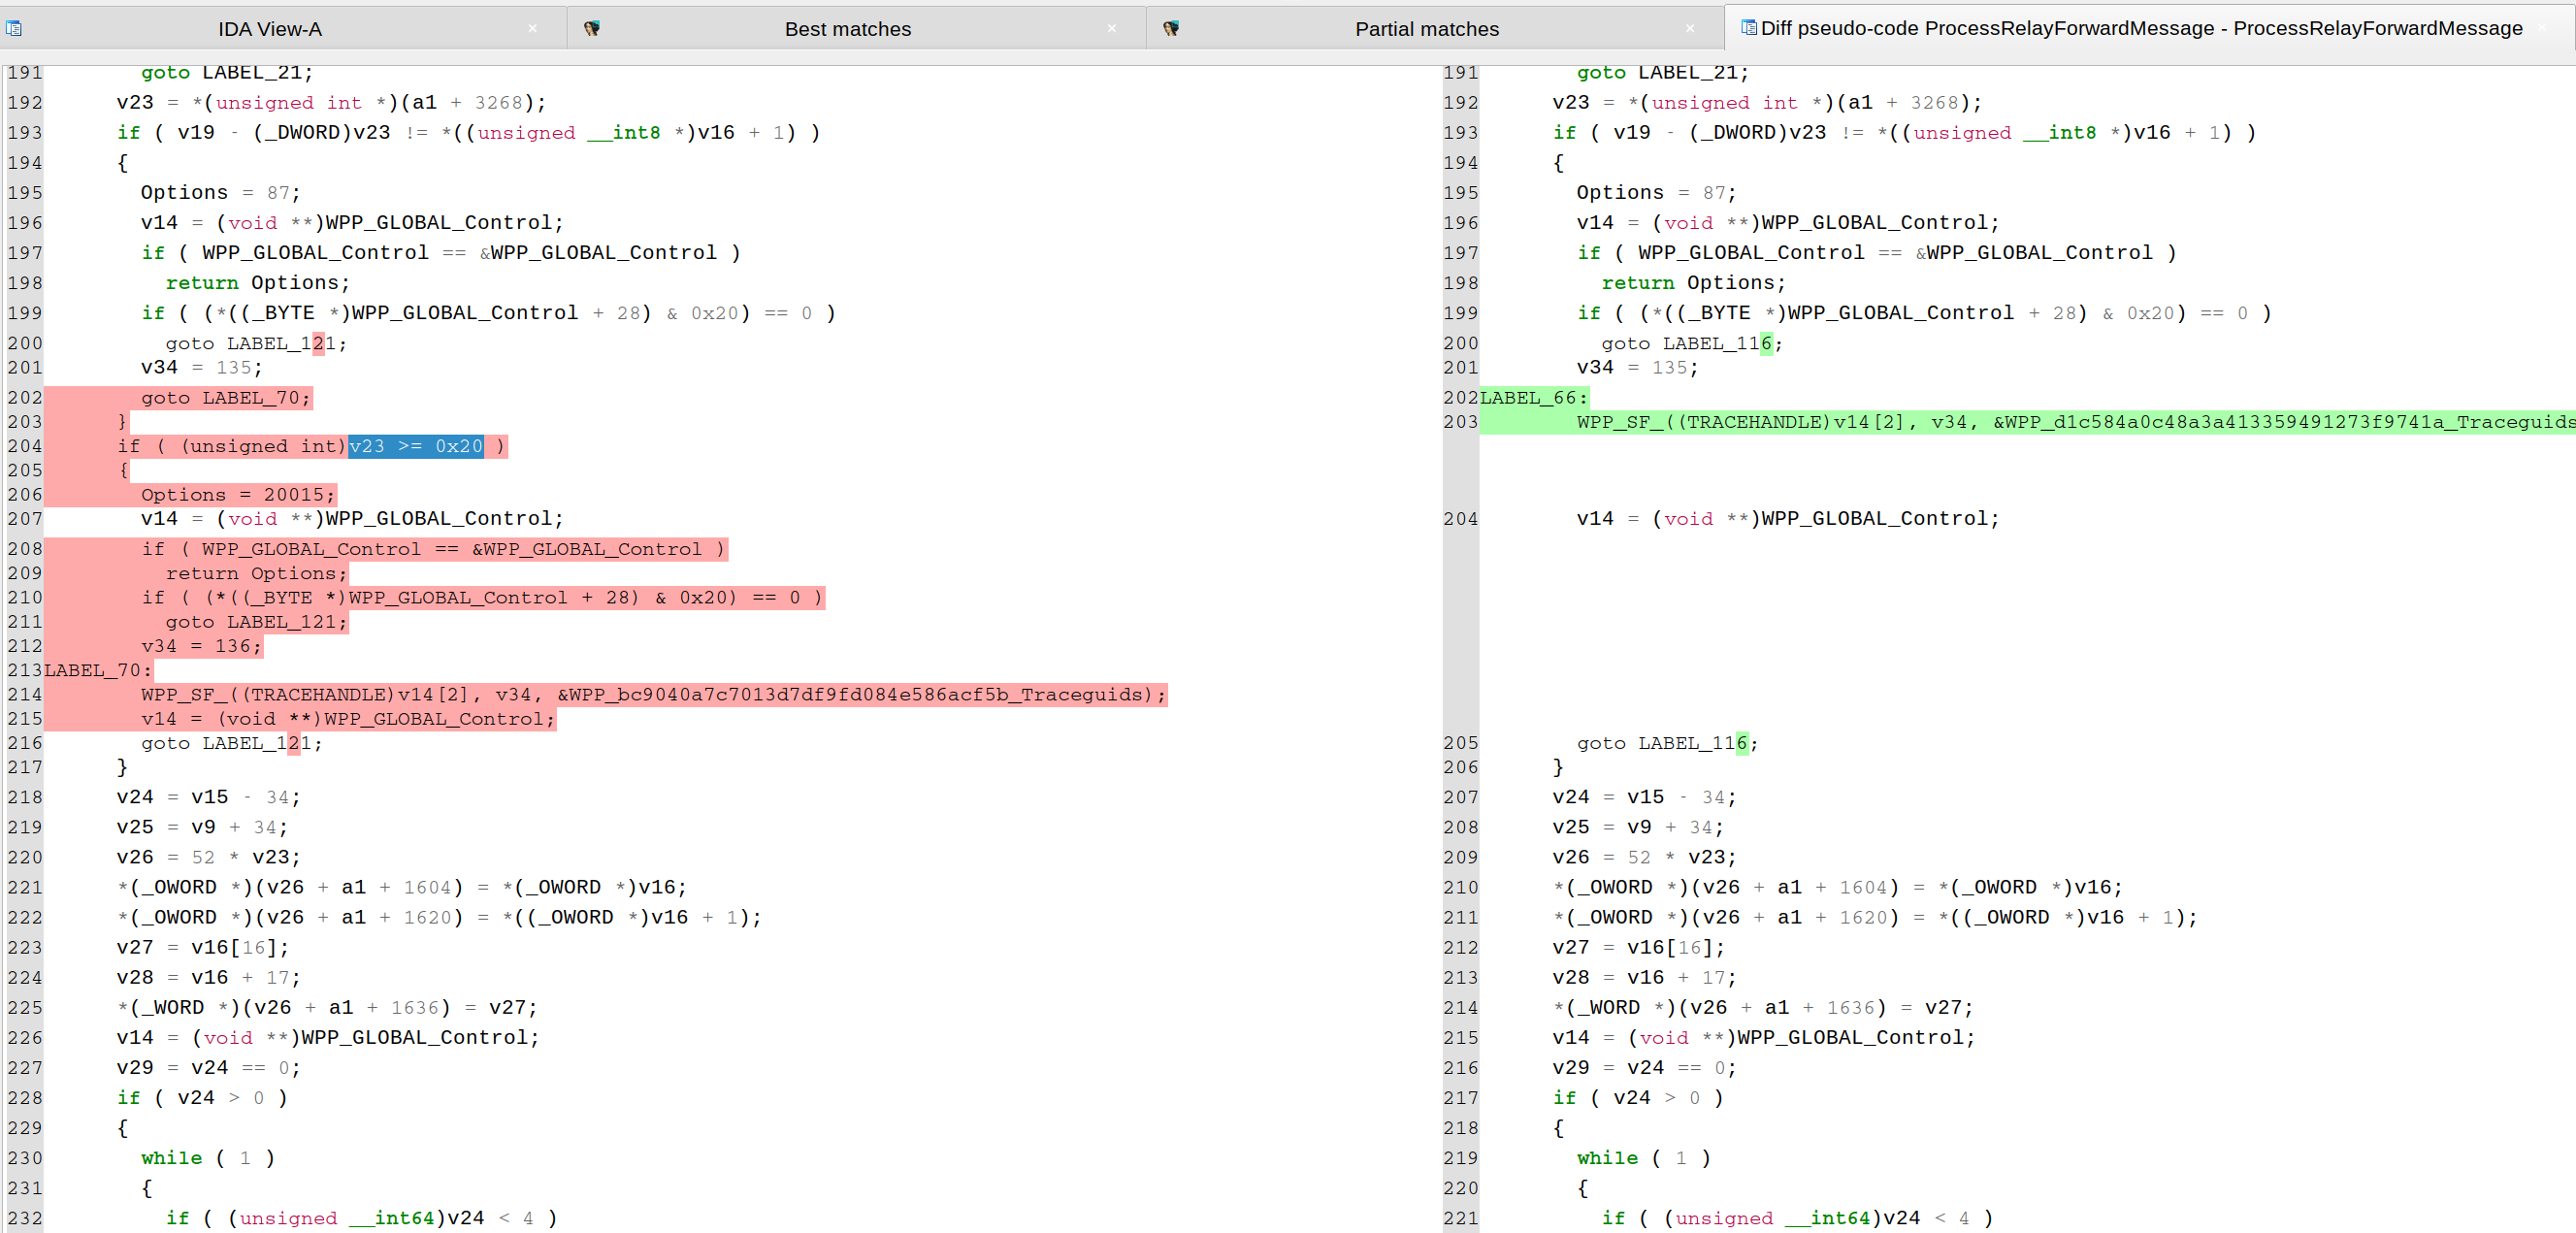
CVE-2023-28231. As explained in a blog from ZDI, the vulnerability was fixed by checking that the number of relay forward messages in "ProcessRelayForwardMessage()" is not bigger or equal than 32 (0x20), as shown in the following pseudo-code diffing:
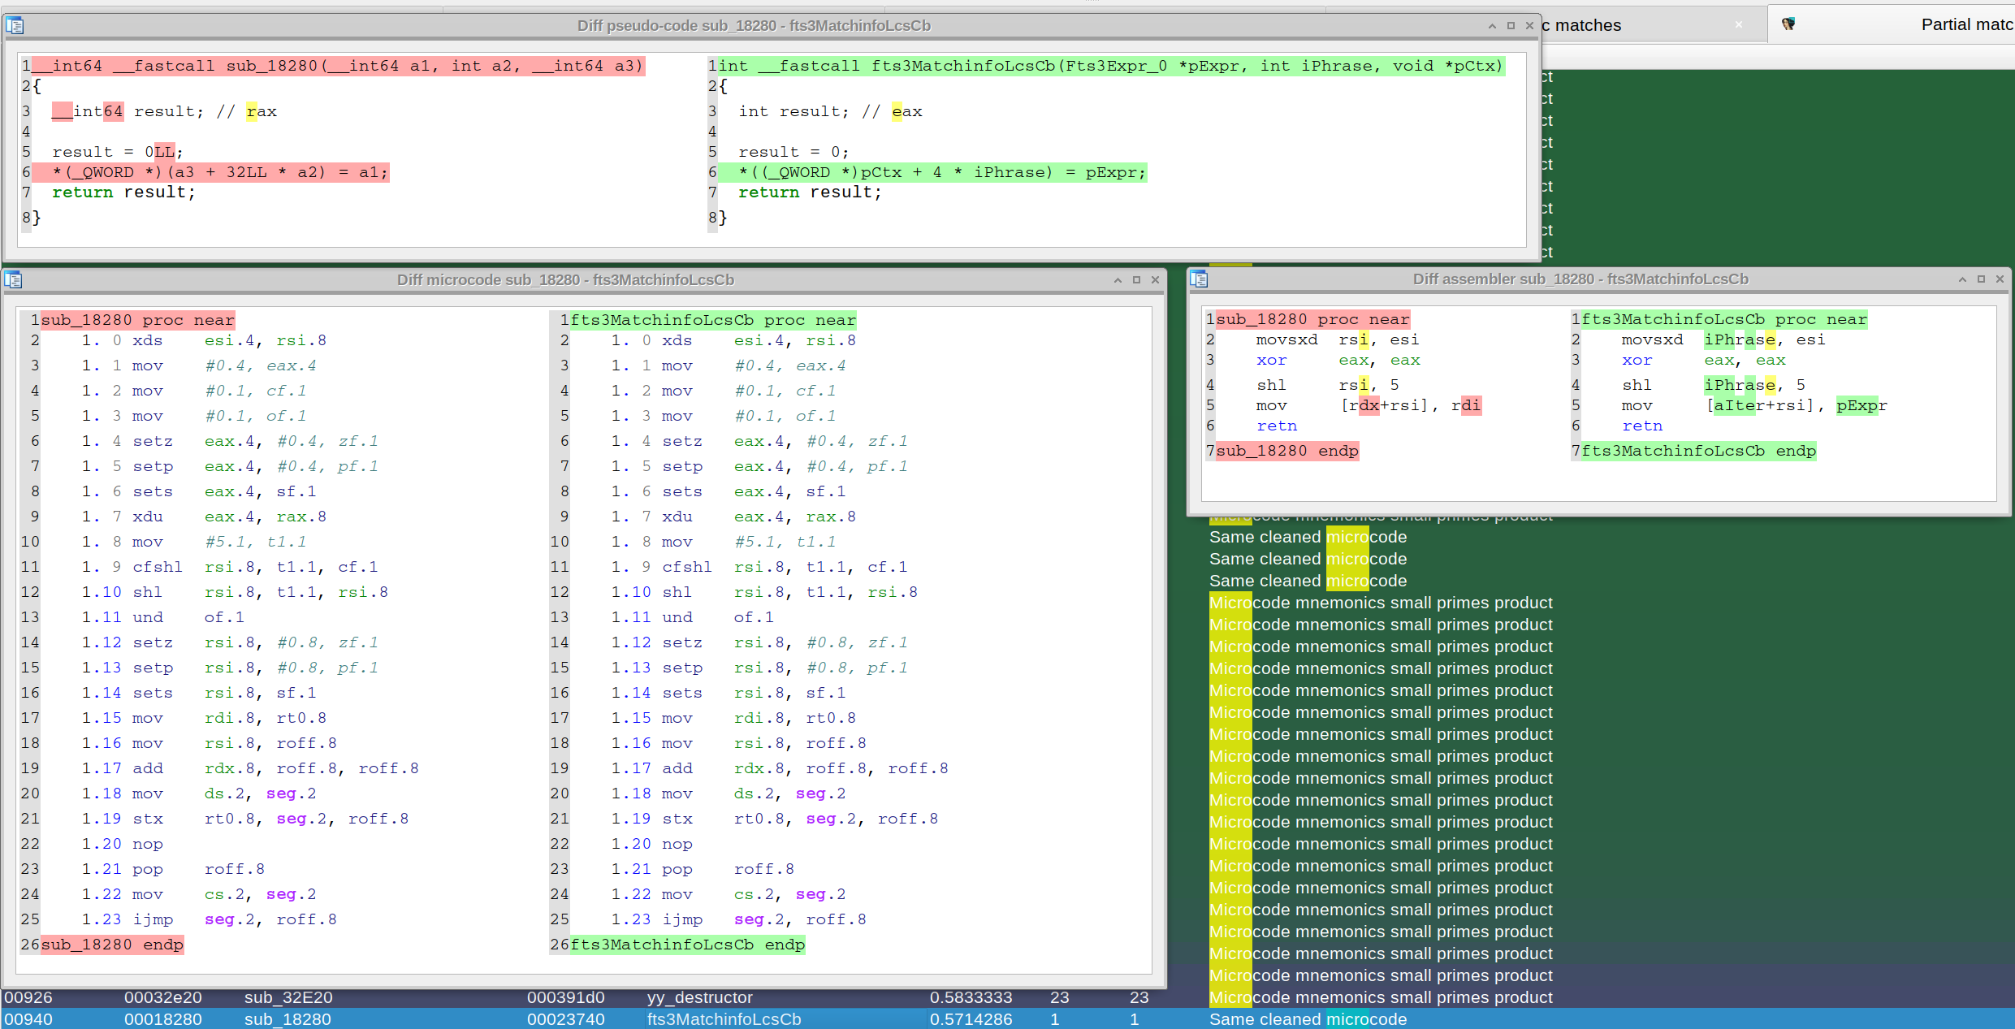
Diaphora doing Hex-Ray's microcode diffing:
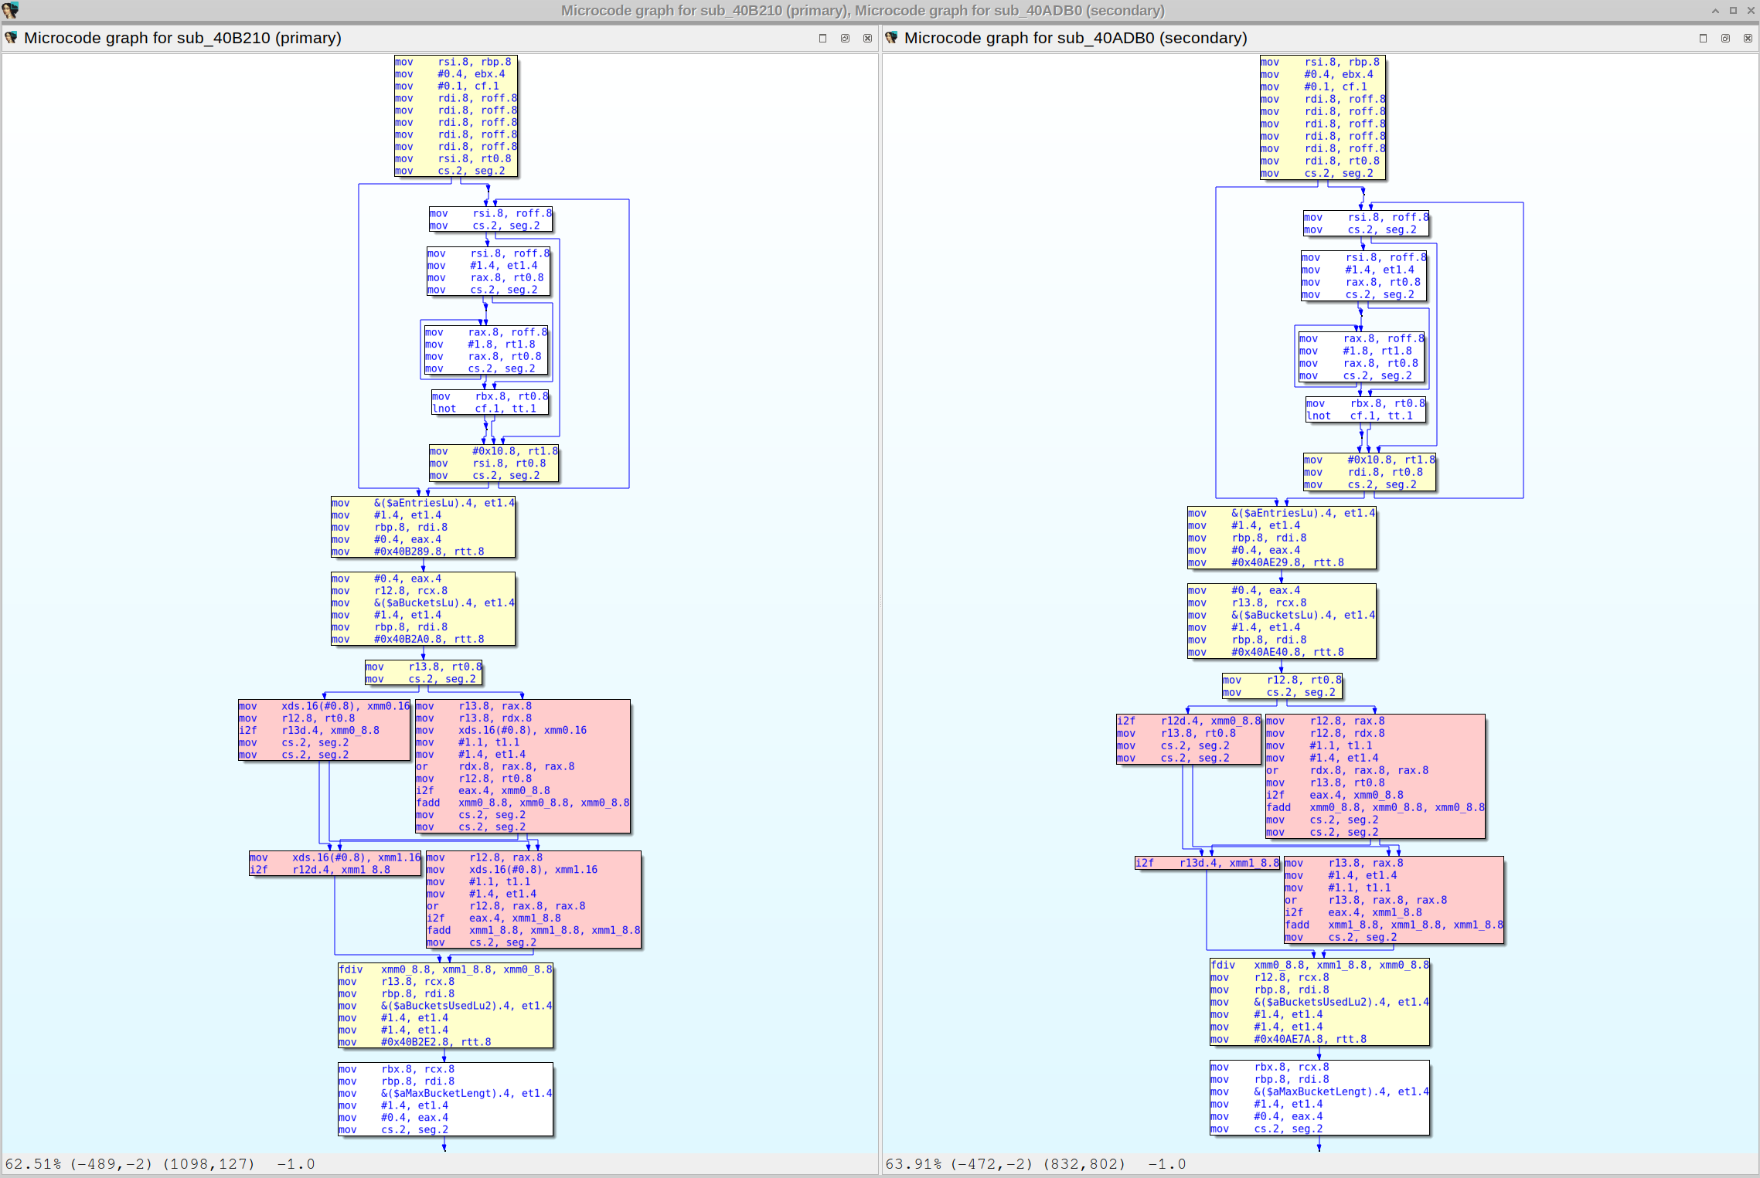
Diffing assembly, pseudo-code and microcode:

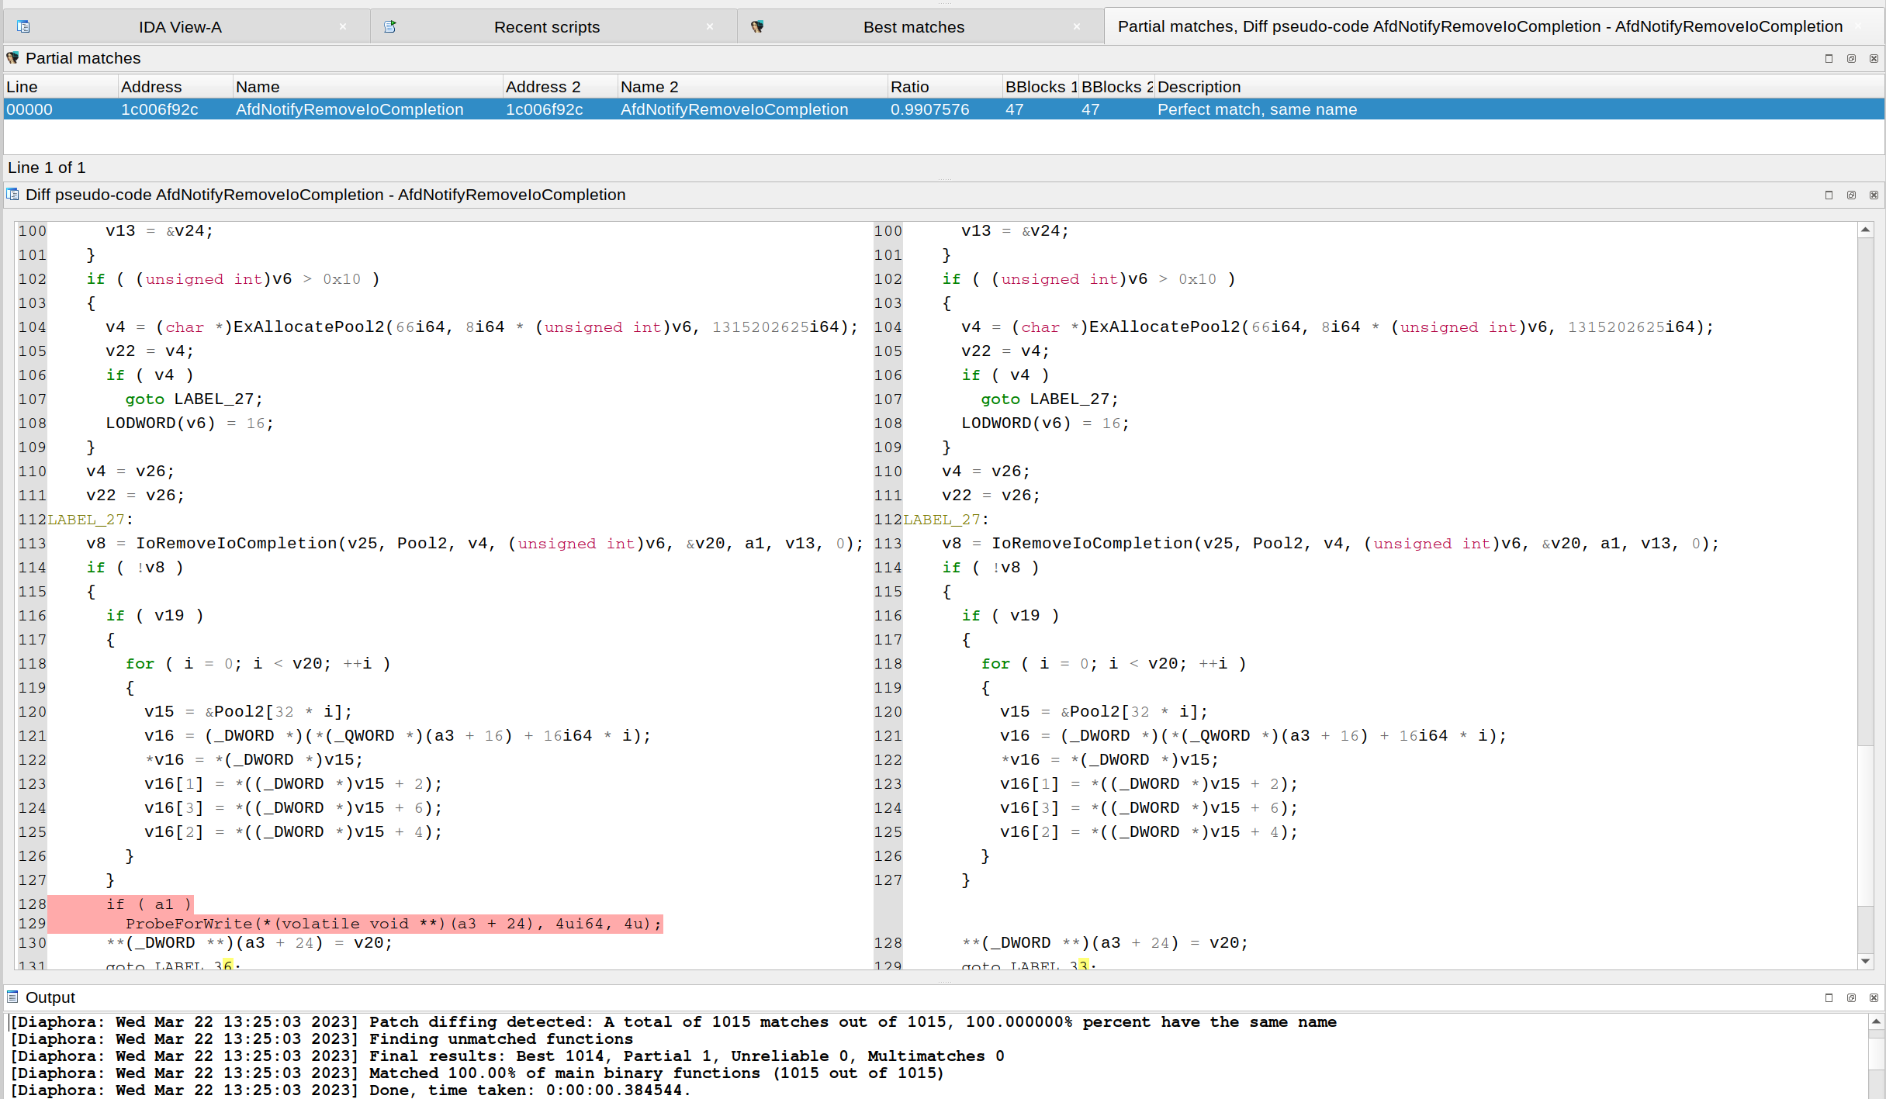
Diffing CVE-2023-21768 with Diaphora 3.0:
This is a screenshot of Diaphora diffing the PEGASUS iOS kernel Vulnerability fixed in iOS 9.3.5:

And this is an old screenshot of Diaphora diffing the Microsoft bulletin MS15-034:
Diaphora diffing MS15-034
These are some screenshots of Diaphora diffing the Microsoft bulletin MS15-050, extracted from the blog post Analyzing MS15-050 With Diaphora from Alex Ionescu.
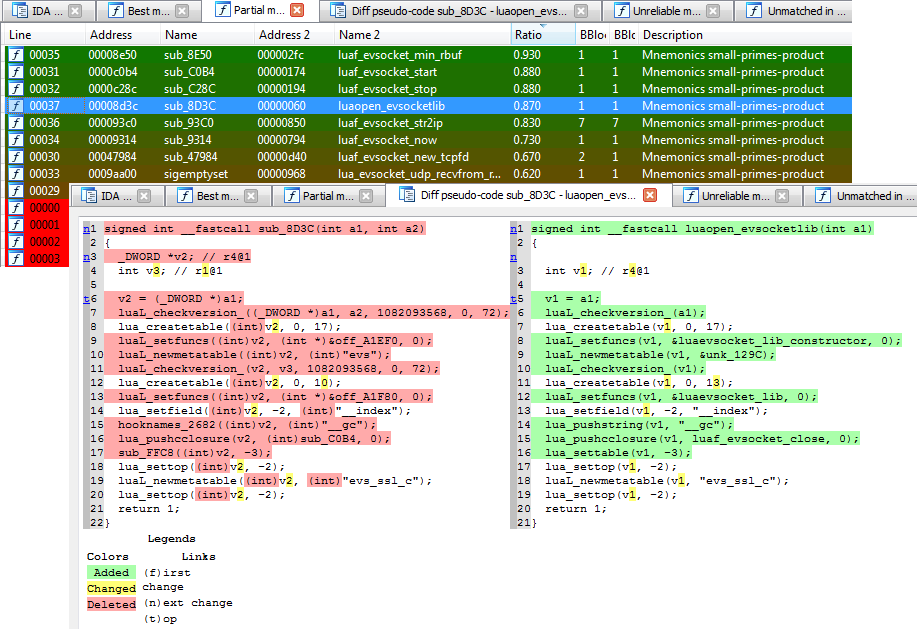
Here is a screenshot of Diaphora diffing iBoot from iOS 10.3.3 against iOS 11.0: