 bishopfox/bfinject
Dylib injection per iOS 11.0 - 11.1.2 con i jailbreak LiberiOS ed Electra

Iniezione semplice di dylib per iOS 64-bit jailbroken 11.0 - 11.1.2. Compatibile con i jailbreak Electra e LiberiOS.
bfinject carica dylib arbitrari in app App Store in esecuzione. Include il supporto integrato per la decrittazione delle app App Store e include iSpy e Cycript.
bfinject è un wrapper che si occupa di firmare correttamente i tuoi dylib prima di iniettarli usando bfinject4realz. È completamente autonomo, non richiede jailbreakd, QiLin o niente del genere. Funziona e basta.
Nota: bfinject non funziona su Electra se "Tweaks" è abilitato. Riavvia e riesegui Electra senza tweaks per usare bfinject. Se vedi errori con "thread_create", questo è il problema.
Nota: bfdecrypt è disponibile come dylib autonomo qui: https://github.com/BishopFox/bfdecrypt/
wget di Electra non supporta SSL.ssh root@your-device-ip # (the password is 'alpine')
mkdir bfinject
cd bfinject
wget http://<your_server>/bfinject.tar
tar xvf bfinject.tar
wget di LiberiOS non supporta SSL.ssh root@your-device-ip # (the password is 'alpine')
export PATH=$PATH:/jb/usr/bin:/jb/bin:/jb/sbin:/jb/usr/sbin:/jb/usr/local/bin:
cd /jb
mkdir bfinject
cd bfinject
wget http://<your_server>/bfinject.tar
tar xvf bfinject.tar
bash bfinject per l'aiutobash o non funzionerà. Sandbox, eccetera eccetera.-bash-3.2# bash bfinject
Syntax: bfinject [-p PID | -P appname] [-l /path/to/yourdylib | -L feature]
For example:
bfinject -P Reddit.app -l /path/to/evil.dylib # Injects evil.dylib into the Reddit app
or
bfinject -p 1234 -L cycript # Inject Cycript into PID
or
bfinject -p 4566 -l /path/to/evil.dylib # Injects the .dylib of your choice into PID
Instead of specifying the PID with -p, bfinject can search for the correct PID based on the app name.
Just enter "-P identifier" where "identifier" is a string unique to your app, e.g. "fing.app".
Available features:
cycript - Inject and run Cycript
decrypt - Create a decrypted copy of the target app
test - Inject a simple .dylib to make an entry in the console log
ispy - Inject iSpy. Browse to http://<DEVICE_IP>:31337/
Prima di fare qualsiasi cosa più complessa, verifica che funzioni. bfinject ha test automatici integrati. Ecco un esempio usando l'app Reddit come destinazione:
Cs-iPhone:~ root# bash bfinject -P Reddit -L test
[+] Electra detected.
[+] Injecting into '/var/containers/Bundle/Application/55C94FAA-A282-4FDC-967D-6A012D01087E/Reddit.app/Reddit'
[+] Getting Team ID from target application...
[+] Thinning dylib into non-fat arm64 image
[+] Signing injectable .dylib with Team ID 2TDUX39LX8 and platform entitlements...
[bfinject4realz] Calling task_for_pid() for PID 486.
[bfinject4realz] Calling thread_create() on PID 486
[bfinject4realz] Looking for ROP gadget... found at 0x1019a2ba0
[bfinject4realz] Fake stack frame at 0x12ac5c000
[bfinject4realz] Calling _pthread_set_self() at 0x182bfb814...
[bfinject4realz] Returned from '_pthread_set_self'
[bfinject4realz] Calling dlopen() at 0x1829bb460...
[bfinject4realz] Returned from 'dlopen'
[bfinject4realz] Success! Library was loaded at 0x1c016e1c0
[+] So long and thanks for all the fish.
Sullo schermo del dispositivo dovresti vedere questo:
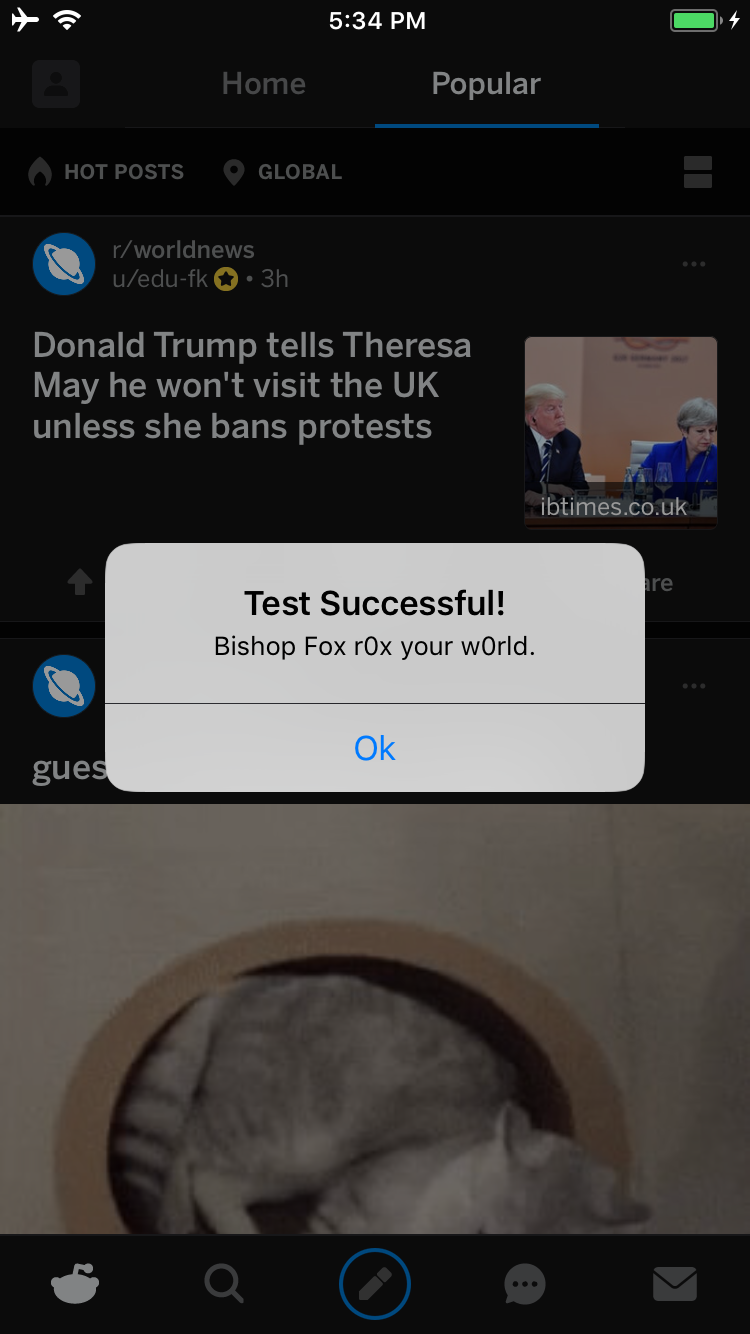
In caso contrario, qualcosa è rotto ;)
Ecco un esempio di decrittazione dell'app Reddit su un iPhone con jailbreak Electra:
Cs-iPhone:~ root# bash bfinject -P Reddit -L decrypt
[+] Electra detected.
[+] Injecting into '/var/containers/Bundle/Application/BCEBDD64-6738-45CE-9B3C-C6F933EA0793/Reddit.app/Reddit'
[+] Getting Team ID from target application...
[+] Thinning dylib into non-fat arm64 image
[+] Signing injectable .dylib with Team ID 2TDUX39LX8 and platform entitlements...
[bfinject4realz] Calling task_for_pid() for PID 3218.
[bfinject4realz] Calling thread_create() on PID 3218
[bfinject4realz] Looking for ROP gadget... found at 0x1016a5110
[bfinject4realz] Fake stack frame at 0x10a06c000
[bfinject4realz] Calling _pthread_set_self() at 0x181303814...
[bfinject4realz] Returned from '_pthread_set_self'
[bfinject4realz] Calling dlopen() at 0x1810c3460...
[bfinject4realz] Returned from 'dlopen'
[bfinject4realz] Success! Library was loaded at 0x1c03e1100
[+] So long and thanks for all the fish.
Vedrai questa schermata sul tuo dispositivo:
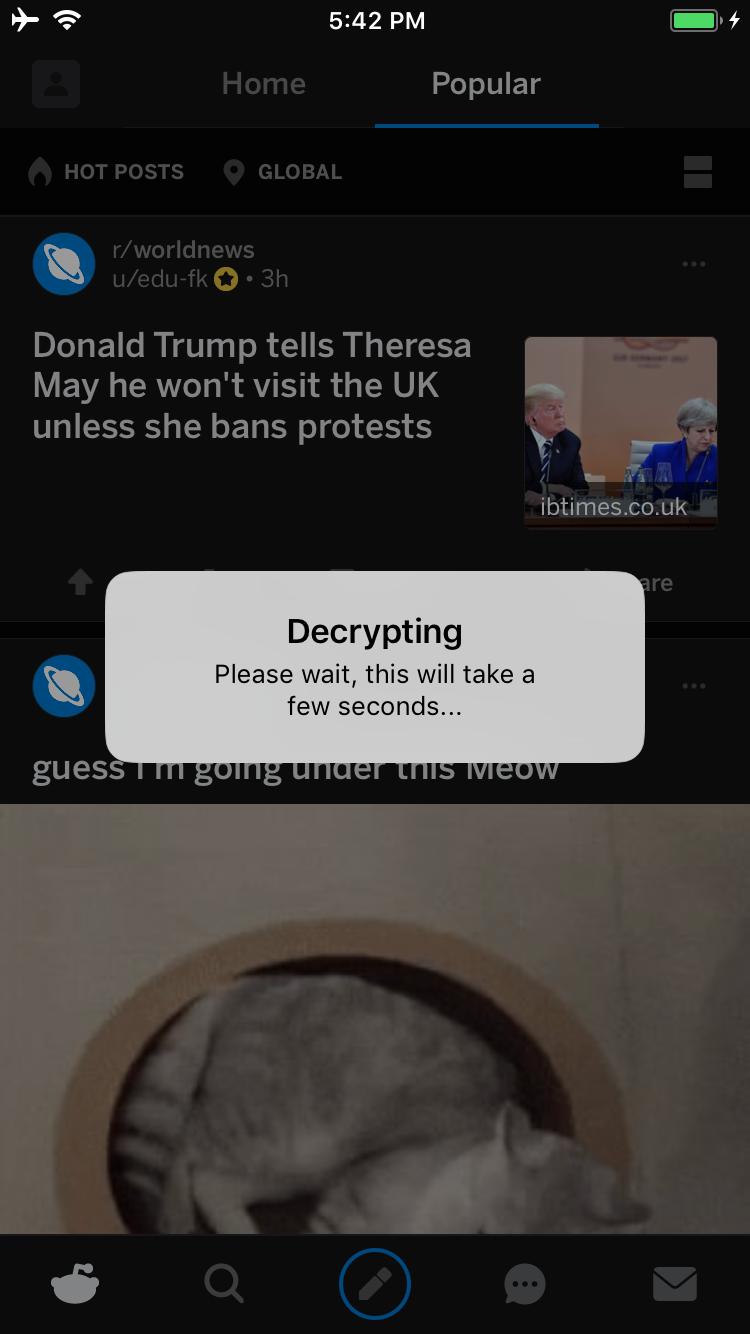
Una volta completato, ti verrà mostrato un avviso UI che ti chiederà se vuoi avviare un servizio dal quale scaricare l'IPA decrittato:
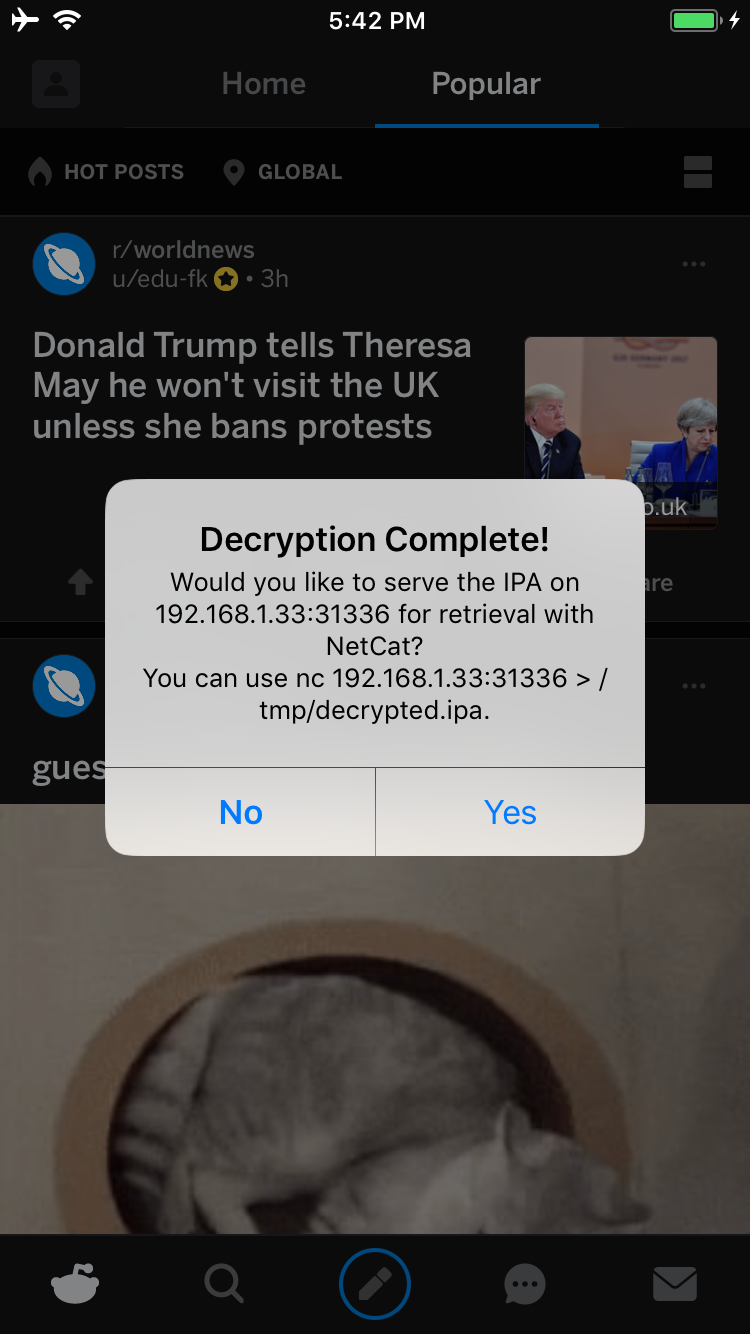
Se tocchi Yes, verrà avviato un servizio sulla porta 31336 del tuo dispositivo. Collegati ad esso e riceverai una copia grezza dell'IPA, che può essere scaricata con netcat in questo modo:
carl@calisto-3 /tmp $ nc 192.168.1.33 31336 > decrypted.ipa
carl@calisto-3 /tmp $ ls -l decrypted.ipa
-rw-r--r--  1 carl  wheel  14649063 Jan 25 16:57 decrypted.ipa
carl@calisto-3 /tmp $ file decrypted.ipa
decrypted.ipa: iOS App Zip archive data, at least v2.0 to extract
In alternativa, controlla il registro di console del dispositivo: ti dirà dove è archiviato l'IPA decrittato. Per esempio:
[dumpdecrypted] Wrote /var/mobile/Containers/Data/Application/6E6A5887-8B58-4FC5-A2F3-7870EDB5E8D1/Documents/decrypted-app.ipa
Puoi anche cercare l'IPA nel filesystem in questo modo:
find /var/mobile/Containers/Data/Application/ -name decrypted-app.ipa
Per estrarre il file .ipa dal dispositivo puoi usare netcat. Sul tuo laptop, imposta un servizio in ascolto:
ncat -l 0.0.0.0 12345 > decrypted.ipa
E sul dispositivo con jailbreak:
cat /path/to/decrypted.ipa > /dev/tcp/<IP_OF_YOUR_COMPUTER>/12345
