Skip to content
KitploitKITPLOIT
StrumentiBlog
Log in
Invia
StrumentiBlog
Invia

Strumenti di Hacking, PenTest e Cybersecurity per il tuo Arsenale di Sicurezza!

Kitploit è una directory di strumenti di hacking, cybersecurity e pentesting. Scopri gli ultimi aggiornamenti dei progetti per trovare vulnerabilità, analizzare sistemi, automatizzare i test e rafforzare la tua sicurezza.

··Feed·Contatto·Privacy·© 2026 Kitploit

Directory degli strumenti

Categorie

Vedi tutte le categorie
Loading categories
Bug-Bounty — Bug Bounty ~ Awesome | Libri | Cheatsheet | Checklist | Strumenti | Wordlist | Altro | Kitploit
Strumenti/GitHubGitHub/anlominus/bug-bounty
RicognizioneAnalisi delle VulnerabilitàSicurezza WebCTFPenetration TestingApprendimento e FormazioneRisorse CurateLab e Pratica
GitHubanlominus/bug-bounty

Bug-Bounty

Bug Bounty ~ Awesome | Libri | Cheatsheet | Checklist | Strumenti | Wordlist | Altro

Vedi Repository
6511082411 mesi faRevisionato da Kitploit

Più Popolari

Vedi tutti →

Scopri gli strumenti più utilizzati dalla nostra community.

Esplora tutti gli strumenti

Sfoglia la nostra collezione di strumenti

Vedi tutti gli strumenti →
Condividi

בס״ד

⚜️ Aภl๏miuภuຮ ⚜️

⫷ HacKingPro ⫸
⫷ TryHackMe | KoTH ⫸
⫷ Privilege-Escalation⫸
⫷ ScanPro | Linfo | Diablo ⫸
⫷ Offensive-Security | PenTest ⫸
⫷ Goals | Studies | HacKing | AnyTeam ⫸
image


Bug Bounty

  • Awesomes
  • Books
  • Cheatsheets
  • Checklists
  • Tools
  • Wordlists
  • More

GitHub Bounty

GitHub Security Bug Bounty

I ricercatori di sicurezza informatica collaborano sempre più spesso con le aziende Internet per scovare vulnerabilità.

Il nostro programma di bounty rende omaggio a questi ricercatori e offre ricompense di $30.000 o più per vulnerabilità critiche.

Awesomes

  • Awesome Bug Bounty Tools

    Una lista curata di vari strumenti per bug bounty

    https://github.com/vavkamil/awesome-bugbounty-tools

  • Awesome Bug Bounty

    Una lista curata e completa di programmi di Bug Bounty e write-up dei cacciatori di bug bounty.

  • Awesome CTF

    Una lista curata di framework, librerie, risorse, software e tutorial per Capture The Flag (CTF). Questa lista mira ad aiutare sia i principianti sia i giocatori di CTF esperti a trovare tutto ciò che riguarda i CTF in un unico posto.

  • Awesome Bug Bounty Builder

    Progetto Awesome Bug bounty builder - TUTTI gli strumenti comuni per trovare le tue vulnerabilità.

    image


Books

  • Hacking-Books Ecco alcuni PDF popolari sull'hacking

  • The Threat Hunter Playbook ~ The Threat Hunter Playbook

  • image

    The Threat Hunter Playbook è un progetto open source guidato dalla community per condividere logiche di rilevamento, tecniche degli avversari e risorse per rendere più efficiente lo sviluppo dei rilevamenti. Tutti i documenti di rilevamento di questo progetto seguono la struttura di MITRE ATT&CK, che classifica il comportamento degli avversari post-compromissione in gruppi tattici, e sono disponibili sotto forma di notebook interattivi. L'uso dei notebook non solo ci consente di condividere testo, query e output attesi, ma anche codice per aiutare altri a eseguire logiche di rilevamento su dataset di sicurezza pre-registrati, localmente o da remoto tramite gli ambienti di cloud computing BinderHub.


Cheatsheets

  • Bug Bounty Cheat Sheet

    Una lista di payload interessanti, suggerimenti e trucchi per i cacciatori di bug bounty.

  • Bug Bounty Cheat Sheet

    Una lista di payload interessanti, suggerimenti e trucchi per i cacciatori di bug bounty.


Cheacklists

  • Galaxy-Bugbounty-Checklist

    Suggerimenti e tutorial per il Bug Bounty e anche per i test di penetrazione.


Tools

  • Bug Bounty Methodology & Tools

Ecco alcuni degli strumenti che usiamo quando eseguiamo SOLO Live Recon Passive su Twitch:

  1. Recon-ng https://github.com/lanmaster53/recon-ng
  2. httpx https://github.com/projectdiscovery/httpx
  3. isup.sh https://github.com/gitnepal/isup
  4. Arjun https://github.com/s0md3v/Arjun
  5. jSQL https://github.com/ron190/jsql-injection
  6. Smuggler https://github.com/defparam/smuggler
  7. Sn1per https://github.com/1N3/Sn1per
  8. Spiderfoot https://github.com/smicallef/spiderfoot
  9. Nuclei https://github.com/projectdiscovery/nuclei
  10. Jaeles https://github.com/jaeles-project/jaeles
  11. ChopChop https://github.com/michelin/ChopChop
  12. Inception https://github.com/proabiral/inception
  13. Eyewitness https://github.com/FortyNorthSecurity/EyeWitness
  14. Meg https://github.com/tomnomnom/meg
  15. Gau - Ottieni tutti gli URL https://github.com/lc/gau
  16. Snallygaster https://github.com/hannob/snallygaster
  17. NMAP https://github.com/nmap/nmap
  18. Waybackurls https://github.com/tomnomnom/waybackurls
  19. Gotty https://github.com/yudai/gotty
  20. GF https://github.com/tomnomnom/gf
  21. GF Patterns https://github.com/1ndianl33t/Gf-Patterns
  22. Paramspider https://github.com/devanshbatham/ParamSpider
  23. XSSER https://github.com/epsylon/xsser
  24. UPDOG https://github.com/sc0tfree/updog
  25. JSScanner https://github.com/dark-warlord14/JSScanner
  26. Takeover https://github.com/m4ll0k/takeover
  27. Keyhacks https://github.com/streaak/keyhacks
  28. S3 Bucket AIO Pwn https://github.com/blackhatethicalhacking/s3-buckets-aio-pwn
  29. BHEH Sub Pwner Recon https://github.com/blackhatethicalhacking/bheh-sub-pwner
  30. GitLeaks https://github.com/zricethezav/gitleaks
  31. Domain-2IP-Converter https://github.com/blackhatethicalhacking/Domain2IP-Converter
  32. Dalfox https://github.com/hahwul/dalfox
  33. Log4j Scanner https://github.com/Black-Hat-Ethical-Hacking/log4j-scan
  34. Osmedeus https://github.com/j3ssie/osmedeus
  35. getJS https://github.com/003random/getJS
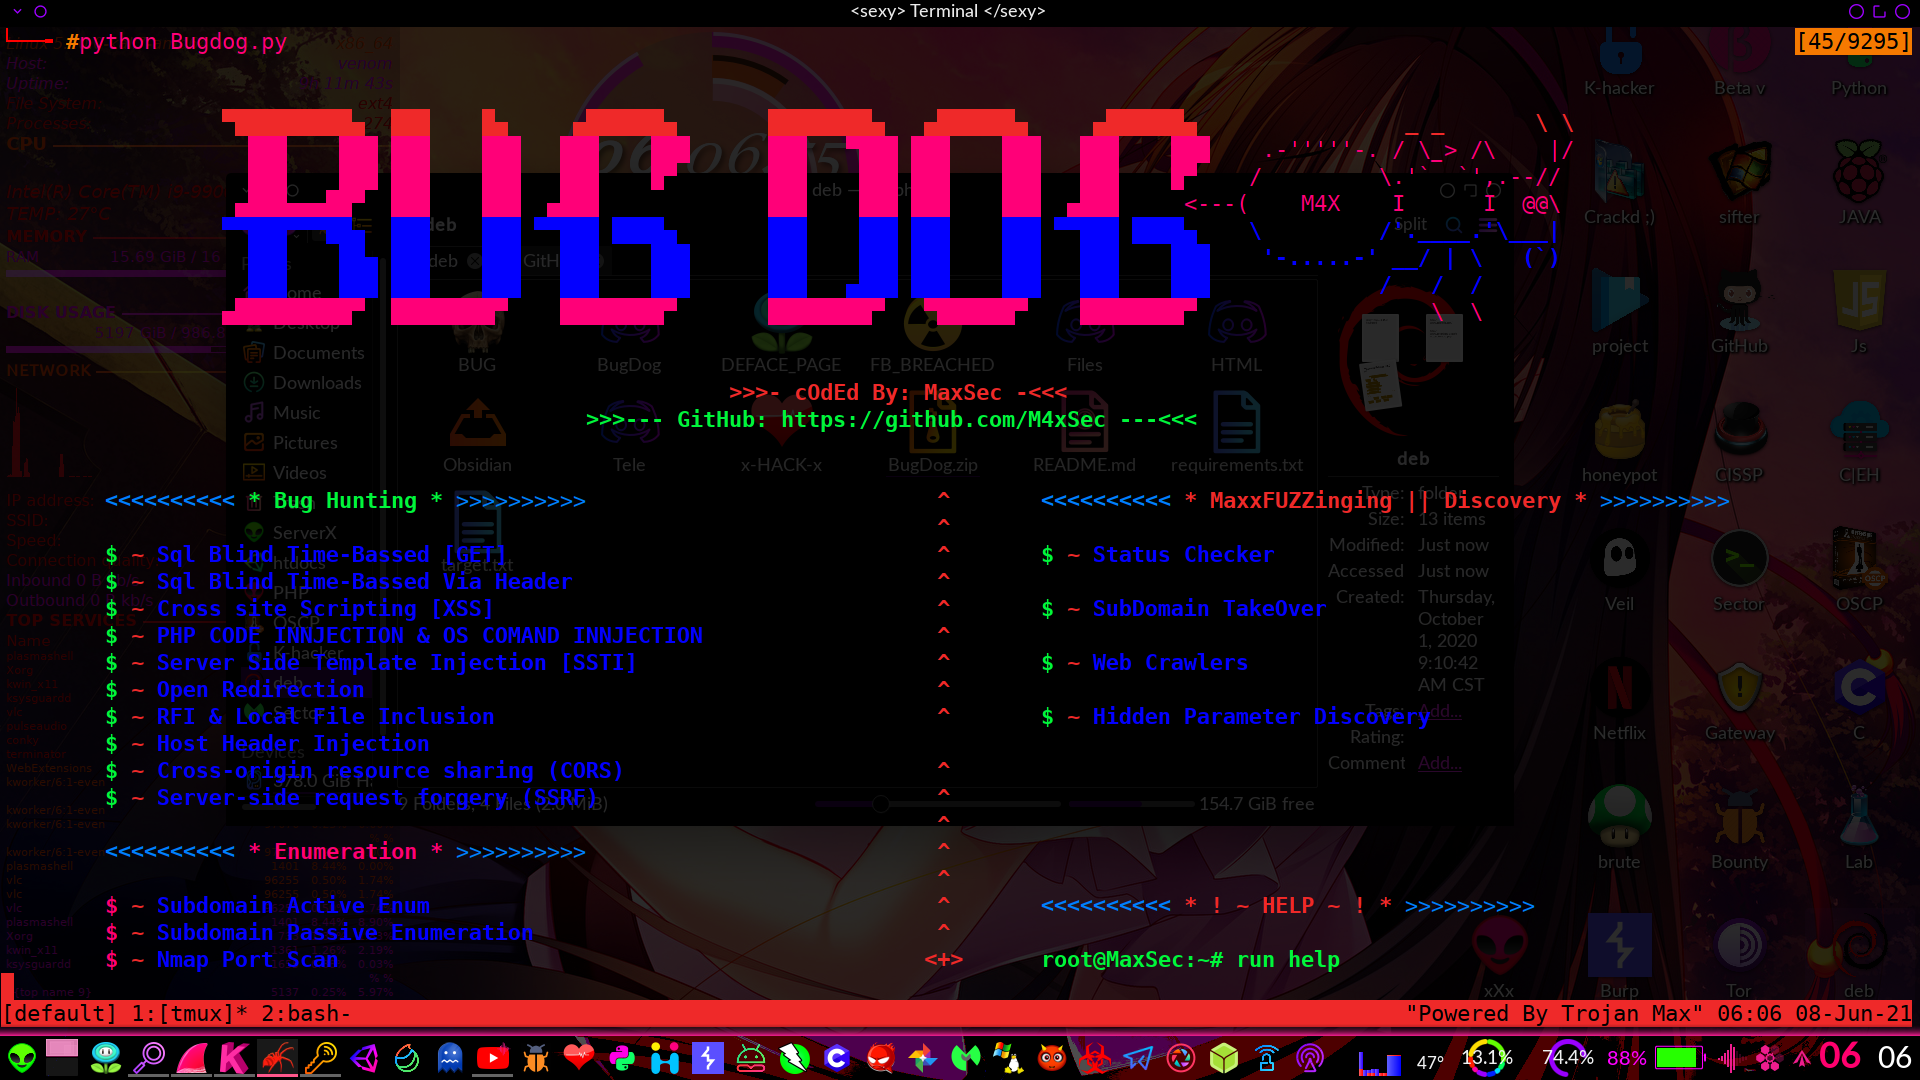
  • BugDog

    Un POTENTE STRUMENTO per la CACCIA AI BUG. Supporta SQL, XSS, esecuzione di codice PHP, SSRF,.... Ho aggiunto i miei payload personali trovati durante la mia caccia ai bug. Puoi aggiungere anche i tuoi payload PERSONALIZZATI ;)

    image

    • NOTA: BugDog è realizzato con Python e richiede python2 per funzionare perfettamente.

  • Bug-Bounty-Tools: Strumenti vari per Bug Bounty

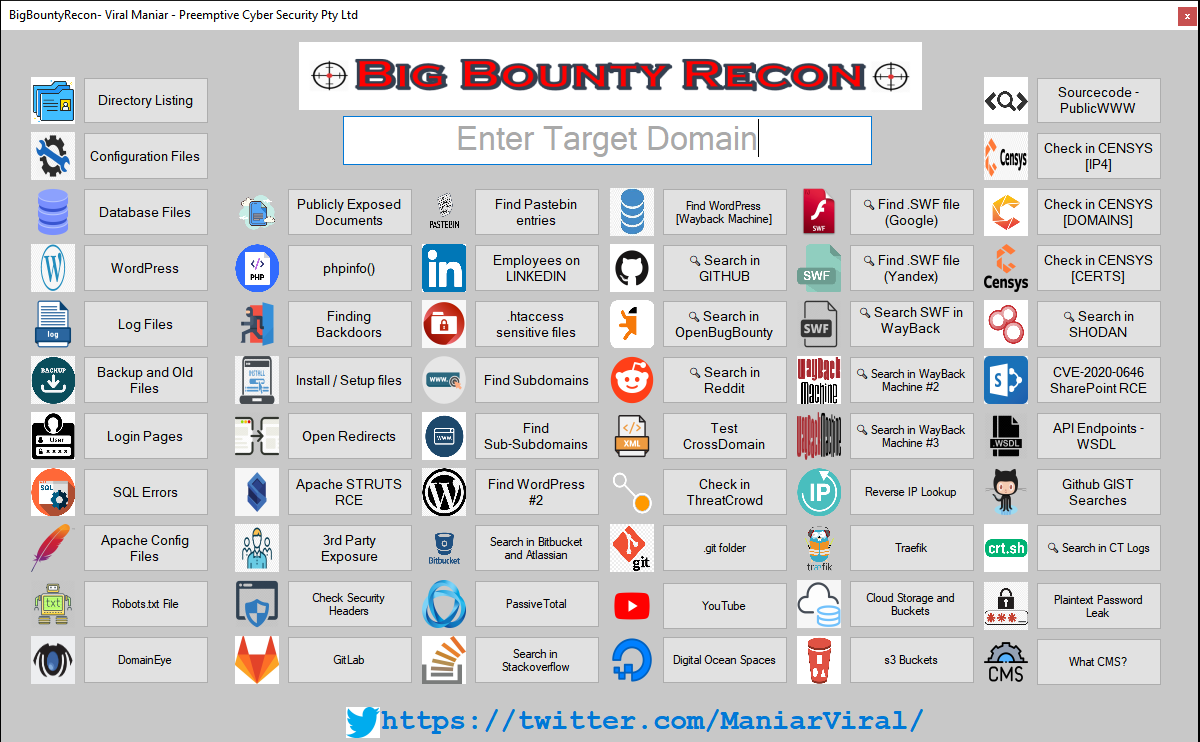
  • BigBountyRecon

    Lo strumento BigBountyRecon utilizza 58 diverse tecniche, usando vari Google dorks e strumenti open source, per accelerare il processo di ricognizione iniziale sull'organizzazione target.
    • image
Scarica lo strumento