
Skip to content
KitploitKITPLOIT
StrumentiExploitsBlog
Log in
Invia
StrumentiExploitsBlog
Invia

Strumenti di Hacking, PenTest e Cybersecurity per il tuo Arsenale di Sicurezza!

Kitploit è una directory di strumenti di hacking, cybersecurity e pentesting. Scopri gli ultimi aggiornamenti dei progetti per trovare vulnerabilità, analizzare sistemi, automatizzare i test e rafforzare la tua sicurezza.

FeedContattoPrivacy© 2026 Kitploit

Directory degli strumenti

Categorie

Vedi tutte le categorie
Loading categories
FISSURE — Il framework RF e di reverse engineering per tutti. Segui e ★ per mostrare il tuo supporto! | Kitploit

Strumenti/GitHubGitHub/ainfosec/fissure
Reverse EngineeringFuzzingSicurezza WirelessCTFApprendimento e Formazione
GitHubainfosec/fissure

FISSURE

Il framework RF e di reverse engineering per tutti. Segui e ★ per mostrare il tuo supporto!
Vedi Repository
2.0k1381402 giorni faRevisionato da Kitploit
Condividi
Sito web
Contenuto non disponibile nella lingua richiesta. Visualizzazione della versione inglese.

FISSURE - The RF Framework

Frequency Independent SDR-based Signal Understanding and Reverse Engineering
Overview

FISSURE GRCon26 Conference Talk
GRCon26 Conference Talk
FISSURE Tactical Workflow Demo
Tactical Workflow Demo
GRCon26 Presentation Slides

Introduction

FISSURE is an open-source framework for RF analysis, automation, and distributed operations. It connects SDR hardware, signal processing, Sensor Nodes, geolocation, protocol analysis, targeting, and situational awareness within a single extensible environment.

FISSURE can run as a standalone workstation or scale across distributed Sensor Nodes connected over IP networks. GNU Radio and other tools provide the underlying RF processing, while FISSURE coordinates hardware, data, context, plugins, Actions, and operator workflows across local and remote systems.

The framework is designed for experimentation, research, education, capability development, and operational integration without locking users to a single protocol, sensor, platform, or use case.
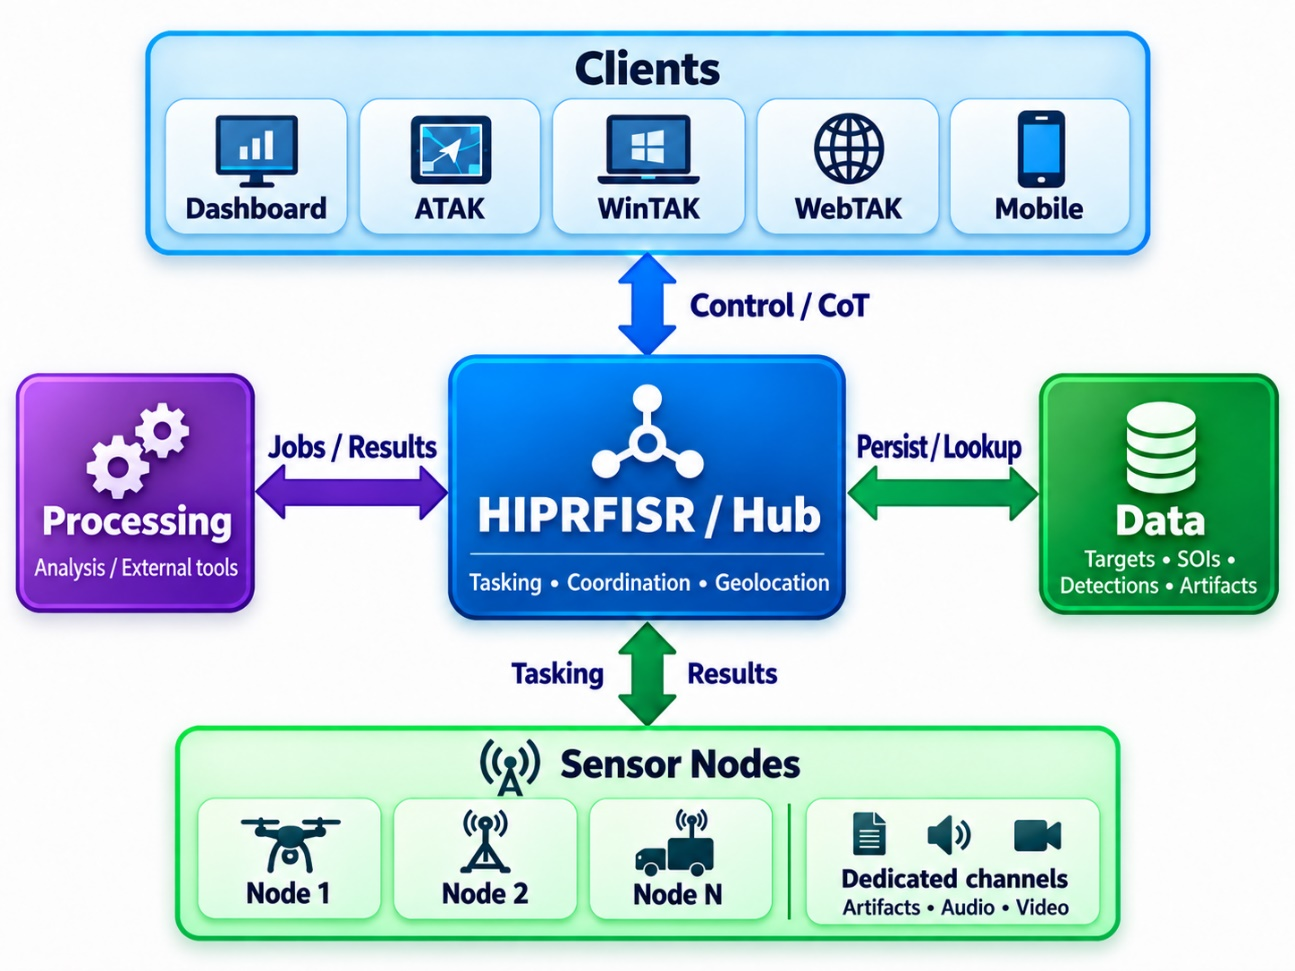
FISSURE distributed architecture

Workflow Overview

FISSURE organizes RF workflows around connected workspaces that share Sensor Nodes, SOIs, Targets, Detections, Artifacts, Findings, and plugin Actions.
  • Tactical: Monitor distributed Sensor Nodes, detections, SOIs, Targets, geolocation results, and other RF activity on a shared operational map.
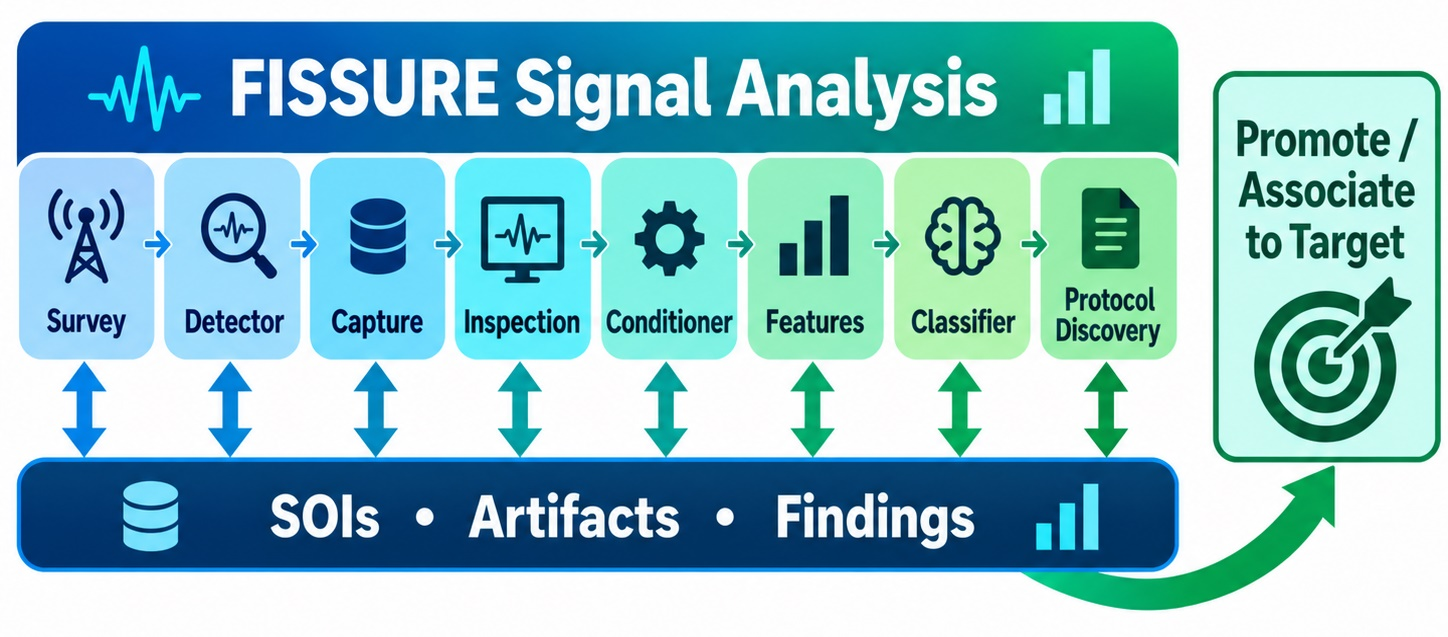
  • Signal Analysis: Move from survey and detection through capture, inspection, conditioning, feature extraction, classification, and protocol discovery.
  • Targets & Actions: Manage Targets and execute reusable plugin Actions through focused, sequential, fuzzing, and packet-crafting workflows.
  • Sensor Nodes: Configure local and remote nodes, manage hardware, transfer files, automate startup behavior, and monitor node status.
  • Library: Maintain reusable protocol information, packet definitions, archived signals, replay content, datasets, and RF reference material.
  • Plugins & Actions: Add, deploy, and execute capabilities across supported nodes and interfaces without modifying the FISSURE core.

FISSURE signal analysis workflow

Core Information Model

FISSURE connects workflows through a shared information model rather than treating each tool or tab as an isolated function. SOIs anchor signal analysis, Targets anchor operational context, Detections capture sensor observations, Artifacts and Findings preserve data and results, and Alerts and Action Recommendations surface information that may require attention or follow-on action.
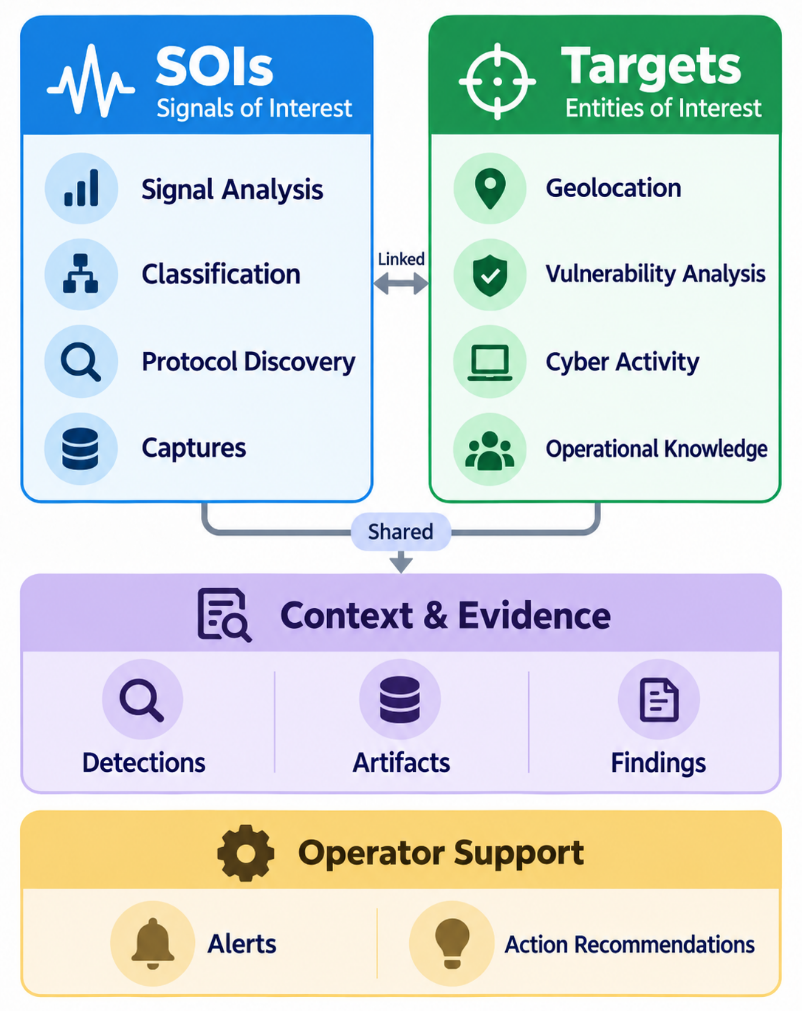
FISSURE core information model

Key Capabilities

  • Detect, classify, capture, and analyze RF signals
  • Record, inspect, replay, and manipulate IQ data
  • Discover protocols, build packets, and perform RF/cyber experimentation
  • Execute fuzzing, vulnerability analysis, and reusable test workflows
  • Coordinate local and distributed Sensor Nodes, SDRs, sensors, and tools
  • Geolocate emitters and maintain persistent Targets, detections, and observations
  • Share RF-derived awareness, alerts, artifacts, and target information through TAK
  • Extend capabilities through deployable plugins, Actions, and reusable Operations
  • Automate multi-step workflows across local and remote systems
  • Integrate custom analysis, external tools, and emerging AI/ML capabilities

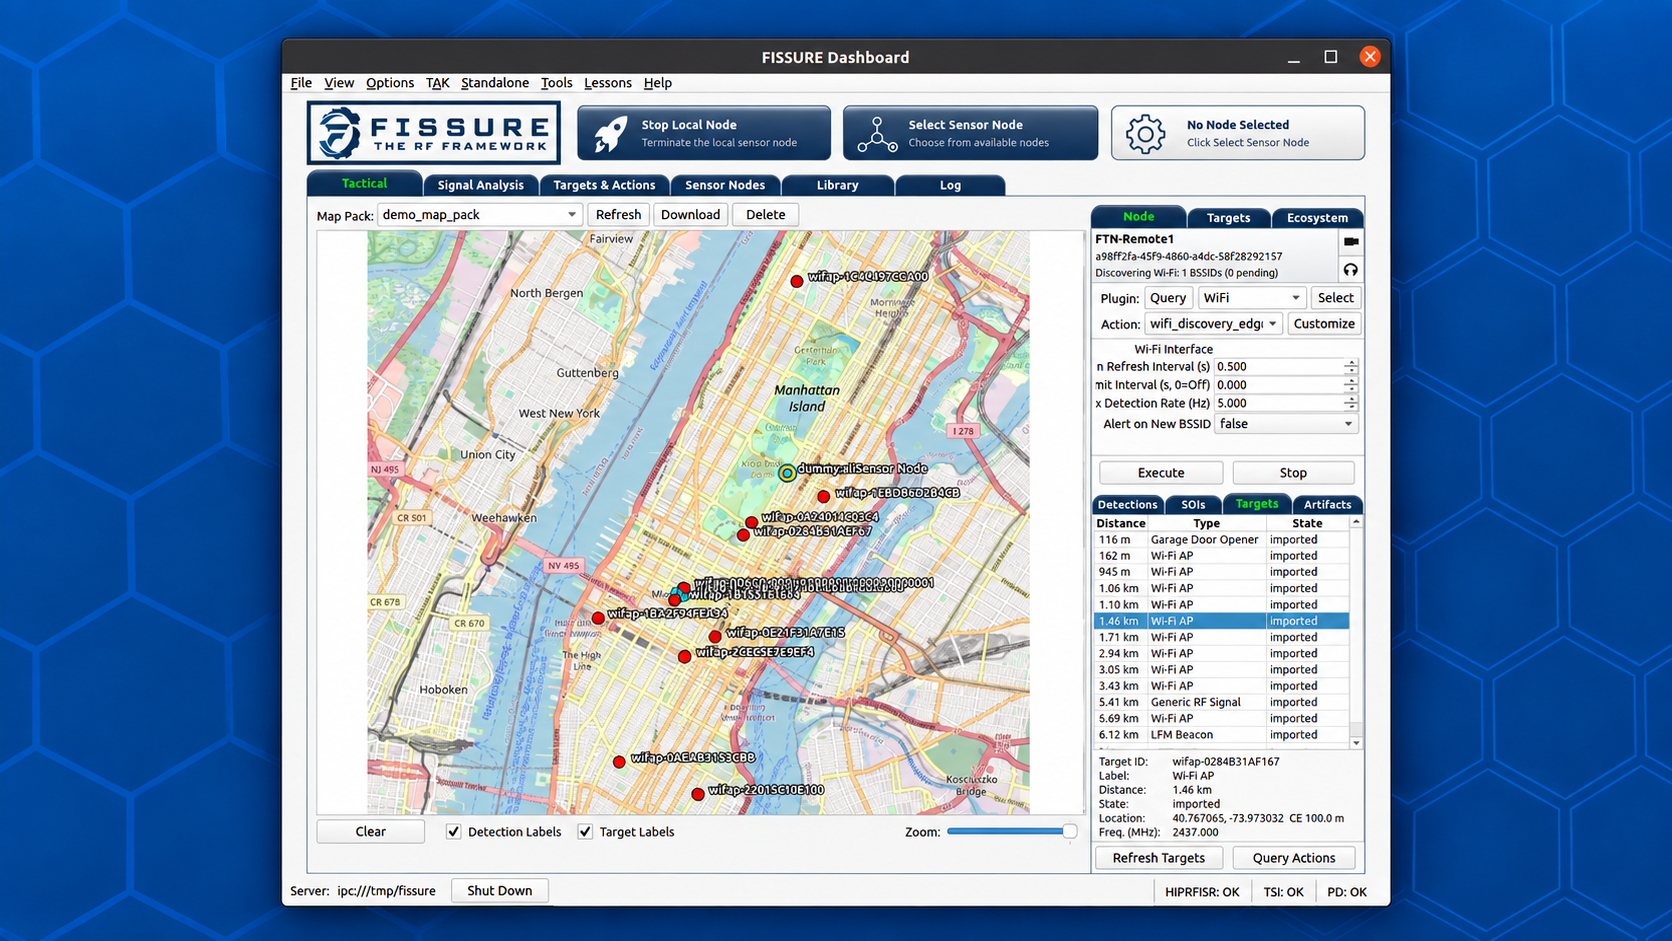
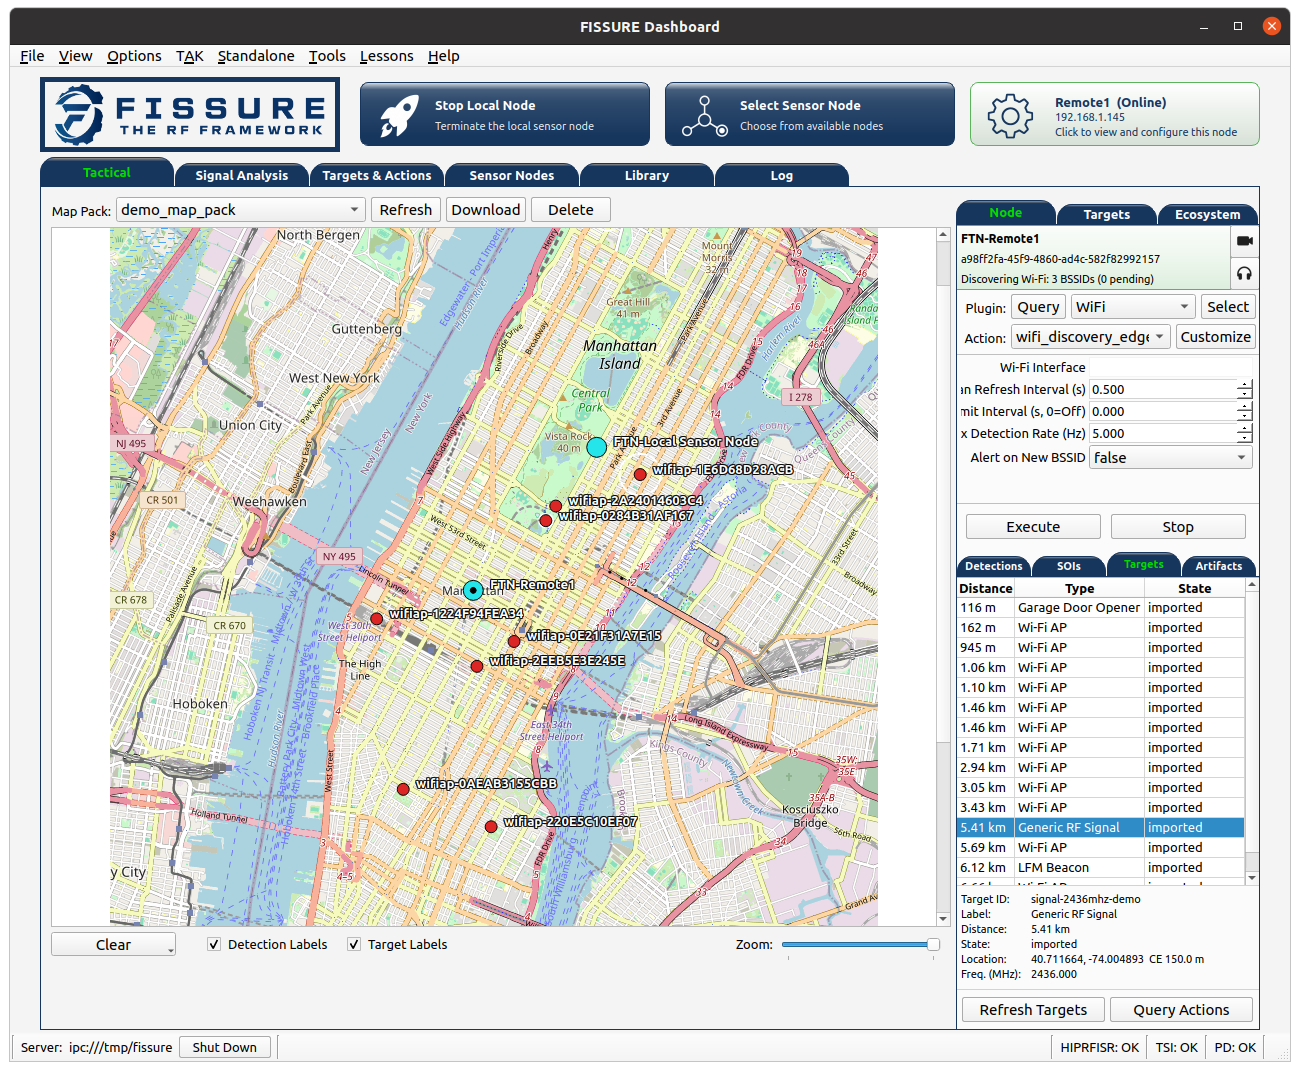
FISSURE Tactical Dashboard
FISSURE Tactical view connecting distributed Sensor Nodes, detections, SOIs, Targets, and operational context.

FISSURE and Fracture

Fracture is AIS's deployable tactical RF system built on the open-source FISSURE framework.

FISSURE provides the software foundation for RF sensing, signal analysis, distributed Sensor Nodes, geolocation, TAK integration, automation, and plugin-based capability development. Fracture packages that foundation into purpose-built hardware and software configurations designed for operational deployment.

Fracture combines SDRs, compute, networking, plugins, and mission-specific integrations around fixed-site, vehicle, manpack, sUAS, and other distributed deployments while preserving the flexibility and extensibility of FISSURE.
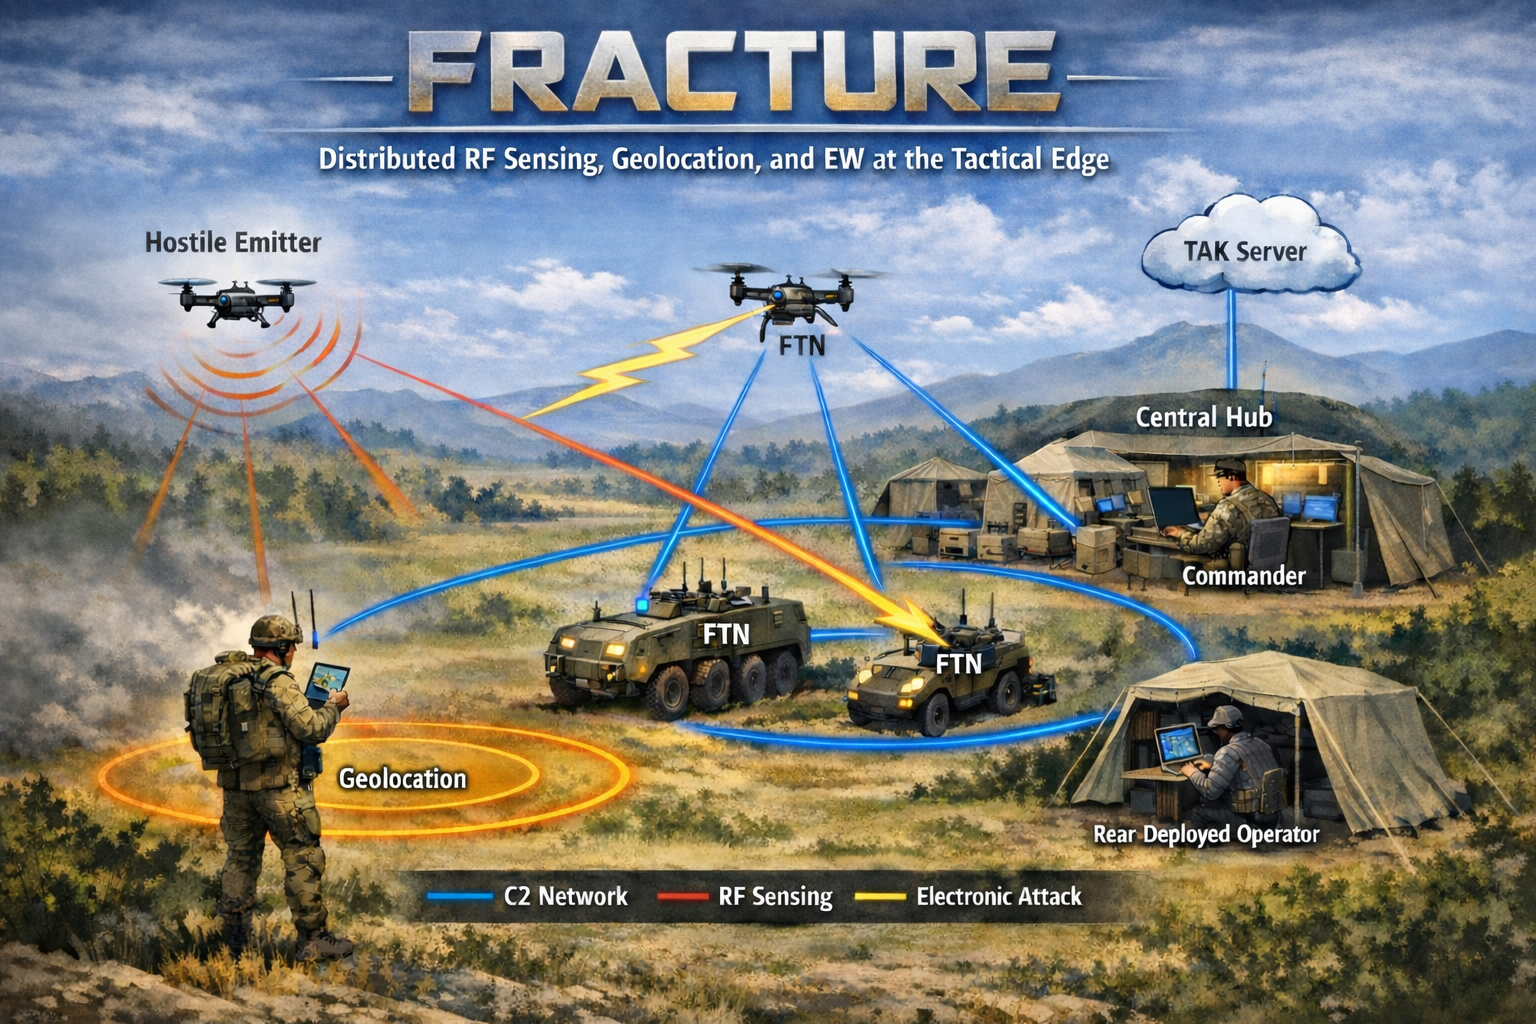
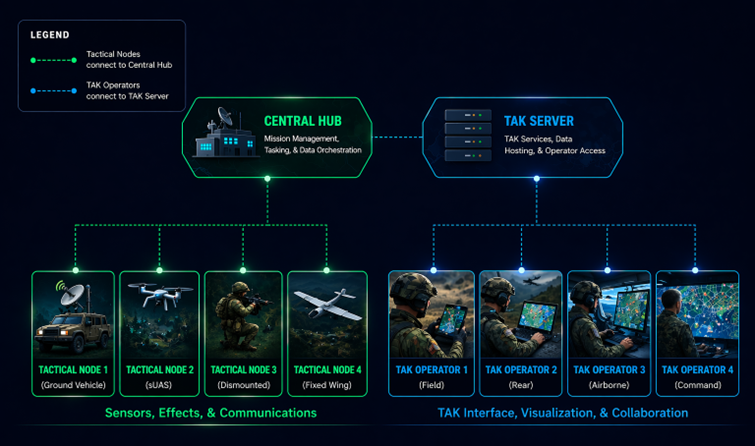
Fracture System Architecture

Deployment Options

FISSURE supports multiple deployment models depending on the intended workflow and operating environment:
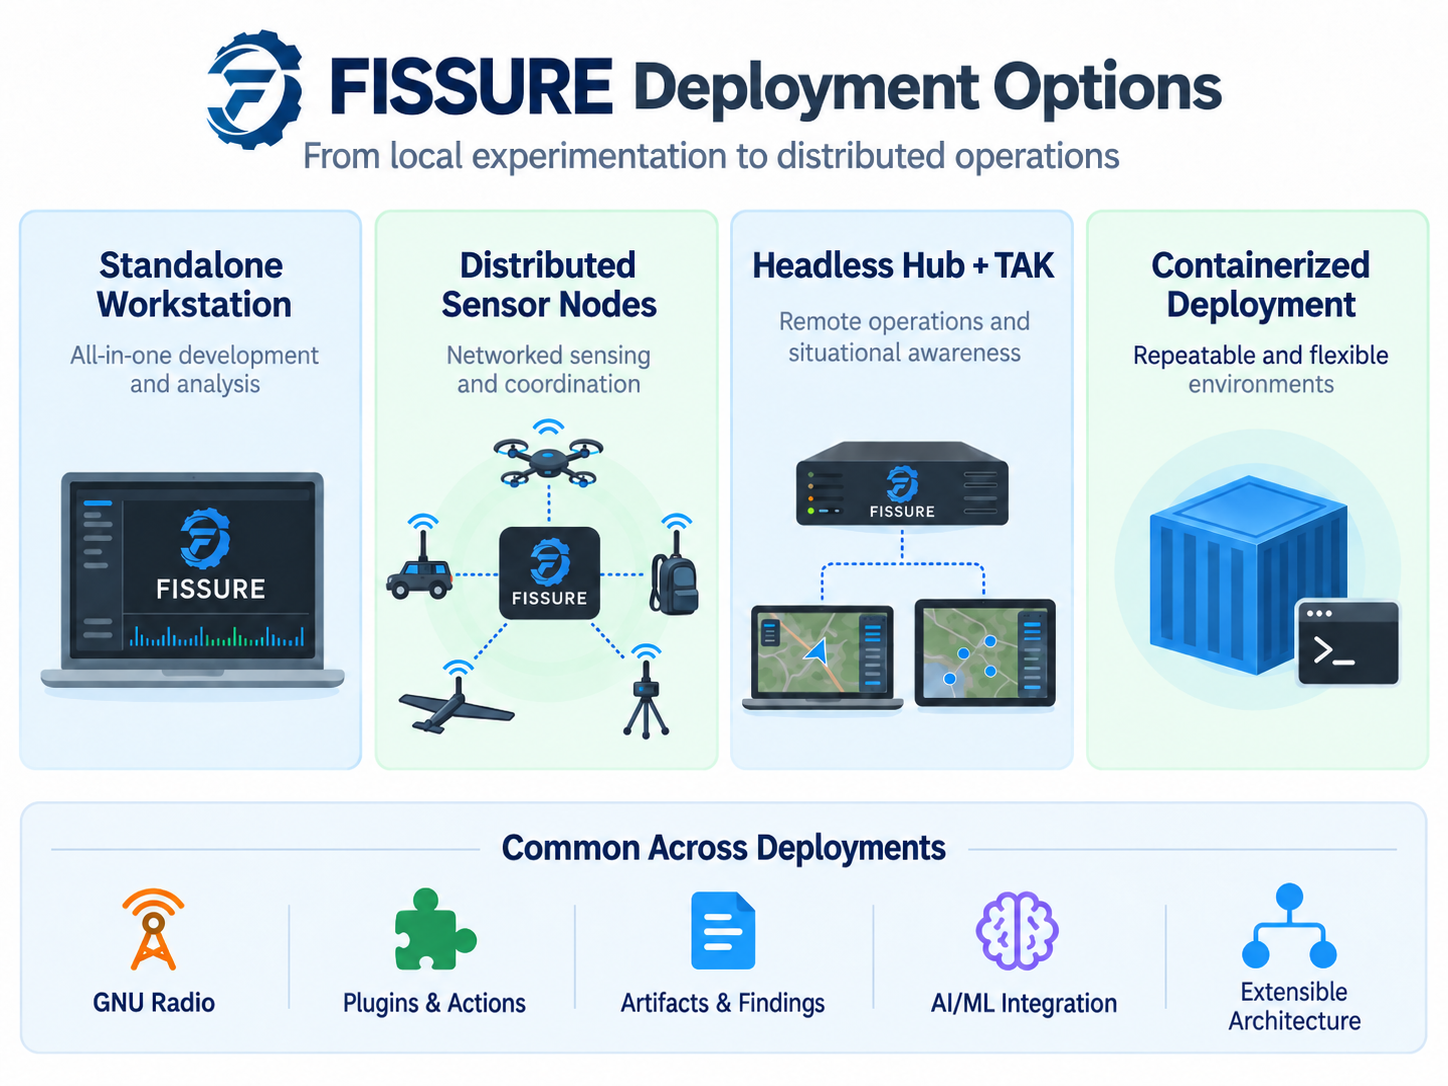
  • Standalone Workstation: Run the Dashboard, HIPRFISR, and a local Sensor Node on a single system for development, analysis, and experimentation.
  • Distributed Sensor Nodes: Run RF and plugin capabilities on remote systems while coordinating tasking, results, and data through a central hub.
  • Headless Hub: Run HIPRFISR and supporting services without the Dashboard for remote operations, TAK integration, and distributed deployments.
  • Containerized Deployment: Use Apptainer to build repeatable Dashboard, HIPRFISR, Sensor Node, Base, Full, or custom environments.
  • TAK-Integrated Operations: Share targets, detections, alerts, geolocation results, artifacts, and other operational information through ATAK, WinTAK, and TAK Server.

FISSURE deployment options

What's New

NEW

Connected Signal Analysis Workflows: FISSURE now connects survey, detection, capture, inspection, conditioning, feature extraction, classification, and protocol discovery through SOI-centered workflows with associated Artifacts and Findings.

NEW

Scarica lo strumento

Più Popolari

Vedi tutti →

Scopri gli strumenti più utilizzati dalla nostra community.

  • 1

    OsintHunter

    letox4/osinthunter

    🎯 Il toolkit OSINT definitivo: grafo di indagine, punteggio di affidabilità, famiglie di alias, mappa, timeline e report. 49 moduli, oltre 400 siti, nessuna chiave API richiesta.

    640
  • 2

    ghostlock-app

    yukonga/ghostlock-app

    # App di esecuzione con un tocco GhostLock (CVE-2026-43499)

    479
  • 3

    ARTEX

    baarai/artex

    Piattaforma di penetration testing autonoma multi-agente basata su LLM con agenti planner/worker, grafi di asset e di esplorazione, registrazione del traffico MITM e retesting delle vulnerabilità.

    391
  • 4

    redforge

    cybersecurity91/redforge

    Toolkit red team lato browser con 102 strumenti offline per ricognizione, generazione di payload, attacchi alle credenziali, crittografia, codifica e reportistica dell'engagement.

    335
  • 5

    CyberStrikeAI

    ed1s0nz/cyberstrikeai

    Il sistema d'azione per la cybersecurity nativa AI—dove l'intento diventa esecuzione governata, le evidenze diventano memoria operativa, e ogni operazione migliora la successiva.

    258
  • 6

    antifox

    antifox-ai/antifox

    Piattaforma multi-agente di penetration testing autonoma basata sull'IA che esegue ricognizione, scoperta della superficie d'attacco, validazione dello sfruttamento e consegna di report supportati da evidenze.

    249

Esplora tutti gli strumenti

Sfoglia la nostra collezione di strumenti

Vedi tutti gli strumenti →