CyberStrikeAI
The system of action for AI-native cybersecurity—where intent becomes governed execution, evidence becomes operational memory, and every operation…

The system of action for AI-native cybersecurity—where intent becomes governed execution, evidence becomes operational memory, and every operation…

वास्तविक समय भू-स्थानिक OSINT प्लेटफॉर्म जो 60+ सार्वजनिक टेलीमेट्री फीड्स (ADS-B, AIS, उपग्रह, CCTV) को एकीकृत मानचित्र में एकत्रित करता है, जिसमें…

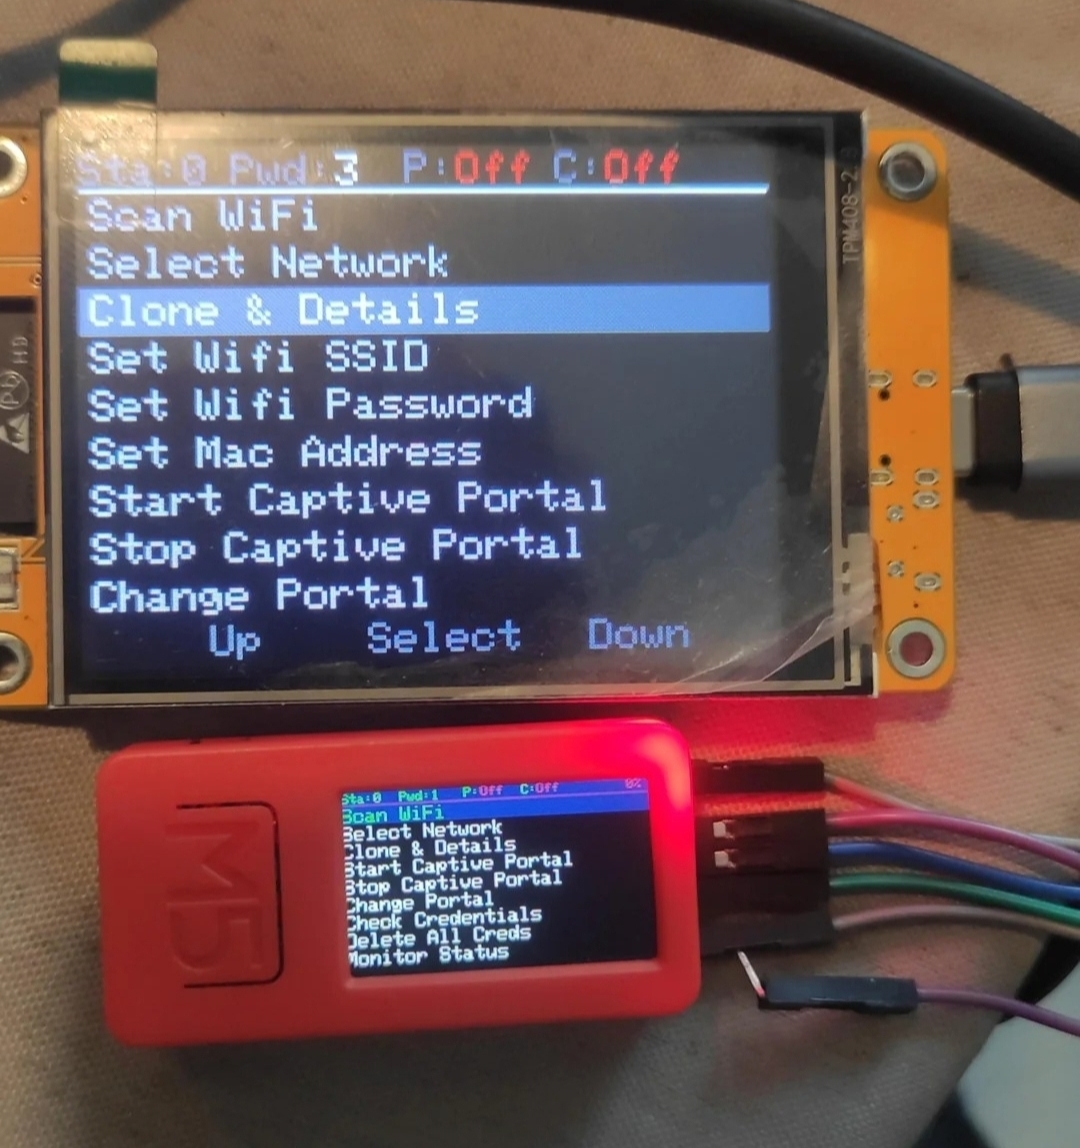
M5Stack उपकरणों के लिए बहुउद्देशीय WiFi पैठ परीक्षण टूलकिट। सुरक्षा शिक्षा और रेड टीम मूल्यांकन के लिए नेटवर्क स्कैनिंग, ईविल-ट्विन हमले,…

सर्व-इन-वन पेनिट्रेशन टेस्टिंग प्लेटफॉर्म जिसमें MITM प्रॉक्सी, वेब फ़ज़र, रिवर्स कनेक्शन हैंडलर, और स्वचालित सुरक्षा परीक्षण और एक्सप्लॉइटेशन के लिए…

Autonomous Hacking Agent for Red Team

Red team framework and multi-operator C2 platform with AI agents, malleable implants, rootkits, phishing engine, and 741 CLI commands covering the…

विंडोज/एडी वातावरण में स्वचालित नेटवर्क प्रमाणीकरण परीक्षण, क्रेडेंशियल हार्वेस्टिंग, और पार्श्व आंदोलन के लिए मॉड्यूलर प्रोटोकॉल समर्थन वाला…

AI एजेंट्स के लिए एक्सेस कंट्रोल। Claude Code, Codex, Gemini, Cursor और किसी भी MCP सर्वर को क्या करने की अनुमति है, यह सेट करें, जोखिम भरे कार्यों…

Go-आधारित शोषण विकास ढांचा जिसमें लक्ष्य सत्यापन, संस्करण स्कैनिंग, शोषण और C2 के लिए निर्मित चरण हैं। कई पेलोड, प्रोटोकॉल सहायकों और Metasploit जैसे…

CAPE कोर और सामुदायिक पार्सर

Aggregated Zeek-format threat intelligence feeds with combined indicators from public and curated sources for continuous IDS and network threat…

a guard that blocks catastrophic agent actions

ब्राउज़र शोषण फ्रेमवर्क परियोजना

पुल-आधारित C2 फ्रेमवर्क जिसमें दस नेटिव ट्रांसपोर्ट, समवर्ती मल्टी-प्रोफ़ाइल हैंडलर, ECDSA-हस्ताक्षरित टास्किंग, और RBAC तथा Qt/CLI कंसोल के साथ एक…

एक मॉड्यूलर C2 फ्रेमवर्क

खुला-स्रोत शोषण ढांचा जिसमें पेनिट्रेशन टेस्टिंग, कमजोरियों की पुष्टि और नेटवर्क व अनुप्रयोगों में सुरक्षा अनुसंधान के लिए मॉड्यूलर पेलोड, एनकोडर और…

Feature-rich single-binary file server for red teamers and developers. HTTP/S · WebDAV · FTP/SFTP · SMB · LDAP/S · NTLM hash capture · DNS/SMTP…

स्वायत्त Rust एंडपॉइंट सुरक्षा एजेंट जो Ring-0 Windows ड्राइवर और Linux eBPF प्री-एक्ज़ीक्यूशन ब्लॉकिंग, YARA डिटेक्शन, MITRE ATT&CK मैपिंग, और P2P…