


AI-संचालित सुरक्षा सह-पायलट जो आपके कोडिंग करते समय कमज़ोरियों को पकड़ता है। डेवलपर्स के लिए रीयल-टाइम सुरक्षा स्कैनिंग, शैक्षिक व्याख्याएँ, और ऑटो फिक्स।


आपका AI-संचालित सुरक्षा संरक्षक — अब लाइव हमलावर इंटेलिजेंस से जुड़ा हुआ
विशेषताएँ • आर्किटेक्चर • Raven एकीकरण • इंस्टॉलेशन • रोडमैप • योगदान
CodeGuard Copilot सुरक्षा कमज़ोरियों को आपके कोडिंग करते समय पकड़ता है, कमिट करने के बाद नहीं। यह नियतात्मक regex पैटर्न डिटेक्शन को AI-संचालित गहन विश्लेषण और Raven/WraithWall इकोसिस्टम से लाइव हमलावर इंटेलिजेंस के साथ जोड़ता है ताकि आपको ऐसा संदर्भ मिले जो कोई अन्य VS Code सुरक्षा एक्सटेंशन नहीं दे सकता।
इसे अलग क्या बनाता है:
.codeguard.json कस्टम नियम कॉन्फ़िगरेशन — regex, severity, CWE, प्रति-फ़ाइल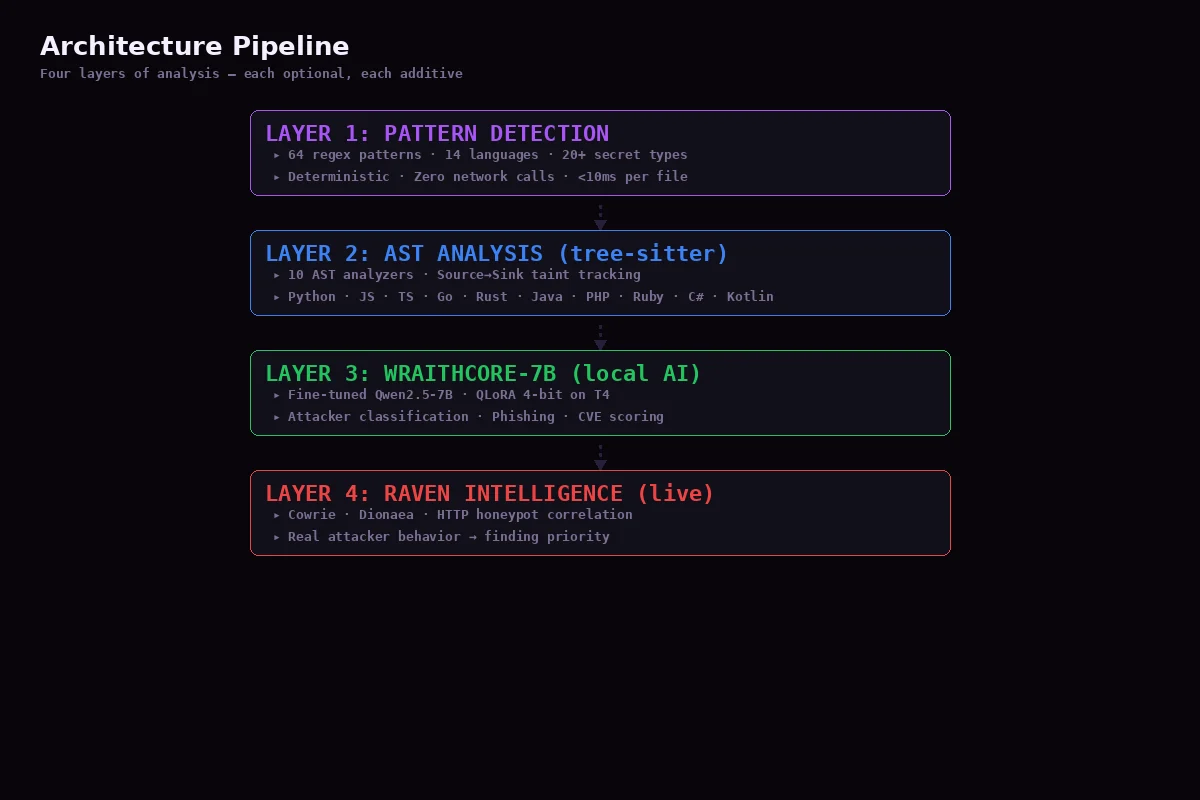
 │ │ │ │
│ │ ┌─────────────┐ ┌────────────────┐ │ │
│ │ │ Knowledge │ │ Raven Bridge │ │ │
│ │ │ Graph │ │ ← attacker data │ │ │
│ │ │ finding→CWE │ │ → threat intel │ │ │
│ │ │ →MITRE→fix │ │ │ │ │
│ │ └─────────────┘ └────────────────┘ │ │
│ └──────────────────┬───────────────────┘ │
│ │ │
│ ▼ │
│ ┌──────────────────────────────────────┐ │
│ │ Developer Feedback │ │
│ │ QuickFix · Explain · Suppress · Fix │ │
│ │ Training · Report · CI/CD │ │
│ └──────────────────────────────────────┘ │
│ │
└──────────────────────────────────────────────┘
│
▼
┌──────────────────────────────────────────────┐
│ WraithWall / Raven │
│ │
│ Cowrie Honeypot → Attacker Telemetry │
│ Campaign Correlation → Behavioral DNA │
│ CISA KEV → OWASP → Composite Scoring │
│ Cross-Repo Systemic Patterns │
│ Dark-Web Breach Monitoring │
└──────────────────────────────────────────────┘
---

## Raven Intelligence Bridge

CodeGuard Copilot, Raven की हमलावर टेलीमेट्री पाइपलाइन के लिए **फ्रंटएंड इंटेलिजेंस उपभोक्ता** है। जब Cowrie honeypots वास्तविक हमलावरों को exploitation तकनीकों का उपयोग करते हुए देखते हैं, तो पैटर्न CodeGuard में प्रवाहित होते हैं:
Attacker uses SQL injection on honeypot ↓ Raven detects: CWE-89, credential_access, threat_score=85 ↓ RavenIntelBridge.ingestEvent() receives event ↓ Generates candidate CodeGuard pattern at confidence 0.85 ↓ Proposed pattern: "SQL Injection (attacker-observed)" ↓ Human review → published as CodeGuard rule ↓ Developers protected against the actual exploit
इसके विपरीत, जब CodeGuard कोई कमज़ोरी पाता है, तो यह संरचित Raven फ़ीडबैक उत्पन्न करता है:
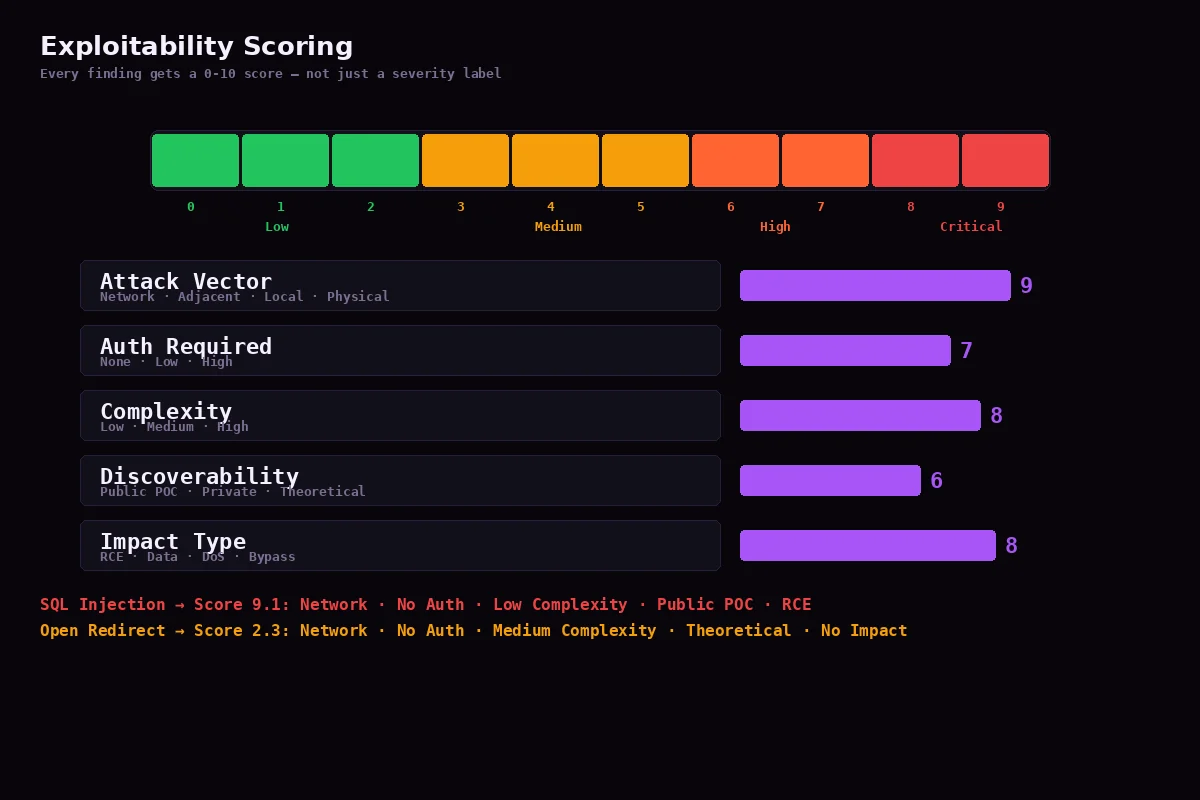
CodeGuard finding: CWE-798 hardcoded secret in auth/login.js ↓ RavenThreatFeedback.generateIntelligence() ↓ MITRE techniques: T1552, T1078 ↓ Raven priority score: 72 (network attack vector, low complexity) ↓ Raven elevates this finding in composite scoring ↓ SOC team sees: "Attacker-aligned credential finding in production repo"
---

## पाई गई कमज़ोरी श्रेणियाँ

### गंभीर
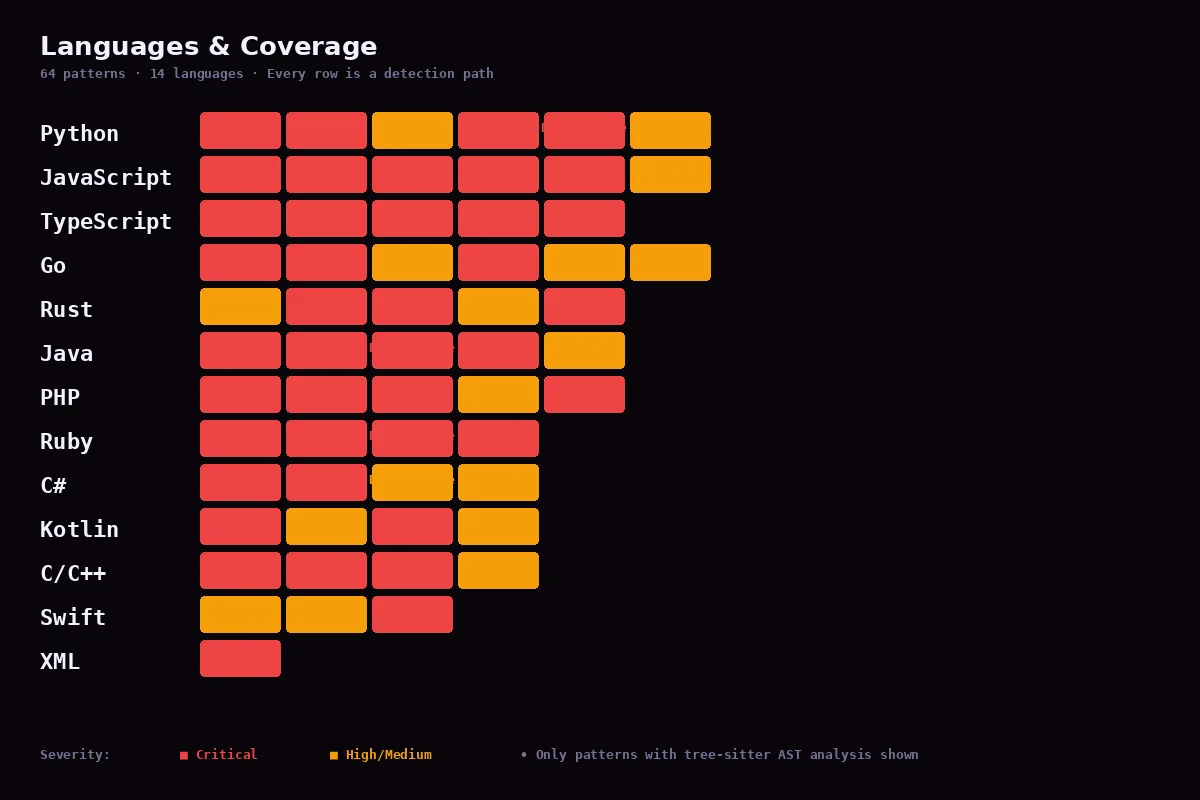
SQL Injection (CWE-89), Command Injection (CWE-78), NoSQL Injection (CWE-943), Hardcoded Secrets (CWE-798), Insecure Deserialization (CWE-502)

### उच्च
XSS (CWE-79), DOM-based XSS, Path Traversal (CWE-22), File Upload (CWE-434), Weak Crypto (CWE-327), Unsafe Blocks (Rust), Unescaped HTML (Go)

### मध्यम
CORS Misconfiguration (CWE-942), Open Redirect (CWE-601), Insecure Random (CWE-338), ReDoS (CWE-1333), Memory Leak (C++), Mass Assignment (Ruby)

### निम्न
Weak Password Storage, Express Trust Proxy, Missing Security Headers, Framework anti-patterns

### भाषा-विशिष्ट (18 नए)
Go: SQLi, Insecure Random, Hardcoded Secret, Unescaped HTML
Rust: Unsafe Block, Hardcoded Secret, Command Injection, Weak Crypto
C++: Buffer Overflow, Memory Leak, SQL Injection
C#: SQL Injection, Connection String, Insecure Deserialization
Ruby: SQL Injection, Command Injection, Mass Assignment, Unsafe YAML

---

## फाइन-ट्यून्ड सुरक्षा मॉडल (v0.3.1)
