Skip to content
KitploitKITPLOIT
उपकरणएक्सप्लॉइटब्लॉग
Log in
जमा करें
उपकरणएक्सप्लॉइटब्लॉग
जमा करें

हैकिंग, पेनटेस्ट और साइबर सुरक्षा उपकरण आपके सुरक्षा शस्त्रागार के लिए!

Kitploit हैकिंग, साइबर सुरक्षा और पेंटेस्टिंग टूल्स की एक निर्देशिका है। कमजोरियों को खोजने, सिस्टम का विश्लेषण करने, परीक्षण को स्वचालित करने और अपनी सुरक्षा को मजबूत करने के लिए नवीनतम प्रोजेक्ट अपडेट खोजें।

फ़ीडसंपर्कगोपनीयता© 2026 Kitploit

टूल निर्देशिका

श्रेणियाँ

सभी श्रेणियाँ देखें
Loading categories
उपकरण/GitHubGitHub/katrielmoses/mailaccess
OSINT (Open Source Intelligence)ReconnaissanceVulnerability AnalysisData ExfiltrationForensicsInformation GatheringPenetration TestingSocial EngineeringThreat IntelligenceIdentity & Access Management (IAM)Email Harvesting
319352211 दिन पहलेKitploit द्वारा समीक्षित
साझा करें
GitHub
katrielmoses/mailaccess

MailAccess

Free email OSINT tool, 2500+ platforms, identity clustering, breach detection. No API keys required. pip install mailaccess

रिपॉजिटरी देखें
अनुरोधित भाषा में सामग्री उपलब्ध नहीं है। अंग्रेज़ी संस्करण दिखाया जा रहा है।

Let's connect
X: @delzynkatriel LinkedIn: /in/katriel-moses

MailAccess: email recon that shows its work

License: MIT Python 3.10+ Docker Compose PyPI version PyPI downloads

mailaccess.pro  ·  Docs  ·  PyPI  ·  Changelog

Open-source email OSINT and email scraper. One email in, every account behind it: 82 modules check 5,300+ platforms, and every finding says how it was found and how sure we are. One domain in, every public email at the company. Run it on your own machine, or use it hosted at mailaccess.pro.


Powered by Netlas: see what runs on every host behind a domain Powered by ipgeolocation.io: IP geolocation and threat intel for every IP Powered by WhoisFreaks: who owned a domain, and what else they registered Partnered with IPBurger: dedicated ISP IPs that stay yours, built for recon Partnered with Mango Proxy: residential IPs that keep big harvests clean

Built for security researchers, OSINT analysts and penetration testers working under authorization. Read DISCLAIMER.md before use.
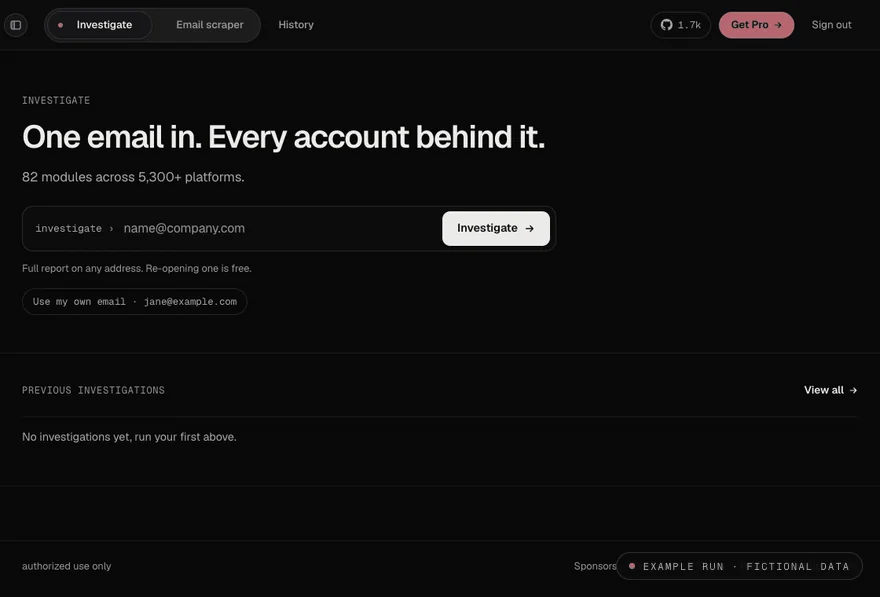
See it run

Example run on the web app: jane@example.com is investigated live, accounts appear as each check returns, then the report opens

Example run with fictional data ([email protected]). The live view, then the report it opens into.

Install

pip install mailaccess
mailaccess investigate [email protected]

Python 3.10+. The CLI starts and stops its backend for each run. Use mailaccess serve for a persistent server, mailaccess[ml] for spaCy name classification, and mailaccess[browser] (then playwright install chromium) for the optional headless-browser checks. Docker and self-hosting: docs/self-hosting.md.

Quick start

mailaccess investigate [email protected]                  # every account behind an email
mailaccess investigate [email protected] -o report.html   # save the report (also .pdf, .md, .json)
mailaccess harvest-emails --domain example.com           # every public email at a domain
mailaccess find-email --name "Jane Doe" --domain example.com
mailaccess login                                         # sign in for your free key
mailaccess doctor                                        # check your setup
mailaccess keys set HIBP_API_KEY your-key                # optional providers
mailaccess upgrade

Pipelines, stdin, JSONL and CI: docs/integrations.md.

What it does

टूल डाउनलोड करें

सबसे लोकप्रिय

सभी देखें →

हमारे समुदाय द्वारा सबसे अधिक उपयोग किए जाने वाले उपकरण खोजें।

  • 1

    OsintHunter

    letox4/osinthunter

    🎯 अंतिम OSINT टूलकिट: जाँच ग्राफ़, विश्वास स्कोरिंग, उपनाम परिवार, मानचित्र, टाइमलाइन और रिपोर्ट। 49 मॉड्यूल, 400+ साइटें, किसी API कुंजी की आवश्यकता नहीं।

    790
  • 2

    ghostlock-app

    yukonga/ghostlock-app

    # घोस्टलॉक वन-टैप निष्पादन ऐप (CVE-2026-43499)

    508
  • 3

    ARTEX

    baarai/artex

    प्लानर/वर्कर एजेंट, एसेट और एक्सप्लोरेशन ग्राफ़, MITM ट्रैफ़िक रिकॉर्डिंग, और भेद्यता पुनःपरीक्षण के साथ LLM मल्टी-एजेंट स्वायत्त पेनेट्रेशन टेस्टिंग प्लेटफ़ॉर्म।

    435
  • 4

    redforge

    cybersecurity91/redforge

    ब्राउज़र-साइड रेड टीम टूलकिट, जिसमें रेकॉन, पेलोड जनरेशन, क्रेडेंशियल हमलों, क्रिप्टो, एन्कोडिंग और एंगेजमेंट रिपोर्टिंग के लिए 102 ऑफ़लाइन टूल्स हैं।

    346
  • 5

    CyberStrikeAI

    ed1s0nz/cyberstrikeai

    AI-मूल साइबरसुरक्षा के लिए कार्रवाई की प्रणाली—जहाँ इरादा नियंत्रित निष्पादन बन जाता है, साक्ष्य परिचालन स्मृति बन जाता है, और हर ऑपरेशन अगले को बेहतर बनाता है।

    263
  • 6

    looking-glass

    anonghosty/looking-glass

    CSIRT प्लेटफ़ॉर्म जो Shadowserver रिपोर्ट्स को MongoDB में इनजेस्ट करता है और उन्हें इंटरैक्टिव मैप्स, विश्लेषण, निष्कर्षों, सलाहों और कार्यकारी डैशबोर्ड के रूप में पुनः प्रस्तुत करता है।

    260

सभी उपकरण खोजें

हमारे उपकरणों का संग्रह ब्राउज़ करें

सभी उपकरण देखें →