
secretlint v13.0.5
प्लगेबल लिंटिंग टूल क्रेडेंशियल कमिट करने से रोकने के लिए।
Secretlint 
Secretlint is a Pluggable linting tool to prevent committing credentials.
Features
- Scanner: Find credentials in a project and report these
- Project Friendly: Easy to set up your project and integrate CI services
- Pre-Commit Hook: Prevent committing credential files
- Pluggable: Allow creating custom rule and flexible configuration
- Documentation: Describe the reason that rule detect it as secret
Quick Demo
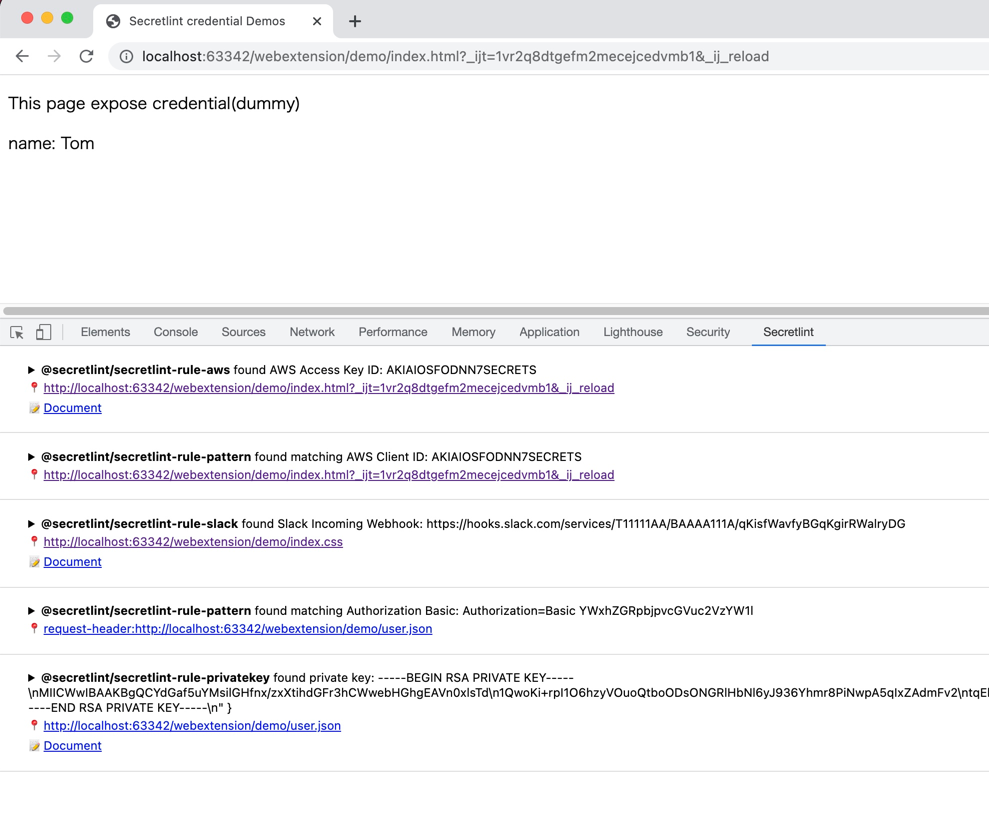
You can view secretlint linting result on https://secretlint.github.io/.
Quick Start
You can try to use Secretlint on your project at one command.
If you already have installed Docker:
docker run -v `pwd`:`pwd` -w `pwd` --rm -it secretlint/secretlint secretlint "**/*"
If you already have installed Node.js:
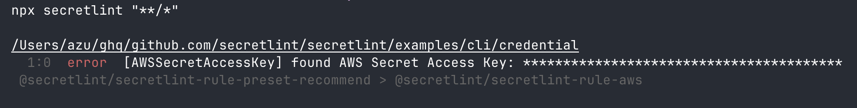
npx secretlint "**/*"
After running,
If you got empty result and exit status is 0, your project is secure.
Otherwise, you got some error report, your project includes credential as raw data.
You want to get continuous security, Please see following installation guide and setup pre-commit hook and CI.
Installation
Using Docker
Prerequisites: Require Docker
Use our Docker container to get an environment with Node.js and secretlint running as fast as you can download them.
You can check all files under the current directory with secretlint by following command:
docker run -v `pwd`:`pwd` -w `pwd` --rm -it secretlint/secretlint secretlint "**/*"
secretlint/secretlint docker container work without configuration by design.
This Docker Image has the built-in rules, such as @secretlint/secretlint-rule-preset-recommend and @secretlint/secretlint-rule-pattern, and this package:
For more details, please see secretlint's Dockerfile.
Using Node.js
Prerequisites: Require Node.js 22+.
Upgrading from Secretlint v13? See the migration guide.
Secretlint is written by JavaScript. You can install Secretlint using npm:
npm install secretlint --save-dev
You can run Secretlint on any file or directory like this:
npx secretlint "**/*"
Without a configuration file, Secretlint uses the recommended rules. To choose the rules and their options, set up a configuration file:
npx secretlint --init
📝 Secretlint supports glob pattern and glob pattern should be wrapped by a double quote.
It is also possible to install Secretlint globally using npm install --global. But, We do not recommend it, some rules may be broken globally.
Using Single-Executable Binary
Prerequisites: None
You can use secretlint command without Node.js by using a single-executable binary.
- Download the latest binary from Releases page
- Change the file permission to executable:
chmod +x ./secretlint - Run
./secretlint "**/*"to lint your project with the recommended rules - Run
./secretlint --initto create a configuration file when you want to choose the rules
For more details, please see publish/binary-compiler README.
Usage
secretlint --help shows Usage.
Secretlint CLI that scan secret/credential data.

Usage
$ secretlint [file|glob*]

Note
supported glob syntax is based on picomatch (the engine used by micromatch)
https://github.com/micromatch/picomatch#globbing-features
https://github.com/micromatch/micromatch#matching-features

Options
--init             setup config file. Create .secretlintrc.json file from your package.json
--format           [String] formatter name. Default: "stylish". Available Formatter: checkstyle, compact, github, jslint-xml, junit, pretty-error, stylish, tap, unix, json, mask-result, table
--output           [path:String] output file path that is written of reported result.
--secretlintrc     [path:String] path to the config file. Default: .secretlintrc.* from the current directory up to the root, or the recommended rules
--secretlintignore [path:String] path to an extra ignore file, relative to cwd. .secretlintignore in each directory is always read
--stdinFileName    [String] filename to process STDIN content. Some rules depend on filename to check content.
--no-color         disable ANSI-color of output.
--no-terminalLink  disable terminalLink of output.
--no-maskSecrets   disable masking of secret values; secrets are masked by default.
--no-glob          disable glob pattern interpretation; treat all inputs as literal file paths.
--no-gitignore     disable .gitignore cascade respect; .gitignore files are
                   respected by default (since v13).

Options for Developer
--profile          Print the performance profile instead of the lint results. --format json prints it as JSON.
--secretlintrcJSON [String] a JSON string of .secretlintrc. use JSON string instead of rc file.

Experimental Options
--locale            [String] locale tag for translating message. Default: en

Examples
# Scan a single file
$ secretlint ./README.md

# Scan all files (wrap glob in double quotes to avoid shell expansion)
$ secretlint "**/*"
$ secretlint "source/**/*.ini"

# Treat inputs as literal paths (for SvelteKit (group) / Next.js [param] etc.)
$ secretlint --no-glob "src/(auth)/login.ts"

# Lint STDIN content (filename hint affects which rules apply)
$ echo "SECRET" | secretlint --stdinFileName=secret.txt

# Use a custom config file
$ secretlint "**/*" --secretlintrc=.secretlintrc.custom.json

# Scan files ignored by .gitignore (e.g. to verify build artifacts)
$ secretlint --no-gitignore "dist/**/*"

# Mask secrets in a file in-place
$ secretlint .zsh_history --format=mask-result --output=.zsh_history

# Output JSON for programmatic parsing
$ secretlint "**/*" --format=json --output=secretlint-report.json

# Output GitHub Actions annotations in CI
$ secretlint "**/*" --format=github

Exit Status
Secretlint exits with the following values:

    - 0:
      - Linting succeeded, no errors found.
      - Found only "warning" or "info" severity messages.
      - Found lint error but --output is specified.
    - 1:
      - Linting failed, errors found.
    - 2:
      - Unexpected error occurred, fatal error.