Skip to content
KitploitKITPLOIT
OutilsExploitsBlog
Log in
Soumettre
OutilsExploitsBlog
Soumettre

Outils de Hacking, PenTest et Cybersécurité pour votre Arsenal de Sécurité !

Kitploit est un répertoire d'outils de hacking, de cybersécurité et de pentesting. Découvrez les dernières mises à jour des projets pour trouver des vulnérabilités, analyser des systèmes, automatiser les tests et renforcer votre sécurité.

FluxContactConfidentialité© 2026 Kitploit

Répertoire d'outils

Catégories

Voir toutes les catégories
Loading categories
Des sources sélectionnées à une fiche d’outil Dépôts, flux, communautés et index passent par la sélection, la classification, l’enrichissement et la traduction pour former une fiche d’outil illustrative. ISC License Copyright (c) 2026 Lucide Icons and Contributors Permission to use, copy, modify, and/or distribute this software for any purpose with or without fee is hereby granted, provided that the above copyright notice and this permission notice appear in all copies. THE SOFTWARE IS PROVIDED "AS IS" AND THE AUTHOR DISCLAIMS ALL WARRANTIES WITH REGARD TO THIS SOFTWARE INCLUDING ALL IMPLIED WARRANTIES OF MERCHANTABILITY AND FITNESS. IN NO EVENT SHALL THE AUTHOR BE LIABLE FOR ANY SPECIAL, DIRECT, INDIRECT, OR CONSEQUENTIAL DAMAGES OR ANY DAMAGES WHATSOEVER RESULTING FROM LOSS OF USE, DATA OR PROFITS, WHETHER IN AN ACTION OF CONTRACT, NEGLIGENCE OR OTHER TORTIOUS ACTION, ARISING OUT OF OR IN CONNECTION WITH THE USE OR PERFORMANCE OF THIS SOFTWARE. --- The following Lucide icons are derived from the Feather project: airplay, alert-circle, alert-octagon, alert-triangle, aperture, arrow-down-circle, arrow-down-left, arrow-down-right, arrow-down, arrow-left-circle, arrow-left, arrow-right-circle, arrow-right, arrow-up-circle, arrow-up-left, arrow-up-right, arrow-up, at-sign, calendar, cast, check, chevron-down, chevron-left, chevron-right, chevron-up, chevrons-down, chevrons-left, chevrons-right, chevrons-up, circle, clipboard, clock, code, columns, command, compass, corner-down-left, corner-down-right, corner-left-down, corner-left-up, corner-right-down, corner-right-up, corner-up-left, corner-up-right, crosshair, database, divide-circle, divide-square, dollar-sign, download, external-link, feather, frown, hash, headphones, help-circle, info, italic, key, layout, life-buoy, link-2, link, loader, lock, log-in, log-out, maximize, meh, minimize, minimize-2, minus-circle, minus-square, minus, monitor, moon, more-horizontal, more-vertical, move, music, navigation-2, navigation, octagon, pause-circle, percent, plus-circle, plus-square, plus, power, radio, rss, search, server, share, shopping-bag, sidebar, smartphone, smile, square, table-2, tablet, target, terminal, trash-2, trash, triangle, tv, type, upload, x-circle, x-octagon, x-square, x, zoom-in, zoom-out The MIT License (MIT) (for the icons listed above) Copyright (c) 2013-present Cole Bemis Permission is hereby granted, free of charge, to any person obtaining a copy of this software and associated documentation files (the "Software"), to deal in the Software without restriction, including without limitation the rights to use, copy, modify, merge, publish, distribute, sublicense, and/or sell copies of the Software, and to permit persons to whom the Software is furnished to do so, subject to the following conditions: The above copyright notice and this permission notice shall be included in all copies or substantial portions of the Software. THE SOFTWARE IS PROVIDED "AS IS", WITHOUT WARRANTY OF ANY KIND, EXPRESS OR IMPLIED, INCLUDING BUT NOT LIMITED TO THE WARRANTIES OF MERCHANTABILITY, FITNESS FOR A PARTICULAR PURPOSE AND NONINFRINGEMENT. IN NO EVENT SHALL THE AUTHORS OR COPYRIGHT HOLDERS BE LIABLE FOR ANY CLAIM, DAMAGES OR OTHER LIABILITY, WHETHER IN AN ACTION OF CONTRACT, TORT OR OTHERWISE, ARISING FROM, OUT OF OR IN CONNECTION WITH THE SOFTWARE OR THE USE OR OTHER DEALINGS IN THE SOFTWARE.
Dépôts
GitHub & GitLab
Veille sécurité
Blogs, RSS et Atom
Communautés
Reddit, X et contributions
Index sélectionnés
Listes et tendances
Trier et sélectionner
Classification
Enrichissement
Traduction
Outil et dépôt fictifs. Description, catégories, étoiles, forks et vues sont des exemples, pas des données réelles ou vérifiées. Outil et dépôt fictifs. Description, catégories, étoiles, forks et vues sont des exemples, pas des données réelles ou vérifiées. {"fictional":true,"name":"Tool","version":"1.0.1","repository":"owner/tool","live_metrics":false,"example_metrics":{"stars":1200,"forks":128,"views":8600}}
Outil
v1.0.1 owner/tool
Découvrez les actifs et
vérifiez les en-têtes HTTP.
Reconnaissance
Sécurité web
1,200 étoiles — Exemple fictif1.2k 128 forks — Exemple fictif128 8,600 vues — Exemple fictif8.6k

Outils

ToutSécurité AndroidAuthentification et AutorisationSécurité de l'Infrastructure CloudOutils DéfensifsCriminalistique DisqueSécurité des Systèmes EmbarquésUtilitaires GénérauxGestion des Indicateurs de Compromission (IOC)OSINT (Renseignement de Sources Ouvertes)Sniffing et Analyse de PaquetsCassage de Mots de PasseFrameworks de Tests d'IntrusionOutils de PhishingEscalade de PrivilègesReconnaissanceAnalyse StatiqueScanners de VulnérabilitésScanners de Vulnérabilités WebAudit Wi-FiSécurité BluetoothSécurité des ConteneursAnalyse Dynamique (Sandboxing)Outils de Chiffrement/DéchiffrementFrameworks d'ExploitationGestion des IdentitésSécurité iOSSécurité IoTCriminalistique MémoireCartographie RéseauOSINT pour l'Ingénierie SocialeAttaques de Mots de PasseGénération de PayloadsMécanismes de PersistanceScan de PortsAnalyse Statique de Code (SAST)Flux et Agrégateurs de MenacesAnalyse des VulnérabilitésProxies Web et InterceptionAnalyse de CodeÉnumération DNS et Sous-domaineAnalyse Dynamique de Code (DAST)ExploitationAnalyse de HachageÉvasion IDS/IPSOutils d'ImpersonationMouvement LatéralPentesting d'Applications MobilesCriminalistique RéseauRétro-ingénierieOutils RFID/NFCSécurité SCADA/ICSScripting et AutomatisationSécurité ServerlessShellcodeExploitation d'Applications WebTests de Sécurité des APIAudit de ConfigurationExfiltration de DonnéesDébogueursAnalyse ForensiqueCollecte d'InformationsCriminalistique MobileContrôle d'Accès RéseauPost-ExploitationVirtualisation de SécuritéHameçonnageContournement de WAFSécurité WebFuzzingSécurité RéseauStéganographieSécurité Sans FilRécupération de DonnéesAnalyse de MalwareCriminalistique NumériqueHacking MatérielCryptographieCTFTests d'IntrusionSécurité CloudDevSecOpsSécurité MobileProtection de la Vie PrivéeCommandement et ContrôleIngénierie SocialeSécurité MatérielleUtilitaires et FrameworksSécurité Matériel et IoTDétection de SecretsAnalyse de BinairesRenseignement sur les MenacesGestion des Identités et des Accès (IAM)Sécurité de la Chaîne LogistiqueAuthentificationApprentissage AutomatiqueDétection d'IntrusionArticles et RechercheMauvaise ConfigurationÉnumération de Sous-domainesCollecte d'EmailsApprentissage et ÉducationRétro-Ingénierie Assistée par IAFuzzing DNSRed TeamingRéponse aux IncidentsCrawlerRessources OrganiséesOutil d'Accès à DistanceGénération de ShellcodeDéveloppement de Charges UtilesCheval de Troie d'Accès à DistanceSécurité des APIAnti-BotUsurpation d'Empreinte NumériqueContournement de CAPTCHASécurité des EmailsAnalyse DNSIngénierie du ChaosParcours et CoursÉvasion de ConteneurSécurité de l'IASécurité des Bases de DonnéesAnalyse de MicrologicielDétection d'AnomaliesAnalyse de JournauxAttaque AdversarialeExploitation de BinairesLabs et Pratique
Plus récentsPertinencePlus populairesMis à jour récemment
1690 résultats
Security_incident_report preview

Security_incident_report

GitHubkevin9480/security_incident_report

Projet DFIR reproduisant un scénario de compromission basé sur la vulnérabilité React2Shell (CVE-2025-55182) et analysant/répondant aux incidents de…

vulnerability-analysisweb-securitynetwork-security+5
il y a 3 mois
wannafind preview

wannafind

GitHubvalarauco/wannafind

Script simple utilisant nmap pour détecter CVE-2017-0143 MS17-010 dans votre réseau

reconnaissancevulnerability-scannersexploitation+3
3il y a 9 ans
Check-Point-Trusted-Access-Review preview

Check-Point-Trusted-Access-Review

GitHubwadesweaponshed/check-point-trusted-access-review

Application web locale pour effectuer une revue Check Point Trusted Access Review. Ce scanner a été conçu spécifiquement pour rechercher des…

vulnerability-scannersconfiguration-auditingnetwork-security+3
il y a 4 mois
camel-pqc-tls preview

camel-pqc-tls

GitHuboscerd/camel-pqc-tls

Cryptographie post-quantique (PQC) : exemples TLS 1.3 avec Apache Camel utilisant l'échange de clés hybride X25519MLKEM768 sur JDK 21 (BouncyCastle)…

network-securitycryptographyeducation+1
2il y a 6 mois
airdecloak-ng preview

airdecloak-ng

GitHubalt3kx/airdecloak-ng

Ma contribution à Aircrack-ng avec Thomas d'Otreppe

packet-sniffing-analysiswi-fi-auditingnetwork-security+2
4il y a 8 ans
cve-2026-1731-scanner preview

cve-2026-1731-scanner

GitHubcybrdude/cve-2026-1731-scanner

Analyseur de vulnérabilités passif pour CVE-2026-1731 — RCE pré-authentification BeyondTrust RS/PRA (CVSS 9.9). Usage éducatif et défensif uniquement.

defensive-toolsreconnaissancevulnerability-scanners+5
4il y a 9 mois
zeek-mercury-npf preview

zeek-mercury-npf

GitHubcorelight/zeek-mercury-npf

Plugin Zeek générant des empreintes Mercury NPF pour TCP, TLS/DTLS, QUIC, HTTP, SSH, OpenVPN et STUN afin de soutenir la surveillance de la sécurité…

defensive-toolspacket-sniffing-analysisnetwork-security
il y a 3 mois
Purdue-Model-for-Industrial-Control-System-Environments preview

Purdue-Model-for-Industrial-Control-System-Environments

GitHubmurataydemir/purdue-model-for-industrial-control-system-environments

Modèle Purdue pour les environnements de systèmes de contrôle industriels (ICS) (turc)

scada-ics-securitynetwork-securitypapers-research+1
3il y a 6 ans
kestrel preview

kestrel

GitHub1-bit-wonder/kestrel

Tableau de bord de sécurité d'exécution mono-hôte sur eBPF — agent Go + SvelteKit. Arborescence des processus en direct, carte du réseau et alertes…

defensive-toolsnetwork-securityintrusion-detection+2
il y a 4 mois
RTSPbrute preview

RTSPbrute

GitLabcamshift/rtspbrute

Simple bruteforce de flux rtsp

vulnerability-scannersiot-securitypassword-attacks+2
2il y a 8 ans
Jozini-network-scanner preview

Jozini-network-scanner

GitHubmngunibanda1-prog/jozini-network-scanner

Scanner réseau basé sur Python avec analyse de ports, récupération de bannières et mise en correspondance des CVE RouterOS pour l'identification et…

port-scanningvulnerability-analysisinformation-gathering+3
il y a 2 mois
reconkg preview

reconkg

GitHubxghst0/reconkg

Triage des vulnérabilités avec provenance. Résout les CVE à partir de corpus construits localement (NVD/KEV/EPSS, ExploitDB, nmap script.db) et émet…

threat-feeds-aggregatorsvulnerability-analysisnetwork-security+2
il y a 2 mois
project_BIT_nmap_script preview

project_BIT_nmap_script

GitHubmgregus/project_bit_nmap_script

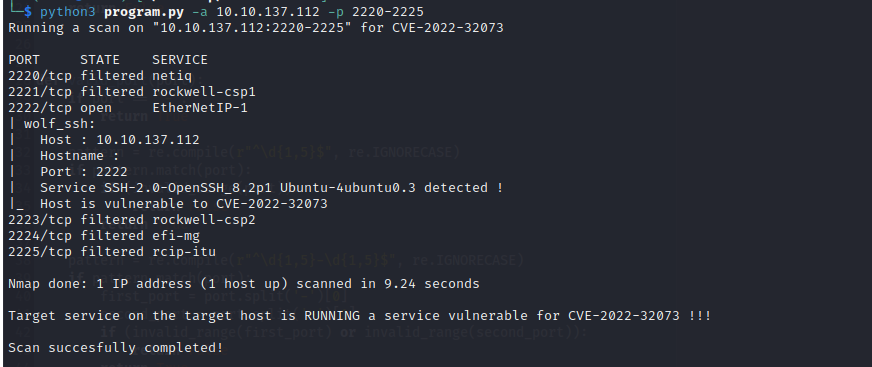
Script Nmap .nse pour scanner la CVE-2022-32073 dans wolfssh

vulnerability-scannersvulnerability-analysisexploitation+3
3il y a 3 ans
heartpatch.us preview

heartpatch.us

GitHubingochris/heartpatch.us

OpenSSL Heartbleed Bug CVE-2014-0160 Toolkit. Créé avec ❤ par Christopher Ngo.

vulnerability-scannersexploitationweb-security+2
3il y a 5 ans
security-operations-labs preview

security-operations-labs

GitHubelihiho/security-operations-labs

Modélisation des menaces, segmentation IT/OT, détection Snort et validation reproductible d’un profil de détection Drupal.

vulnerability-scannersconfiguration-auditingnetwork-security+5
il y a 3 mois
SystemVulnerabilityChecklist_Project4_Decodelabs preview

SystemVulnerabilityChecklist_Project4_Decodelabs

GitHubirsaattiquecyber/systemvulnerabilitychecklist_project4_decodelabs

Projet de liste de contrôle des vulnérabilités système et de durcissement de la sécurité réseau, comprenant la reconnaissance, l'analyse du backdoor…

reconnaissanceport-scanningvulnerability-analysis+5
il y a 3 mois
printnightmare-detection-mitigation-lab preview

printnightmare-detection-mitigation-lab

GitHubkaritamw/printnightmare-detection-mitigation-lab

Laboratoire de sécurité Windows assaini démontrant l'administration d'Active Directory, la détection hôte et réseau, et l'atténuation en couches de…

vulnerability-analysisnetwork-securitydigital-forensics+5
il y a 3 mois
coronary preview

coronary

GitHubamerine/coronary

Testez les blocs CIDR pour CVE-2014-0160/Heartbleed

vulnerability-scannersvulnerability-analysisinformation-gathering+2
2il y a 12 ans
Précédent1…737475…94Suivant
Des sources sélectionnées à une fiche d’outil Dépôts, flux, communautés et index passent par la sélection, la classification, l’enrichissement et la traduction pour former une fiche d’outil illustrative. ISC License Copyright (c) 2026 Lucide Icons and Contributors Permission to use, copy, modify, and/or distribute this software for any purpose with or without fee is hereby granted, provided that the above copyright notice and this permission notice appear in all copies. THE SOFTWARE IS PROVIDED "AS IS" AND THE AUTHOR DISCLAIMS ALL WARRANTIES WITH REGARD TO THIS SOFTWARE INCLUDING ALL IMPLIED WARRANTIES OF MERCHANTABILITY AND FITNESS. IN NO EVENT SHALL THE AUTHOR BE LIABLE FOR ANY SPECIAL, DIRECT, INDIRECT, OR CONSEQUENTIAL DAMAGES OR ANY DAMAGES WHATSOEVER RESULTING FROM LOSS OF USE, DATA OR PROFITS, WHETHER IN AN ACTION OF CONTRACT, NEGLIGENCE OR OTHER TORTIOUS ACTION, ARISING OUT OF OR IN CONNECTION WITH THE USE OR PERFORMANCE OF THIS SOFTWARE. --- The following Lucide icons are derived from the Feather project: airplay, alert-circle, alert-octagon, alert-triangle, aperture, arrow-down-circle, arrow-down-left, arrow-down-right, arrow-down, arrow-left-circle, arrow-left, arrow-right-circle, arrow-right, arrow-up-circle, arrow-up-left, arrow-up-right, arrow-up, at-sign, calendar, cast, check, chevron-down, chevron-left, chevron-right, chevron-up, chevrons-down, chevrons-left, chevrons-right, chevrons-up, circle, clipboard, clock, code, columns, command, compass, corner-down-left, corner-down-right, corner-left-down, corner-left-up, corner-right-down, corner-right-up, corner-up-left, corner-up-right, crosshair, database, divide-circle, divide-square, dollar-sign, download, external-link, feather, frown, hash, headphones, help-circle, info, italic, key, layout, life-buoy, link-2, link, loader, lock, log-in, log-out, maximize, meh, minimize, minimize-2, minus-circle, minus-square, minus, monitor, moon, more-horizontal, more-vertical, move, music, navigation-2, navigation, octagon, pause-circle, percent, plus-circle, plus-square, plus, power, radio, rss, search, server, share, shopping-bag, sidebar, smartphone, smile, square, table-2, tablet, target, terminal, trash-2, trash, triangle, tv, type, upload, x-circle, x-octagon, x-square, x, zoom-in, zoom-out The MIT License (MIT) (for the icons listed above) Copyright (c) 2013-present Cole Bemis Permission is hereby granted, free of charge, to any person obtaining a copy of this software and associated documentation files (the "Software"), to deal in the Software without restriction, including without limitation the rights to use, copy, modify, merge, publish, distribute, sublicense, and/or sell copies of the Software, and to permit persons to whom the Software is furnished to do so, subject to the following conditions: The above copyright notice and this permission notice shall be included in all copies or substantial portions of the Software. THE SOFTWARE IS PROVIDED "AS IS", WITHOUT WARRANTY OF ANY KIND, EXPRESS OR IMPLIED, INCLUDING BUT NOT LIMITED TO THE WARRANTIES OF MERCHANTABILITY, FITNESS FOR A PARTICULAR PURPOSE AND NONINFRINGEMENT. IN NO EVENT SHALL THE AUTHORS OR COPYRIGHT HOLDERS BE LIABLE FOR ANY CLAIM, DAMAGES OR OTHER LIABILITY, WHETHER IN AN ACTION OF CONTRACT, TORT OR OTHERWISE, ARISING FROM, OUT OF OR IN CONNECTION WITH THE SOFTWARE OR THE USE OR OTHER DEALINGS IN THE SOFTWARE.
Dépôts
GitHub & GitLab
Veille sécurité
Blogs, RSS et Atom
Communautés
Réseaux et contributions
Index sélectionnés
Listes et tendances
Trier et classer
Enrichir et traduire
Outil et dépôt fictifs. Description, catégories, étoiles, forks et vues sont des exemples, pas des données réelles ou vérifiées. Outil et dépôt fictifs. Description, catégories, étoiles, forks et vues sont des exemples, pas des données réelles ou vérifiées. {"fictional":true,"name":"Tool","version":"1.0.1","repository":"owner/tool","live_metrics":false,"example_metrics":{"stars":1200,"forks":128,"views":8600}}
Outil
owner/tool v1.0.1
Découvrez les actifs et vérifiez les en-têtes HTTP.
Reconnaissance
Sécurité web
1,200 étoiles — Exemple fictif1.2k 128 forks — Exemple fictif128 8,600 vues — Exemple fictif8.6k